Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Standard SSH Access with Compute OS Login
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
An enterprise is managing several Linux-based Compute Engine virtual machines (VMs) with OS Login enabled at the project level.
A junior developer requires SSH access to log into the VM instances to inspect application logs and run standard user scripts. According to company security policy, the developer must not have administrative or sudo privileges on the guest operating system.
Which IAM role should you grant to the developer to fulfill this requirement?
Explanations
roles/iam.securityAdmin
roles/iam.securityAdmin
What the Security Admin Role Is
The Security Admin role (roles/iam.securityAdmin) is a control-plane IAM role that grants permissions to view, create, update, and delete IAM policies across Google Cloud resources.
Why it doesn't meet the requirement
- Does not grant OS access: This role does not configure POSIX accounts or grant permission to establish SSH connections to Compute Engine VM instances via OS Login.
- Over-privileged control plane access: Grants extensive control over access control policies, which would allow the junior developer to alter project security bindings, violating the principle of least privilege.
Key characteristics and limitations
- Focuses on IAM policies: Primarily provides permissions such as
resourcemanager.projects.setIamPolicyandresourcemanager.projects.getIamPolicy. - No data or runtime access: Does not allow viewing compute resources, reading instance logs directly, or logging into operating systems.
This answer would be correct if
A security compliance officer needed to audit, modify, and manage the IAM role bindings and access permissions granted across Google Cloud project resources.
roles/compute.osAdminLogin
roles/compute.osAdminLogin
What the Compute OS Admin Login Role Is
The Compute OS Admin Login role (roles/compute.osAdminLogin) grants users the ability to log into Compute Engine instances via SSH with full administrator (sudo) privileges on the guest operating system.
Why it doesn't meet the requirement
- Violates security restrictions: The scenario explicitly states that the junior developer must not have administrative or
sudoprivileges on the instances. - Grants elevated rights: Assigning this role automatically adds the user's POSIX account to the
google-sudoersorsudogroup on the Linux instance, allowing them to execute any command as therootsuperuser.
Key characteristics and limitations
- Superuser access: Enables modifying core operating system packages, network settings, and sensitive system files.
- Administrative overhead: Requires strict governance and is generally reserved for systems administrators and DevOps engineers.
- Excessive permissions: Bypasses guest OS protections intended for standard application developers.
This answer would be correct if
The scenario required the developer or administrator to install software packages, modify system service daemon configurations, or perform maintenance tasks that require sudo or root permissions inside the Linux VM.
roles/iam.supportUser
roles/iam.supportUser
What the Support User Role Is
The Support User role (roles/iam.supportUser) is an administrative role designed to allow designated users to create, view, and manage Google Cloud Customer Care support cases.
Why it doesn't meet the requirement
- No instance connectivity: It provides no permissions to connect to Compute Engine instances or authenticate via OS Login.
- Unrelated functionality: Opening support tickets does not assist the developer in inspecting real-time application logs or executing troubleshooting scripts directly on the VM.
Key characteristics and limitations
- Support case management: Provides access to the Google Cloud Support Center console and APIs.
- No infrastructure visibility: Does not grant rights to list, start, stop, or inspect VMs or cloud workloads.
This answer would be correct if
The junior developer needed access to communicate with Google Cloud Technical Support to open and manage support tickets regarding service issues.
roles/compute.osLogin
roles/compute.osLogin
What the Compute OS Login Role Is
The Compute OS Login role (roles/compute.osLogin) allows users to access Compute Engine Linux instances via SSH using OS Login without granting administrator permissions on the guest operating system.
How it meets the requirements
- Provides SSH connectivity: Authorizes the user to log in to Linux VMs managed by OS Login using their federated Google identity.
- Enforces least privilege: Specifically creates a standard user account inside the Linux environment that does not belong to the
sudoersgroup or have elevated administrative rights. - Prevents root access: Ensures that the junior developer can read application files, run user scripts, and check logs while strictly preventing system-level configuration changes.
Key advantages and capabilities
- Centralized identity management: Ties Linux POSIX user accounts directly to Google Cloud IAM identities.
- Consistent UID/GID allocation: Assigns consistent user IDs and usernames across all instances in the project.
- Revocable access: Automatically cuts off SSH access immediately when the IAM role is removed or when the Google identity is disabled.
- Audit logging: Interoperates with Cloud Audit Logs to track OS-level SSH login events.
Why this is optimal
Compared to administrative roles, roles/compute.osLogin satisfies the principle of least privilege. When combined with roles/iam.serviceAccountUser (if the VM runs as a service account), it grants the exact level of access needed to troubleshoot and inspect logs without risking unauthorized modifications to critical system files.
OS Login Role Comparison: osLogin vs osAdminLogin
Comparison Matrix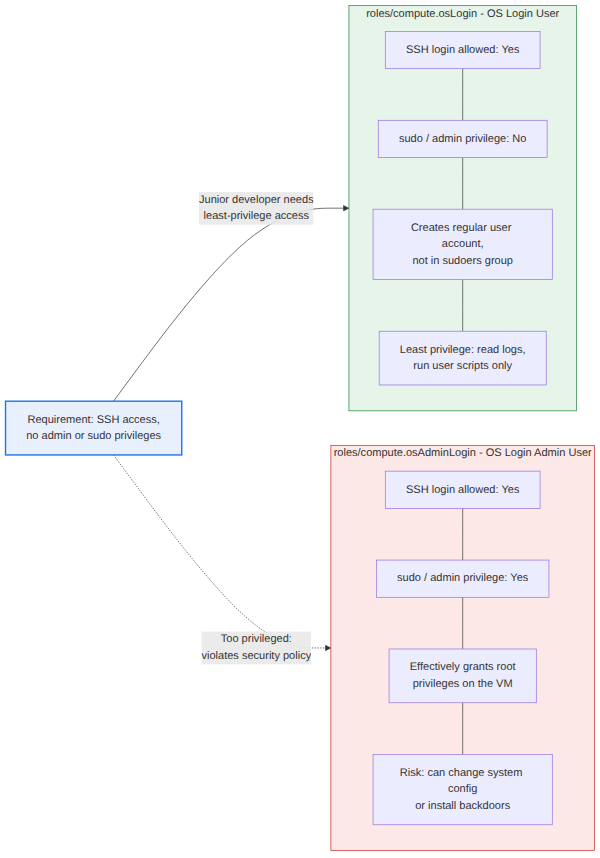
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
OS Login Ignores Metadata SSH Keys
Configuring OS Login
FundamentalAssociate Cloud Engineer
Compute Engine SSH Key Expiration Metadata
Configuring OS Login
FundamentalAssociate Cloud Engineer
OS Login IAM SSH Access
Remotely connecting to a Compute Engine instance
FundamentalAssociate Cloud Engineer
Cloud Profiler Continuous CPU Heap Profiling
Using cloud diagnostics to research an application issue (e.g., Cloud Trace, Cloud Profiler, Query Insights, index advisor)
FundamentalAssociate Cloud Engineer
Cloud Logging and Monitoring IAM Roles
Viewing the Personalized Service Health dashboard
FundamentalCloud Digital Leader
Vertex AI Managed ML Workflow
Discuss how building custom models by using Google Cloud’s Vertex AI can create opportunities for business differentiation.
Last updated