Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Temporary Object Access With Signed URLs
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your company stores confidential audit reports in a private Google Cloud Storage bucket. A third-party compliance auditor who does not have a Google account or IAM credentials in your organization needs temporary access to download specific files within a 2-hour window.
Which approach should you use to grant the auditor secure, time-limited access to the files?
Explanations
Use cookie-based authenticated browser downloads and provide the standard storage URL
Use cookie-based authenticated browser downloads and provide the standard storage URL
What this option does
Authenticated browser downloads (cookie-based authentication) allow users to access files via URLs formatted like https://storage.cloud.google.com/BUCKET_NAME/OBJECT_NAME by prompting them to log in with an authenticated Google account.
Why it doesn't meet the requirement
- Requires a Google account: Cookie-based downloads require the visiting user to authenticate with a valid Google Workspace, Cloud Identity, or Gmail account that already has explicit
storage.objects.getIAM or ACL permissions on the object. - No external anonymous support: Because the auditor has no Google identity or credentials in the organization, visiting this URL will simply result in a
403 Forbidden (access denied)error. - Lacks automatic expiration: Cookie-based authentication does not provide built-in, fine-grained URL expiration windows like signed URLs do.
Key characteristics and limitations
- Identity dependency: Relies entirely on the user's active Google browser session.
- IAM/ACL prerequisite: Requires pre-existing
Storage Object Vieweror ACLREADpermissions assigned directly to that specific identity. - Direct link: Navigates through
storage.cloud.google.comrather than query-string signed endpoints.
This answer would be correct if
The auditor was an internal employee or external collaborator with an existing corporate Google account that had already been granted the Storage Object Viewer role on the bucket.
Additional context
Authenticated browser downloads are intended for quick human collaboration within an organization, not for sharing private data with external users who lack Google identities.
Grant the Storage Object Admin role directly to the auditor's external email address on the bucket
Grant the Storage Object Admin role directly to the auditor's external email address on the bucket
What this option does
The Storage Object Admin (roles/storage.objectAdmin) role grants full control over objects within a bucket, including uploading, listing, deleting, and modifying object ACLs.
Why it doesn't meet the requirement
- Requires a registered Google identity: Direct IAM role assignment requires the external email address to be associated with an active Google Account or Cloud Identity domain.
- Excessive permissions (violates least privilege): An auditor only requires read/download access to specific files. Granting
Storage Object Admingrants full read, write, overwrite, and delete capabilities over all objects in the bucket. - No automatic expiration: Standard bucket-level IAM role grants do not automatically revoke after 2 hours without configuring complex conditional bindings or manual removal.
Key characteristics and limitations
- Overprivileged: Permits object deletion, overwriting existing reports, and managing object ACLs.
- Bucket-wide scope: Grants permissions across the entire bucket rather than limiting access to the specific requested files.
- Administrative overhead: Requires administrators to remember to manually revoke the role after the 2-hour window.
This answer would be correct if
A vendor needed long-term, full administrative and upload control over their own dedicated drop box bucket and possessed a valid Google account.
Additional context
Always apply the principle of least privilege. An auditor only requires temporary read permissions, making administrative roles fundamentally inappropriate.
Generate a signed URL with a 2-hour expiration time using a service account
Generate a signed URL with a 2-hour expiration time using a service account
What a Signed URL is
A Signed URL is a mechanism in Google Cloud Storage that gives time-limited read or write access to a specific Cloud Storage resource. Anyone who possesses the URL can use it to access the specified object without requiring a Google account or IAM permissions of their own, because the URL carries cryptographic authentication derived from a delegated service account.
Signed URL: 2-Hour Auditor Access Flow
Sequence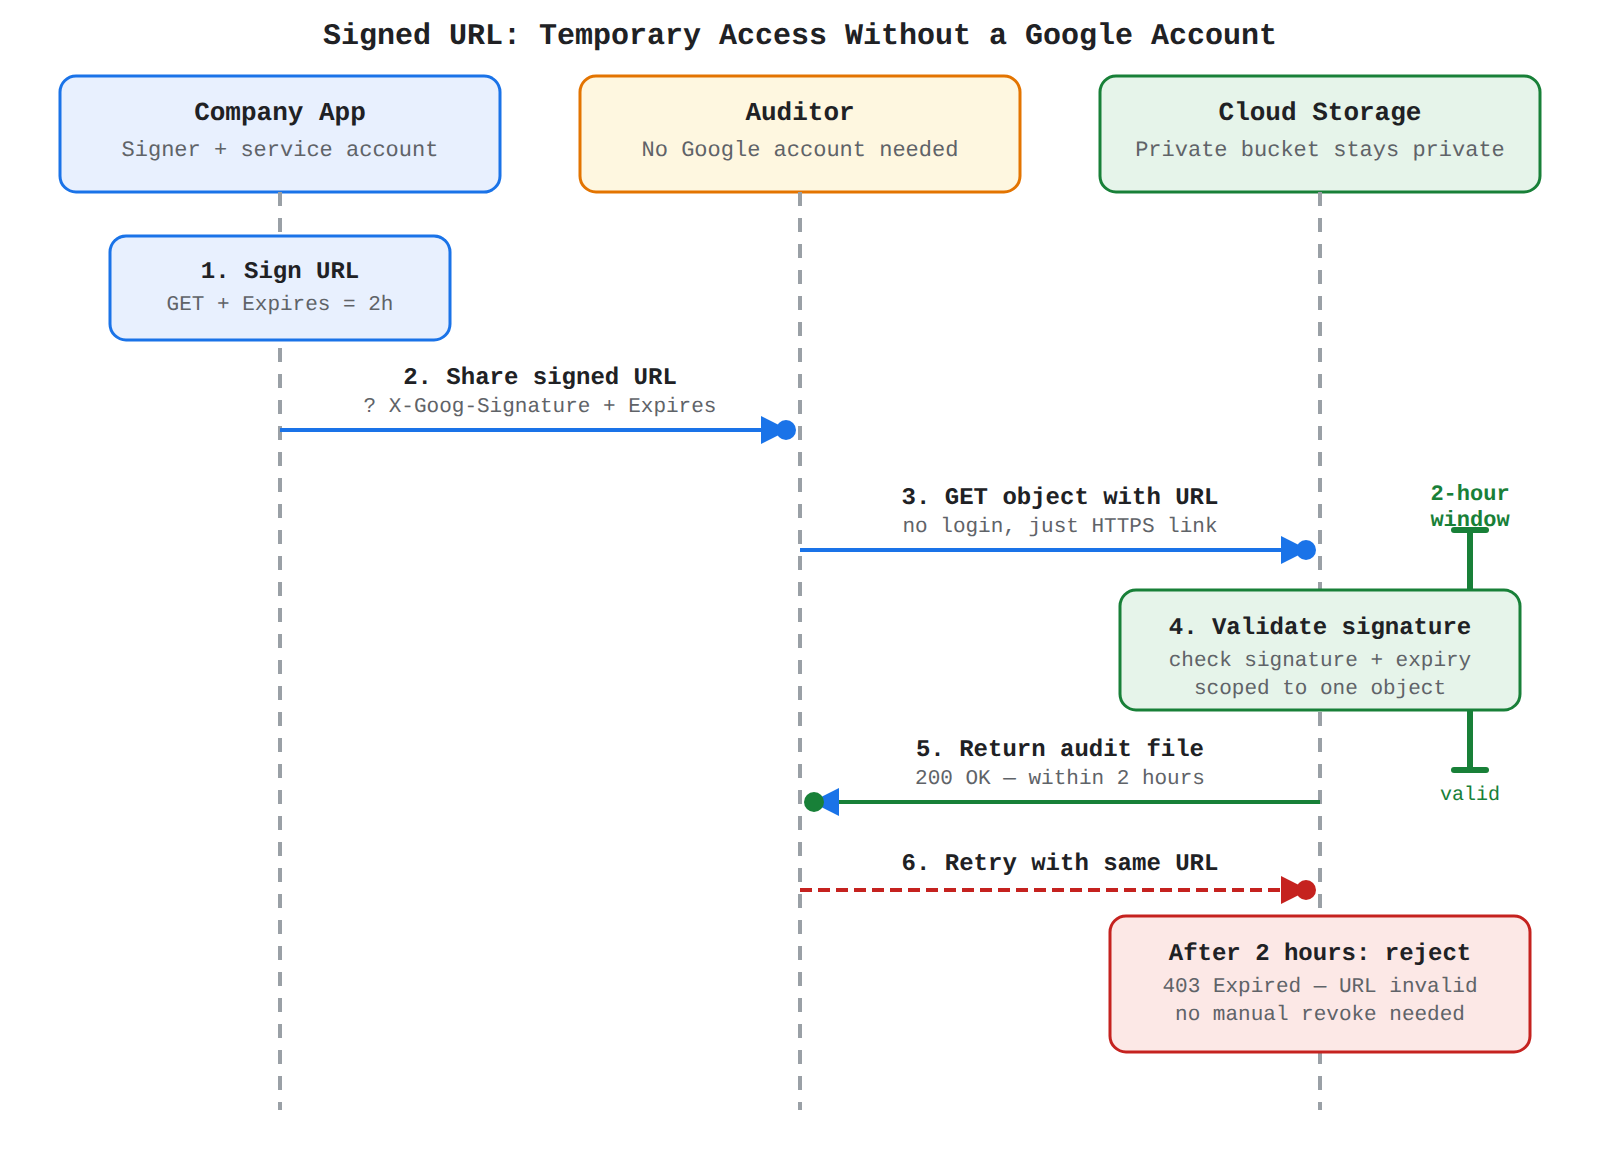
How it meets the requirements
- Time-limited access: Signed URLs include an explicit expiration timestamp (in this scenario, set to exactly 2 hours). Once the expiration deadline passes, the URL becomes invalid and subsequent requests return an authorization error.
- No Google account required: The auditor does not need a Google identity, workforce federation, or Cloud Identity account. The signature embedded in the query string validates the request on their behalf.
- Maintains bucket privacy: The bucket and the objects remain strictly private. Access is restricted exclusively to the specific object path targeted by the signed URL rather than exposing the entire bucket.
Key advantages and capabilities
- Granular scoping: URLs can be generated for specific HTTP methods (such as
GETfor downloading orPUTfor uploading) and specific object paths. - Self-expiring authorization: Eliminates administrative overhead because you do not need to manually revoke permissions after the 2-hour review period concludes.
- Delegated authority: Access permissions are bounded by the permissions held by the signing service account at the time of the request.
- Query string authentication: Provides a simple HTTPS link that works in any browser, script, or
curlcommand.
Why this is optimal
Signed URLs are specifically designed for external, unauthenticated, or third-party sharing where creating and managing temporary IAM principals or Google accounts is impractical or undesired.
Grant the Storage Object Viewer role to allUsers with an IAM condition that expires in 2 hours
Grant the Storage Object Viewer role to allUsers with an IAM condition that expires in 2 hours
What this option does
Assigning the Storage Object Viewer role to the allUsers principal identifier makes the bucket's contents accessible to anyone on the public internet without any authentication.
Why it doesn't meet the requirement
- Breaches confidentiality: Granting permissions to
allUsersmakes sensitive audit reports completely public across the internet for anyone who discovers or guesses the object URL. - Violates security best practices: Storage buckets containing private or confidential company data should never be exposed to anonymous public access (
allUsers). - Lacks target restriction: It grants read access to all public internet users rather than restricting access specifically to the authorized third-party auditor.
Key characteristics and limitations
- Public exposure:
allUsersrepresents all unauthenticated users on the public internet. - Domain exposure risk: Even with temporary IAM condition constraints, making confidential objects publicly readable introduces severe compliance and data exposure risks.
- Data governance violation: Security tools like Cloud Storage domain-restricted sharing or organizational policies often explicitly block grants to
allUsers.
This answer would be correct if
You were hosting a publicly distributed open-source file or static website asset intended for anonymous download by the general public without authentication.
Additional context
Security frameworks and cloud posture tools flag allUsers access on private storage buckets as a critical security vulnerability.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
IAM Roles at Project vs Bucket Level
Managing and securing objects in Cloud Storage buckets
FundamentalAssociate Cloud Engineer
Managed Collection vs Self-Deployed Collection
Deploying Google Cloud Managed Service for Prometheus
FundamentalAssociate Cloud Engineer
Cloud Trace Distributed Tracing Spans
Using cloud diagnostics to research an application issue (e.g., Cloud Trace, Cloud Profiler, Query Insights, index advisor)
FundamentalAssociate Cloud Engineer
Artifact Registry Reader Role for GKE Nodes
Configuring GKE to access Artifact Registry
FundamentalAssociate Cloud Engineer
Windows Sysprep Specialize Script Metadata
Launching a compute instance (e.g., availability policy, SSH keys)
IntermediateProfessional Cloud Developer
BigQuery Nested Repeated Fields Schema Evolution
Writing data to BigQuery for analytics and AI/ML workloads
Last updated