Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Least Privilege Image Pulls for GKE Nodes
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
An operations team is deploying workloads to a Google Kubernetes Engine (GKE) cluster. The container images are stored in a private Artifact Registry repository in the same project.
To adhere to the principle of least privilege, the team configures the GKE cluster nodes to use a dedicated custom IAM service account rather than the Compute Engine default service account. The cluster nodes only need permission to download and run the container images.
Which IAM role should be assigned to the custom service account attached to the GKE nodes?
Explanations
Storage Admin (roles/storage.admin)
Storage Admin (roles/storage.admin)
What the Storage Admin Role Is
The Storage Admin (roles/storage.admin) role provides full administrative control over Cloud Storage buckets and objects. This includes creating buckets, deleting buckets, changing bucket permissions, and reading/writing all stored objects.
Why It Doesn't Meet the Requirement
- Wrong Target Service: Artifact Registry is a dedicated artifact management service that utilizes its own distinct IAM roles (
roles/artifactregistry.*) rather than Cloud Storage IAM roles. - Severe Over-Privileging: Granting Storage Admin provides full administrative access across Cloud Storage, violating the principle of least privilege.
- Historical Confusion: In legacy Container Registry (
gcr.io), images were directly stored in backing Cloud Storage buckets, leading some administrators to use storage roles. Artifact Registry decouples these permissions and requires Artifact Registry-specific roles.
Key Characteristics and Limitations
- Applies to Cloud Storage: Controls Google Cloud Storage (
gs://) buckets, not Artifact Registry repository APIs. - Full Administrative Control: Includes destructive actions like deleting entire storage buckets.
- Legacy Legacy GCR Distinction: Container Registry used
roles/storage.objectViewerfor pulling, but Artifact Registry requiresroles/artifactregistry.reader.
This Answer Would Be Correct If
The service account belonged to an infrastructure management automation system designed to create, configure, and delete Cloud Storage buckets across the project.
Artifact Registry Administrator (roles/artifactregistry.admin)
Artifact Registry Administrator (roles/artifactregistry.admin)
What the Artifact Registry Administrator Role Is
The Artifact Registry Administrator (roles/artifactregistry.admin) role gives users full control over Artifact Registry repositories and their contents. This includes creating repositories, deleting repositories, modifying IAM policies on repositories, and managing repository configurations.
Why It Doesn't Meet the Requirement
- Unnecessary Administrative Power: GKE worker nodes only need to download container images during workload scheduling. They have no operational requirement to manage registry infrastructure or alter access policies.
- Security Risk: Granting administrative control to compute instances means any compromised workload accessing the metadata server could delete repositories or modify IAM access controls across the project.
Key Characteristics and Limitations
- Full Lifecycle Management: Allows repository creation, configuration, and destruction.
- IAM Policy Modification: Grants authority to grant and revoke access permissions on Artifact Registry resources.
- Intended for Platform Engineers: Designed for human administrators or central infrastructure provisioning automation.
This Answer Would Be Correct If
The task involved provisioning a central identity for a Terraform or Infrastructure-as-Code pipeline responsible for creating, updating, and securing Artifact Registry repositories.
Artifact Registry Reader (roles/artifactregistry.reader)
Artifact Registry Reader (roles/artifactregistry.reader)
What the Artifact Registry Reader Role Is
The Artifact Registry Reader (roles/artifactregistry.reader) role is a predefined Identity and Access Management (IAM) role that provides read-only access to Artifact Registry resources. It grants the essential permissions required to view repository metadata and pull container images or language packages without granting permissions to upload, modify, or delete artifacts.
How It Meets the Requirements
- Pulls Private Images: When GKE nodes pull container images during pod creation, the node uses its attached service account credentials to authenticate against Artifact Registry. The Artifact Registry Reader role contains the exact permissions (
artifactregistry.repositories.downloadArtifacts) needed to authenticate and stream image layers to the node runtime. - Enforces Least Privilege: Using a dedicated custom service account with the reader role ensures that if a workload or node is compromised, it cannot overwrite or delete container images, tamper with repositories, or access unrelated cloud services.
GKE Node Pulls Image via Reader Role
Sequence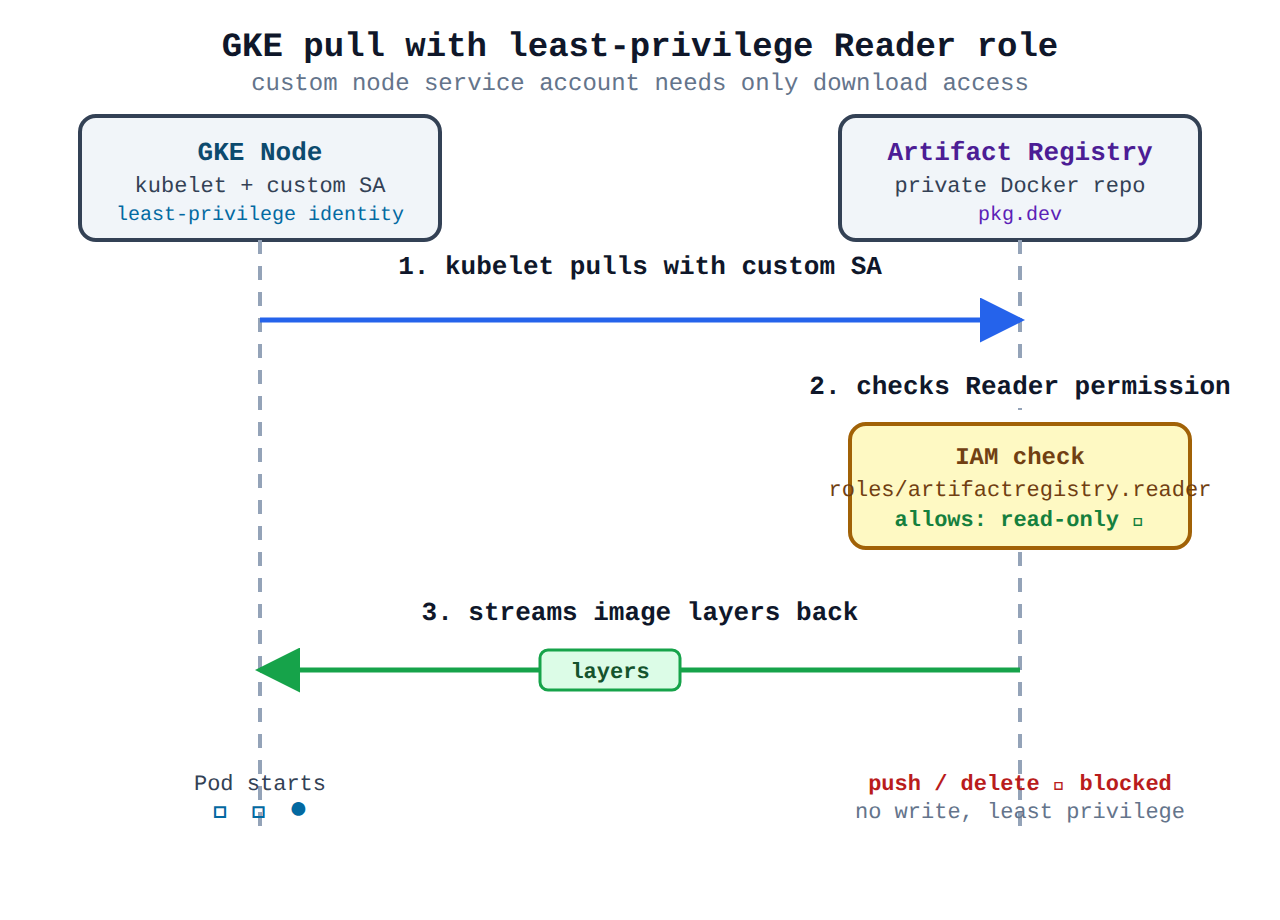
Key Advantages and Capabilities
- Granular Security Boundary: Limits the node identity to read-only capabilities for container registries.
- Native GKE Integration: Works seamlessly with the container runtime on GKE nodes without requiring manual Kubernetes image pull secrets.
- Repository and Project Scope: Can be granted at the project level or scoped down directly to a specific Artifact Registry repository for stricter access control.
- Replaces Overly Permissive Defaults: Avoids granting broad access like the Compute Engine default service account historically possessed.
Why This Is Optimal
Granting the Artifact Registry Reader role directly to the custom node service account provides the minimal necessary permissions for GKE image deployment while eliminating security risks associated with administrative or write-level privileges.
Artifact Registry Writer (roles/artifactregistry.writer)
Artifact Registry Writer (roles/artifactregistry.writer)
What the Artifact Registry Writer Role Is
The Artifact Registry Writer (roles/artifactregistry.writer) role is designed for CI/CD pipelines, build systems, and developers who need to read and upload artifacts. It grants permissions to read repositories as well as push new container images and create repository tags.
Why It Doesn't Meet the Requirement
- Violates Least Privilege: GKE cluster nodes only pull and execute container images; standard worker nodes do not build or publish new container images to Artifact Registry. Assigning write permissions introduces unnecessary risk.
- Excessive Node Privileges: If an application pod on the node is compromised and has access to the node service account token, malicious actors could potentially overwrite existing container image tags or upload untrusted images.
Key Characteristics and Limitations
- Read and Write Access: Grants both
artifactregistry.repositories.uploadArtifactsand download capabilities. - Intended for Build Agents: Best suited for build tools like Cloud Build, Jenkins, or GitLab CI/CD runners.
- Not Required for Deployment: Kubernetes worker nodes do not require write access to deploy workloads.
This Answer Would Be Correct If
The cluster nodes were specifically running continuous integration (CI) worker workloads or container builder processes that compile code and push newly created container images to the registry.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Gemini Cloud Assist Required APIs
Configuring Cloud Asset Inventory and using Gemini Cloud Assist to analyze resources
FundamentalAssociate Cloud Engineer
gcloud projects add-iam-policy-binding
Granting members Identity and Access Management (IAM) roles within a project
FundamentalAssociate Cloud Engineer
GKE Regional vs Zonal Cluster
Deploying a GKE cluster with different configurations (e.g., GKE Autopilot, regional clusters, private clusters)
FundamentalAssociate Cloud Engineer
Hyperdisk Balanced Proportional Auto-Growth
Choosing the appropriate storage for Compute Engine (e.g., zonal Persistent Disk, regional Persistent Disk, Google Cloud Hyperdisk)
FundamentalAssociate Cloud Engineer
Shared VPC Subnet-Level IAM
Creating a VPC with subnets (e.g., custom mode VPC, Shared VPC)
IntermediateProfessional Cloud Developer
Firestore Subcollections and Collection Group Indexes
Designing appropriate schemas for structured databases (e.g., AlloyDB, Spanner) and unstructured databases (e.g., Bigtable, Firestore)
Last updated