Diagram
CMEK Envelope Encryption Flow
Sequence
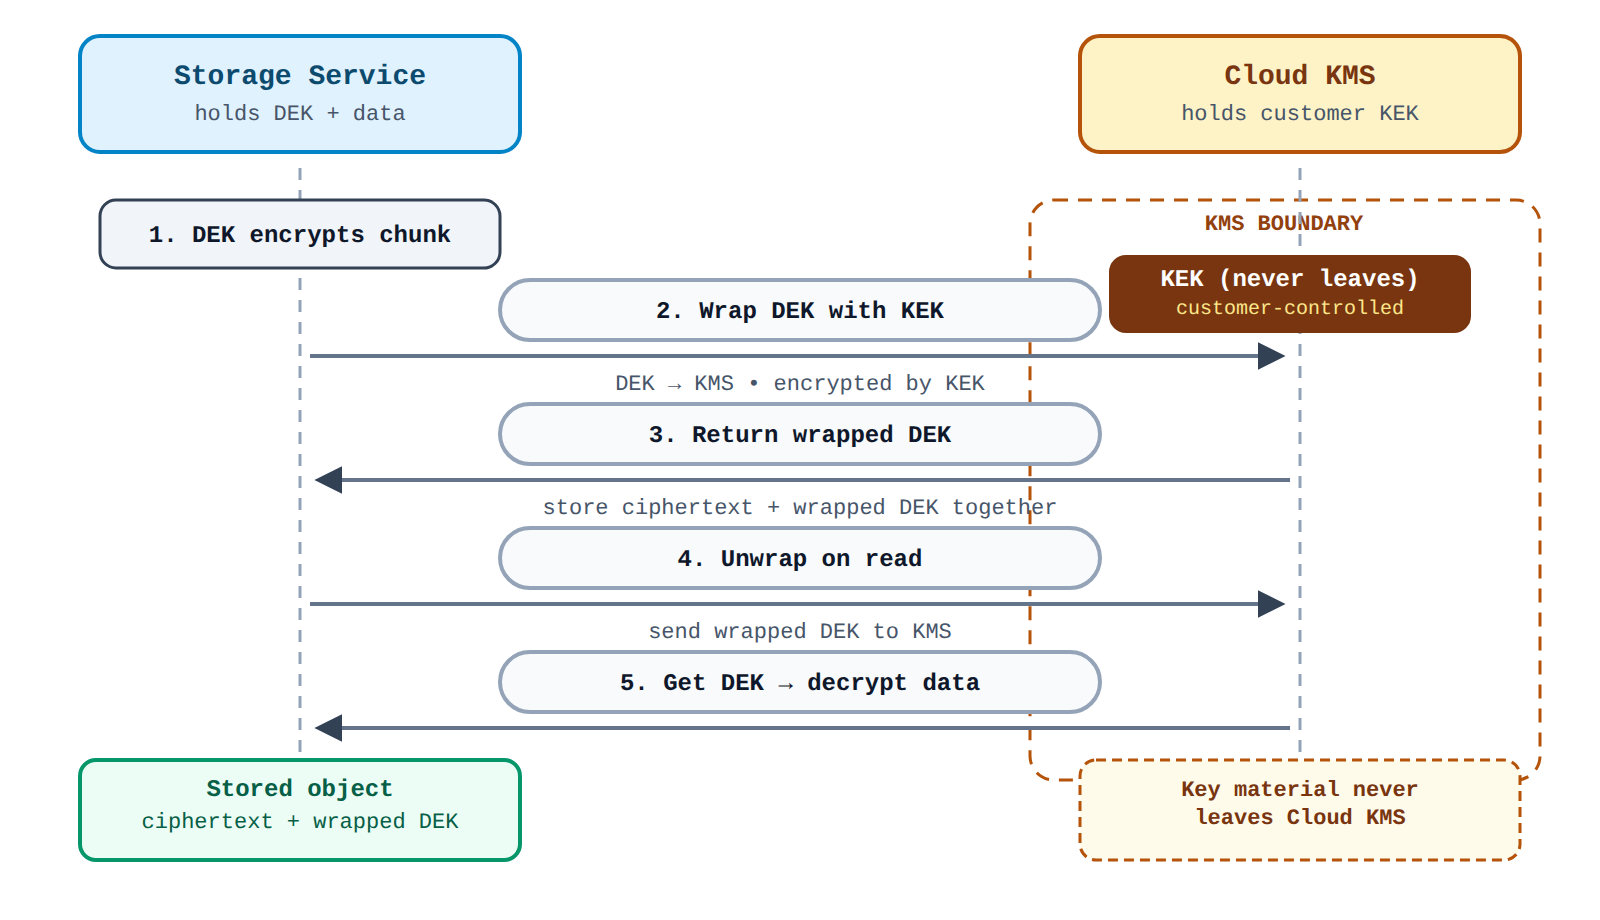
A sequence showing the storage service generating a DEK to encrypt data, sending it to Cloud KMS to be wrapped by the customer-controlled KEK, storing ciphertext with the wrapped DEK, then unwrapping it on read to decrypt.
In the Domain
How Customer-Managed Encryption Keys Work With Cloud KMS
Customer-managed encryption keys (CMEK) are customer-controlled KEKs stored in Cloud Key Management Service (Cloud KMS) and used through envelope encryption to protect stored data. The storage service calls Cloud KMS to encrypt and decrypt its data encryption keys, so the customer key never leaves Cloud KMS but still governs access to the data. This model gives control over protection level, location, rotation, permissions, and audit visibility while keeping normal storage access.
CMEK control helps meet regulatory and data sovereignty rules because the key carries its own location, access, and lifecycle policy:
Domain 3 of 7
Security and access management
Read the Domain summaryPractice this Domain
23 practice questions
Practice this DomainLast updated