Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
CMEK Encryption, IAM Permissions and VPC Perimeters
Data Encryption and Key Management Strategies control how data at rest is protected and who controls the keys that unlock it. With Google default encryption, Google owns and manages the symmetric key encryption keys (KEKs) that protect customer content with no customer action. With Customer-managed encryption keys (CMEK), the customer controls those KEKs in Cloud Key Management Service (Cloud KMS) while access to the storage resource feels much the same.
How Customer-Managed Encryption Keys Work With Cloud KMS
Customer-managed encryption keys (CMEK) are customer-controlled KEKs stored in Cloud Key Management Service (Cloud KMS) and used through envelope encryption to protect stored data. The storage service calls Cloud KMS to encrypt and decrypt its data encryption keys, so the customer key never leaves Cloud KMS but still governs access to the data. This model gives control over protection level, location, rotation, permissions, and audit visibility while keeping normal storage access.
CMEK Envelope Encryption Flow
Sequence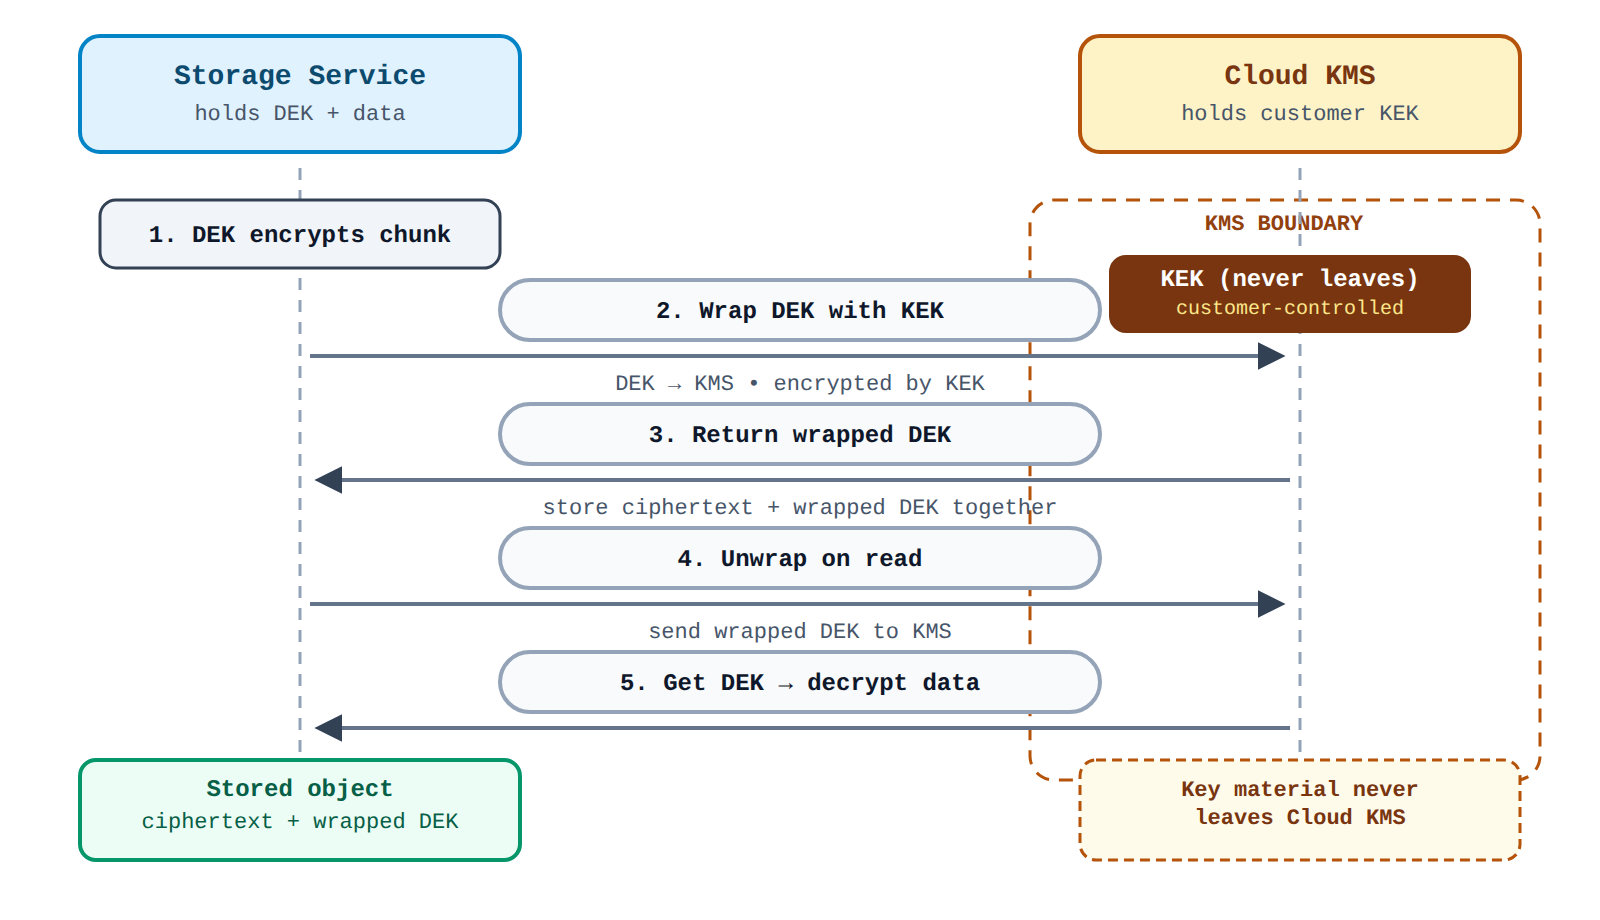
A sequence showing the storage service generating a DEK to encrypt data, sending it to Cloud KMS to be wrapped by the customer-controlled KEK, storing ciphertext with the wrapped DEK, then unwrapping it on read to decrypt.
CMEK control helps meet regulatory and data sovereignty rules because the key carries its own location, access, and lifecycle policy:
- Protection level: choose software keys, hardware keys in a hardware security module (HSM) cluster, or externally managed keys through Cloud External Key Manager (Cloud EKM).
- Location and boundary: keep the key ring and key in the same location as the protected data to enforce residency and cryptographic boundaries.
- Rotation schedule: define rotation so a new key version is created on schedule and used automatically for new encryption.
- Usage and access permissions: grant or revoke access through Identity and Access Management (IAM) without moving the data.
- Audit and inventory: track which keys protect which resources and who accessed them through Key Inventory, Key Usage dashboards, and Cloud Logging.
- Lifecycle control: disable, enable, schedule destruction, or destroy key versions to suspend or permanently remove access.
Configuring CMEK for a Storage System
Configuring CMEK for a storage system links a Cloud KMS key to the storage resource and authorizes the storage service to use it. The key ring and key can live in a different project from the storage instance, but they must be in the same location as the data, and the region selected for the service must match the Cloud KMS key location. The storage service depends on its Google-managed service account holding the CryptoKey Encrypter/Decrypter role on that key, or requests fail with permission_denied for cloudkms.cryptoKeyVersions.useToEncrypt.
A typical CMEK enablement follows this order:
- Create key ring and key: Enable the Cloud KMS API and create a symmetric key ring and crypto key where the data will reside.
- Identify the service account: Obtain the Google-managed service account for the storage service, such as the Filestore (opens in a new tab) service account or the
service-org-ORG_ID@gcp-sa-dataplex.iam.gserviceaccount.comaccount for Knowledge Catalog. - Grant encrypt and decrypt access: Grant
roles/cloudkms.cryptoKeyEncrypterDecrypteron the key to that service account so the service can call Cloud KMS. - Assign configuration rights: Assign the service-specific encryption admin role, such as Dataplex Encryption Admin, to the administrator who will set the encryption configuration.
- Attach the key to the resource: Select the key resource ID, for example
projects/PROJECT_ID/locations/LOCATION/keyRings/KEY_RING/cryptoKeys/KEY_NAME, when creating the instance, subscription, or organization-level encryption config. - Verify completion: Check the encryption state until it reports completion, such as
encryptionState: COMPLETED, before treating the migration as finished.
Support varies by service and tier. Filestore supports CMEK on Zonal, Regional, and Enterprise tiers but not on Basic HDD or Basic SSD tiers. Some services require CMEK at creation time only and do not allow adding CMEK to an existing resource or reverting from CMEK to Google default encryption.
Monitoring, Rotation, and Key Lifecycle Protection
Monitoring, rotation, and key lifecycle protection determine whether encrypted data stays available and auditable over time. Cloud KMS Data Access audit logs show when a CMEK-integrated service makes encrypt and decrypt calls to Cloud KMS, and some services use a poller that checks the key about every five minutes rather than calling on every data request. Filter Cloud Logging with resource.type="cloudkms_cryptokey" plus the key ring, key, and location labels to isolate entries for one key.
Key rotation creates a new key version that is automatically used for new encryption, and existing data is also re-encrypted with the new version in services that support it. Disabling or destroying the active key version makes the protected data inaccessible within minutes to a few hours, and the change can take up to 3 hours to fully take effect. If the key stays disabled, destroyed, or unreachable for more than 30 days, the encrypted data is automatically deleted and cannot be recovered, so keys in active use must remain enabled and accessible.
Exam tip: A disabled or destroyed CMEK key blocks data access first and causes permanent loss after 30 days — restore the key or its permissions within that window to recover access.
Enforcing CMEK With Organization Policies
CMEK organization policies enforce consistent encryption compliance across an organization, folder, or project. The policies apply at resource creation and at encryption-config time, so a request that lacks an allowed CMEK key fails instead of creating unprotected data. Project-level key choices must align with organization-wide constraints to avoid inconsistent denials.
| Constraint | What it controls | Effect when enforced |
|---|---|---|
constraints/gcp.restrictNonCmekServices | Whether listed services must use CMEK | Setting the service, such as dataplex.googleapis.com, to Deny blocks creation of resources without CMEK protection |
constraints/gcp.restrictCmekCryptoKeyProjects | Which hierarchies can supply CMEK keys | Setting allowed projects, folders, or organizations to Allow blocks CMEK resources protected by keys from disallowed hierarchies |
Availability and Sovereignty Tradeoffs With External Keys
Availability and sovereignty tradeoffs with external keys balance customer control against dependence on a third-party key manager. By design, Cloud EKM keys are managed outside Google Cloud, so Google Cloud is not responsible for their availability. If Cloud KMS is notified that an external key is unreachable, users receive an ekm_key_unreachable_detected notification with limited operations for up to one hour, then encrypt and decrypt operations fail and the instance is suspended.
Short-term Cloud KMS or EKM unavailability causes temporary data inaccessibility, with full operations continuing on a best-effort basis for up to one hour in some services. Enabling CMEK can also pause management operations during rollout, such as Dataplex API methods becoming temporarily unavailable for up to two hours while existing data is encrypted after 6 to 8 hours of infrastructure provisioning. Choose Cloud KMS or Cloud HSM keys when operational continuity matters most, and choose Cloud EKM only when sovereignty or regulatory mandates require keys to remain outside Google Cloud despite the higher availability risk.
Network security perimeters and temporary access are controls that keep private storage and data services from sending data to untrusted places while still allowing approved outside requests. VPC Service Controls (opens in a new tab) is a resource-centric control that creates a service perimeter around projects and explicitly specified services, so resources inside the perimeter can communicate but requests that would copy data outside are blocked. Temporary outside access is granted through access levels that are checked on each request, while Identity and Access Management (IAM) still controls who can act inside the perimeter.
What VPC Service Controls Perimeters Do
VPC Service Controls perimeters protect the resources and data of services explicitly added as restricted services. Data flows only between protected projects and protected services inside the same perimeter, and any API call that tries to move data from a protected service to a resource outside the perimeter is denied. This boundary applies to all user identities and all service account identities, which helps mitigate data exfiltration even when authorization credentials are compromised. After a perimeter is created or updated, changes can take up to 30 minutes to propagate, during which blocked requests can return Error 403: Request is prohibited by organization's policy.
User-Centric Compared With Resource-Centric Controls
Chrome Enterprise Premium access control and VPC Service Controls solve different parts of unauthorized access. Chrome Enterprise Premium is user-centric and rejects user API traffic that does not meet defined conditions, while VPC Service Controls is resource-centric and defines the perimeters within which resources can communicate.
| Control | What it protects | Which identities it checks |
|---|---|---|
| Chrome Enterprise Premium | User API traffic against per-request conditions | User identities within the organization only |
| VPC Service Controls | Resources and data inside a service perimeter | All user identities and service account identities |
Chrome Enterprise Premium conditions are evaluated on every API request and can include IP-based access or certificate-based access for mutual TLS. When used together, Chrome Enterprise Premium blocks requests from an attacker-controlled machine outside the environment, and VPC Service Controls blocks movement of protected data outside the perimeter.
Exam tip: Access levels apply only to requests for protected resources coming from outside the service perimeter; they cannot give protected resources or VMs permission to access data and services outside the perimeter.
Creating and Managing a Service Perimeter
A service perimeter is created by selecting the projects to protect and then choosing which APIs are restricted inside that boundary. The workflow depends on the perimeter containing both the projects and their dependent services, because a missing service leaves a path for data to leave.
- Select protected projects: Add the project IDs that contain the instances or data to protect to the resources-to-protect list.
- Create the perimeter: Create the service perimeter that will enforce the boundary around those projects.
- Add more instances: Add existing instances to the perimeter by updating the service perimeter.
- Add restricted services: Add the APIs to restrict, such as
databasecenter.googleapis.comfor Database Center, Secure Source Manager,geminidataanalytics.googleapis.comfor Conversational Analytics API, orces.googleapis.comandcontactcenterinsights.googleapis.comfor CX Agent Studio.
Restricted services must include supporting services in the same perimeter to prevent exfiltration through dependencies. For Database Center, restrict the Database Center API, Compute Engine API, Cloud Storage API, Container Registry API, Certificate Authority Service API, and Cloud KMS API. For analytics and agent workloads, also protect data sources such as bigquery.googleapis.com, storage.googleapis.com, Looker, and Sensitive Data Protection redaction resources in the same perimeter.
Access Levels for Controlled Outside Access
Access levels are the way to permit limited external access to protected resources inside a perimeter without opening the perimeter itself. An access level defines conditions that an outside request must meet, and only requests flowing from outside the perimeter to a protected resource inside are evaluated against those conditions. Traffic flowing from a protected resource inside the perimeter to the outside cannot be authorized by an access level and remains blocked. This one-way rule keeps temporary access from becoming an exfiltration path, so outside tools, imports, exports, and writes to Cloud Storage or BigQuery datasets outside the perimeter still fail.
Combining Perimeters With IAM Permissions
VPC Service Controls perimeters and IAM work together to enforce complete storage security. The perimeter enforces the network-level security boundary around the service, while IAM governs who can access resources within that boundary. Even when access originates inside a protected perimeter, users or service accounts still require the necessary IAM permissions on both the service and the underlying data sources, such as BigQuery datasets, Looker instances, or Service Directory resources. Setting up a perimeter therefore requires both the roles/accesscontextmanager.policyAdmin role to manage the boundary and correct IAM roles on the protected data, so an allowed network path does not become allowed data access.
Identity and Access Management (IAM) is the system that controls who can create, view, edit, or delete data in Google Cloud storage resources. Access is decided by IAM permissions and roles, and every API request requires the calling principal to have the required permission on the target resource. A principal can be a user account, a group, or a service account used by an application, and permissions are never granted directly but only by binding a role to a principal on a specific resource.
How IAM Policies Connect Principals, Roles, and Resources
An IAM policy is a binding that connects three entities: a principal, a role, and a resource. The principal is the identity making the request, the role is a collection of permissions, and the resource is the object being accessed, such as a Cloud SQL instance, a Cloud Storage bucket or object, or a Secure Source Manager (opens in a new tab) instance or repository. When a role is granted to a principal, the principal receives all permissions contained in that role, and the same principal can hold multiple roles. Bindings can apply at different levels of the hierarchy, including project, folder, instance, and repository, with project-level bindings applying by default to all instances in the project.
Predefined Roles, Custom Roles, and Least Privilege
Predefined roles are Google-maintained collections of permissions for common jobs, while custom roles allow organizations to combine only the permissions a specific job needs. Least privilege means granting only the roles required to accomplish a task at the smallest scope, and reviewing role recommendations to remove unused or excessive grants. For storage systems, role choice controls both management and data access.
roles/storage.admingrants full control of buckets and objects.roles/storage.objectAdmingrants full control of objects without bucket management.roles/storage.objectCreatorallows creating objects without viewing or deleting them.roles/storage.objectViewerallows read-only viewing of objects.roles/cloudsql.admin,roles/cloudsql.editor,roles/cloudsql.client,roles/cloudsql.instanceUser, androles/cloudsql.viewerseparate database administration, connection, login, and read-only work.- Instance-level roles, such as Instance Accessor and Instance Repository Creator, control access to the container, while repository-level roles, such as Repo Reader, Repo Writer, and Repo Admin, control access to the data inside.
Exam tip: A principal cannot receive a permission directly; the permission must come from a role binding, such as roles/storage.objectViewer for read-only object access or roles/cloudsql.instanceUser which includes cloudsql.instances.login.
Managing Access at Scale with Groups and Service Accounts
Centralized group management simplifies administration by granting IAM roles and database privileges once to a Cloud Identity group instead of to each user or service account. When a user is added to the group, the user automatically inherits the group's login ability and data privileges, and when the user is removed, login access and privileges are removed at the same time. Even with group-level grants, each user and service account still authenticates with its own individual credentials and temporary token, not a shared group account. Cloud SQL creates an individual database account on first login, so audit logs still show which account performed each action, and service-account workloads authenticate as the service account principal with only the roles bound to that account.
Choosing a Database Authentication Model
Database authentication verifies the identity of a user attempting to access databases, and Cloud SQL supports built-in, individual IAM, and group IAM models. Built-in authentication uses a stored username and password managed manually on each instance. IAM database authentication replaces passwords with short-lived tokens and requires SSL-encrypted traffic, with access managed centrally through IAM policies.
| Feature | Built-in database authentication | IAM database authentication (individual) | IAM group authentication |
|---|---|---|---|
| Authentication method | Password | Temporary authentication token | Temporary authentication token |
| Network traffic encryption | SSL not required | SSL required | SSL required |
| User management | Manual per user | Centralized through IAM | Centralized through IAM and Cloud Identity groups |
Choose individual IAM authentication when centralized control and short-lived tokens are needed for specific users or service accounts. Choose IAM group authentication when many users need the same access, because adding members to the group automatically grants login and database privileges without updating each account separately.
Key Facts
- Customer-managed encryption keys (CMEK) in Cloud Key Management Service (Cloud KMS) let customers control the key encryption keys that protect data, including protection level, location, rotation, permissions, and lifecycle.
- A disabled, destroyed, or unreachable CMEK key version blocks access to protected data within minutes to hours and causes automatic, unrecoverable deletion if it remains unavailable for more than 30 days.
- VPC Service Controls perimeters block movement of data from a protected service to resources outside the perimeter for all user and service account identities, while access levels only permit outside-to-inside requests that meet defined conditions.
- Identity and Access Management (IAM) grants permissions only through role bindings that connect a principal, a role, and a resource, following least privilege at the smallest effective scope.
- Cloud SQL IAM database authentication uses short-lived tokens with required SSL and centralized management, with group authentication adding automatic login and privilege inheritance through Cloud Identity groups.
Frequently Asked Questions
What is the difference between Google default encryption and Customer-managed encryption keys (CMEK) in Cloud Key Management Service (Cloud KMS)?
Google default encryption uses Google-owned and managed symmetric key encryption keys that protect customer content with no customer action, while Customer-managed encryption keys use customer-controlled keys in Cloud Key Management Service while access to the storage resource feels much the same. Customer-managed encryption keys use envelope encryption where the storage service calls Cloud Key Management Service to encrypt and decrypt its data encryption keys, giving control over protection level, location, rotation, permissions, and audit visibility while keeping normal storage access.
What happens to protected data when a Customer-managed encryption keys (CMEK) key version in Cloud Key Management Service (Cloud KMS) is disabled, destroyed, or unreachable?
Disabling or destroying the active key version makes the protected data inaccessible within minutes to a few hours, and the change can take up to 3 hours to fully take effect. If the key stays disabled, destroyed, or unreachable for more than 30 days, the encrypted data is automatically deleted and cannot be recovered, so keys in active use must remain enabled and accessible.
How do VPC Service Controls perimeters and access levels control movement of data to resources outside the perimeter?
VPC Service Controls perimeters allow data to flow only between protected projects and protected services inside the same perimeter and deny any API call that tries to move data from a protected service to a resource outside the perimeter for all user and service account identities. Access levels permit limited external access by defining conditions that only outside-to-inside requests must meet, while traffic from a protected resource inside the perimeter to the outside cannot be authorized by an access level and remains blocked.
How does Identity and Access Management (IAM) grant permissions to principals for Google Cloud storage resources?
Identity and Access Management grants permissions only through role bindings that connect a principal, a role, and a resource, so a principal receives all permissions contained in the role and the same principal can hold multiple roles. Bindings can apply at project, folder, instance, and repository levels with project-level bindings applying by default to all instances in the project, following least privilege by granting only the roles required at the smallest effective scope.
Sample Question
An enterprise organization is deploying a regional managed database and storage service on Google Cloud to handle sensitive customer workload data. Compliance regulations mandate that all data at rest must be protected using Customer-Managed Encryption Keys (CMEK) to ensure strict cryptographic sovereignty and organizational key lifecycle control.
You need to configure Cloud Key Management Service (Cloud KMS) and grant the necessary permissions so that the Google Cloud service can perform automated cryptographic operations on the underlying data.
Which set of actions should you take?
How learners score on this domain
Last updated