Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Using VPC Service Controls with Shared VPC
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise is designing a secure cloud architecture on Google Cloud across multiple projects. The architecture utilizes a Shared VPC where compute workloads deployed in a service project interact with managed Google Cloud APIs. The security team establishes the following requirements:
- Guard against data exfiltration by enforcing a VPC Service Controls perimeter around sensitive Google Cloud APIs.
- Ensure network communication between the Shared VPC host project and the service project is fully permitted without perimeter boundary violations.
- Allow authorized security administrators connecting from corporate public IP addresses to access and manage protected services via the Google Cloud console.
Which solution should you implement?
Explanations
Place both the Shared VPC host project and the service project within the same VPC Service Controls perimeter, create an Access Context Manager access level containing the corporate public IP ranges, and assign that access level to the perimeter.
Place both the Shared VPC host project and the service project within the same VPC Service Controls perimeter, create an Access Context Manager access level containing the corporate public IP ranges, and assign that access level to the perimeter.
What VPC Service Controls and Access Context Manager Are
VPC Service Controls establishes an isolation perimeter around Google Cloud resources to prevent unauthorized access and mitigate data exfiltration risks. Access Context Manager allows administrators to define fine-grained, context-aware access levels based on attributes such as client IP subnets, device policy, and user identity, which can then be bound directly to VPC Service Controls service perimeters.
How it Meets the Stated Requirements
- Preventing data exfiltration: Encapsulating sensitive projects and APIs within a VPC Service Controls service perimeter prevents data from being copied or exfiltrated to unauthorized storage locations or unauthorized multi-tenant services outside the perimeter.
- Shared VPC compatibility: Including both the Shared VPC host project and the service project in the exact same service perimeter ensures network interfaces, cross-project subnet bindings, and API requests between them do not cross perimeter boundaries, avoiding unexpected policy violations.
- Google Cloud console administration: Because the Google Cloud console operates over the public internet outside the perimeter boundary, defining an access level in Access Context Manager configured with the corporate public IP CIDR blocks and attaching it to the perimeter grants authorized personnel seamless console access to the protected services.
Shared VPC: Both Projects Inside One Perimeter
Set Relationship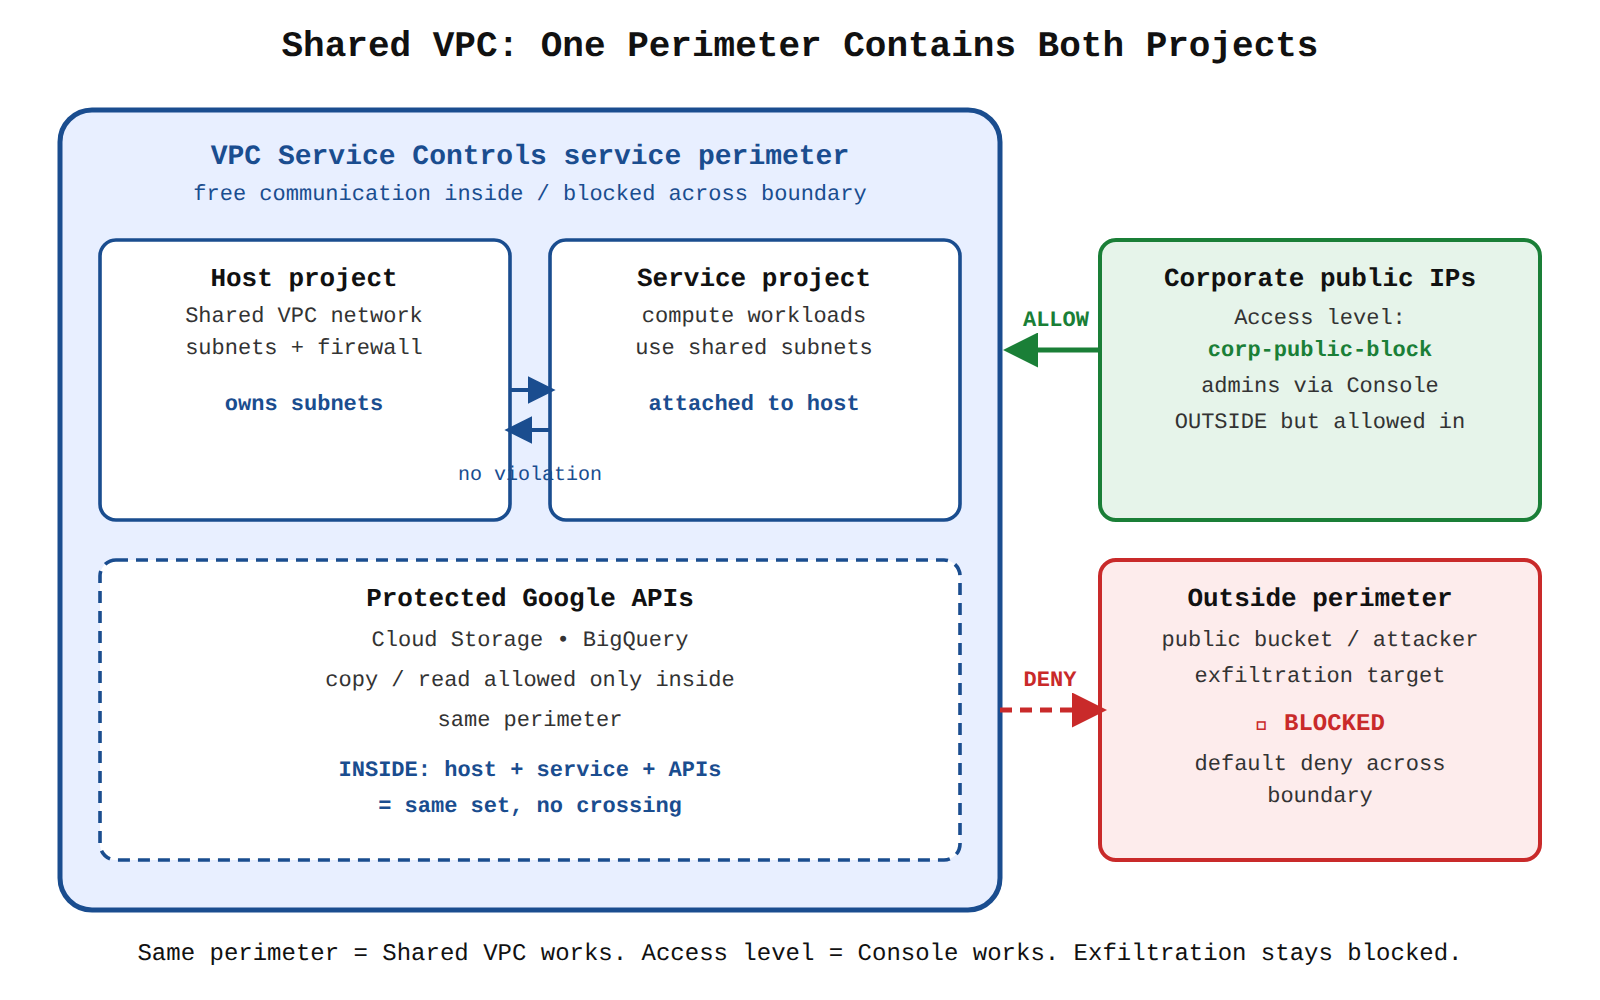
Key Advantages and Capabilities
- Unified perimeter defense: Restricts access to sensitive Google API endpoints (such as Cloud Storage and BigQuery) from unapproved networks and identities.
- Granular context evaluation: Enforces IP subnet and identity conditions without compromising private API security.
- Seamless Shared VPC integration: Prevents communication failures between network infrastructure admins and application developers.
- Multi-layered protection: Complements IAM permissions by placing network-level restrictions on API access.
Why This Is Optimal
This solution natively addresses both cross-project networking constraints in Shared VPC deployments and the operational requirement of console management from verified enterprise networks without weakening perimeter isolation.
Create separate VPC Service Controls perimeters for the host project and service project, deploy an external Application Load Balancer with Cloud Armor edge policies, and route console access through Cloud NAT.
Create separate VPC Service Controls perimeters for the host project and service project, deploy an external Application Load Balancer with Cloud Armor edge policies, and route console access through Cloud NAT.
What This Option Proposes
This approach places the Shared VPC host project and service project into distinct service perimeters, attempts to use Google Cloud Armor on an external load balancer to filter corporate traffic, and leverages Cloud NAT with Private Google Access for console administration.
Why It Doesn't Meet the Requirement
- Split perimeter complications: Splitting a Shared VPC across multiple distinct perimeters triggers ingress/egress blocks unless explicit, complex cross-perimeter bridge rules are established for every communicating resource and API.
- Google Cloud console over Private Google Access/NAT unsupported: Requests directed to the Google Cloud console originating from networks utilizing Private Google Access or Cloud NAT are not supported by VPC Service Controls and will be blocked.
- Misaligned Cloud Armor usage: Cloud Armor protects custom user applications hosted behind Google Cloud Load Balancing, but it cannot intercept or filter requests made directly to Google Cloud control plane APIs or the Google Cloud console.
Key Characteristics and Limitations
- Unnecessary perimeter segmentation: Dividing host and service projects creates administrative overhead and operational disruption.
- Cloud Armor scope: Cloud Armor operates at Layer 7 on external/internal load balancers and does not manage API access to Google services.
- Console limitation: Accessing the Cloud console from networks implicitly enabled by Cloud NAT/Private Google Access is explicitly blocked by VPC Service Controls.
This Answer Would Be Correct If
You were deploying an internet-facing custom web application behind an external HTTPS load balancer that required Layer 7 DDoS and IP filtering rules via Cloud Armor.
Place only the Shared VPC service project inside the perimeter, configure an Identity-Aware Proxy (IAP) TCP forwarding tunnel for Google Cloud console traffic, and rely on IAM conditions to govern the host project.
Place only the Shared VPC service project inside the perimeter, configure an Identity-Aware Proxy (IAP) TCP forwarding tunnel for Google Cloud console traffic, and rely on IAM conditions to govern the host project.
What This Option Proposes
This configuration attempts to isolate only the service project within a VPC Service Controls perimeter while leaving the Shared VPC host project outside, using Identity-Aware Proxy (IAP) TCP forwarding to tunnel Google Cloud console traffic.
Why It Doesn't Meet the Requirement
- Shared VPC perimeter violations: If the host project providing the network and the service project deploying workloads reside on opposite sides of a perimeter boundary, cross-project API calls and network operations will be blocked by VPC Service Controls.
- IAP cannot proxy the Cloud console: IAP TCP forwarding is specifically designed for tunneling administrative protocols like SSH (port 22) and RDP (port 3389) directly to Compute Engine VMs; it cannot be used to route or authenticate browser traffic directed to the public Google Cloud console interface.
Key Characteristics and Limitations
- Shared VPC boundary mismatch: Asymmetric perimeter assignments between host and service projects break private resource bindings.
- IAP scope: IAP protects HTTPS web applications and VM administrative ports, not the Google Cloud management control plane.
- IAM conditions insufficiency: IAM conditions do not provide data exfiltration protection against compromised credentials moving data to unapproved external resources.
This Answer Would Be Correct If
The requirement were strictly focused on establishing secure administrative shell (SSH/RDP) access to backend Compute Engine VMs without public IP addresses instead of securing Google Cloud API management via the console.
Place both projects in the service perimeter, enable Private Services Access, and configure VPC firewall rules matching the corporate IP addresses to permit Google Cloud console traffic.
Place both projects in the service perimeter, enable Private Services Access, and configure VPC firewall rules matching the corporate IP addresses to permit Google Cloud console traffic.
What This Option Proposes
This option places both projects in the service perimeter, configures Private Services Access, and attempts to use internal VPC firewall rules to allow external administrators to connect to the Google Cloud console.
Why It Doesn't Meet the Requirement
- VPC firewalls do not filter Cloud APIs or console traffic: VPC firewall rules filter network traffic entering or leaving VM instances (vNICs) within a VPC network. They have no visibility or control over Google Cloud control plane traffic or external browser connections to the Google Cloud console.
- Console requests will be blocked: Without an access level configured in Access Context Manager, any attempt to access protected APIs via the console from outside the perimeter will be blocked by default with a perimeter violation error.
Key Characteristics and Limitations
- Per-VM enforcement: VPC firewalls operate at Layer 3/4 on virtual machine interfaces, not at the API management perimeter.
- VPC Service Controls evaluation: VPC Service Controls evaluates API requests independently of VPC firewall state.
- Private Services Access role: Private Services Access is designed for internal peering with managed service producer networks (like Cloud SQL), not for managing console access.
This Answer Would Be Correct If
The primary goal was filtering internal network traffic between Compute Engine virtual machines and internal subnets within the Shared VPC network.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Folder IAM Admin Role
Security and compliance
IntermediateProfessional Cloud Architect
Compute Engine Incident Response Procedure
Understanding the principles and recommendations of the operational excellence pillar of the Google Cloud Well-Architected Framework
IntermediateProfessional Cloud Architect
Cloud Build Provenance with Artifact Analysis
Deployment and release management
IntermediateProfessional Cloud Architect
Cloud Pub/Sub vs Self-Managed Messaging
Decision-making processes
IntermediateProfessional Cloud Architect
Uniform Bucket-Level Access
Security and access management
FundamentalGenerative AI Leader
Vertex AI Managed ML Infrastructure
Infrastructure
Last updated