Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Least Privilege Cloud Build Pipelines with Artifact Analysis
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise organization is designing an automated CI/CD pipeline in Google Cloud to build and manage container images across staging and production environments. The cloud architecture and security teams have established the following requirements:
- Build executions must adhere to the principle of least privilege rather than relying on default broad project permissions.
- The build process must be standardized and reusable across environments using a single build configuration file.
- Build artifacts must be versioned, stored securely, and automatically analyzed for vulnerabilities.
- The pipeline must generate verifiable build provenance metadata for software supply chain compliance.
Which solution should the cloud architect implement?
Explanations
Configure Cloud Build triggers with user-specified service accounts granted scoped IAM roles, define parameterized substitutions in cloudbuild.yaml, push images to Artifact Registry, and enable Artifact Analysis for vulnerability scanning and build provenance.
Configure Cloud Build triggers with user-specified service accounts granted scoped IAM roles, define parameterized substitutions in cloudbuild.yaml, push images to Artifact Registry, and enable Artifact Analysis for vulnerability scanning and build provenance.
What the Solution Is
This architecture leverages Google Cloud Build triggers configured with dedicated user-specified service accounts, parameterized build substitutions, and Google Cloud Artifact Registry integrated with Artifact Analysis for end-to-end supply chain security.
How It Meets the Requirements
- Principle of least privilege: By configuring triggers with dedicated user-specified service accounts and assigning granular roles (such as
roles/artifactregistry.writerandroles/logging.logWriter), you prevent builds from executing with broad default project-level permissions. - Standardized and reusable pipelines: Using Cloud Build's built-in default substitutions (like
$PROJECT_ID) and user-defined substitutions (such as${_LOCATION}and${_REPOSITORY}) in a singlecloudbuild.yamlallows the exact same build template to deploy across staging and production environments dynamically. - Secure versioning and vulnerability scanning: Pushing container images directly to Artifact Registry enables centralized, versioned package management, while Artifact Analysis automatically scans images for common vulnerabilities and exposures (CVEs).
- Supply chain security & provenance: Cloud Build automatically records non-falsifiable build provenance (compliant with SLSA standards) and security insights into Artifact Analysis, providing verifiable audit trails of the source, toolchain, and artifact digests.
Secure Build-to-Scan Pipeline Flow
Process Flow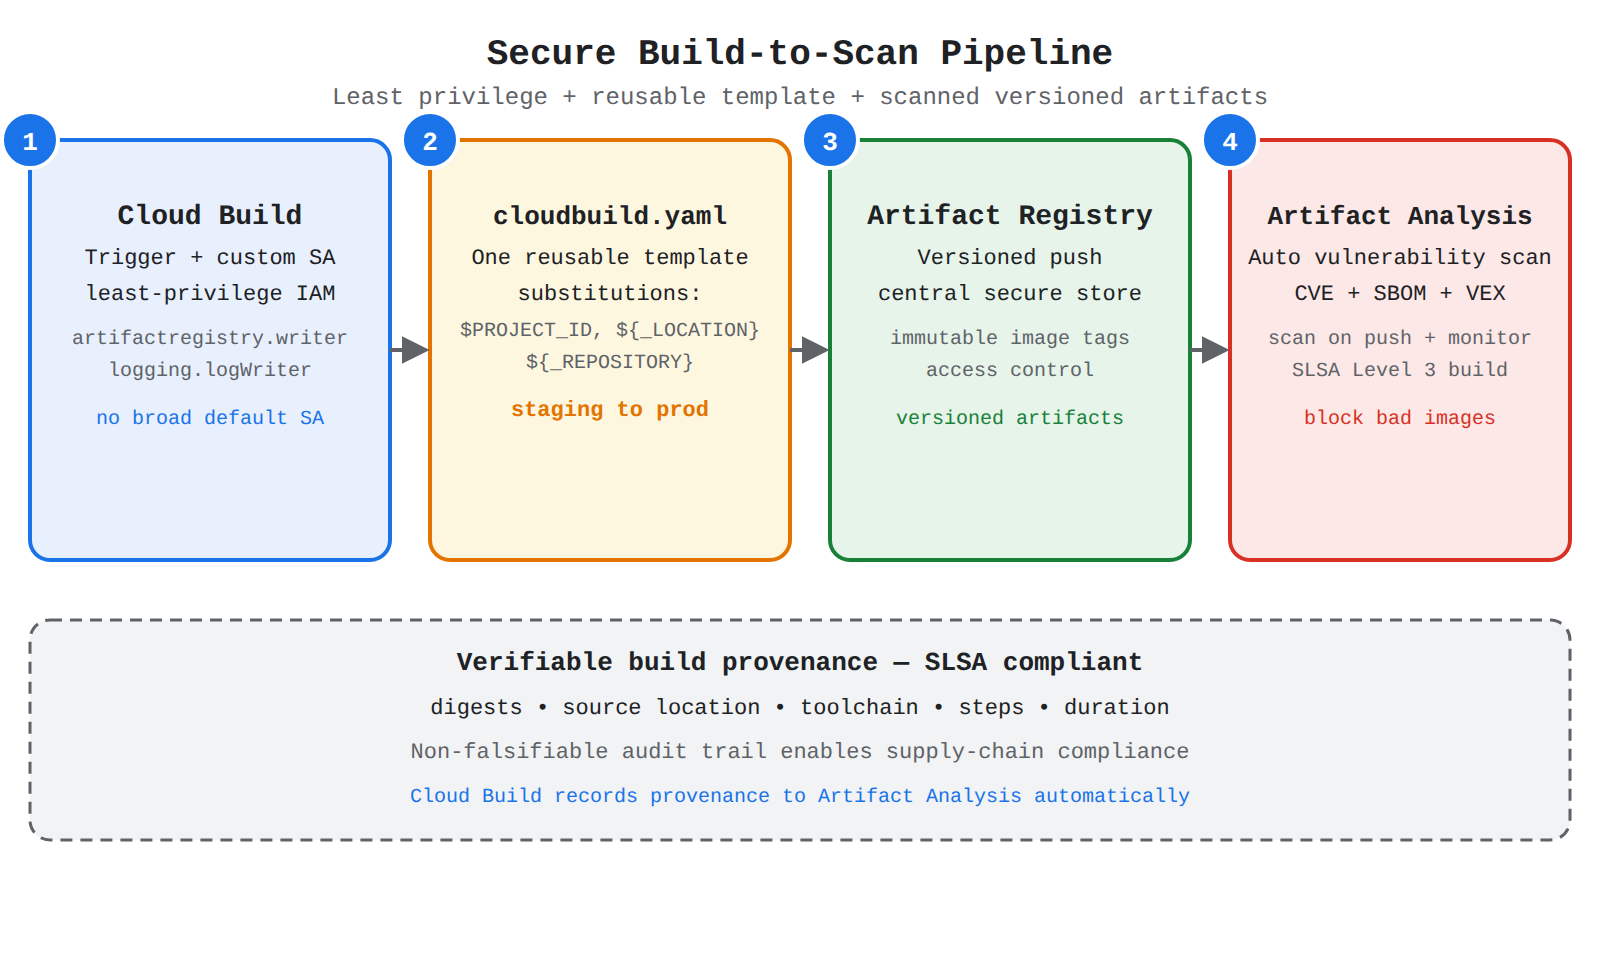
Key Advantages
- Granular Access Control: Isolates build permissions per project or pipeline phase.
- Automated Security Gates: Proactively surfaces dependency vulnerabilities and software bill of materials (SBOM) data.
- Maintainable CI/CD Templates: Reduces configuration drift across multi-environment deployments.
- Native SLSA Provenance: Ensures compliance with enterprise software supply chain security standards.
Why This Is Optimal
Native integration between Cloud Build, Artifact Registry, and Artifact Analysis provides fully managed, serverless, and hardened CI/CD execution without needing third-party plugins or managing underlying build runner infrastructure.
Generate long-lived JSON service account keys, store them in the source Git repository, execute builds using local Docker daemons, and push images to Google Cloud Storage buckets.
Generate long-lived JSON service account keys, store them in the source Git repository, execute builds using local Docker daemons, and push images to Google Cloud Storage buckets.
What the Option Is
This approach relies on downloading static service account JSON keys, storing them inside version control repositories, building container images locally or on unmanaged VM hosts, and using Cloud Storage buckets as an image repository.
Why It Doesn't Meet the Requirement
- Severe Security Risk: Storing long-lived service account keys in source control repositories creates major credential leak and exfiltration risks.
- Missing Artifact Registry Features: Cloud Storage buckets lack native container registry capabilities, OCI format specifications, package management features, and automated container vulnerability scanning provided by Artifact Registry.
- No Automated Provenance: Local Docker builds do not automatically generate non-falsifiable SLSA-compliant build provenance metadata verified by Google Cloud.
Key Limitations
- Service account keys represent long-lived credentials that violate modern zero-trust and least-privilege standards.
- Standard Cloud Storage buckets cannot act as native package managers for Docker, npm, or Java packages.
- Vulnerability scanning with Artifact Analysis cannot be natively integrated into plain Cloud Storage buckets.
This Answer Would Be Correct If
You were archiving raw uncompiled code archives for disaster recovery backup rather than establishing a modern container CI/CD pipeline.
Configure Cloud Deploy to compile application source code and generate containers, push built artifacts to an Artifact Registry remote repository pointing to Docker Hub, and disable vulnerability scanning.
Configure Cloud Deploy to compile application source code and generate containers, push built artifacts to an Artifact Registry remote repository pointing to Docker Hub, and disable vulnerability scanning.
What the Option Is
This option proposes using Cloud Deploy as the build engine, storing build outputs in an Artifact Registry remote repository configured with upstream caching, and disabling vulnerability scanning.
Why It Doesn't Meet the Requirement
- Wrong Tool Responsibility: Cloud Deploy is a continuous delivery service designed to automate release progression across environments (such as GKE or Cloud Run), not a build tool that compiles source code or builds container images.
- Misuse of Remote Repositories: Artifact Registry remote repositories serve as caching proxies for external upstream registries (such as Docker Hub or PyPI), rather than private standard repositories for hosting internal proprietary build outputs.
- Fails Security Mandates: Disabling vulnerability scanning and bypassing Cloud Build's automated build provenance directly violates software supply chain security standards.
Key Limitations
- Cloud Deploy requires pre-built artifacts/manifests and cannot execute Docker build steps directly.
- Remote repositories in Artifact Registry are read-only caches for external package registries.
- Omitting vulnerability scanning leaves deployed containers vulnerable to known vulnerabilities.
This Answer Would Be Correct If
The primary goal was to cache open-source public images from Docker Hub in a local region to improve pull latency and availability.
Use the default Cloud Build service account with Project Editor permissions, create environment-specific static cloudbuild.yaml files, push images to Artifact Registry, and use Cloud Workstations to manually verify image digests.
Use the default Cloud Build service account with Project Editor permissions, create environment-specific static cloudbuild.yaml files, push images to Artifact Registry, and use Cloud Workstations to manually verify image digests.
What the Option Is
This option uses the legacy default Cloud Build service account with broad privileges across the project, hardcoded configuration files per environment, and manual checks inside Cloud Workstations.
Why It Doesn't Meet the Requirement
- Violates Least Privilege: The default Cloud Build service account historically receives wide permissions (or granting
roles/editor) that are unnecessarily broad, violating least-privilege principles. - Redundant Maintenance: Creating static
cloudbuild.yamlfiles for each separate environment introduces configuration duplication and maintenance overhead rather than reusing parameterized templates via substitutions. - Manual vs. Automated Provenance: Cloud Workstations provides developer workspaces, but manual verification does not satisfy automated, non-falsifiable build provenance requirements or automated vulnerability scanning.
Key Limitations
- Over-permissioned service accounts create substantial lateral movement security risks.
- Hardcoding repository names and project identifiers reduces pipeline portability.
- Lacks automated vulnerability scanning and automated compliance attestations.
This Answer Would Be Correct If
The organization had a requirement to conduct ad-hoc, interactive debugging within cloud-hosted IDEs rather than an automated, unattended CI/CD pipeline.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Cloud Deploy Skaffold deploy.statusCheck
Deployment and release management
IntermediateProfessional Cloud Architect
Canary Deployment
Deployment and release management
IntermediateProfessional Cloud Architect
Cloud Functions vs Cloud Run
Serverless computing
IntermediateProfessional Cloud Architect
IAM Recommender Role Recommendations
Identity and Access Management (IAM)
IntermediateProfessional Cloud Architect
Cloud Run Serverless Containers
Design decision trade-offs
AdvancedProfessional Cloud Security Engineer
Uniform Bucket-Level Access Migration
Managing IAM and access control list (ACL) permissions.
Last updated