Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Compromised Compute Engine VM Recovery Steps
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
A financial services organization running critical workloads on Google Cloud receives a high-severity Security Command Center threat finding indicating that an unauthorized binary executed on a production Compute Engine virtual machine (VM).
To adhere to operational excellence and incident response frameworks, the team must rapidly mitigate the immediate threat, preserve forensic evidence for root-cause analysis, and restore service operations.
Which sequence of actions should the cloud architect recommend?
Explanations
Keep the compromised VM running and exposed to allow live system debugging, and assign full administrative permissions to the investigation team.
Keep the compromised VM running and exposed to allow live system debugging, and assign full administrative permissions to the investigation team.
What this option is
This strategy involves leaving an actively compromised virtual machine in its running, network-accessible state while engineers perform real-time interactive troubleshooting on the live production instance.
Why it doesn't meet the requirement
- Fails Containment: Leaving the instance running and connected allows active malware or external adversaries to exfiltrate sensitive financial data, execute remote commands, or pivot laterally to other cloud resources.
- Contaminates Evidence: Performing ad-hoc commands on a live compromised machine alters file timestamps, modifies memory spaces, and invalidates forensic integrity.
- Violates Principle of Least Privilege: Granting broad administrative permissions during an emergency bypasses change management and increases operational risk.
Key limitations
- Exposes adjacent Google Cloud VPC resources to lateral movement.
- Fails to halt ongoing denial-of-service, data destruction, or reconnaissance activities.
- Complicates timeline reconstruction during post-mortem reviews.
This answer would be correct if
The system were inside an isolated honeypot environment specifically instrumented for threat intelligence research rather than an active production workload.
Stop the compromised VM instance, create snapshots of the persistent disks for forensic analysis, deploy a replacement instance from a verified image, and examine Cloud Audit Logs during the post-mortem.
Stop the compromised VM instance, create snapshots of the persistent disks for forensic analysis, deploy a replacement instance from a verified image, and examine Cloud Audit Logs during the post-mortem.
What this incident response approach is
This workflow follows established incident response frameworks and Google Cloud operational excellence principles. It isolates the compromised resource to halt the ongoing threat, captures point-in-time evidence for forensic investigation, restores service availability, and leverages telemetry to analyze root cause during a blameless post-mortem.
Contain, Preserve, Restore, Learn Workflow
Process Flow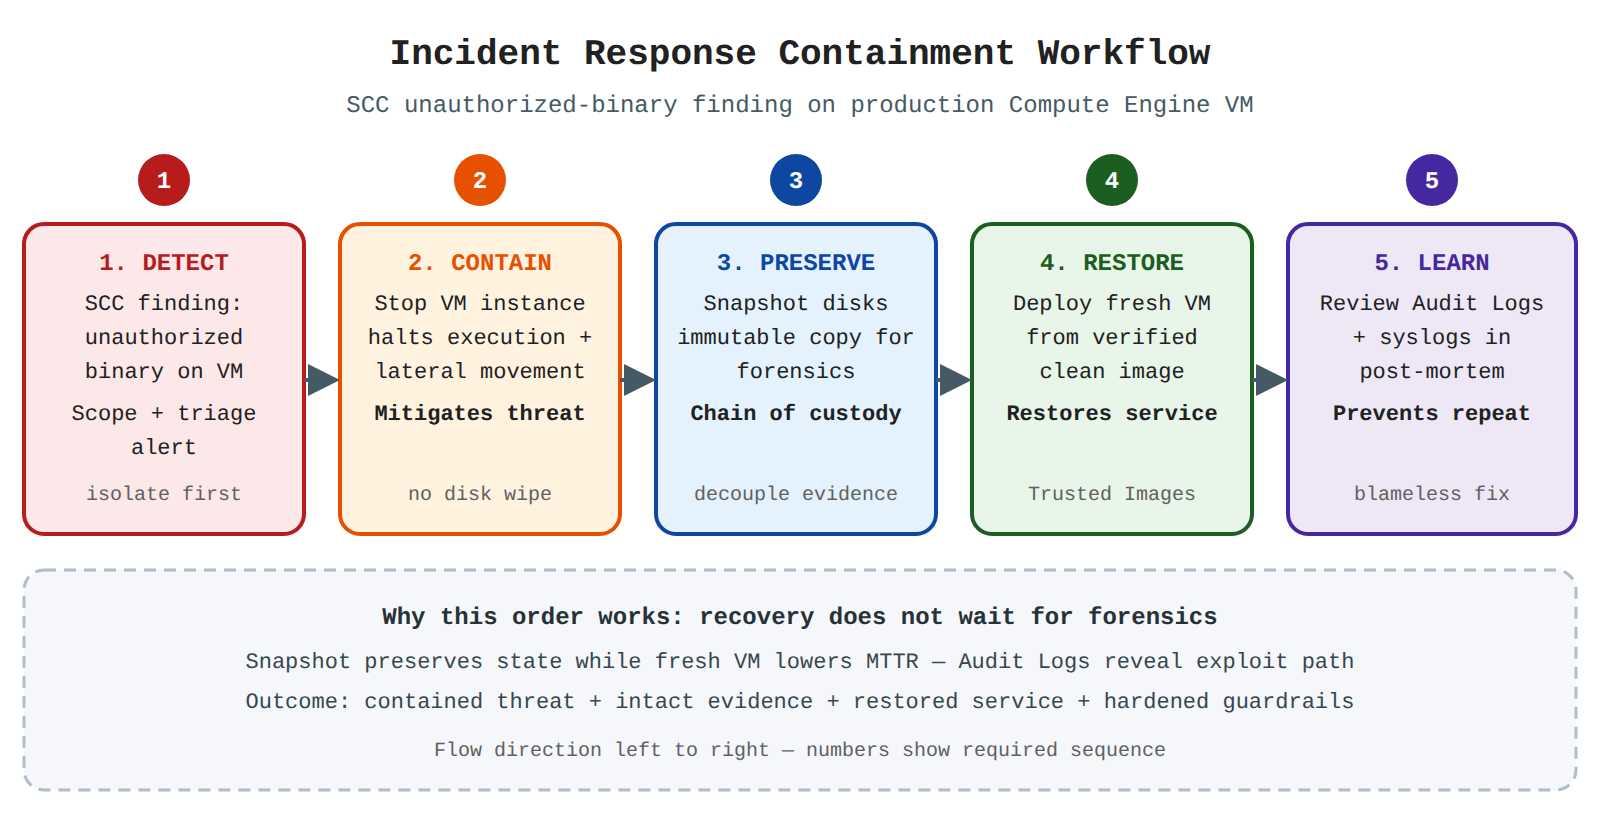
How it meets the operational requirements
- Immediate Threat Mitigation: Stopping the compromised Compute Engine instance cuts off active malicious execution and network lateral movement without losing volatile disk state.
- Forensic Evidence Preservation: Taking snapshots of the attached persistent disks preserves an uncorrupted copy of the file system, binaries, and system logs for deep forensic investigation without delaying workload recovery.
- Service Restoration: Deploying a fresh instance from a verified, known-clean image quickly restores operational availability while isolating the affected environment.
- Continuous Improvement: Reviewing Cloud Audit Logs and system logs during the post-mortem identifies how the vulnerability was exploited, driving preventative policies like Trusted Images and perimeter guardrails.
Key advantages
- Minimizes Mean Time to Recovery (MTTR) by decoupling evidence collection from workload restoration.
- Maintains chain of custody by preserving disk states via immutable snapshots.
- Prevents recurring failures by analyzing audit trails to patch root vulnerabilities.
- Aligns with blameless post-mortem practices focused on system design fixes rather than individual blame.
Why this is optimal
This approach cleanly balances security containment, continuous operational availability, and data-driven root cause analysis, preventing future incidents while restoring production systems.
Immediately delete the compromised VM instance and its attached disks, then redeploy the workload using the latest automated unverified build.
Immediately delete the compromised VM instance and its attached disks, then redeploy the workload using the latest automated unverified build.
What this option is
This option attempts rapid containment by permanently deleting the affected Compute Engine instance and all attached storage immediately upon receiving the threat finding.
Why it doesn't meet the requirement
- Destroys Forensic Evidence: Deleting the persistent disks before capturing snapshots eliminates critical digital evidence, including attacker artifacts, malware binaries, and local operating system event logs needed for a proper post-mortem.
- Risks Immediate Re-infection: Redeploying from an automated build without analyzing how the breach occurred or verifying image provenance can redeploy the same vulnerability into production.
- Fails Continuous Improvement: Without forensic data, the engineering team cannot conduct an effective root-cause analysis to mitigate future risks.
Key limitations
- Prevents deep forensic analysis by wiping non-volatile memory and disk state.
- Violates incident response frameworks that mandate evidence preservation.
- Lacks verification controls like Binary Authorization or Trusted Images.
This answer would be correct if
The workload were strictly ephemeral, completely stateless, and the organization had already determined the exact vector of compromise through separate external telemetry.
Modify the instance's OS login credentials while leaving the VM running, and disable VPC firewall rules to prevent remote connectivity drops.
Modify the instance's OS login credentials while leaving the VM running, and disable VPC firewall rules to prevent remote connectivity drops.
What this option is
This response attempts to remediate the incident by resetting operating system credentials in-place while keeping the virtual machine active and loosening firewall restrictions to maintain administrative access.
Why it doesn't meet the requirement
- Incomplete Remediation: Resetting credentials does not terminate active malicious processes, unauthorized kernel modules, or memory-resident backdoors already executing on the machine.
- Weakens Network Security: Disabling firewall rules increases the attack surface rather than restricting outbound command-and-control channels or ingress scanning.
- Prolongs Operational Disruption: In-place remediation on a live compromised system is error-prone and does not provide high confidence of clean operational state compared to replacement.
Key limitations
- Leaves persistence mechanisms (such as cron jobs or modified binaries) intact.
- Fails to leverage immutable snapshots for forensic analysis.
- Does not integrate audit logging or post-mortem learning into future operational safeguards.
This answer would be correct if
The threat finding was confirmed to be a false alarm caused solely by an expired user password or standard administrative credential rotation.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Cloud Build with Kubernetes Engine Developer Role
Understanding the principles and recommendations of the operational excellence pillar of the Google Cloud Well-Architected Framework
IntermediateProfessional Cloud Architect
Windows-Based SLI vs Request-Based SLI
Understanding the principles and recommendations of the operational excellence pillar of the Google Cloud Well-Architected Framework
IntermediateProfessional Cloud Architect
Exponential Backoff with Jitter and Partial Responses
Accessing Google API best practices
IntermediateProfessional Cloud Architect
Apigee Adapter for Envoy
Supporting the application design
IntermediateProfessional Cloud Architect
Cloud Storage Bucket Lock Object Legal Holds
Data retention and data lifecycle management
AdvancedProfessional Data Engineer
BigQuery ML Remote Models with Vertex AI
AI data enrichment
Last updated