Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Private Google Access with Perimeter Data Protection
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An organization hosts a data-processing workload on Compute Engine instances that have only internal RFC 1918 IP addresses and no access to the public internet. The application running on these instances needs to interact programmatically with BigQuery and Cloud Storage APIs to analyze and store sensitive corporate data.
Security requirements dictate that:
- Compute Engine workloads must reach Google APIs securely without traversing the public internet or requiring external IP addresses.
- Data exfiltration must be strictly prevented, ensuring authorized service accounts cannot copy or export data to storage buckets or datasets residing in unauthorized external Google Cloud projects.
Which combination of architectural controls should you implement to satisfy these requirements?
Explanations
Assign external IP addresses to all instances, enforce strict egress VPC firewall rules blocking non-Google IP ranges, and implement Customer-Managed Encryption Keys (CMEK).
Assign external IP addresses to all instances, enforce strict egress VPC firewall rules blocking non-Google IP ranges, and implement Customer-Managed Encryption Keys (CMEK).
What external IPs, egress firewall rules, and CMEK do
Assigning external IP addresses directly exposes instances to the internet routing table. VPC egress firewall rules filter outbound packets based on destination CIDR IP ranges, protocols, and ports. Customer-Managed Encryption Keys (CMEK) with Cloud KMS allow organizations to control cryptographic keys used to encrypt data at rest.
Why it doesn't meet the requirements
- Violates private networking requirements: Assigning external IPs contradicts the explicit requirement to avoid public IPs and keep instances isolated without public internet routing.
- Ineffective against data exfiltration: VPC firewall rules operate at Layer 3/Layer 4 (IP/port). Because valid Google APIs share common IP ranges, a firewall rule allowing traffic to Google IPs allows connections to any Google Cloud project's storage bucket or BigQuery dataset, failing to stop exfiltration.
- CMEK does not stop authorized read-and-export: While CMEK secures data at rest, an identity that has read access to decrypted data can still transmit that data out to an external destination if no perimeter boundaries exist.
Key characteristics and limitations
- External IP addresses increase attack surface and require public IP management.
- VPC firewalls cannot inspect API request payloads or distinguish between different project destinations within Google APIs.
- CMEK protects data confidentiality at rest but does not restrict API destinations.
This answer would be correct if
The primary requirement was meeting regulatory cryptographic governance for data at rest using keys managed in Cloud KMS, while instances were allowed direct public network interfaces.
Enable Private Google Access on the subnet hosting the Compute Engine instances, and create a VPC Service Controls service perimeter enclosing the project and its BigQuery and Cloud Storage resources.
Enable Private Google Access on the subnet hosting the Compute Engine instances, and create a VPC Service Controls service perimeter enclosing the project and its BigQuery and Cloud Storage resources.
What Private Google Access and VPC Service Controls are
Private Google Access allows virtual machine (VM) instances that have only internal (private) IP addresses to privately connect to the public IP addresses and endpoints of Google APIs and services without requiring external IPv4 addresses. VPC Service Controls allows security architects to define fine-grained security perimeters around Google Cloud resources (such as Cloud Storage and BigQuery) to isolate sensitive services and prevent unauthorized data egress across organizational boundaries.
How it meets the requirements
- No external IPs / Internal connectivity: Enabling Private Google Access on the subnet ensures VM instances without external IP addresses can route API calls to BigQuery and Cloud Storage over Google's internal network backbone without needing external IP addresses or NAT gateways.
- Preventing data exfiltration: Placing the project and resources inside a VPC Service Controls perimeter ensures that even if credentials or service accounts are compromised, API calls attempting to move data to external buckets or BigQuery datasets outside the defined perimeter are blocked at the perimeter edge.
VPC SC Perimeter Blocks Data Exfiltration
System Architecture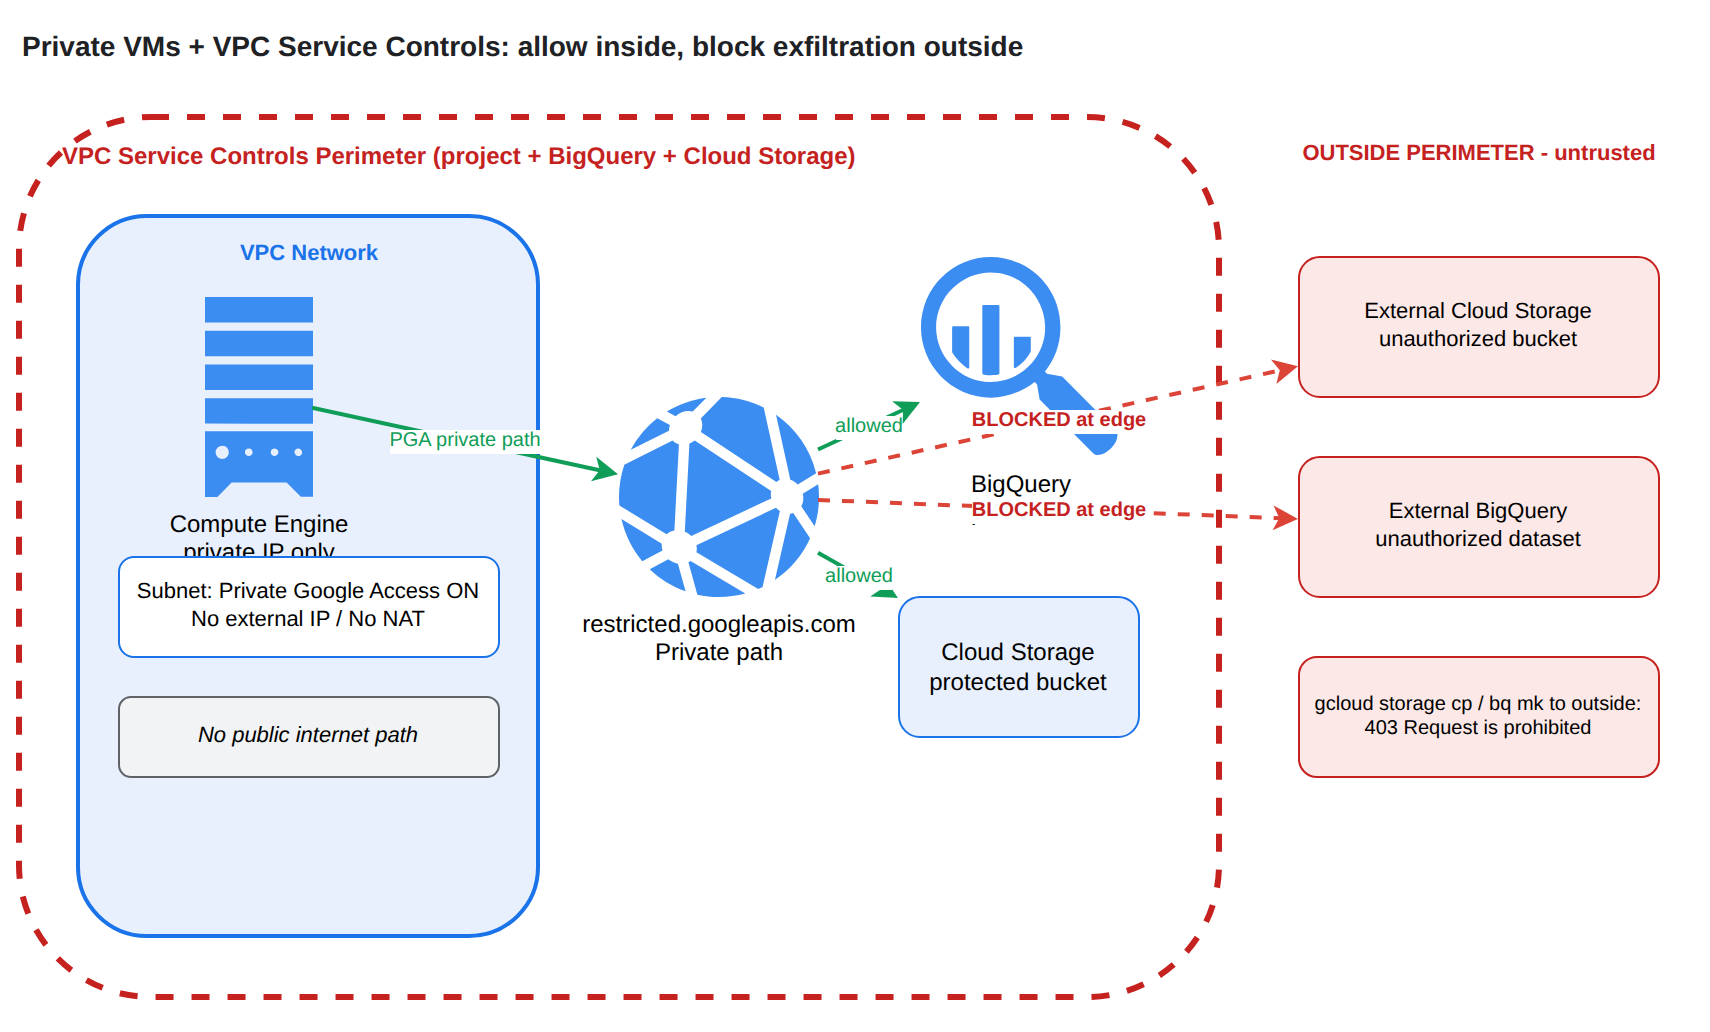
Key advantages and capabilities
- Internal network routing: Keeps all API communication strictly within Google's high-performance internal network infrastructure.
- Context-aware boundary defense: Enforces perimeter boundaries independent of Identity and Access Management (IAM) permissions, mitigating insider threat and credential theft risks.
- Zero public internet exposure: Completely removes the requirement for public IPv4 assignments or internet egress paths on compute instances interacting with Google APIs.
- Granular API restriction: Restricts API calls to specified services like
bigquery.googleapis.comandstorage.googleapis.comwithin protected projects.
Why this is optimal
This approach directly addresses both network egress constraints and perimeter data exfiltration risks. IAM permissions govern identity-based authorization, while Private Google Access and VPC Service Controls provide the required network isolation and perimeter boundaries to stop data movement to untrusted external projects.
Deploy Cloud NAT on the VPC network to provide outbound internet access for the instances, and configure Identity-Aware Proxy (IAP) on BigQuery and Cloud Storage.
Deploy Cloud NAT on the VPC network to provide outbound internet access for the instances, and configure Identity-Aware Proxy (IAP) on BigQuery and Cloud Storage.
What Cloud NAT and Identity-Aware Proxy do
Cloud NAT (Network Address Translation) allows Google Cloud instances without external IP addresses to initiate outbound connections to the internet, translating private IPs to shared external IPs. Identity-Aware Proxy (IAP) provides context-aware identity and access control for web applications and VMs accessed via HTTPS and SSH/TCP, typically fronted by Cloud Load Balancing.
Why it doesn't meet the requirements
- Fails data exfiltration controls: Cloud NAT allows instances to make outbound requests to any public endpoint on the internet, including arbitrary external Google Cloud projects, providing no boundary enforcement against data exfiltration.
- Misapplied technology: IAP cannot be attached directly to Google-managed multi-tenant APIs like BigQuery and Cloud Storage; it is designed for user access to application frontends, Compute Engine instances, or GKE ingress services.
- Violates private access best practices: Routing Google API traffic through Cloud NAT exposes traffic to generic outbound NAT egress rather than leveraging private, internal Google API routing.
Key characteristics and limitations
- Cloud NAT manages outbound internet translation but does not provide API-level or perimeter-level exfiltration security.
- IAP verifies identity for application ingress rather than restricting destination endpoints for programmatic API egress.
- Lacks the boundary protections required to prevent copying data to external buckets.
This answer would be correct if
The goal was to allow private VMs to download third-party software updates from public repositories over the internet while securing administrative HTTPS/SSH access into custom enterprise applications.
Configure VPC Network Peering directly to the Google APIs VPC network, and enforce the Domain Restricted Sharing organization policy constraint on the organization.
Configure VPC Network Peering directly to the Google APIs VPC network, and enforce the Domain Restricted Sharing organization policy constraint on the organization.
What VPC Network Peering and Domain Restricted Sharing do
VPC Network Peering connects two Virtual Private Cloud networks together to route private RFC 1918 traffic between them. Domain Restricted Sharing (constraints/iam.allowedPolicyMemberDomains) is an organization policy constraint that restricts IAM role bindings to specific allowed identity domains (such as a corporate Google Workspace account).
Why it doesn't meet the requirements
- Invalid network architecture: Google APIs are multi-tenant services accessed via internal VIPs/endpoints (Private Google Access, Private Service Connect), not by creating direct VPC Network Peering to a proprietary "Google APIs VPC".
- Incomplete exfiltration protection: Domain Restricted Sharing prevents adding external user identities to your project's IAM policies, but it does not prevent an internal workload with valid credentials from sending data to an existing public/external bucket owned by a third party outside the organization.
- Fails API perimeter controls: It does not establish a network perimeter or service boundary around the specific Google Cloud resources.
Key characteristics and limitations
- VPC Network Peering cannot be directly targeted to multi-tenant Google API infrastructure without supported Private Service Connect or Private Services Access workflows.
- Domain Restricted Sharing governs who can be granted IAM roles in resource policies, not where outbound API network traffic can deliver data.
- Lacks context-aware perimeter enforcement.
This answer would be correct if
The primary goal was to prevent project administrators from accidentally granting IAM roles on company projects to external Google accounts (e.g., @gmail.com users).
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Exponential Backoff with Jitter and Partial Responses
Accessing Google API best practices
IntermediateProfessional Cloud Architect
Google Cloud Application Default Credentials
Accessing Google API best practices
IntermediateProfessional Cloud Architect
Cloud Logging Sinks and Logs-Based Metrics
Observability
IntermediateProfessional Cloud Architect
Project IAM Admin Separation of Duties
Separation of duties
IntermediateProfessional Cloud Architect
Cloud Storage Bucket Lock Object Legal Holds
Data retention and data lifecycle management
AdvancedProfessional Data Engineer
VPC Global Dynamic Routing Mode
Networking fundamentals
Last updated