Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Using Application Default Credentials Across Environments
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise development team is building a microservices application that interacts programmatically with Google Cloud APIs, including BigQuery and Cloud Storage. The application codebase is deployed across multiple environments: developer workstations for local testing, Compute Engine instances for staging, and Google Kubernetes Engine (GKE) clusters for production.
The security architecture requires eliminating the risks associated with downloadable, long-lived service account keys and ensuring least privilege access across each deployment tier without code changes.
Which identity and authentication strategy should the team implement?
Explanations
Grant service agent roles directly to user accounts and compute instances, and enable default project-wide API access scopes across all environments.
Grant service agent roles directly to user accounts and compute instances, and enable default project-wide API access scopes across all environments.
What Service Agent Roles and Access Scopes Are
Service agent roles (such as roles/bigquery.serviceAgent or roles/container.serviceAgent) are specialized IAM roles designed exclusively for Google-managed internal service accounts to coordinate service-to-service operations. Access scopes are legacy mechanisms used on Compute Engine to limit API token capabilities for the default Compute Engine service account.
Why It Doesn't Meet the Requirement
- Misuse of Service Agent Roles: Google Cloud explicitly warns against granting service agent roles to user accounts, developer groups, or custom compute instances. Service agent roles contain internal permissions that can cause unintended privilege escalation or system instability.
- Fails Automated Discovery: Access scopes and service agent roles do not configure identity discovery for local developer environments.
- Violates Least Privilege: Project-wide default access scopes provide broad, coarse-grained access rather than granular, role-based access tailored to specific microservices.
Key Characteristics and Limitations
- Reserved for System Agents: Service agent roles are calibrated specifically for Google internal daemon processes and automated service controllers.
- Legacy Control Mechanism: Access scopes act as a legacy ceiling filter and do not replace fine-grained Cloud IAM policies on modern compute runtimes.
- No Pod-Level Isolation: Compute-level scopes apply uniformly to all workloads running on a host, failing multi-tenant container isolation requirements in GKE.
This Answer Would Be Correct If
You were configuring internal Google Cloud service-to-service orchestration where the platform automatically provisions and manages the service agent principal.
Configure the application to use Application Default Credentials (ADC) via official client libraries, using user credentials via gcloud auth application-default login locally, attached IAM service accounts on Compute Engine, and Workload Identity on GKE.
Configure the application to use Application Default Credentials (ADC) via official client libraries, using user credentials via gcloud auth application-default login locally, attached IAM service accounts on Compute Engine, and Workload Identity on GKE.
What Application Default Credentials (ADC) and Runtime Identities Are
Application Default Credentials (ADC) is a flexible authentication mechanism provided by Google Cloud client libraries that automatically detects credentials based on the application's runtime environment. Instead of requiring hardcoded paths or static tokens, ADC searches a predefined order of locations—such as local user configuration, environment variables, or platform metadata services—to seamlessly acquire short-lived OAuth 2.0 access tokens.
How it Meets the Stated Requirements
- No Long-Lived Service Account Keys: Eliminates the need to create, download, or rotate JSON service account private keys. Tokens are generated dynamically and are short-lived.
- Automated Discovery Across Environments: The application code calls standard client library constructors (
StorageClient(),BigQueryClient()), which transparently invoke ADC across developer machines, VMs, and Kubernetes pods. - Least Privilege and Environment Separation: Developers authenticate using their individual Google accounts via
gcloud auth application-default loginwith bounded developer roles, Compute Engine VMs use attached service accounts via the instance metadata server, and GKE workloads leverage Workload Identity to bind Kubernetes Service Accounts (KSAs) to specific Google Service Accounts (GSAs).
ADC Discovers Identity Across Local, VM, GKE
System Architecture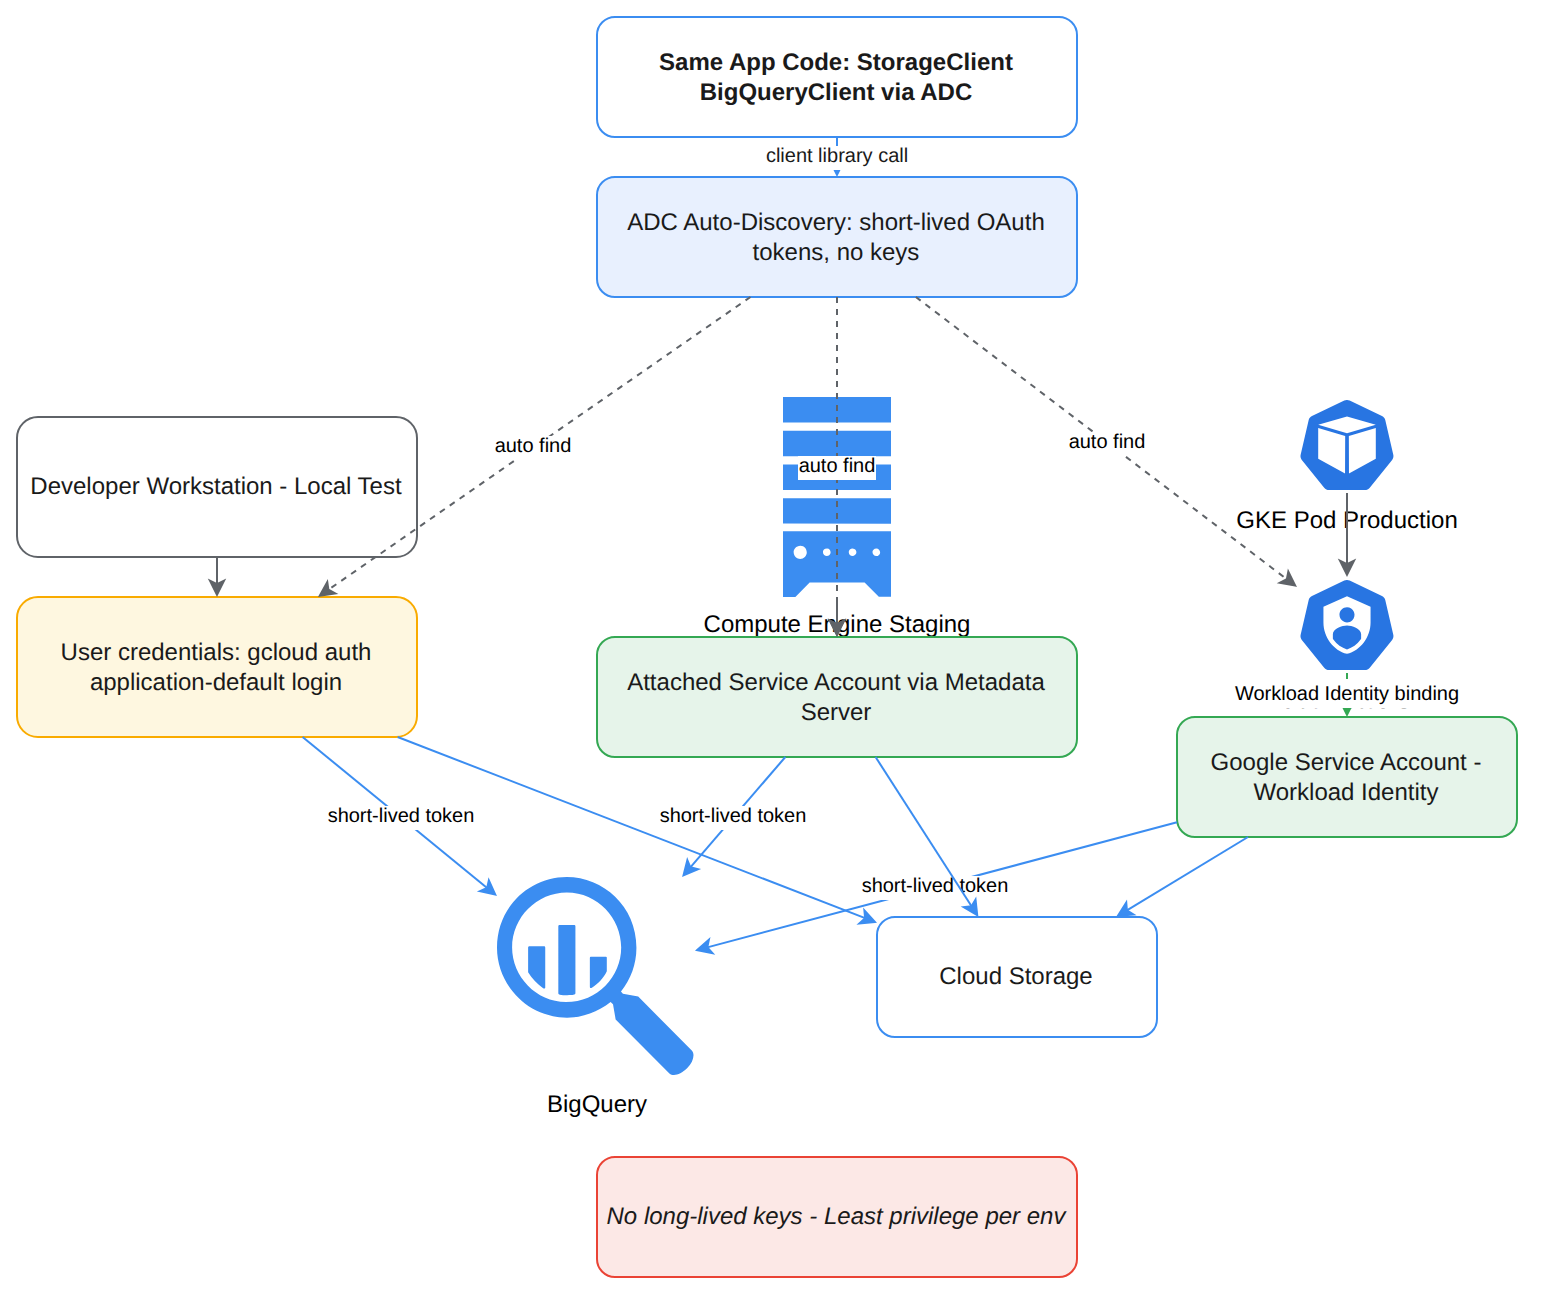
Key Advantages and Capabilities
- Unified Codebase: The application code remains identical across development, staging, and production environments.
- Reduced Blast Radius: Short-lived tokens minimize the window of opportunity if credentials are intercepted.
- Granular IAM Scoping: Enables distinct IAM roles for each individual microservice rather than sharing overly broad project-level credentials.
- Seamless Key Rotation: Cryptographic key rotation is completely managed under the hood by Google Cloud infrastructure.
Why This Is Optimal
ADC combined with platform-native identity binding (Compute Engine metadata service and GKE Workload Identity) adheres directly to Google Cloud security best practices. It avoids secret leakage vectors associated with static files while automating credential discovery and token refresh lifecycles without developer intervention.
Embed OAuth 2.0 refresh tokens directly inside application container images and deploy an internal token-vending proxy to exchange them for long-lived access tokens.
Embed OAuth 2.0 refresh tokens directly inside application container images and deploy an internal token-vending proxy to exchange them for long-lived access tokens.
What Token-Vending Proxies and Embedded Tokens Are
A token-vending proxy is a custom middleware pattern where applications request credentials from an internal service that handles token generation and refresh flows using embedded static refresh tokens or master secrets.
Why It Doesn't Meet the Requirement
- Severe Security Anti-Pattern: Hardcoding or baking OAuth 2.0 refresh tokens into container images creates immediate secret sprawl and exfiltration vulnerabilities across image registries.
- Unnecessary Architectural Complexity: Building and maintaining a custom proxy replicates capabilities already built natively into Google Cloud client libraries, the Compute Engine metadata server, and GKE Workload Identity.
- Issues with Token Lifespans: Generating long-lived access tokens directly violates the principle of short-lived credentials and increases exposure duration upon compromise.
Key Characteristics and Limitations
- Static Image Vulnerability: Embedding secrets into container layers makes secrets accessible to anyone with pull permissions to the registry.
- Single Point of Failure: An internal custom token-vending proxy introduces latency and operational overhead for every API request.
- Breaks Native ADC Integration: Standard Google Cloud client libraries cannot automatically locate credentials from custom proprietary proxies without writing custom credential providers.
This Answer Would Be Correct If
You were integrating proprietary, non-standard third-party external applications that lack any native OAuth 2.0 or OIDC federation capabilities and cannot run Google Cloud SDKs.
Additional Context
Google Cloud APIs only accept short-lived access tokens (typically valid for 1 hour). Constructing architectural workarounds to simulate long-lived access credentials contradicts modern zero-trust security principles.
Create a centralized IAM service account, generate a downloadable JSON key file, and configure the GOOGLE_APPLICATION_CREDENTIALS environment variable pointing to the file across all environments.
Create a centralized IAM service account, generate a downloadable JSON key file, and configure the GOOGLE_APPLICATION_CREDENTIALS environment variable pointing to the file across all environments.
What JSON Service Account Keys Are
Service account private keys are asymmetric JSON files generated directly from Cloud IAM that allow any bearer holding the file to authenticate as the associated service account from anywhere over the public internet.
Why It Doesn't Meet the Requirement
- Violates Long-Lived Key Restrictions: The scenario explicitly mandates eliminating the risks of downloadable, long-lived service account keys. Service account keys have a default lifetime of many years and present severe secret exfiltration risks.
- Violates Least Privilege: Sharing a centralized service account key across local workstations, staging, and production mixes environment boundaries and over-privileges local developer environments.
- High Operational Overhead: Managing, distributing, and rotating JSON keys across numerous development laptops and server environments creates significant maintenance complexity and compliance audit risk.
Key Characteristics and Limitations
- No Automatic Expiration: Static keys remain valid indefinitely until manually deleted or rotated in Cloud IAM.
- High Exfiltration Risk: JSON key files can be accidentally committed to source control repositories or leaked via unprotected build artifacts.
- Lack of Non-Repudiation: When individual developers share a service account JSON file, logging cannot distinguish which developer performed a specific API action.
This Answer Would Be Correct If
The workload was running on a legacy, non-Google Cloud on-premises environment where Workload Identity Federation was strictly not supported and alternative managed federation mechanisms were unavailable.
Additional Context
While setting GOOGLE_APPLICATION_CREDENTIALS is one lookup mechanism used by ADC, relying on downloadable JSON service account keys is strongly discouraged when platform-native managed identities (like GKE Workload Identity) are available.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Exponential Backoff with Jitter and Partial Responses
Accessing Google API best practices
IntermediateProfessional Cloud Architect
Private Google Access and VPC Service Controls
Accessing Google API best practices
IntermediateProfessional Cloud Architect
Exponential Backoff with Jitter and Pagination
Google API client libraries
IntermediateProfessional Cloud Architect
Cloud Pub/Sub to Dataflow to BigQuery Streaming
Choosing data processing solutions
IntermediateProfessional Cloud Architect
Active Assist and IAM Recommender
Gemini Cloud Assist
AdvancedProfessional Data Engineer
Cloud SQL PostgreSQL WAL Compression
Data replication and failover (e.g., Cloud SQL, Redis clusters)
Last updated