Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Least Privilege GitOps with Break-Glass Access
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise organization is designing a formal change management and governance framework for its Google Cloud production environment. The cloud architecture team must enforce separation of duties, ensure infrastructure modifications are fully audited, and prevent unauthorized manual drift while supporting rapid incident response.
The design must meet these key requirements:
- Routine operational changes to infrastructure must follow a version-controlled GitOps pipeline, with regular users restricted from directly creating or updating production resources.
- Site Reliability Engineers (SREs) and operators need visibility to monitor application health across project folders without having permissions to modify the underlying infrastructure.
- Emergency break-glass access must be established with 2 to 5 dedicated accounts configured with hardware FIDO security keys in a separate Organizational Unit (OU), ensuring any emergency intervention leaves an auditable trail in Cloud Audit Logs.
Which governance and change management strategy should the enterprise implement?
Explanations
Assign the Cloud Hub Operator role to all personnel, disable Cloud Identity two-step verification for emergency users to accelerate incident response, and store break-glass credentials in a shared software password manager.
Assign the Cloud Hub Operator role to all personnel, disable Cloud Identity two-step verification for emergency users to accelerate incident response, and store break-glass credentials in a shared software password manager.
What this approach represents
This approach grants baseline operational viewing roles to staff but severely compromises the security of emergency administrative accounts by disabling multi-factor authentication and utilizing centralized software-based password storage.
Why it doesn't meet the requirement
- Severe credential risk: Disabling 2-step verification on highly privileged emergency break-glass accounts leaves them vulnerable to credential theft, phishing, and brute-force attacks.
- Violates physical security guidelines: Storing super-admin emergency credentials in a software-based password manager creates an attractive single point of compromise compared to distributed physical security controls (such as hardware tokens and physical safes).
- Inadequate emergency governance: Emergency accounts must have phishing-resistant FIDO security keys enforced rather than relaxed authentication controls.
Key limitations
- No phishing resistance: Lacks hardware-backed authentication for critical administrative accounts.
- Software vault exposure: If the shared password manager is breached, all cloud emergency accounts are compromised simultaneously.
- Fails compliance standards: Security compliance frameworks mandate strict MFA enforcement on all privileged administrative identities.
This answer would be correct if
The organization had no external network exposure, zero compliance requirements, and prioritized instantaneous, unauthenticated recovery over credential security.
Provision a single emergency super-admin user enrolled in SMS-based multi-factor authentication, and grant all SREs the App Management Viewer role with full Editor permissions inherited from the organization root.
Provision a single emergency super-admin user enrolled in SMS-based multi-factor authentication, and grant all SREs the App Management Viewer role with full Editor permissions inherited from the organization root.
What this approach represents
This option provisions a single emergency user relying on SMS multi-factor authentication and grants broad roles/editor rights to SREs across the entire organization hierarchy.
Why it doesn't meet the requirement
- Single point of failure: Having only one emergency access user introduces a critical single point of failure; if the key, phone, or password is lost, emergency access is blocked.
- Insecure MFA method: SMS-based verification is vulnerable to SIM-swapping and phishing attacks. Google Cloud best practices require hardware FIDO security keys for emergency accounts.
- Violates least privilege and separation of duties: Granting the Editor role at the organization root allows SREs to directly modify, delete, and deploy resources in any project, bypassing version-controlled pipelines and eliminating the read-only monitoring separation.
Key limitations
- Account lockout risk: A single break-glass account cannot guarantee continuous access during an emergency.
- Excessive permissions: Inherited Editor rights at the organization root override any intended folder-level restrictions.
- Drift vulnerability: Unrestricted editing capabilities lead to unrecorded manual configuration changes across projects.
This answer would be correct if
The environment was an unmanaged personal sandbox where only one administrator existed and full organization-wide editing was needed for testing.
Assign project-level Owner roles to operational teams, use Cloud Audit Logs to detect manual changes after they occur, and configure an automated Cloud Function to rotate break-glass super-admin passwords every 24 hours.
Assign project-level Owner roles to operational teams, use Cloud Audit Logs to detect manual changes after they occur, and configure an automated Cloud Function to rotate break-glass super-admin passwords every 24 hours.
What this approach represents
This approach relies on granting broad, highly privileged administrative roles (roles/owner) directly to operational engineers while relying entirely on post-hoc detective controls (auditing) and automated scripts to manage break-glass passwords.
Why it doesn't meet the requirement
- Fails separation of duties: Granting the Owner role violates the principle of least privilege. It gives operators unrestricted access to modify infrastructure, bypass version control, and alter IAM policies directly in production.
- Fails emergency access security best practices: Automating password rotation for emergency super-admin accounts requires automation scripts or service accounts to possess super-admin privileges. This creates high-value targets for attackers and weakens the security posture of emergency credentials.
- No monitoring-only separation: SREs receive full administrative write access rather than scoped viewing roles.
Key limitations
- Direct drift creation: Operators can make untracked, manual configuration changes directly in production.
- Automation risk: Storing super-admin automation credentials in scripts introduces critical security vulnerabilities.
- Audit complexity: Disentangling valid changes from unauthorized drift in audit logs becomes difficult when everyone possesses broad Owner rights.
This answer would be correct if
The organization operated a non-production development sandbox where rapid, unrestricted prototyping by all developers was prioritized over compliance, separation of duties, and change control.
Grant predefined view-only roles to monitoring personnel, restrict resource modification to CI/CD service accounts, and establish redundant break-glass users protected with FIDO security keys in a dedicated Organizational Unit.
Grant predefined view-only roles to monitoring personnel, restrict resource modification to CI/CD service accounts, and establish redundant break-glass users protected with FIDO security keys in a dedicated Organizational Unit.
What the solution is
This strategy establishes a robust change governance framework by combining least-privilege IAM roles, GitOps automation, and emergency break-glass procedures. It enforces separation of duties between viewing operational status and deploying production changes.
How it meets the requirements
- Separation of duties & GitOps enforcement: By granting operational teams and SREs view-only roles (such as
roles/apphub.appManagementViewerorroles/cloudhub.operator), personnel can monitor applications without possessing direct write permissions. All production modifications must flow through version-controlled CI/CD pipelines executed by dedicated service accounts. - Auditable change tracking: Automated pipeline deployments ensure all changes are tracked in version control, while Cloud Audit Logs automatically capture all API operations and administrative activity for compliance audits.
- Emergency access governance: Creating between 2 and 5 emergency access users in a separate Organizational Unit (OU) ensures redundancy without single points of failure. Enforcing FIDO security keys and avoiding automated credential rotation maintains strict physical and cryptographic security controls for high-privilege emergency accounts.
GitOps Separation of Duties on Google Cloud
System Architecture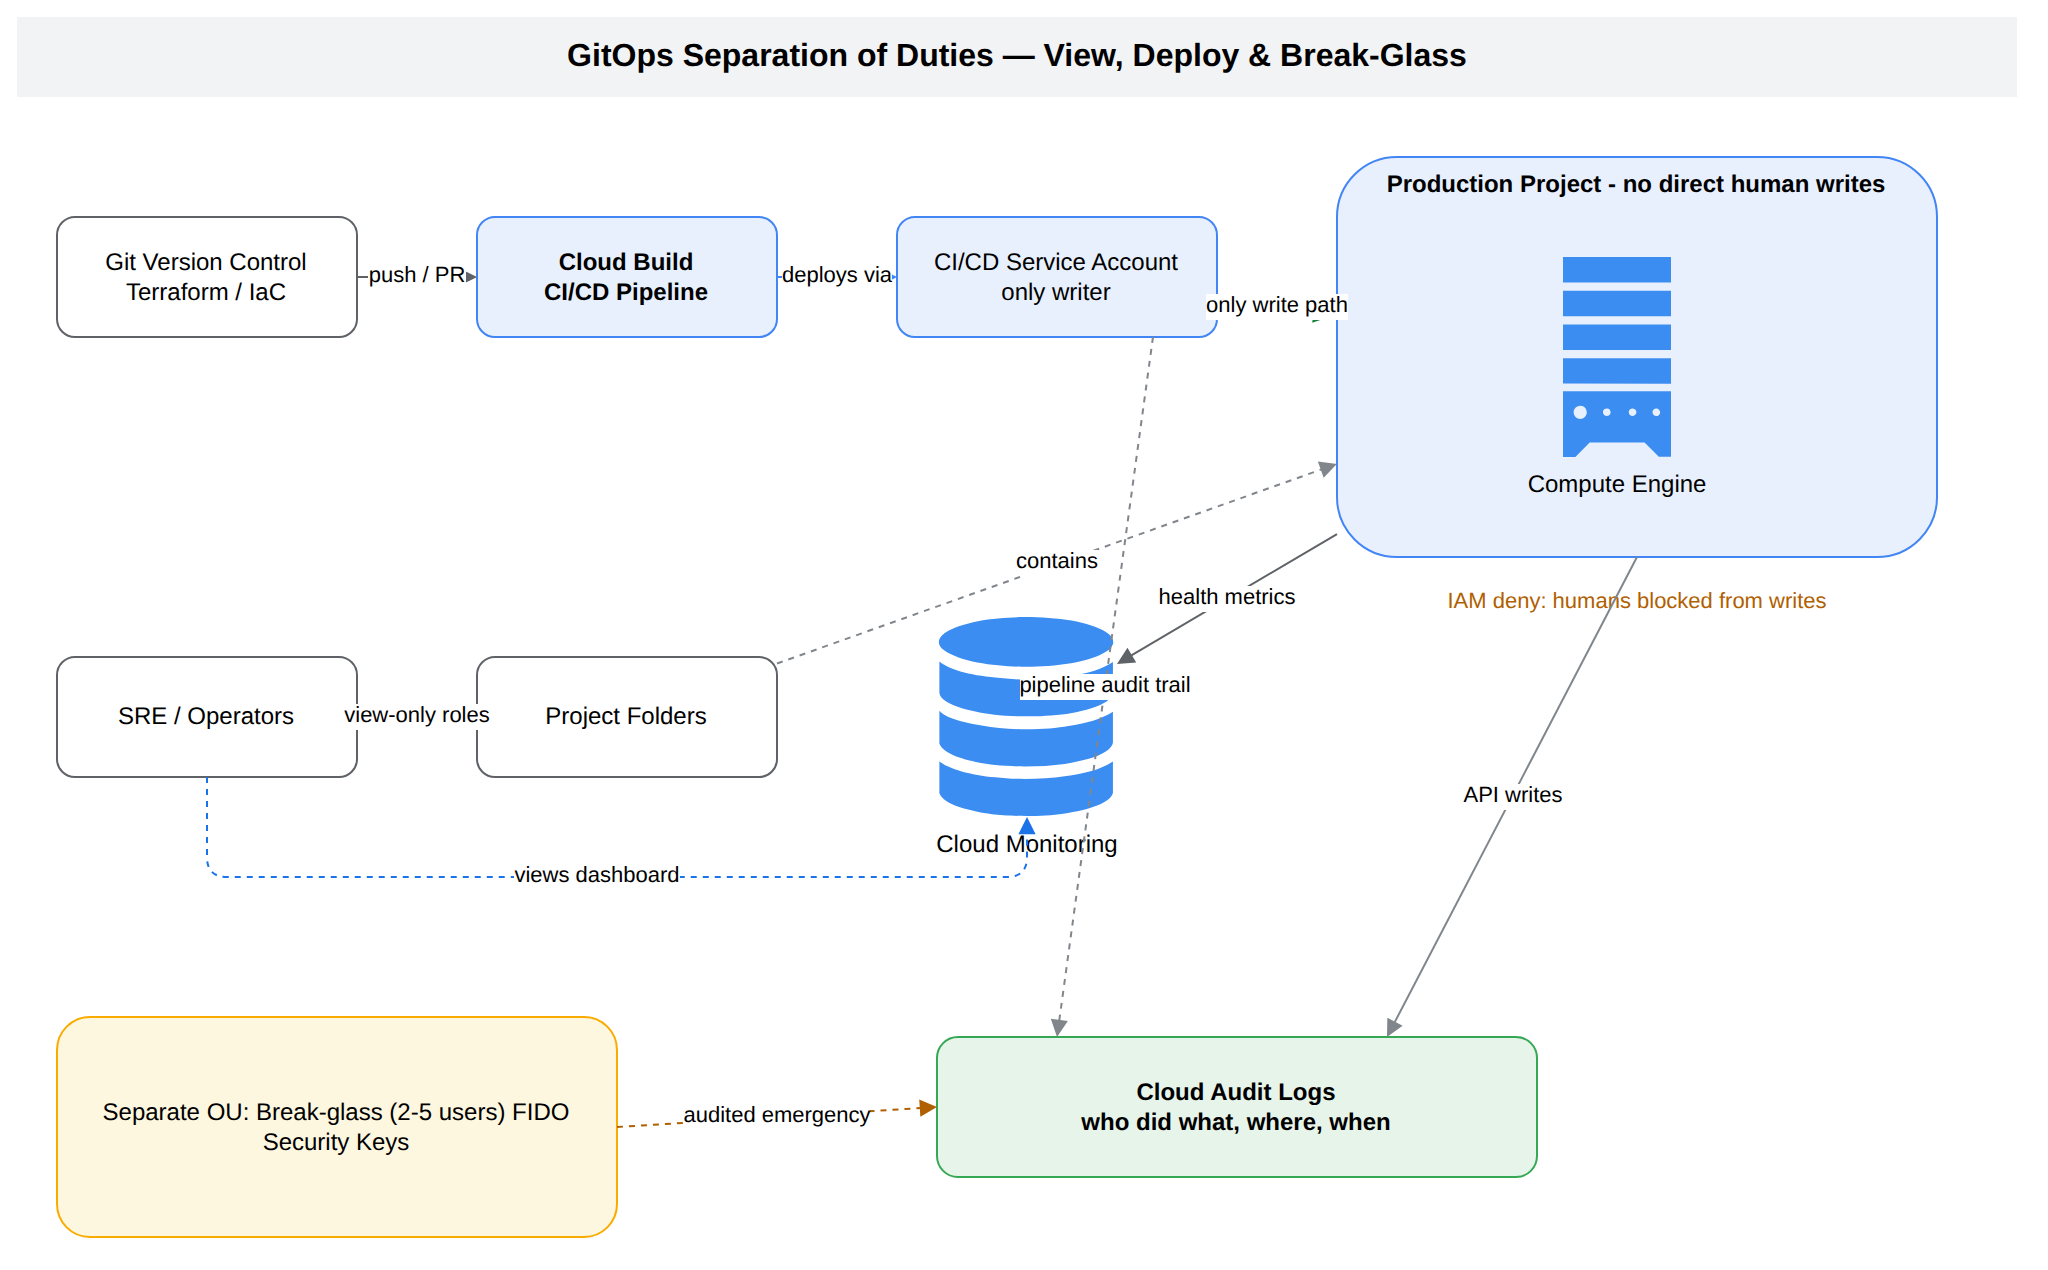
Key advantages
- Eliminates configuration drift: Prevents manual out-of-band updates by disallowing direct human write access to production.
- High resilience: Multiple emergency accounts protected by hardware keys guarantee access during catastrophic identity provider or pipeline outages.
- Full auditability: Clean distinction between automated CI/CD service account changes and emergency human interventions in Cloud Audit Logs.
Why this is optimal
This approach aligns with Google Cloud architecture best practices for continuous access, strict change control, and regulatory compliance.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
SRE Error Budget Change Management
Change management
IntermediateProfessional Cloud Architect
Secret Manager
Data security (key management, encryption, secret management)
IntermediateProfessional Cloud Architect
BigQuery Long-Term Storage Automatic Transition
Choosing appropriate storage types (e.g., object, file, and databases)
IntermediateProfessional Cloud Architect
Cloud Trace and Cloud Profiler
Performance and latency
IntermediateProfessional Cloud Architect
Workload Identity Federation and VPC Service Controls
Integration patterns with external systems
AdvancedProfessional Cloud DevOps Engineer
Cloud Logging Distribution Log-Based Metrics
Creating custom metrics, including log-based metrics
Last updated