Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Centralized Runtime Secrets with Secret Manager
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise organization is modernizing a multi-tier web application deployed across Google Cloud compute services. The application currently loads third-party API keys, TLS certificates, and database passwords from local plaintext configuration files bundled inside the container images and source code repository.
The security architect has established the following requirements:
- Sensitive configuration values and credentials must be completely decoupled from application source code and deployment images.
- The solution must centralize credential storage, support secret versioning for rotation, and provide access auditing.
- Applications must retrieve the plaintext credentials securely at runtime using the principle of least privilege.
Which solution should the architect implement?
Explanations
Store the credentials and certificates in Secret Manager, manage rotation through secret versions, and grant the application service account the Secret Manager Secret Accessor (roles/secretmanager.secretAccessor) role.
Store the credentials and certificates in Secret Manager, manage rotation through secret versions, and grant the application service account the Secret Manager Secret Accessor (roles/secretmanager.secretAccessor) role.
What Secret Manager Is
Secret Manager is a secure, fully-managed Google Cloud service designed specifically for the centralized storage, management, and auditing of sensitive data, such as API keys, passwords, TLS certificates, and database connection strings.
How It Meets the Requirements
- Decoupling Sensitive Configuration: Storing credentials in Secret Manager removes hardcoded values and configuration files from container images and source code repositories.
- Versioning and Centralization: Secret Manager organizes data as first-class secret resources containing immutable, numbered secret versions. When credentials rotate, administrators add a new version without modifying code paths or redeploying infrastructure.
- Programmatic Access with Least Privilege: Applications authenticate using their attached service account via Application Default Credentials (ADC) and request secret payloads at runtime. Granting
roles/secretmanager.secretAccessorprovides the exact permission (secretmanager.versions.access) required to retrieve secret payloads without granting administrative management permissions. - Auditing: Every retrieval and administrative action is recorded in Cloud Audit Logs, providing clear visibility into which identities access specific credentials.
Least-Privilege Runtime Secret Access
Sequence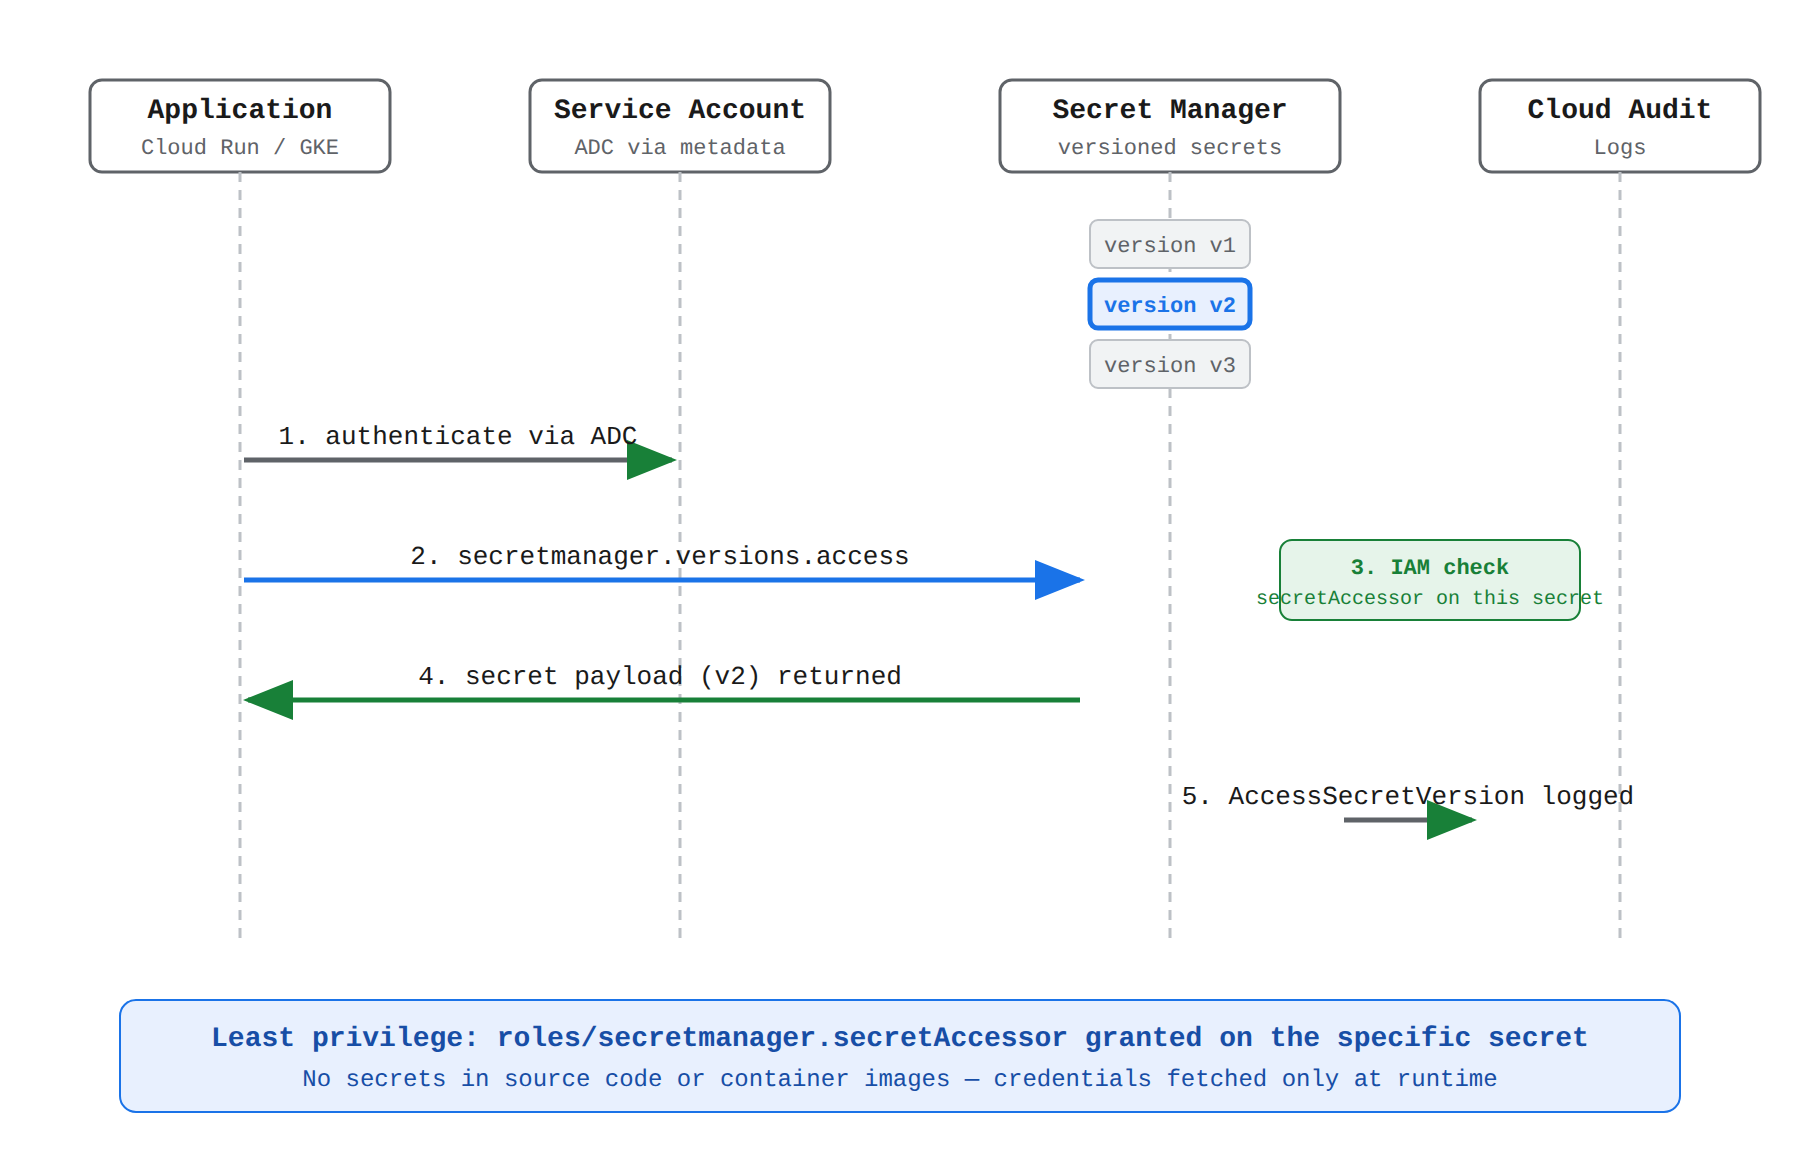
Key Advantages
- Automatic Payload Encryption: Secret payloads are encrypted at rest using AES-256 by default, with optional Customer-Managed Encryption Keys (CMEK).
- Granular IAM Control: Permissions can be applied at the project, folder, organization, or individual secret level.
- Native Integration: Works seamlessly with Google Cloud compute services (Compute Engine, GKE, Cloud Run) and orchestration workflows.
- Simple String and Binary Storage: Handles structured strings, base64 data, and binary certificates up to 64 KiB per secret version.
Why This Is Optimal
This solution directly satisfies all security mandates by separating sensitive metadata from application binaries, providing robust version management, and enforcing least-privilege runtime access with granular IAM roles.
Store the credentials in an encrypted Cloud Storage bucket with Customer-Managed Encryption Keys (CMEK), and grant the application service account the Storage Object Viewer (roles/storage.objectViewer) role.
Store the credentials in an encrypted Cloud Storage bucket with Customer-Managed Encryption Keys (CMEK), and grant the application service account the Storage Object Viewer (roles/storage.objectViewer) role.
What Cloud Storage with CMEK Does
Cloud Storage is an object storage service designed for storing unstructured files, images, and backups. When paired with Customer-Managed Encryption Keys (CMEK), object data is protected at rest using symmetric keys managed in Cloud KMS.
Why It Doesn't Meet the Requirement
- Lack of Dedicated Secret Management: Cloud Storage is not optimized for serving individual API tokens, short configuration strings, or runtime secret versioning.
- Coarse Access Boundaries: The
roles/storage.objectViewerrole granted at the bucket level allows the service account to read every object within that bucket, violating strict least-privilege access for individual secrets. - Missing Purpose-Built Features: Cloud Storage lacks purpose-built secret lifecycle states (such as destroying individual secret versions, disabling compromised versions immediately, or integrating with specialized secret backends).
Key Characteristics and Limitations
- Object Storage Focus: Cloud Storage is designed for large binary objects, archives, and streaming media rather than low-latency, small-payload secret retrieval.
- Complex Rotation: Managing separate versions of small credential files inside storage buckets introduces complex synchronization overhead.
- Broad Permissions: Object-level permissions require Access Control Lists (ACLs) or complex IAM conditions rather than simple secret-level IAM bindings.
This Answer Would Be Correct If
The workload required storing large sensitive data files, database backups, or media archives protected under customer-controlled encryption policies.
Store the credentials and certificates in Cloud Key Management Service (Cloud KMS) as asymmetric cryptographic keys, and grant the application service account the Cloud KMS CryptoKey Decrypter (roles/cloudkms.cryptoKeyDecrypter) role.
Store the credentials and certificates in Cloud Key Management Service (Cloud KMS) as asymmetric cryptographic keys, and grant the application service account the Cloud KMS CryptoKey Decrypter (roles/cloudkms.cryptoKeyDecrypter) role.
What Cloud KMS Is and Does
Cloud Key Management Service (Cloud KMS) is designed to manage cryptographic keys and execute cryptographic operations, such as encrypting, decrypting, and signing arbitrary data payloads.
Why It Doesn't Meet the Requirement
- Purpose Mismatch: Cloud KMS manages the encryption keys themselves, but it is not a secret storage repository. Cloud KMS does not store or return plain configuration strings, database passwords, or third-party API tokens directly.
- Key Inaccessibility: In Cloud KMS, raw cryptographic key material cannot be viewed or extracted as plaintext values by users or applications.
- Operational Overhead: To protect secrets with Cloud KMS alone, developers must implement a custom envelope encryption workflow, manually storing ciphertext files in object storage and performing decryption calls inside the application.
Key Characteristics and Limitations
- Cryptographic Operations: Cloud KMS handles key lifecycle management, rotation schedules, and cryptographic boundary enforcement.
- No Direct Secret Payloads: It does not offer built-in key-value storage for application configuration strings or TLS certificates.
- Role Scope: The
roles/cloudkms.cryptoKeyDecrypterrole allows cryptographic decryption of ciphertext, not direct access to stored secret strings.
This Answer Would Be Correct If
The requirement called for encrypting large volumes of application data, database fields, or storage buckets using customer-managed cryptographic keys where the application performs cryptographic signing or decryption operations.
Store the credentials and certificates in Secret Manager, and assign the application service account the Secret Manager Admin (roles/secretmanager.admin) role to allow runtime configuration fetching.
Store the credentials and certificates in Secret Manager, and assign the application service account the Secret Manager Admin (roles/secretmanager.admin) role to allow runtime configuration fetching.
What Secret Manager Admin Is and Does
The Secret Manager Admin (roles/secretmanager.admin) role is an administrative identity role that provides complete control over all Secret Manager resources in a project, including creating, modifying, listing, and deleting secrets and secret versions.
Why It Doesn't Meet the Requirement
- Violates Principle of Least Privilege: Application workloads only need read access to the specific secret payload required for execution (
secretmanager.versions.access). Granting administrative rights gives the workload excessive privileges. - Security Risk: If an application instance running with
roles/secretmanager.adminis compromised, an attacker could create, alter, disable, or delete critical organizational secrets and tamper with IAM policies across the project. - Improper Role Assignment: Administrative roles should be restricted to CI/CD automation pipelines, security engineers, or platform administrators, not runtime workload identities.
Key Characteristics and Limitations
- Includes Control Plane Permissions:
roles/secretmanager.admincontains permissions such assecretmanager.secrets.delete,secretmanager.secrets.create, andsecretmanager.secrets.setIamPolicy. - Overly Broad: Exceeds the read-only requirement of runtime application fetching.
- Least-Privilege Alternative: The appropriate role for runtime access is
roles/secretmanager.secretAccessor.
This Answer Would Be Correct If
You were configuring permissions for a cloud platform security administrator who is responsible for managing the entire lifecycle, replication policies, and IAM access controls of all Secret Manager resources.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Customer-Managed Encryption Keys (CMEK)
Data security (key management, encryption, secret management)
IntermediateProfessional Cloud Architect
Cloud KMS Dedicated Key Project Architecture
Data security (key management, encryption, secret management)
IntermediateProfessional Cloud Architect
Model Armor Generative AI Security
Securing AI (e.g., Model Armor, Sensitive Data Protection, and secure model deployment)
IntermediateProfessional Cloud Architect
Separation of Duties with Resource Hierarchy and IAM
Separation of duties
IntermediateProfessional Cloud Architect
Sensitive Data Protection, Resource Location Policies, VPC Service Controls
Legislation and regulation (e.g., health record privacy, children's privacy, data privacy, ownership, and data sovereignty)
AdvancedProfessional Cloud Security Engineer
Cloud DLP, BigQuery Differential Privacy, Confidential Computing
Implementing security and privacy controls for AI/ML systems to protect against unintentional exploitation of data or models.
Last updated