Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Blocking Vulnerable Container Images in Cloud Build
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
A DevOps team uses Google Cloud Build to run automated tests and build container images for a critical application. The organization's security policy requires shifting security left by validating that container images do not contain severe vulnerabilities before they are stored in the artifact repository.
The team has the following requirements:
- Scan locally built container images for OS and application language package vulnerabilities directly within the CI/CD pipeline.
- Automatically halt the build and prevent the image from being pushed to Artifact Registry if any
CRITICALorHIGHseverity vulnerabilities are detected.
Which strategy should the team implement in their Cloud Build configuration?
Explanations
Configure a Binary Authorization policy inside Cloud Build that evaluates the local Docker build context and prevents the Docker daemon from outputting image layers that contain critical vulnerabilities.
Configure a Binary Authorization policy inside Cloud Build that evaluates the local Docker build context and prevents the Docker daemon from outputting image layers that contain critical vulnerabilities.
What Binary Authorization is
Binary Authorization is a deploy-time security control that ensures only trusted container images are deployed to Google Cloud runtime environments, such as Google Kubernetes Engine (GKE) and Cloud Run. It enforces signature validation against predefined policies by verifying attestations created by trusted authorities.
Why it doesn't meet the requirement
- Deploy-time vs. build-time enforcement: Binary Authorization does not integrate directly into the Docker engine to alter how image layers are built, nor does it perform vulnerability scanning itself.
- Cannot block registry pushes: Binary Authorization intercepts admission requests when a pod or service is being created in a runtime cluster; it has no mechanism to block the
docker pushstep in a CI build pipeline.
Key characteristics and limitations
- Enforces admission control: Works as a Kubernetes admission controller or Cloud Run deploy-time check.
- Relies on external attestations: Requires an attestation (often produced after an Artifact Analysis scan or manual review) to authorize a deployment.
- No built-in static scanner: Binary Authorization verifies cryptographic signatures rather than scanning software packages directly.
This answer would be correct if
The objective was to prevent GKE clusters from running container images that lack a valid cryptographic attestation confirming compliance with organizational vulnerability policies.
Enable automatic vulnerability scanning in Artifact Registry, push all built container images immediately after unit testing, and trigger a Cloud Function via Pub/Sub to delete the image if vulnerabilities are discovered.
Enable automatic vulnerability scanning in Artifact Registry, push all built container images immediately after unit testing, and trigger a Cloud Function via Pub/Sub to delete the image if vulnerabilities are discovered.
What automatic scanning with reactive deletion does
This architecture relies on Artifact Analysis automatic scanning, which triggers an asynchronous vulnerability scan only after a container image has already been pushed to an Artifact Registry repository. When scan results are available, Artifact Analysis publishes notifications to a Pub/Sub topic, which can trigger an event-driven Cloud Function to delete non-compliant images.
Why it doesn't meet the requirement
- Fails pre-upload prevention: The requirement explicitly mandates blocking vulnerable artifacts before they are uploaded to Artifact Registry. With automatic scanning, vulnerable images are written to the registry and could potentially be pulled by downstream deployment triggers before deletion occurs.
- Pipeline feedback delay: Deleting an image post-push decouples the vulnerability failure from the CI/CD build run, making it harder for developers to receive immediate feedback within the Cloud Build pipeline output.
Key characteristics and limitations
- Asynchronous execution: Automatic scans take time to complete after upload, creating a window where vulnerable artifacts are accessible.
- Unnecessary storage and API operations: Writing and subsequent deletion consume registry write quotas and storage operations unnecessarily.
- Race conditions: Automated continuous deployment tools watching the registry might pull the image before the deletion script executes.
This answer would be correct if
The requirement was to continuously monitor images already deployed or stored in Artifact Registry for newly discovered Common Vulnerabilities and Exposures (CVEs) over time.
Configure build steps in cloudbuild.yaml to execute gcloud artifacts docker images scan on the local image, evaluate the results using gcloud artifacts docker images list-vulnerabilities, and fail the pipeline prior to executing docker push if matching severity levels are found.
Configure build steps in cloudbuild.yaml to execute gcloud artifacts docker images scan on the local image, evaluate the results using gcloud artifacts docker images list-vulnerabilities, and fail the pipeline prior to executing docker push if matching severity levels are found.
What On-Demand Scanning in Cloud Build is
Artifact Analysis On-Demand Scanning allows developers and CI/CD pipelines to initiate vulnerability scans on container images stored locally or in Artifact Registry. By leveraging the Google Cloud SDK within Cloud Build, organizations can scan images as a build step immediately after compilation and containerization.
How it meets the requirements
- Shifting security left: Scanning the local container before uploading ensures that security assessments happen immediately after artifact creation and before publication.
- Blocking vulnerable artifacts: By running
gcloud artifacts docker images scanfollowed bygcloud artifacts docker images list-vulnerabilities, the build pipeline can parse the effective severity levels. If vulnerabilities matchingCRITICALorHIGHare discovered, the script exits with a non-zero code, failing the build and preventing subsequentdocker pushexecution. - Comprehensive package scanning: On-Demand Scanning analyzes both base operating system packages and language-level dependencies (such as Java, Go, Python, and Node.js) against a centralized vulnerability database.
Pre-Push Scan Gate Blocks Vulnerable Images
Process Flow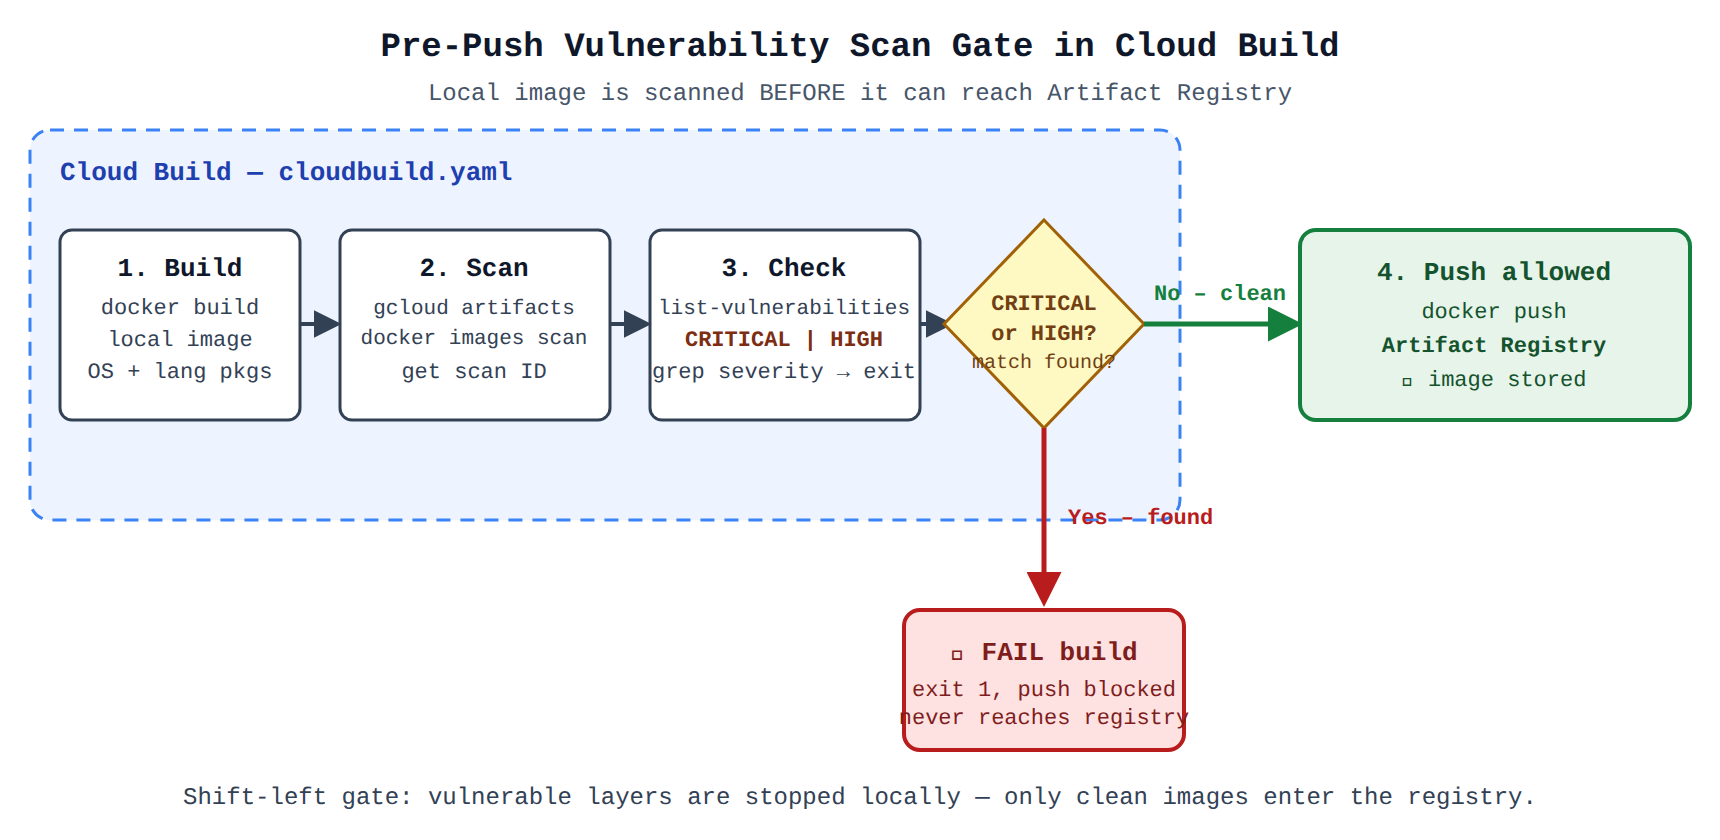
Key advantages and capabilities
- Pre-upload validation: Guarantees that untrusted or vulnerable container layers never enter the centralized Artifact Registry repository.
- Granular policy gating: Enables custom filtering rules and regex matching against specific Common Vulnerability Scoring System (CVSS) scores or severity categories.
- Automated integration: Integrates natively with standard Cloud Build service accounts and builders without requiring third-party scanning infrastructure.
- Audit readiness: Generates verifiable scan IDs and occurrences that can be reviewed in logs and security dashboards.
Why this is optimal
This approach directly prevents vulnerable images from reaching the repository, saving storage and network overhead while establishing a clean separation between validated release candidates and failed builds.
Incorporate a Web Security Scanner execution step into cloudbuild.yaml to scan the local container image filesystem for CVEs and halt the build upon detection of high-risk vulnerabilities.
Incorporate a Web Security Scanner execution step into cloudbuild.yaml to scan the local container image filesystem for CVEs and halt the build upon detection of high-risk vulnerabilities.
What Web Security Scanner is
Web Security Scanner is a security tool within Security Command Center designed to scan public-facing web applications for common web application vulnerabilities such as Cross-Site Scripting (XSS), Flash content, mixed content, and cleartext passwords in web endpoints.
Why it doesn't meet the requirement
- Incompatible target type: Web Security Scanner requires a deployed, running web endpoint accessible via HTTP/HTTPS (such as App Engine, GKE, or Compute Engine) to crawl pages and test inputs. It cannot inspect static, local container image files or tarballs on disk.
- Wrong scope of detection: Web Security Scanner analyzes runtime application behavior and OWASP Top 10 vulnerabilities, not underlying operating system packages or language-specific package manifests inside container layers.
Key characteristics and limitations
- Network endpoint crawler: Dispatches HTTP GET and POST requests against active URLs.
- Cannot scan binaries: Has no capability to parse container file layers, OS package databases (like
dpkgorrpm), or language lockfiles. - Late lifecycle phase: Operates exclusively in dynamic testing environments rather than static CI build phases.
This answer would be correct if
The goal was to run automated Dynamic Application Security Testing (DAST) against a deployed staging URL to detect OWASP Top 10 security risks prior to production release.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
MIG Auto-healing and Simulate Maintenance Event
Testing and validation of software and infrastructure
IntermediateProfessional Cloud Architect
JIT Access Groups and Automatic IAM Grants Constraint
Service catalog and provisioning
IntermediateProfessional Cloud Architect
Separation of Duties with Resource Hierarchy and IAM
Separation of duties
IntermediateProfessional Cloud Architect
SLIs and SLOs for Critical User Journeys
Success measurements (e.g., key performance indicators [KPI], return on investment [ROI], and metrics)
IntermediateProfessional Cloud Architect
Cloud Trace and Cloud Profiler Correlation
Profiling and benchmarking
FundamentalAssociate Data Practitioner
Cloud Storage Lifecycle matchesStorageClass Condition
Evaluate Google Cloud services for archiving data given business requirements
Last updated