Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Model Armor Protection for Generative AI Workloads
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
A financial enterprise is deploying a customer-facing conversational application powered by foundation large language models (LLMs) on Google Cloud. During security assessments, red-team testers successfully executed sophisticated prompt injection and jailbreaking attacks that bypassed standard system prompts and caused the model to exhibit unintended behaviors.
The enterprise has the following operational requirements:
- Defend the generative AI workload against adversarial prompt injections and jailbreak attempts
- Inspect user prompts and model responses to prevent sensitive data leakage
- Enforce customizable content moderation to block prohibited content harms
Which security capability should the cloud architect implement to meet these requirements?
Explanations
Rely exclusively on Gemini default non-configurable safety filters
Rely exclusively on Gemini default non-configurable safety filters
What default non-configurable safety filters are
Default non-configurable safety filters provide an automated baseline layer of safety built directly into foundation models like Gemini. Their primary function is to enforce essential legal and ethical baselines without requiring explicit configuration.
Why it doesn't meet the requirement
- No Jailbreak Protection: Default baseline filters are primarily focused on blocking specific critical violations such as Child Sexual Abuse Material (CSAM) and verbatim copyrighted content recitation.
- Vulnerable to Adversarial Inputs: Default settings do not protect against sophisticated, motivated adversarial prompt injections or jailbreaking attacks that attempt to override application logic.
- Lacks Sensitive Data Guardrails: Default filters do not inspect prompts or responses for enterprise-specific sensitive data leakage.
Key characteristics and limitations
- Operates as a static, non-configurable baseline across standard queries.
- Intended for general workflows where adversarial or malicious user input is not anticipated.
- Does not offer customizable blocking thresholds or domain-specific safety policies.
This answer would be correct if
The workload were an internal, low-risk demonstration environment where no malicious or untrusted user input is expected and baseline CSAM/copyright protection is sufficient.
Configure detailed behavioral system instructions within the model prompt context
Configure detailed behavioral system instructions within the model prompt context
What system instructions are
System instructions provide direct behavioral guidance and persona framing to a model before processing incoming user prompts. They define preferred communication styles, task constraints, tone, and operational boundaries.
Why it doesn't meet the requirement
- Susceptible to Prompt Overrides: System instructions reside inside the model's context window. Skilled attackers can craft adversarial prompt injection payloads that convince the model to ignore, reveal, or override preceding system instructions.
- No Hard Enforcement Perimeter: System instructions provide soft behavioral steering rather than an external, deterministic security inspection barrier.
- No Automated Data Leakage Redaction: System instructions cannot deterministically scan for and redact complex sensitive data formats or intercept malicious content before model invocation.
Key characteristics and limitations
- Guides natural language behavior and conversational tone.
- Can be circumvented by adversarial jailbreaking techniques.
- Operates entirely within model inference rather than as an external security gateway.
This answer would be correct if
The goal was simply to establish brand tone, conversational context, or general behavioral guidelines for normal user interactions without defending against active security exploits.
Deploy Google Cloud Armor security policies on an External HTTP(S) Load Balancer
Deploy Google Cloud Armor security policies on an External HTTP(S) Load Balancer
What Google Cloud Armor does
Google Cloud Armor is a network edge and application perimeter security service that integrates with Google Cloud External Application Load Balancers. It provides Layer 3 to Layer 7 protection against Distributed Denial of Service (DDoS) attacks and common web exploits (such as SQL injection and Cross-Site Scripting via OWASP Top 10 rules).
Why it doesn't meet the requirement
- Lacks Generative AI Threat Inspection: Cloud Armor inspects HTTP headers, IP origins, and standard web payloads, but it does not analyze the semantic meaning of natural language prompts to detect generative AI jailbreaks or prompt injections.
- No LLM Output Validation: Cloud Armor does not inspect or sanitize LLM-generated text for content harms or sensitive data exposure.
- Mismatched Threat Domain: Protecting against prompt injection requires AI-specific semantic security layers rather than traditional network/WAF filtering.
Key characteristics and limitations
- Protects edge infrastructure from Layer 3/4 volumetric DDoS attacks and Layer 7 web vulnerabilities.
- Enforces IP allowlists, geofencing, and rate-limiting.
- Blind to adversarial prompt semantics and foundation model security vulnerabilities.
This answer would be correct if
The primary requirement were protecting the web frontend and API gateways from network DDoS attacks, IP-based scraping, or traditional SQL/XSS injections.
Implement Model Armor as a security layer for the generative AI application
Implement Model Armor as a security layer for the generative AI application
What Model Armor is
Model Armor is an enterprise-grade security service designed specifically for generative AI workloads and foundation models in Google Cloud. It acts as an operational guardrail layer that evaluates both user inputs (prompts) and generated outputs to safeguard LLM interactions against specialized AI threats.
How it meets the requirements
- Prompt Injection & Jailbreak Defense: Model Armor is engineered to detect and mitigate adversarial manipulation techniques, including prompt injection and jailbreaking attempts, where malicious actors attempt to override system instructions.
- Sensitive Data Protection: It integrates data inspection mechanisms to identify and sanitize or block the leakage of sensitive training data, personal data, and confidential credentials.
- Content Harms & Prohibited Content: Model Armor enforces policy-driven content safety checks, inspecting inputs and responses against prohibited categories such as hate speech, harassment, and dangerous content.
Key advantages and capabilities
- Comprehensive AI Perimeter Defense: Delivers multi-faceted protection covering jailbreaks, prompt injection, content harms, sensitive data exposure, and malicious payloads.
- Bi-directional Inspection: Secures both prompt ingestion and model inference generation workflows.
- Policy Enforcement: Enables enterprises to balance model utility and risk posture through configurable guardrails.
Model Armor Bi-directional Screening Flow
Sequence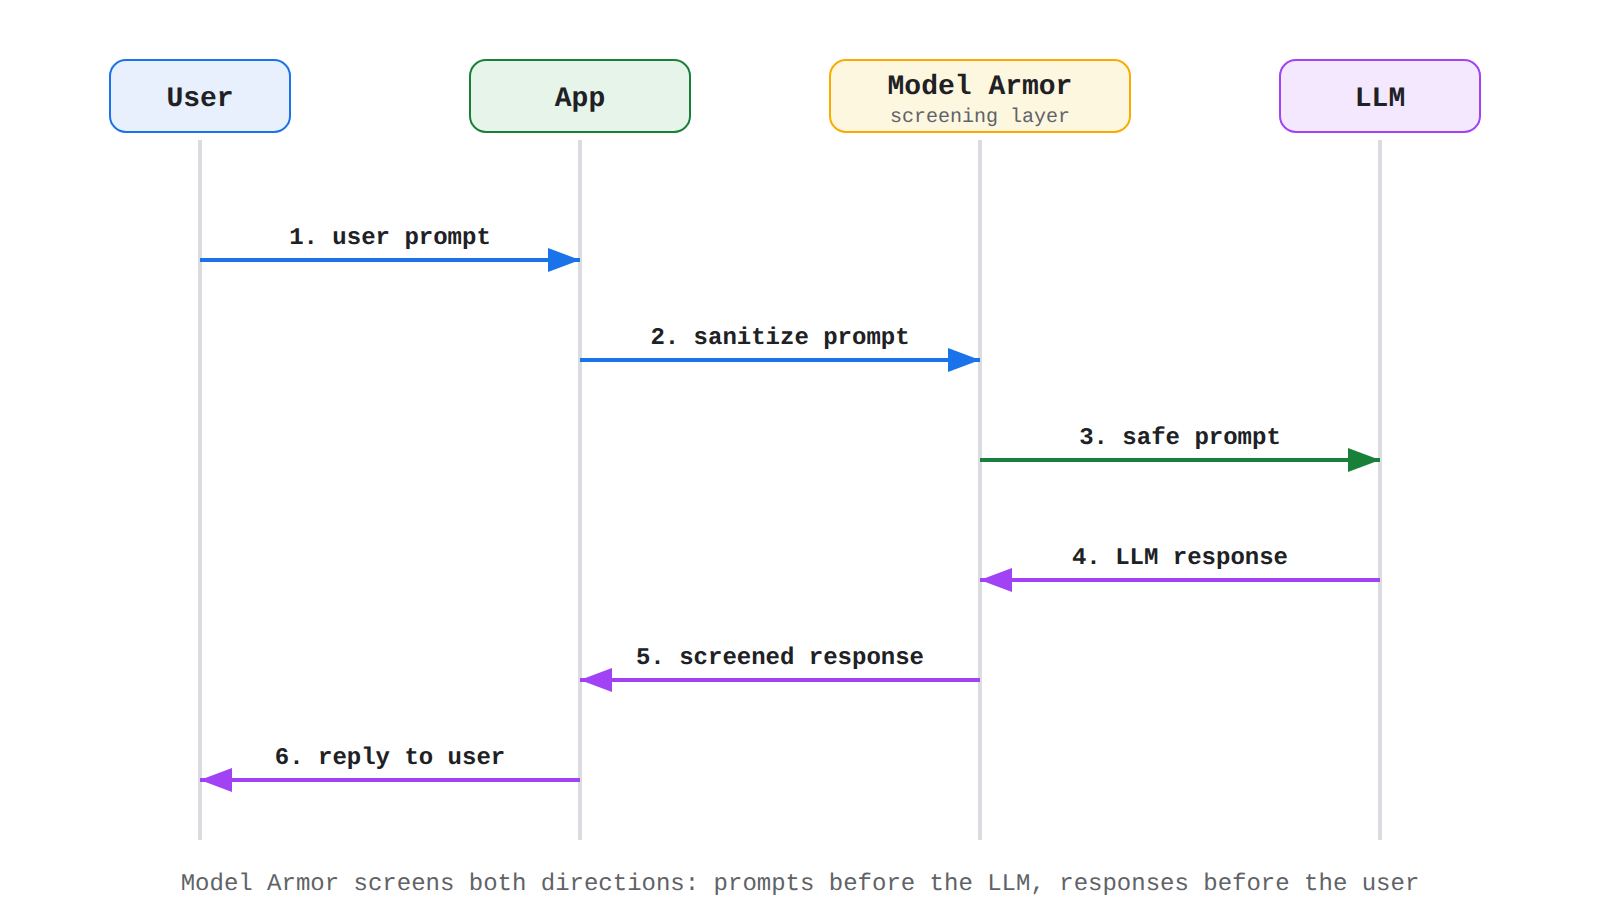
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Vertex AI Security Architecture
Securing AI (e.g., Model Armor, Sensitive Data Protection, and secure model deployment)
IntermediateProfessional Cloud Architect
Sensitive Data Protection De-identification Templates
Securing AI (e.g., Model Armor, Sensitive Data Protection, and secure model deployment)
IntermediateProfessional Cloud Architect
Cloud NAT for Private VM Egress
Gemini Cloud Assist
IntermediateProfessional Cloud Architect
Monolith to Microservices on GKE with HPA
Cloud and technology improvements
IntermediateProfessional Cloud Architect
Exponential Backoff with Jitter and Partial Responses
Accessing Google API best practices
AdvancedProfessional Data Engineer
VPC Service Controls Analytics Hub Ingress Egress
Publishing datasets
Last updated