Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Filtering Edge Traffic With Cloud Armor Policies
Free sample question with answers and detailed explanation below. The Cloud Digital Leader practice bank has an additional 3,070 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
A retail company runs a public web application behind a global external Application Load Balancer. The security team wants to safeguard their backend services from unauthorized access and potential web attacks by enforcing the following controls at the Google Cloud network edge:
- Block incoming traffic from specific external IP address ranges
- Restrict access based on the client's geographic region code
- Filter incoming requests based on custom HTTP request headers and URL paths
Which solution should the company implement to meet these requirements?
Explanations
Implement Identity-Aware Proxy (IAP) to scrub incoming Layer 7 traffic and block specific geographic regions at the network edge
Implement Identity-Aware Proxy (IAP) to scrub incoming Layer 7 traffic and block specific geographic regions at the network edge
What Identity-Aware Proxy (IAP) is
Identity-Aware Proxy (IAP) is a Google Cloud service that establishes a central authorization layer for applications accessed by HTTPS or TCP forwarding. It implements a zero-trust access model by verifying a user's identity and the context of the request to determine whether the user should be granted access to an internal application or virtual machine.
Why it doesn't meet the requirements
- Identity-focused rather than unauthenticated traffic filtering: IAP is designed to authenticate and authorize specific known users (such as employees or contractors) via Google identities, which makes it unsuitable for filtering anonymous, public retail traffic on an e-commerce website.
- Not a traffic-scrubbing engine: IAP does not perform Layer 3 to Layer 7 packet scrubbing or evaluate custom rule sets against arbitrary HTTP request headers to mitigate web attacks at the network edge.
- Commonly used for administrative access: In network security architectures, IAP is primarily used with TCP forwarding to replace permissive SSH and Remote Desktop Protocol (RDP) firewall rules and prevent brute-force attacks against virtual machines.
Key characteristics and limitations
- Replaces VPNs: Enables secure, identity-based access to internal enterprise applications and VMs from untrusted networks without requiring a traditional VPN.
- Secures management ports: Restricts inbound SSH and RDP access by allowing administrators to lock down VPC firewall rules strictly to IAP source IP ranges.
- Requires user authentication: Cannot be used as a transparent, rule-based IP and geographic traffic filter for unauthenticated public consumers visiting a retail site.
This answer would be correct if
The company wanted to restrict inbound administrative access to SSH and RDP ports on their virtual machines or require employees to authenticate with their corporate credentials before accessing an internal web application.
Attach an authorization policy based on service accounts and secure tags to the global external Application Load Balancer
Attach an authorization policy based on service accounts and secure tags to the global external Application Load Balancer
What load balancer authorization policies are
Authorization policies in Google Cloud Load Balancing allow administrators to enforce access controls based on the identity of the workload sending the traffic—specifically using service accounts or secure tags—rather than relying solely on source IP addresses. This enables identity-based microsegmentation between internal cloud resources.
Why it doesn't meet the requirements
- Unsupported on external load balancers: Authorization policies based on service accounts or secure tags are only supported for regional internal Application Load Balancers and cross-region internal Application Load Balancers. They cannot be attached to a global external Application Load Balancer.
- Designed for internal cloud workloads: Service accounts and secure tags are Google Cloud resource attributes attached to internal workloads like Compute Engine VMs or Google Kubernetes Engine (GKE) nodes, not external internet users.
- Does not filter external geography or public IPs: Because public retail customers on the internet do not send traffic from Google Cloud service accounts or VPC secure tags, this mechanism cannot filter public IP ranges or geographic region codes.
Key characteristics and limitations
- Shifts from IP to identity: Allows rules such as permitting only Compute Engine VMs with an
environment: prodsecure tag or a specific service account to reach sensitive internal API paths like/api/payments. - Internal VPC scope: Operates across internal VPC architectures, including Shared VPC, VPC Network Peering, and Private Service Connect.
- No edge DDoS protection: Does not operate at Google's external points of presence (PoPs) to block volumetric internet attacks.
This answer would be correct if
The organization needed to enforce identity-based access controls on a regional internal Application Load Balancer to ensure that only specific Compute Engine VMs with designated service accounts or secure tags could communicate with an internal microservice.
Configure a Google Cloud Armor security policy and associate it with the load balancer's backend service
Configure a Google Cloud Armor security policy and associate it with the load balancer's backend service
What Google Cloud Armor security policies are
Google Cloud Armor security policies are collections of traffic-filtering rules designed to protect externally facing applications and services from distributed denial-of-service (DDoS) attacks and targeted web exploits. When integrated with Google Cloud Load Balancing, these policies evaluate incoming requests across Layer 3 through Layer 7 of the network stack before the traffic ever reaches the underlying backend resources.
Cloud Armor L3 to L7 Filter Taxonomy
Hierarchy / Taxonomy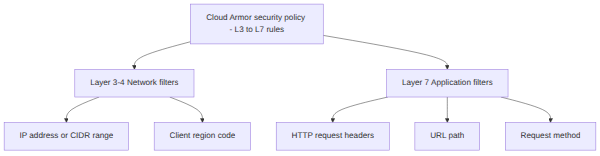
How it meets the requirements
- IP-based access controls: Administrators can configure match conditions using specific IP addresses or CIDR ranges to create allowlists and denylists that block malicious external sources.
- Geographic filtering: Security policies can evaluate the incoming request's client geography (region code) to allow or deny traffic originating from specific countries or regions.
- Custom Layer 7 traffic rules: Using the Cloud Armor custom rules language, teams can inspect deep application-layer attributes—including HTTP request headers, URL paths, and request methods—to scrub traffic and block unauthorized requests.
- Edge enforcement: When associated with the backend service of a global external Application Load Balancer, the security policy is enforced at Google's points of presence (PoPs) at the network edge, stopping unwanted traffic before it consumes backend capacity or enters the Virtual Private Cloud (VPC) network.
Key capabilities and advantages
- Flexible rule actions: Supports multiple actions when a rule condition is met, including Allow, Deny, Throttle, Rate-based ban, and Redirect (such as redirecting suspicious traffic to
GOOGLE_RECAPTCHA). - Preconfigured WAF rules: Offers out-of-the-box web application firewall (WAF) signatures to defend against common industry vulnerabilities like SQL injection and cross-site scripting.
- Multi-layered defense: Allows organizations to combine edge security policies (for cached content in Cloud CDN or Cloud Storage buckets) with backend security policies (for instance groups and network endpoint groups).
- Broad tier support: Operates seamlessly across both Premium Tier and Standard Tier network configurations.
Why this is optimal
Associating a Cloud Armor security policy directly with the load balancer's backend service is the native, purpose-built mechanism in Google Cloud for inspecting and filtering public internet traffic across network and application layers at the global edge.
Enable VPC Service Controls to establish an isolation perimeter around the backend service and filter incoming request headers
Enable VPC Service Controls to establish an isolation perimeter around the backend service and filter incoming request headers
What VPC Service Controls is
VPC Service Controls is a Google Cloud security feature that allows organizations to define fine-grained isolation perimeters around sensitive cloud resources and managed multi-tenant services (such as Cloud Storage or BigQuery). Its primary purpose is to mitigate the risk of data exfiltration by ensuring that private data cannot be copied to unauthorized resources outside the trusted perimeter.
Why it doesn't meet the requirements
- Not a web application firewall: VPC Service Controls governs access to Google Cloud APIs and managed services rather than acting as a Layer 7 web traffic scrubber for public-facing applications.
- Lacks HTTP header and URL path filtering: It does not inspect custom application-level HTTP request headers or URL paths destined for compute backend services behind a public load balancer.
- Different architectural purpose: While it can restrict API requests based on client context, it is designed to prevent compromised credentials from exfiltrating data rather than blocking volumetric DDoS traffic or enforcing public web application traffic rules at the load balancer edge.
Key characteristics and limitations
- API-level isolation: Creates a logical boundary (
PERIMETER_TYPE_REGULAR) around projects and services to block unauthorized API calls from external, attacker-controlled endpoints. - Mitigates credential theft: Limits the usefulness of stolen IAM credentials by blocking requests that originate outside the authorized network environment.
- Protects managed services: Primarily focuses on safeguarding Google-managed APIs rather than filtering arbitrary internet traffic routed through a global external Application Load Balancer.
This answer would be correct if
The organization needed to prevent data exfiltration from sensitive Google Cloud storage and analytics services by creating a logical security perimeter that blocks unauthorized cross-project data transfers and external API requests.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 3,070 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalCloud Digital Leader
Cloud Armor Edge DDoS Mitigation
Describe how an organization can protect against network attacks using Google products, including distributed denial-of-service (DDoS) using Google Cloud Armor.
FundamentalCloud Digital Leader
Cloud Armor Preconfigured WAF Rules
Describe how an organization can protect against network attacks using Google products, including distributed denial-of-service (DDoS) using Google Cloud Armor.
FundamentalCloud Digital Leader
SRE with Google Cloud Observability
Discuss the fundamental concepts of modern operations, reliability, and resilience in the cloud.
FundamentalCloud Digital Leader
IAM Allow Policy on Bucket
Differentiate between authentication, authorization, and auditing.
FundamentalCloud Digital Leader
Cloud Elasticity vs On-Premises Provisioning
Describe the differences between cloud technology and traditional or on-premises technology.
AdvancedProfessional Data Engineer
BigQuery Nested and Repeated Fields
Designing the data model
Last updated