Diagram
Certificate-Based Login Flow with OS Login
Sequence
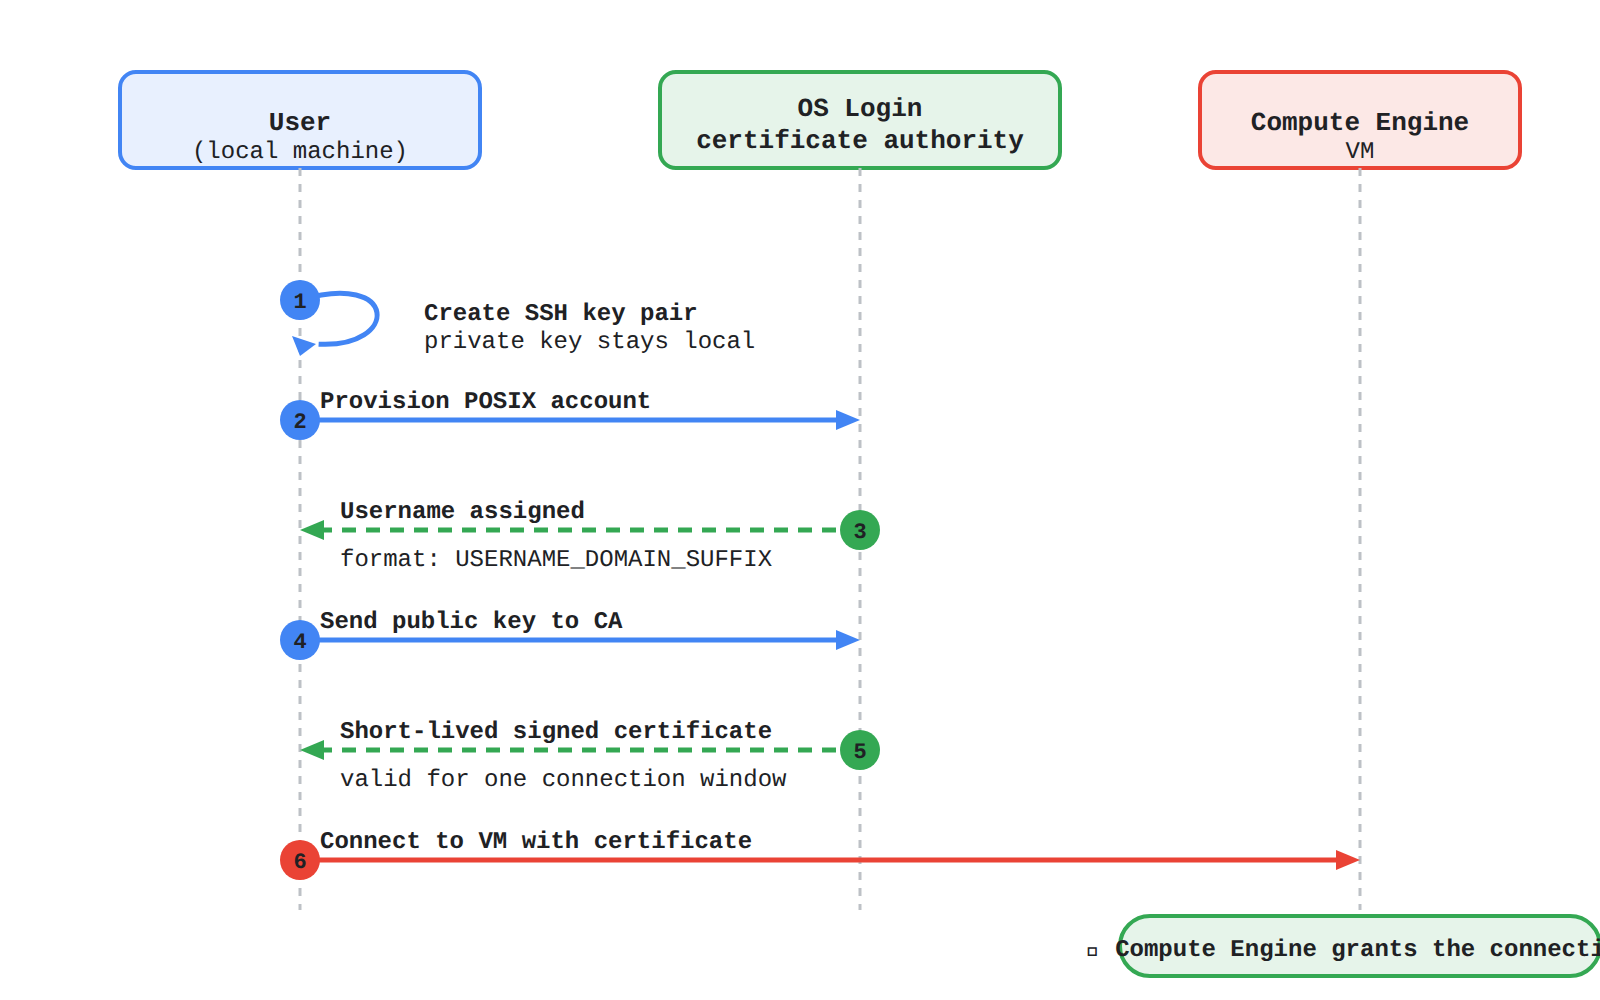
A sequence diagram showing six ordered steps of certificate-based OS Login: the user creates an SSH key pair, provisions a POSIX account, receives a username, sends the public key to the OS Login certificate authority, receives a short-lived signed certificate, and connects to the VM, which grants access.
In the Domain
Certificate-Based Login Flow
Certificate-based authentication with OS Login replaces long-lived keys on VMs with a short-lived signed SSH certificate issued by the OS Login certificate authority. The certificate proves the user's identity for one connection window, and Compute Engine authenticates the certificate to grant the connection. Usernames longer than 32 characters are truncated, service account users are prefixed with sa_, and users from a different Google Workspace organization are prefixed with ext_. The login flow runs in order:
- Create key pair: The user creates an SSH key pair and keeps the private key locally.
- Provision POSIX account: The user provisions a POSIX account if one does not already exist for the Google identity.
- Assign username: Compute Engine assigns a username in the format
USERNAME_DOMAIN_SUFFIX, for examplecloudysanfrancisco_gmail_com. - Send public key: The user sends the public key from the local machine to the OS Login certificate authority.
- Receive certificate: The OS Login certificate authority returns a short-lived signed SSH certificate.
- Connect to VM: The user presents the certificate to the VM, and Compute Engine authenticates the certificate and grants the connection.
Domain 5 of 11
Configuring OS Login
Read the Domain summaryPractice this Domain
24 practice questions
Practice this DomainLast updated