Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Centralized Firewall Control with Secure Tags
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your organization wants to enforce centralized traffic filtering rules across virtual machine (VM) instances located in multiple projects. The security team requires an access control method where VM administrators cannot independently modify or bypass their instances' security classifications, overcoming the governance limitations of legacy network tags.
Which mechanism should the organization implement in Cloud NGFW policies to achieve this?
Explanations
Custom static routes configured with next-hop gateway definitions
Custom static routes configured with next-hop gateway definitions
What Custom Static Routes Are
Custom static routes define the network paths that packets must follow to reach destination IP ranges from within a Virtual Private Cloud (VPC) network, specifying next hops such as VPN tunnels, instances, or default internet gateways.
Why It Doesn't Meet the Requirement
- Routing vs. packet filtering: Routes define path forwarding decisions (where packets go), whereas Cloud NGFW policies evaluate and enforce access decisions (whether packets are permitted or denied).
- No identity-based classification: Static routes operate based on destination CIDR IP ranges and cannot provide identity-based, dynamic classification for VMs.
- Cannot enforce granular security boundaries: Using routes to isolate traffic lacks fine-grained stateful filtering, protocol inspection, and centralized security governance.
Key Characteristics and Limitations
- Dictates Layer 3 packet forwarding topology rather than stateful security policies.
- Cannot replace firewall policy rules for access control.
- Lacks dynamic tag-based IAM evaluation for VM traffic isolation.
This Answer Would Be Correct If
The scenario required redirecting outbound network traffic destined for on-premises subnets through a specific Cloud VPN gateway or virtual appliance.
Resource Manager labels attached to the Compute Engine instances
Resource Manager labels attached to the Compute Engine instances
What Resource Manager Labels Are
Resource Manager labels are lightweight key-value pairs used primarily for resource categorization, inventory querying, and billing allocation across Google Cloud resources.
Why It Doesn't Meet the Requirement
- No firewall enforcement integration: Labels cannot be evaluated as criteria or targets within Cloud NGFW or VPC firewall rules.
- Not security-enforced: Labels are intended for organizational grouping, cost tracking, and filtering scripts, rather than access control or traffic filtering mechanisms.
- No fine-grained IAM protection: Labels do not have independent IAM authorization mechanisms to prevent modification by general resource administrators.
Key Characteristics and Limitations
- Primary use case is cost attribution, reporting, and operational filtering.
- Evaluated by client tools and billing export, not by the Cloud NGFW datapath.
- Cannot dynamically allow or deny network packets based on traffic flow.
This Answer Would Be Correct If
The organization wanted to track billing and categorize infrastructure spending by department or environment name.
Legacy network tags assigned directly in VM instance metadata
Legacy network tags assigned directly in VM instance metadata
What Legacy Network Tags Are
Legacy network tags are simple, plain-text string attributes added directly to the metadata of individual Compute Engine VM instances to apply VPC firewall rules or custom static routes.
Why It Doesn't Meet the Requirement
- Lack of centralized IAM control: Legacy network tags are not governed by dedicated IAM roles. Any user who has general compute instance editing permissions (
roles/compute.instanceAdminor compute edit access) can add, modify, or delete network tags on their VMs. - Risk of policy bypass: Because VM administrators have control over instance metadata, they can inadvertently or maliciously assign tags to bypass security restrictions or gain unauthorized traffic access.
- No hierarchical organization: Network tags are unstructured string literals that exist only within the context of a single VPC network, making cross-project and organization-wide enforcement difficult to manage safely.
Key Characteristics and Limitations
- Simple text strings without organization-level key-value validation.
- Bound directly to instance properties rather than formal Resource Manager tag bindings.
- Cannot be controlled with fine-grained Resource Manager IAM roles.
This Answer Would Be Correct If
The organization were using legacy VPC firewall rules in a single project without requiring centralized administrative separation between VM operators and security teams.
Secure tags (Resource Manager tags) governed by Identity and Access Management (IAM)
Secure tags (Resource Manager tags) governed by Identity and Access Management (IAM)
What Secure Tags Are
Secure tags (officially managed as Resource Manager tags) are strongly typed key-value pairs defined at the organization or folder level in Google Cloud. They are attached to resources, such as Compute Engine virtual machine (VM) instances, through formal tag bindings and managed via dedicated Identity and Access Management (IAM) roles.
How It Meets the Requirements
- Centralized governance: Secure tags are defined centrally at the organization hierarchy level rather than locally within individual networks or VM configurations.
- Prevents unauthorized modification: Unlike legacy network tags, which any user with VM edit permissions (
compute.instances.createorcompute.instances.setTags) can attach or remove, secure tags require distinct IAM permissions (roles/resourcemanager.tagUserandroles/resourcemanager.tagAdmin). VM administrators cannot alter tags unless explicitly granted permission on the tag values. - Cross-project dynamic enforcement: Cloud Next-Generation Firewall (NGFW) policies can dynamically reference these secure tags to evaluate source and destination traffic across different projects in an organization.
IAM-Governed Tag Access: Secure vs Network Tags
Comparison Matrix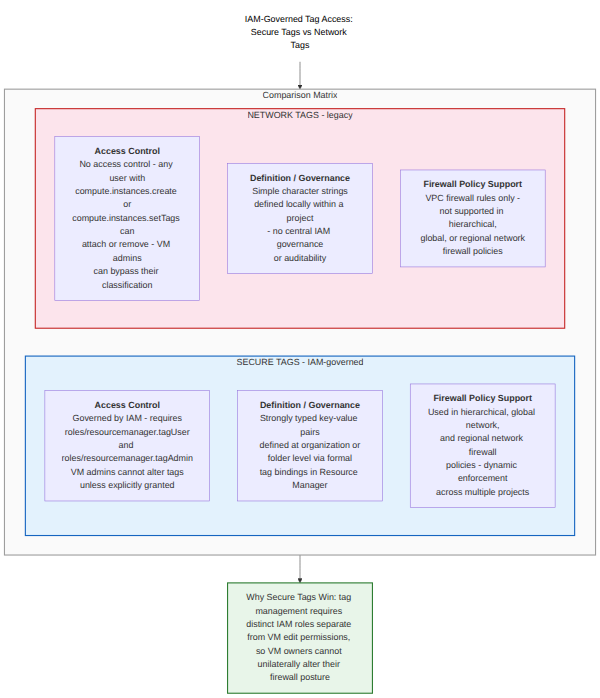
Key Advantages and Capabilities
- IAM-based access delegation: Separates network and VM deployment duties from security policy assignment.
- Dynamic policy enforcement: Firewall rules automatically adapt as instances are created with or bound to specific tag values.
- Hierarchical structure: Keys and values are scoped under the organization, preventing naming collisions and spoofing.
- Auditability: Tag creation, assignment, and modification events are tracked and audited centrally.
Why This Is Optimal
Using secure tags solves the fundamental security challenge of legacy network tags by ensuring that security classifications are strictly governed by central IAM policies. This ensures VM owners cannot unilaterally alter their firewall postures or bypass perimeter controls.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Service Account-Based Firewall Filtering
Using Tags (e.g., secure Tags) and service accounts in Cloud NGFW policy rules
FundamentalAssociate Cloud Engineer
Cloud SQL Query Insights Index Advisor
Using cloud diagnostics to research an application issue (e.g., Cloud Trace, Cloud Profiler, Query Insights, index advisor)
FundamentalAssociate Cloud Engineer
Kubernetes Node Taints and Tolerations
Working with GKE node pools (e.g., add, edit, or remove a node pool; autoscaling node pool)
FundamentalAssociate Cloud Engineer
Cloud DNS Managed Private Zones
Working with Cloud DNS and Cloud NAT
FundamentalAssociate Cloud Engineer
GKE Gateway API HTTPRoute Weighted Traffic Splitting
Adjusting application traffic splitting parameters (e.g., Cloud Run, Cloud Run functions, GKE)
FundamentalAssociate Data Practitioner
BigQuery SQL Data Validation
Assess data quality
Last updated