Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Google Cloud Directory Sync One-Way Synchronization
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your organization manages its workforce identities, departments, and security groups in an on-premises Microsoft Active Directory server. As part of establishing a new Google Cloud environment, you need to manage access to Google Cloud resources using these existing corporate identities.
You have the following requirements:
- Automatically synchronize user accounts and group memberships into Cloud Identity.
- Ensure synchronization is one-way so that Cloud Identity never modifies or overwrites your on-premises directory.
- Avoid manually recreating user accounts and group structures.
Which tool should you implement to satisfy these requirements?
Explanations
Active Directory Federation Services (ADFS)
Active Directory Federation Services (ADFS)
What Active Directory Federation Services (ADFS) Is
Active Directory Federation Services (ADFS) is an identity federation service provided by Microsoft that enables Single Sign-On (SSO) and federated identity assertions across organizational boundaries and external cloud service providers.
Why It Doesn't Meet the Requirement
- Federation vs. Provisioning: ADFS handles authentication and token issuance (via SAML 2.0 or WS-Federation) when a user attempts to log in. It does not provision, synchronize, or manage user directory objects and group memberships within Cloud Identity.
- Requires Pre-Existing Cloud Accounts: For SAML SSO via ADFS to succeed in Google Cloud, corresponding user identities must already exist in Cloud Identity. ADFS cannot create these accounts or synchronize group hierarchies on its own.
Key Characteristics and Limitations
- Validates user credentials against on-premises Active Directory during active authentication handshakes.
- Generates secure SAML assertions passed via browser redirects to Google's sign-in endpoints.
- Does not manage group memberships or synchronize directory schemas into target cloud platforms.
This Answer Would Be Correct If
The requirement was to configure Single Sign-On (SSO) so that users authenticate against their corporate on-premises Active Directory credentials instead of entering a distinct Google password when accessing Google Cloud.
Cloud Identity SAML 2.0 Single Sign-On (SSO) Profile
Cloud Identity SAML 2.0 Single Sign-On (SSO) Profile
What Cloud Identity SAML 2.0 SSO Profile Is
The SAML 2.0 Single Sign-On (SSO) Profile in Cloud Identity is an administrative configuration setting that redirects authentication requests from Google Cloud to an external third-party Identity Provider (IdP).
Why It Doesn't Meet the Requirement
- Authentication Mechanism, Not Synchronization: The SAML SSO profile coordinates authentication handshakes and token validation. It does not synchronize directory objects, users, or security groups into Cloud Identity.
- Account Existence Dependency: Google Cloud Identity requires the user's primary email address (the principal identifier) to exist in the directory before authenticating via SAML assertions. The SSO profile cannot populate the directory automatically.
Key Characteristics and Limitations
- Redirects browser sessions to an external IdP sign-in URL.
- Validates incoming SAML responses using public X.509 certificates.
- Does not provide scheduled or automated account provisioning from LDAP sources.
This Answer Would Be Correct If
The organization already had all user accounts in Cloud Identity and needed to delegate authentication to an external third-party identity provider (such as Okta, Ping Identity, or Azure AD/Entra ID) using the SAML 2.0 standard.
Google Workspace Admin Console CSV Bulk Upload
Google Workspace Admin Console CSV Bulk Upload
What Google Workspace Admin Console CSV Bulk Upload Is
The CSV Bulk Upload feature in the Google Admin Console allows administrators to create, update, or delete multiple user accounts simultaneously by manually uploading a structured comma-separated values (CSV) spreadsheet.
Why It Doesn't Meet the Requirement
- Manual and Static: CSV uploads require manual file generation, formatting, and administrative intervention for every batch of updates. This fails the requirement for automated directory management.
- No Continuous Synchronization: It does not maintain an active connection with Active Directory or track ongoing user changes, group membership modifications, or departures in real time.
- High Operational Overhead and Risk: Manual exports and imports are prone to human error, schema mismatch, and delayed de-provisioning.
Key Characteristics and Limitations
- Suitable for one-time initial batch imports or small organizations without an LDAP server.
- Requires administrative access to export data from AD and upload spreadsheets manually to the console.
- Cannot schedule automated recurring delta synchronization runs.
This Answer Would Be Correct If
The organization had a small, static user base without an existing LDAP/Active Directory deployment and needed a simple one-off method to create fifty accounts without deploying sync infrastructure.
Google Cloud Directory Sync (GCDS)
Google Cloud Directory Sync (GCDS)
What Google Cloud Directory Sync (GCDS) Is
Google Cloud Directory Sync (GCDS) is a dedicated, on-premises Java application designed to synchronize identity data from existing LDAP servers or Microsoft Active Directory environments to Cloud Identity or Google Workspace.
How It Meets the Requirements
- Automated Directory Synchronization: GCDS connects directly to your directory service via LDAP queries, comparing directory objects against Cloud Identity and automatically applying additions, updates, or deletions based on configured sync rules.
- One-Way Synchronization: GCDS enforces a strict one-way sync model (from on-premises LDAP/AD to Google Cloud Identity). It never writes back, modifies, or deletes objects in your on-premises Active Directory system, ensuring on-premises remains the authoritative source of truth.
- Elimination of Manual Effort: User profiles, organizational units, and group memberships are provisioned and updated programmatically on a scheduled basis, removing manual administrative overhead.
One-Way AD to Cloud Identity Sync via GCDS
System Architecture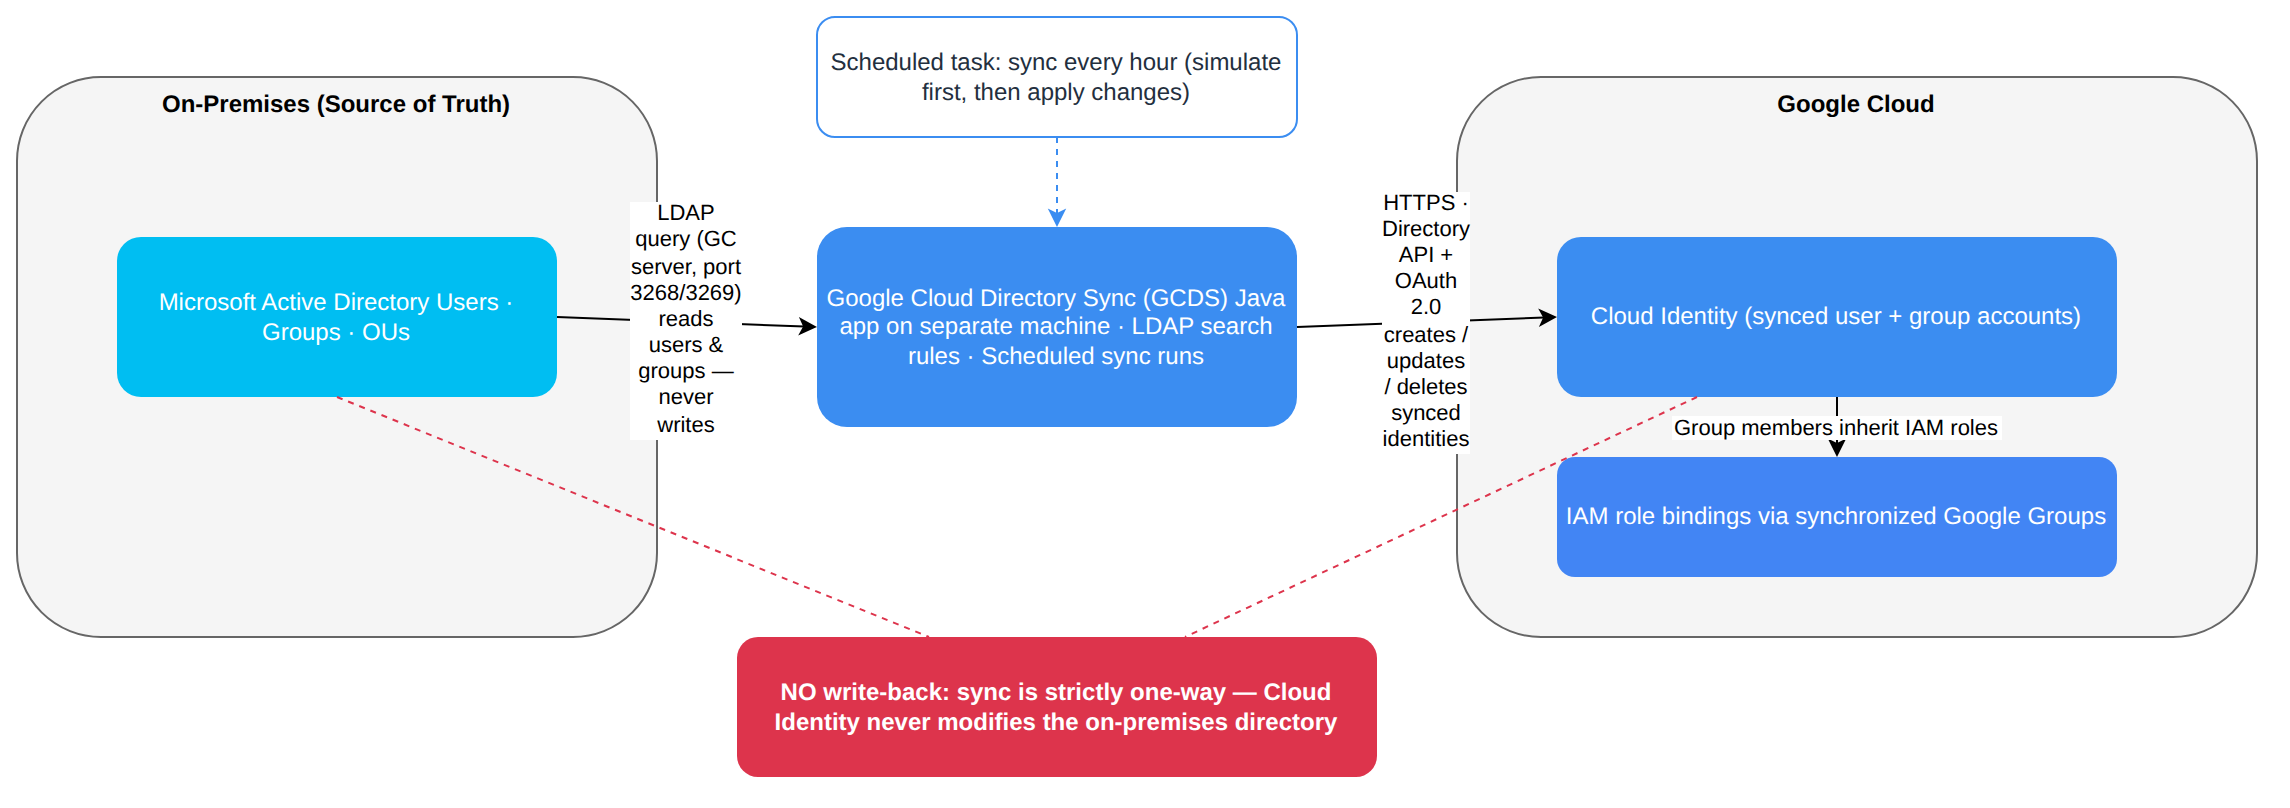
Key Advantages and Capabilities
- Customizable Rule Configuration: Allows administrators to define precise LDAP search rules to include or exclude specific Organizational Units (OUs), groups, or user attributes.
- Simulated Sync (Dry Run): Supports a simulation mode to generate audit reports and review changes before applying updates to production Cloud Identity directories.
- Group Synchronization: Automatically maps Active Directory distribution lists and security groups to Google Groups, enabling seamless IAM role bindings in Google Cloud.
- Secure Credential Storage: Connects to the Google domain using OAuth 2.0 with administrator authorization without exposing master passwords.
Why This Is Optimal
GCDS is the standard and recommended solution for organizations establishing a hybrid identity architecture. It bridges on-premises identity infrastructure with Cloud Identity cleanly without modifying existing source directories.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Cloud Identity Organizational Units Google Groups IAM
Managing users and groups in Cloud Identity (manually and automated)
FundamentalAssociate Cloud Engineer
Cloud Identity Groups For IAM
Managing users and groups in Cloud Identity (manually and automated)
FundamentalAssociate Cloud Engineer
External Application Load Balancer Frontend Backend Configuration
Choosing and deploying load balancers
FundamentalAssociate Cloud Engineer
Workload Identity Federation for External Workloads
Creating and managing short-lived service account credentials
FundamentalAssociate Cloud Engineer
gcloud Billing Projects Link
Linking projects to a billing account
AdvancedProfessional Cloud Security Engineer
Private Service Connect vs VPC Peering
Configuring network isolation and data encapsulation for N-tier applications.
Last updated