Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Keyless CI/CD Access With Workload Identity Federation
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
An organization runs automated deployment pipelines in an external CI/CD environment hosted outside of Google Cloud. The pipeline jobs need to authenticate to Google Cloud to deploy artifacts and update infrastructure.
To follow security best practices, your security team has mandated the following requirements:
- Prevent the creation, export, and storage of long-lived service account JSON keys.
- Use short-lived credentials that are automatically requested and expire when deployment tasks finish.
- Use a programmatic identity integration pattern designed specifically for external non-human workloads.
Which access pattern should you implement to satisfy these requirements?
Explanations
Configure Workforce Identity Federation to authenticate the CI/CD pipeline against an external enterprise identity provider using interactive user sign-in
Configure Workforce Identity Federation to authenticate the CI/CD pipeline against an external enterprise identity provider using interactive user sign-in
What Workforce Identity Federation Is
Workforce Identity Federation is Google Cloud's identity federation solution designed for human users, including employees, contractors, and partners. It allows users to authenticate to the Google Cloud Console, Cloud Shell, and gcloud CLI using an external enterprise identity provider (such as Okta, Microsoft Entra ID, or PingIdentity) via standard Single Sign-On (SSO) and multi-factor authentication (MFA).
Why It Doesn't Meet the Requirement
- Designed for human users, not automated workloads: Google Cloud identity services explicitly differentiate between human users (workforce) and programmatic services (workloads). Workforce Identity Federation manages human personnel rather than non-human CI/CD automation.
- Requires interactive authentication: Workforce flows typically require browser-based redirects, user consent prompts, or interactive CLI login sequences that cannot execute in automated, headless CI/CD runners.
Key Characteristics and Limitations
- User-centric administration: Designed around user session lifetimes, employee identity life cycles, and corporate SSO re-authentication policies.
- Principal structure: Generates workforce identity pool principal identifiers tied to human employee email addresses or enterprise subject IDs.
- Interactive focus: Lacks native claim-mapping features optimized for software deployment pipelines (such as verifying source code repositories or build branches).
This Answer Would Be Correct If
You needed human developers and cloud engineers to access Google Cloud resources and console interfaces using their corporate single sign-on credentials without creating dedicated Cloud Identity or Google Workspace accounts.
Generate a service account private JSON key, register it in the external environment's secrets vault, and use it to sign service account JWT assertions locally
Generate a service account private JSON key, register it in the external environment's secrets vault, and use it to sign service account JWT assertions locally
What Service Account Keys and JWT Assertions Are
A service account private JSON key contains an asymmetric RSA private key downloaded from the Google Cloud console. External workloads can store this private key locally and use it to sign a service account JSON Web Token (JWT) assertion, which is subsequently transmitted to Google's OAuth 2.0 token endpoint to obtain short-lived service account access tokens.
Why It Doesn't Meet the Requirement
- Explicitly violates security mandates: The scenario specifically requires preventing the creation, export, and storage of long-lived service account JSON keys. Generating and storing a private key file directly breaches this mandate.
- Persistent exposure risks: Service account keys do not expire automatically and can remain valid for up to 10 years unless manually rotated. Storing them inside external CI/CD variable stores creates significant risks of accidental leakage through build logs, compromised runner hosts, or code commits.
Key Characteristics and Limitations
- Long-lived credentials: Keys present an ongoing management burden, requiring continuous auditing, rotation pipelines, and secure storage mechanisms.
- High blast radius: Stolen service account keys allow unauthorized parties to generate valid access tokens from any network location, bypassing perimeter firewalls.
- No default session limits: Unlike federated tokens, service account keys are static cryptographic secrets that require manual revocation.
This Answer Would Be Correct If
You were integrating a legacy external platform that lacks OpenID Connect (OIDC) or SAML capabilities, preventing the use of Workload Identity Federation, and your security policy explicitly permitted managing static private keys.
Configure the CI/CD pipeline to query the Compute Engine metadata server over HTTP to retrieve short-lived OAuth2 access tokens
Configure the CI/CD pipeline to query the Compute Engine metadata server over HTTP to retrieve short-lived OAuth2 access tokens
What the Compute Engine Metadata Server Is
The Compute Engine metadata server is an internal, link-local HTTP service hosted inside Google Cloud virtualized infrastructure at http://metadata.google.internal/computeMetadata/v1/ (IP address 169.254.169.254). Compute Engine instances, Google Kubernetes Engine nodes, and serverless compute environments query this endpoint to inspect instance attributes and retrieve short-lived OAuth2 access tokens for attached service accounts.
Why It Doesn't Meet the Requirement
- Inaccessible from external environments: The metadata server is strictly a link-local service accessible only from within virtual machines and compute environments running inside Google Cloud. It cannot be reached or queried by external CI/CD platforms or on-premises servers across the public internet.
- Network boundary restrictions: The
169.254.0.0/16IP block is non-routable over external network paths, meaning any HTTP request originating from external runners will immediately fail.
Key Characteristics and Limitations
- Internal infrastructure bound: Strictly reserved for workloads physically hosted within Google Cloud environments.
- Automatic token rotation: Supplies short-lived tokens to attached VMs without key management overhead, but only within the local hypervisor.
- SSRF mitigation: Enforces custom headers (such as
Metadata-Flavor: Google) to safeguard internal instances against Server-Side Request Forgery.
This Answer Would Be Correct If
The build runners were self-hosted virtual machines running on Compute Engine or worker nodes in a Google Kubernetes Engine (GKE) cluster inside your Google Cloud project, allowing build scripts to read access tokens directly from the local metadata server.
Configure Workload Identity Federation to exchange external identity tokens issued by the CI/CD platform for short-lived Google Cloud access tokens
Configure Workload Identity Federation to exchange external identity tokens issued by the CI/CD platform for short-lived Google Cloud access tokens
What Workload Identity Federation Is
Workload Identity Federation is Google Cloud's recommended identity mechanism that enables external software workloads—such as automated CI/CD runners, on-premises applications, and multi-cloud services—to access Google Cloud APIs without managing downloadable service account keys. It establishes a secure trust relationship between Google Cloud and an external Identity Provider (IdP) that supports OpenID Connect (OIDC) or SAML 2.0.
How It Meets the Requirements
- Eliminates long-lived service account keys: Workload Identity Federation avoids creating, downloading, storing, or rotating private RSA key pairs (
JSONcredential files) in external platforms. - Delivers short-lived credentials: The external CI/CD runner obtains a native identity token (such as an OIDC JSON Web Token issued by GitHub Actions or GitLab CI) and exchanges it via Google Cloud's Security Token Service (STS) for a temporary, short-lived federated access token that automatically expires.
- Engineered for non-human workloads: Google Cloud distinguishes between human access (workforce) and programmatic system access (workloads). Workload Identity Federation is built specifically to handle non-interactive software systems.
Key Advantages and Capabilities
- Zero credential management overhead: Removes the risk of developers accidentally committing secret keys to source repositories or runner logs.
- Granular attribute conditions: Allows security teams to map external token claims (such as source repository, branch name, or environment) to IAM roles so only verified build jobs acquire permissions.
- Native token exchange: Works seamlessly with the Google Cloud client libraries and
google-github-actions/authtools. - Automatic lifecycle management: Because tokens are short-lived, there is no need to manually revoke credentials when an automated job completes.
CI Claims to IAM Access Mapping
Concept Map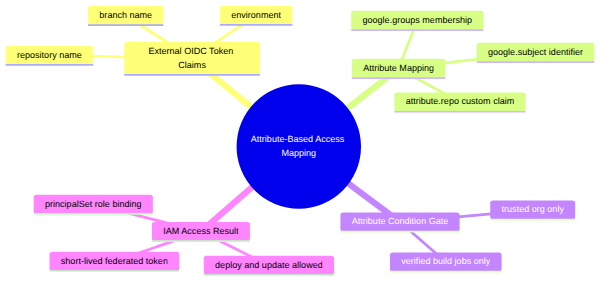
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Service Account Impersonation Keyless Access
Using service accounts in IAM policies with minimum permissions
FundamentalAssociate Cloud Engineer
Network-Tagged Custom Static Routes
Adding custom static routes in a VPC
FundamentalAssociate Cloud Engineer
GKE Cluster Autoscaler Node Pool Scaling
Working with GKE node pools (e.g., add, edit, or remove a node pool; autoscaling node pool)
FundamentalAssociate Cloud Engineer
Organization Policy Inheritance
Applying organizational policies to the resource hierarchy
FundamentalAssociate Cloud Engineer
Folder-Level Project Creator and Billing Account User
Creating a resource hierarchy
FundamentalAssociate Data Practitioner
BigQuery ML
Identify ML use cases for developing models by using BigQuery ML and AutoML
Last updated