Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Shared VPC Access With Subnet-Level IAM
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your company is organizing its Google Cloud environment. You need to centralize network management within a dedicated host project while allowing an application team working in a separate development project to deploy virtual machine (VM) instances into a designated subnet (10.0.1.0/24 in us-west1).
You must implement this architecture while adhering to the principle of least privilege.
What should you do?
Explanations
Attach the development project as a service project to the host project, and grant the application team the Compute Network User role on the specific subnet in the host project.
Attach the development project as a service project to the host project, and grant the application team the Compute Network User role on the specific subnet in the host project.
What Shared VPC with Subnet-Level IAM Is
Shared VPC allows an organization to connect resources from multiple service projects to a common, centralized Virtual Private Cloud (VPC) network hosted in a dedicated host project. Instead of granting broad project-wide access, administrators can apply Identity and Access Management (IAM) roles at the individual subnet level.
How It Meets the Requirements
- Centralizes network administration: The host project retains ownership of the VPC network, routes, firewall rules, and subnets, allowing central network administrators to manage infrastructure.
- Attaches service projects: Linking the development project as a service project allows its workloads to leverage network resources created in the host project.
- Adheres to least privilege: Granting the Compute Network User role (
roles/compute.networkUser) specifically on the10.0.1.0/24subnet allows the application team to attach VM instances only to that designated subnet without giving them access to other subnets or full administrative rights over the network.
Key Advantages and Capabilities
- Granular access control: Subnet-level IAM ensures service project teams only consume the IP ranges intended for their specific workloads.
- Simplified internal connectivity: Instances deployed across different service projects in the same Shared VPC can communicate securely via private internal IP addresses without public internet routing.
- Operational segregation: Development teams manage their VM lifecycles in their own project while network engineers manage topology, CIDR allocations, and security policies centrally.
- Cost attribution: Outbound network traffic and compute resource costs are billed directly to the respective service project where the VM instances reside.
Why This Is Optimal
This approach directly separates network management duties from compute deployment while ensuring the application team receives only the exact permissions needed on the designated subnet.
Configure VPC Network Peering between the host project VPC and a new VPC in the development project, and grant the Compute Network Admin role on the host project.
Configure VPC Network Peering between the host project VPC and a new VPC in the development project, and grant the Compute Network Admin role on the host project.
What VPC Network Peering Is
VPC Network Peering connects two separate VPC networks directly, allowing internal IP communication across independent networks without using an external gateway or public IP addresses.
Why It Doesn't Meet the Requirement
- Fails centralization requirement: VPC Network Peering requires creating and managing a separate VPC network inside the development project, which decentralizes network definitions rather than managing subnets centrally in a host project.
- Violates least privilege: Assigning the Compute Network Admin role (
roles/compute.networkAdmin) on the host project gives the application team broad permissions to create, modify, and delete networking resources in the host project. - Wrong architecture: The scenario explicitly calls for a centralized architecture where the service project consumes a subnet defined in the host project.
Key Characteristics and Limitations
- Independent administration: Peered networks remain independently managed entities with separate routing tables and firewall rules.
- No transitive peering: VPC Peering does not support transitive routing (e.g., reaching on-premises networks through a hub VPC without custom network appliances).
- Excessive privileges: Network Admin permissions allow modifying all networking resources rather than simply consuming a designated subnet.
This Answer Would Be Correct If
Two distinct organizations or autonomous business units maintained completely separate administrative boundaries and wanted to interconnect their independently managed VPC networks directly.
Attach the development project as a service project to the host project, and grant the application team the Compute Admin role on the host project.
Attach the development project as a service project to the host project, and grant the application team the Compute Admin role on the host project.
What the Compute Admin Role on the Host Project Does
The Compute Admin role (roles/compute.admin) grants full control over all Compute Engine resources within a project, including VM instances, disks, networks, firewalls, and subnets.
Why It Doesn't Meet the Requirement
- Violates least privilege: Granting Compute Admin at the host project level gives the application team full administrative power over the entire network infrastructure, including the ability to modify or delete networks, routes, and firewalls.
- Excessive scope: The application team only needs to deploy VMs in a single subnet; they should not have compute or network administrative rights across the host project.
Key Characteristics and Limitations
- Broad administrative reach: Compute Admin includes permissions to modify all VPC configurations and delete vital resources in the host project.
- Lack of restriction: It fails to restrict the application team to the specific
10.0.1.0/24subnet, allowing them to use any subnet in the host network. - Security risk: Combining service project administration with host project network administration defeats the security segregation intended by Shared VPC.
This Answer Would Be Correct If
The application team was responsible for managing the entire host project infrastructure, including defining global firewall policies, configuring Cloud VPN gateways, and managing all subnet allocations.
Additional Context
In a proper Shared VPC deployment, developers only need compute rights in their own service project and the Compute Network User role on the relevant shared subnets.
Deploy a Cloud VPN gateway in both the host and development projects, and grant the Service Project Admin role on the host project.
Deploy a Cloud VPN gateway in both the host and development projects, and grant the Service Project Admin role on the host project.
What Cloud VPN Is
Cloud VPN connects an on-premises network or remote VPC network to a Google Cloud VPC network through an encrypted IPsec VPN tunnel over the public internet or private interconnects.
Why It Doesn't Meet the Requirement
- Unnecessary complexity and cost: Creating a Cloud VPN tunnel between two projects within the same Google Cloud organization introduces unnecessary latency, egress bandwidth costs, and configuration overhead compared to native Shared VPC.
- Incorrect role and placement: There is no generic predefined IAM role called "Service Project Admin" granted on a host project; instead, permissions are granted via standard roles like
Compute Network User. - Fails shared subnet requirement: Cloud VPN connects distinct networks with distinct CIDRs; it does not allow service project VMs to be directly provisioned inside a host project's subnet.
Key Characteristics and Limitations
- Bandwidth limitations: Cloud VPN tunnels are capped per tunnel (e.g., 3 Gbps per tunnel) and subject to IPsec encryption overhead.
- Operational overhead: Requires configuring Cloud Routers, Border Gateway Protocol (BGP) sessions, and VPN gateways in both projects.
- Designed for hybrid/inter-VPC connectivity: Cloud VPN is primarily intended to connect Google Cloud VPCs to external on-premises data centers or across different cloud providers.
This Answer Would Be Correct If
The development project resided in a completely separate cloud provider or external on-premises data center requiring encrypted IPsec communication into the host project.
Additional Context
Shared VPC allows instances in service projects to attach directly to host subnets without any virtual appliances, gateways, or tunnel configurations.
Try the scenario
Shared VPC: centralize networking and let the dev team deploy VMs with least privilege
Change the inputs and watch how the outcome changes.
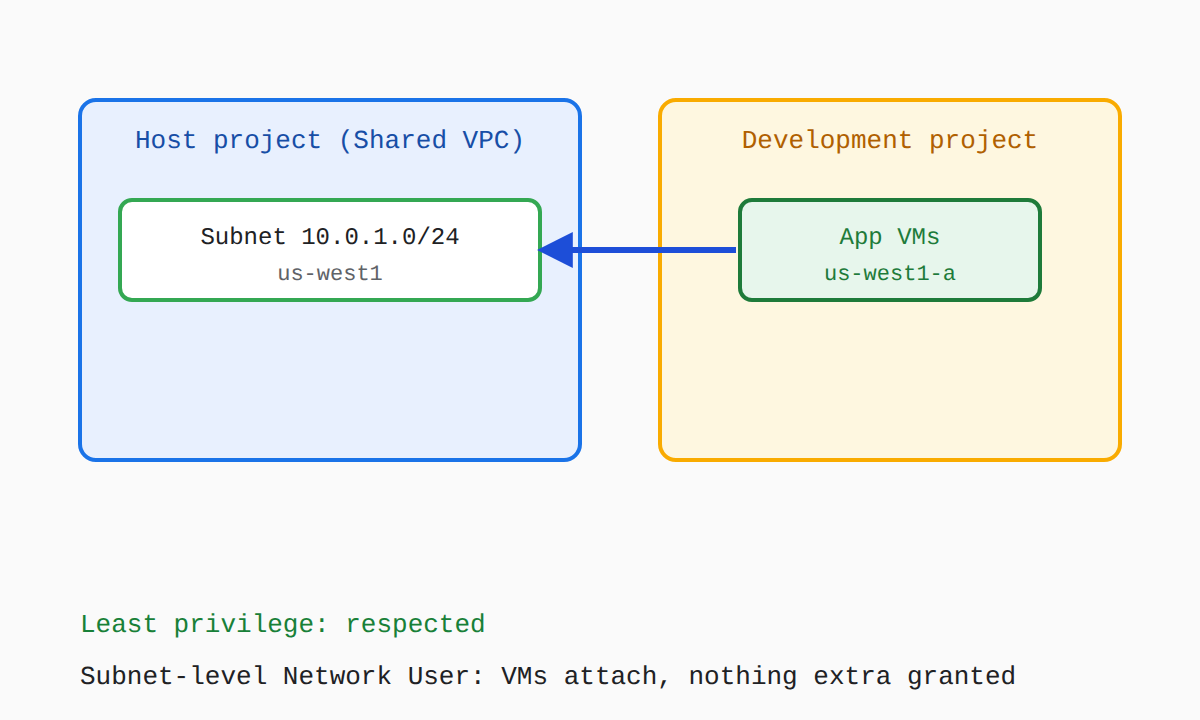
Pick an approach and a requirement to see how the architecture and permissions behave.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Gcloud Custom VPC Subnet Creation
Creating a VPC with subnets (e.g., custom mode VPC, Shared VPC)
FundamentalAssociate Cloud Engineer
Cloud Monitoring Alerting Policy Documentation
Creating Cloud Monitoring alerts based on resource metrics
FundamentalAssociate Cloud Engineer
Eventarc Cloud Run Invoker Role
Deploying an application to serverless compute platforms, including for the processing of Google Cloud events (e.g., Pub/Sub events, Cloud Storage object change notification events, Eventarc)
FundamentalAssociate Cloud Engineer
VPC Firewall Target Tags
Setting up cloud networking
FundamentalAssociate Cloud Engineer
MIG Autohealing Initial Delay
Creating an autoscaled managed instance group by using an instance template
FundamentalGenerative AI Leader
Role Prompting
Identifying prompting techniques and use cases (e.g., zero-shot, one-shot, few-shot, role prompting, prompt chaining)
Last updated