Diagram
Envelope Encryption: Wrap & Unwrap Flow
Sequence
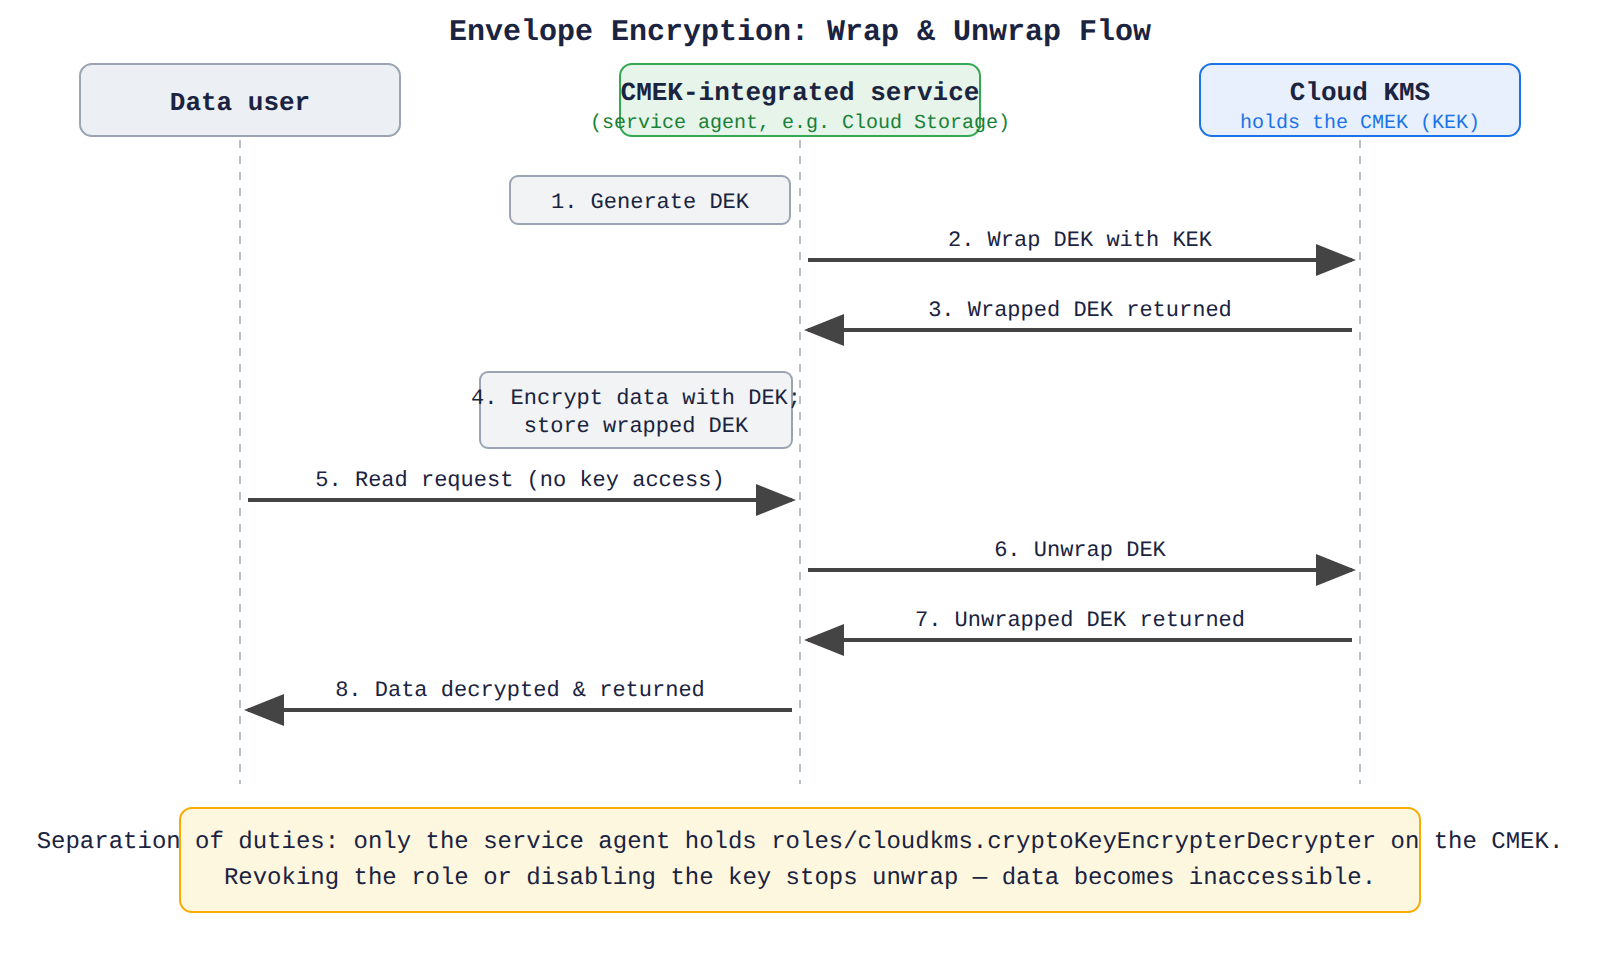
A sequence diagram showing envelope encryption between a data user, a Google Cloud service, and Cloud KMS: the service generates a DEK, sends it to Cloud KMS to be wrapped with the customer-managed KEK, encrypts data at rest, and later unwraps the DEK to serve a read request, illustrating that the data user never needs direct access to the key.
In the Domain
How Cloud KMS Uses IAM for Envelope Encryption
How Cloud KMS uses IAM for envelope encryption is by granting cryptographic use without granting key management. Services with a CMEK integration protect data with envelope encryption, where the service creates a data encryption key (DEK) for the data and Cloud KMS wraps that DEK with a customer-managed key encryption key (KEK). Traffic flows from the Google Cloud service to Cloud KMS for wrap and unwrap operations, then the service uses the unwrapped DEK to protect data at rest. A person requesting the data does not need direct access to the CMEK because access flows through the service account that holds permission on the key.
Domain 6 of 9
Managing customer-managed encryption keys with Cloud Key Management Service (Cloud KMS)
Read the Domain summaryPractice this Domain
24 practice questions
Practice this DomainLast updated