Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Customer-Managed Encryption Keys with Cloud KMS
IAM Integration and Separation of Duties for customer-managed encryption keys (CMEKs) is the use of Identity and Access Management (IAM) to separate control of encryption keys from use of protected data. Cloud Key Management Service (Cloud KMS) (opens in a new tab) is integrated with IAM and Cloud Audit Logging, so permissions can be assigned on individual keys and key use can be monitored. Key administrators manage rotation, disabling, destruction, and access policy, while services receive only the ability to encrypt and decrypt.
How Cloud KMS Uses IAM for Envelope Encryption
How Cloud KMS (opens in a new tab) uses IAM for envelope encryption is by granting cryptographic use without granting key management. Services with a CMEK integration protect data with envelope encryption, where the service creates a data encryption key (DEK) for the data and Cloud KMS wraps that DEK with a customer-managed key encryption key (KEK). Traffic flows from the Google Cloud service to Cloud KMS for wrap and unwrap operations, then the service uses the unwrapped DEK to protect data at rest. A person requesting the data does not need direct access to the CMEK because access flows through the service account that holds permission on the key.
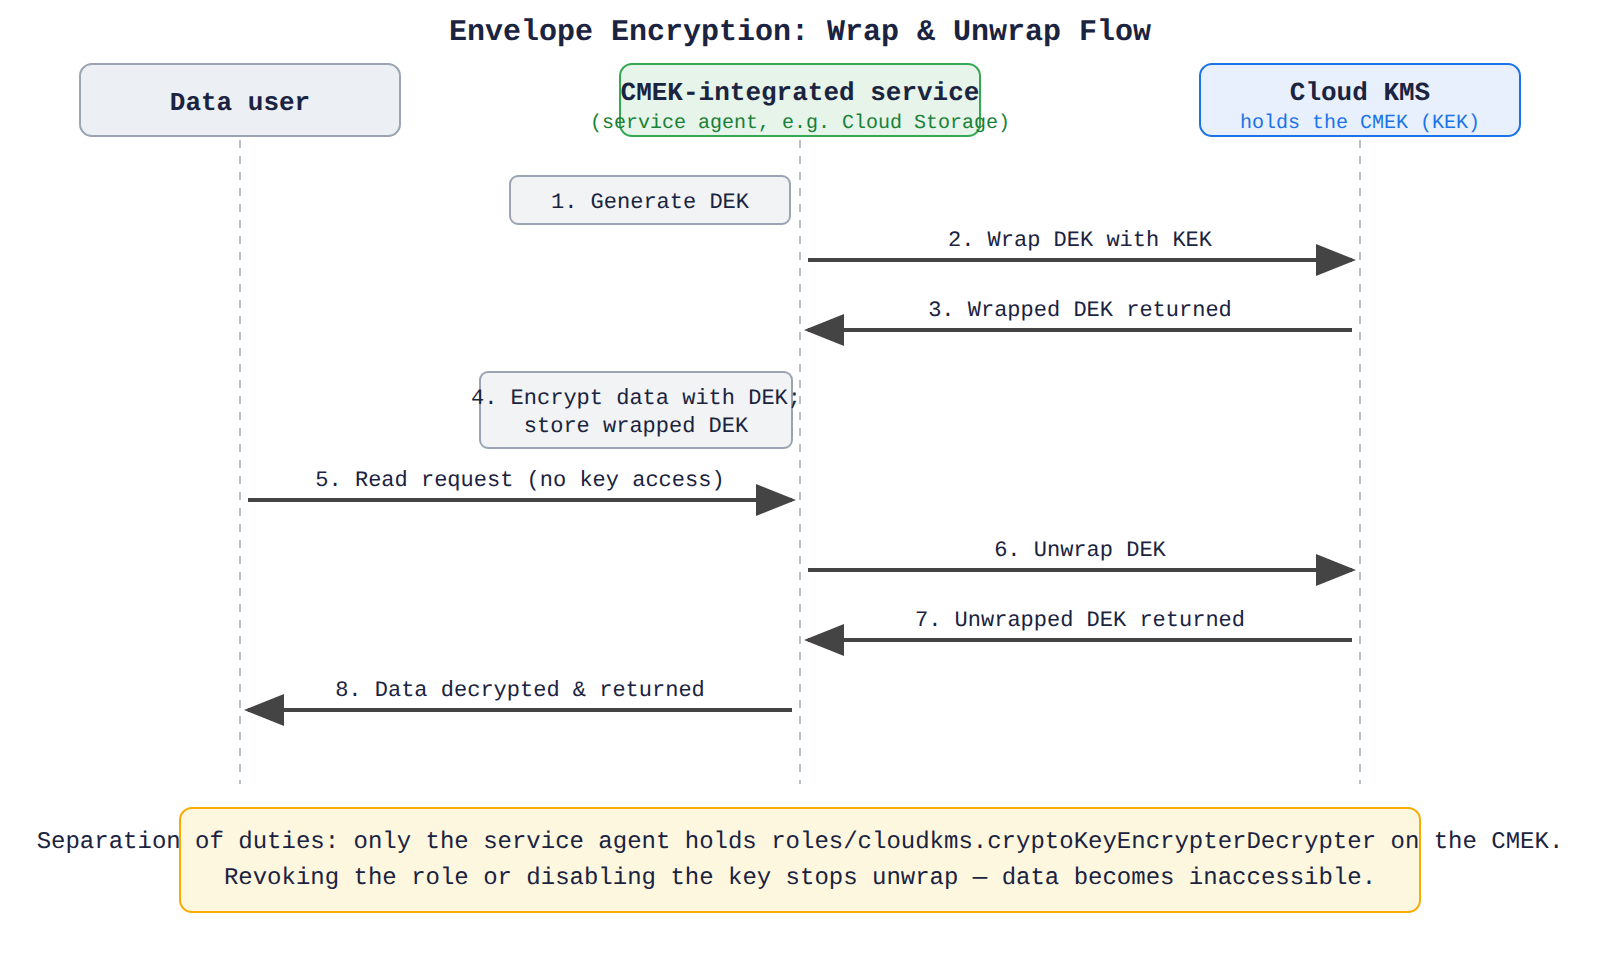
A sequence diagram showing envelope encryption between a data user, a Google Cloud service, and Cloud KMS: the service generates a DEK, sends it to Cloud KMS to be wrapped with the customer-managed KEK, encrypts data at rest, and later unwraps the DEK to serve a read request, illustrating that the data user never needs direct access to the key.
Enabling a CMEK integration follows an ordered workflow that connects key ownership to service use:
- Create or choose a key ring: Create the key ring in a location geographically near the resources it will protect.
- Create or choose a key: Create the CMEK in that key ring with a protection level, purpose, and algorithm that matches the resource.
- Grant use permission: Grant the CryptoKey Encrypter/Decrypter role (
roles/cloudkms.cryptoKeyEncrypterDecrypter) on the CMEK to the service account for the service. - Configure the resource: Configure the resource to use the CMEK resource ID when the resource is created or updated.
Only after the service account holds the role can the service encrypt new data and decrypt existing data.
Separation of Duties with Separate Projects
Separation of duties with separate projects means placing Cloud KMS keys in a different trust boundary from the data they protect. The recommended pattern creates and manages keys in a separate Google Cloud project that contains no other resources, while protected resources live in one or more data projects. The key project is owned by key administrators and each data project is owned by application or service teams, so no single identity controls both the data and the keys that can make that data unreadable.
This project boundary gives greater control over IAM roles and supports compliance goals such as data sovereignty and cryptographic isolation. Key administrators grant narrow use permission outward from the key project to the service account in the data project, and they retain exclusive control over lifecycle actions such as rotation, disabling, and destruction. With Cloud KMS Autokey, key rings and keys are generated on demand and service agents are created and granted the required IAM roles automatically, but the same boundary still applies because the keys remain centrally managed apart from the resources.
Applying Least Privilege to Cryptographic Resources
Applying least privilege to cryptographic resources means granting only the encrypt and decrypt ability needed for service operation at the narrowest resource scope possible. The CryptoKey Encrypter/Decrypter role allows the service account to encrypt and decrypt data but does not allow it to manage key settings, rotate versions, or change IAM policy. That role can be granted at the key, key ring, project, folder, or organization level, and granting it at the lowest level that meets the need limits which keys a compromised service account could use.
Revocation is the enforcement side of this model. As long as the service account holds the role and the key version is enabled, the service can unwrap DEKs and access its data. If the role is revoked, or if the key is disabled or destroyed, the service can no longer unwrap DEKs and the protected data becomes inaccessible until access is restored.
Exam tip: Grant roles/cloudkms.cryptoKeyEncrypterDecrypter to the service account at the single-key level when possible, and remember that removing that grant or disabling the key blocks data access without changing access to the data resource itself.
CMEK integration with Google Cloud Services is a supported connection between Cloud Key Management Service (Cloud KMS) (opens in a new tab) and another Google Cloud service for customer-controlled encryption of data at rest. Google Cloud encrypts data at rest by default with FIPS 140 validated AES-256, but with a customer-managed encryption key (CMEK) integration you control the key encryption keys (KEKs) that wrap data encryption keys (DEKs). This practice is called envelope encryption, where the service creates a DEK for the data and then Cloud KMS wraps that DEK with your KEK.
What a CMEK Integration Is
What a CMEK integration (opens in a new tab) is, is a supported path for a service to call Cloud KMS to wrap and unwrap the DEKs that protect stored data. Services that support CMEK integrations include Cloud Storage, BigQuery, and Compute Engine, and some services such as GKE have multiple integrations for different data types. You can manage CMEKs directly in Cloud KMS or through Cloud KMS Autokey, which generates key rings, keys, and service-agent permissions on demand. With Cloud External Key Manager (Cloud EKM), the same integration model can use keys that remain in an external key manager outside Google Cloud.
How to Enable CMEK for a Service
How to enable CMEK for a service follows the same architectural pattern across services, even though exact console fields differ. The key ring should be located as geographically near as possible to the resources being protected, and a separate project for Cloud KMS resources is recommended to support separation of duties. The service accesses the key through its own service account, so data requesters do not need direct access to the CMEK.
The typical workflow proceeds in order:
- Create or select a key ring: Create a key ring near the resources to protect, in the same project as the resources or in a dedicated key-management project.
- Create or select a key: Create the CMEK in that key ring with the correct protection level, purpose, and algorithm, then get the resource ID of the key for later use.
- Grant key access to the service: Grant the CryptoKey Encrypter/Decrypter role (
roles/cloudkms.cryptoKeyEncrypterDecrypter) on the CMEK to the service account for the service, at the lowest level that meets least-privilege needs. - Configure the resource to use the key: When creating or configuring the resource, select the CMEK by project, location, key ring, and protection level, or enter its resource ID manually.
Only after the key exists and the service account holds the role can the service encrypt and decrypt its data. Some services allow CMEK only at resource-creation time, while other services allow CMEK to be enabled or disabled on existing resources.
What CMEK Means for Cloud Storage, BigQuery, and Compute Engine
What CMEK means for Cloud Storage, BigQuery, and Compute Engine is that your Cloud KMS key controls access to service data at rest, from buckets to tables to virtual-machine disks. The service sends encrypt and decrypt requests from its service account to Cloud KMS, and Cloud KMS unwraps the DEK only while that service account retains the Encrypter/Decrypter role and the key remains enabled. If you revoke the role, or disable or destroy the key, the service can no longer decrypt the data, and some services can suffer permanent data loss if the key stays inaccessible too long.
The three services differ in the data they protect and in support for external keys:
| Service | Data protected with CMEK | External keys with Cloud EKM |
|---|---|---|
| Cloud Storage | Data in storage buckets | Supported |
| BigQuery | Data in tables and datasets | Supported |
| Compute Engine | Persistent disks, snapshots, custom images, and machine images | Supported for listed disk and image types |
All three services support software keys and hardware keys in Cloud HSM, which uses Cloud KMS as its frontend on FIPS 140 validated modules. Encryption and decryption with hardware or external keys consume Cloud KMS cryptographic-request quotas, so quota planning is part of the operational design. When an external key becomes unavailable in your external manager, dependent resources such as encrypted disks cannot be used until access is restored.
Exam tip: The data user needs permission on the service resource, not on the key; only the service account needs roles/cloudkms.cryptoKeyEncrypterDecrypter, and removing that access blocks the service from its own data.
How to Govern CMEK Use Across an Organization
How to govern CMEK use across an organization is to combine organization policies with visibility into where keys are applied. Organization policy constraints can require CMEK protection, restrict which Cloud KMS keys may be used, limit allowed protection levels and key locations, and control key-version destruction. Key usage tracking shows which resources, projects, and products within an organization are protected by a specific CMEK and whether the key is in use. Together, policies enforce consistent encryption boundaries while usage tracking supports rotation, off-boarding by crypto-shredding, and audit of administrative and data access to keys.
Key lifecycle management in Cloud Key Management Service (Cloud KMS) (opens in a new tab) is the end-to-end administration of customer-managed encryption keys (CMEKs) from creation through versioning, rotation, state changes, and eventual destruction. A Cloud KMS key lives inside a key ring and can have unlimited key versions, where each rotation creates a new primary version for future encryption while older versions remain available to decrypt existing data. This design keeps data accessible during normal operations while limiting how much data is exposed if one version is compromised.
Key Creation and Versioning
Key creation and versioning in Cloud KMS separates the named CMEK object from the cryptographic material that protects data. A Cloud KMS key is the named object that holds the rotation schedule and access policy, while key versions hold the actual cryptographic material used for encryption and decryption. All CMEK keys must use the symmetric ENCRYPT_DECRYPT purpose with the GOOGLE_SYMMETRIC_ENCRYPTION algorithm, and Cloud KMS uses envelope encryption where the CMEK acts as a key encryption key (KEK) that encrypts data encryption keys (DEKs).
Key material can be generated by Cloud KMS or imported from outside Google Cloud, and Google-generated material is preferred because it never exposes raw key material and automatically creates new versions on the rotation schedule. Manually creating a CMEK follows an ordered setup before protected resources can use it:
- Create or choose a key ring: Create the key ring in a location near the resources it will protect, in the same project as the data or in a separate key project for stronger Identity and Access Management (IAM) control and separation of duties.
- Create or import the key: Create a Cloud KMS key in that key ring, either with Google-generated material or with imported material for bring-your-own-key (BYOK) needs.
- Grant service access: Grant the CryptoKey Encrypter/Decrypter role (
roles/cloudkms.cryptoKeyEncrypterDecrypter) on the key to the service agent of the CMEK-integrated service. - Attach the key to resources: Configure each new resource, such as a BigQuery table or Cloud Storage bucket, to use the CMEK at creation time.
After setup, end users do not need direct access to the key because the service agent performs encrypt and decrypt operations on their behalf. Using Cloud KMS incurs costs based on the number of active key versions and cryptographic operations, with no minimum purchase.
Automatic Rotation Schedules
Automatic rotation schedules in Cloud KMS create a new primary key version on schedule or when an administrator triggers rotation manually. Administrators can set and modify the rotation period, trigger rotation on demand, and control access and use of each version through IAM. The recommended practice is to enable automatic rotation with a period that meets business needs, ideally at least once per year, and to rotate more frequently for sensitive workloads.
The source of key material changes how rotation works. Keys with Google-generated material rotate automatically according to the schedule, while keys that use imported material require outside automation to generate and import each new version consistently. Keys created by Cloud KMS Autokey follow the same pattern automatically: they are multi-tenant hardware (HSM) AES-256 GCM keys that reside in the same location as the resource, use per-resource-type specificity, maintain separation between key users and key managers, and rotate yearly. If import automation fails or is missing, rotation does not happen on time and older key material protects data longer than intended.
Exam tip: Rotating a Cloud KMS key creates a new version for new encryption; it does not automatically re-encrypt data already written with older versions.
Managing Key States to Keep Data Accessible
Managing key states to keep data accessible means controlling whether each key version can perform cryptographic operations. A key version moves through administrative states that directly control whether protected data can be read. The lifecycle moves in order from active use toward irreversible loss, with recovery possible only before destruction completes:
- Enabled: The version can encrypt and decrypt, and the service can access data while it holds the Encrypter/Decrypter role.
- Disabled: The version cannot be used until it is re-enabled, so protected data becomes inaccessible during the disabled period.
- Scheduled for destruction: The version cannot perform cryptographic operations and every request to use it fails, but the version can still be restored.
- Destroyed: The key material is irrecoverably lost and any data that still depends on that version cannot be decrypted.
Destruction uses a soft-delete safety window before key material is irrecoverably lost. While a version is scheduled for destruction, administrators should check audit logs and key usage tracking to confirm the version is not still protecting live resources. The scheduled for destruction duration can only be set at key creation, defaults to practices around 30 days, and can be as low as 24 hours if set by a Cloud KMS Admin. A version can be restored at any time before the window ends, but only before destruction completes.
To reduce accidental loss, administrators use guardrails and monitoring around state changes. The organization policy constraints/cloudkms.minimumDestroyScheduledDuration can require a minimum destruction window, such as 30 days, across newly created keys. The key usage dashboard and Cloud KMS Inventory API show which resources, projects, and products depend on each key and flag data that is inaccessible because of a disabled or destroyed version, while Cloud Monitoring can alert on sensitive actions such as scheduling destruction.
How Rotation Affects Different Services
How rotation affects different services depends on how each CMEK-integrated service uses key versions to protect DEKs and stored objects. The key version that encrypted the data must remain available to decrypt it, so older versions cannot be disabled or destroyed until the data they protect is re-encrypted, recreated, or deleted. Spanner moves protection forward when rotation occurs because the new key version re-encrypts the DEK. Cloud Storage applies the new version only to newly written objects, so different versions of the same key protect different subsets of data. BigQuery by default keeps existing tables on the version they were created with and does not automatically switch them to the new version.
This difference shapes the rotation strategy for each workload. For services where old objects keep their original version, the lifecycle plan must retain older enabled versions, track which resources depend on each version, and schedule re-encryption or resource recreation when the goal is to retire a potentially exposed version.
Key Facts
- Cloud Key Management Service (Cloud KMS) uses envelope encryption where a customer-managed key encryption key (KEK) wraps service data encryption keys (DEKs), and the service calls Cloud KMS to wrap and unwrap DEKs.
- The CryptoKey Encrypter/Decrypter role (
roles/cloudkms.cryptoKeyEncrypterDecrypter) granted to a service account allows encryption and decryption without allowing key rotation, destruction, or IAM policy changes. - Placing Cloud KMS keys in a separate key-management project from data projects enforces separation of duties between key administrators and service teams.
- Cloud Storage, BigQuery, and Compute Engine support customer-managed encryption keys (CMEKs) for buckets, tables and datasets, and persistent disks, snapshots, custom images, and machine images.
- Rotating a Cloud KMS key creates a new primary version for future encryption and does not automatically re-encrypt existing data, so older enabled versions must remain available until their data is re-encrypted, recreated, or deleted.
Frequently Asked Questions
How does Cloud Key Management Service (Cloud KMS) use envelope encryption with Identity and Access Management (IAM) to protect service data?
Cloud Key Management Service uses envelope encryption where the service creates a data encryption key for the data and Cloud Key Management Service wraps that key with a customer-managed key encryption key. The service accesses the key through its service account holding the CryptoKey Encrypter/Decrypter role, so the service can encrypt and decrypt without managing keys and data requesters do not need direct access to the key.
Why should Cloud Key Management Service (Cloud KMS) keys be stored in a separate Google Cloud project from the data they protect?
Placing Cloud Key Management Service keys in a separate key-management project with no other resources enforces separation of duties between key administrators and service teams. Key administrators retain exclusive control over rotation, disabling, destruction, and access policy while granting only narrow encrypt and decrypt permission outward to service accounts in data projects.
What happens to Cloud Storage, BigQuery, and Compute Engine data when a Cloud Key Management Service (Cloud KMS) key is rotated, disabled, or destroyed?
Rotating a Cloud Key Management Service key creates a new primary version for future encryption and does not automatically re-encrypt existing data, so older enabled versions must remain available until their data is re-encrypted, recreated, or deleted. If the CryptoKey Encrypter/Decrypter grant is revoked or the key version is disabled or destroyed, the service can no longer unwrap data encryption keys and the protected buckets, tables, datasets, disks, snapshots, and images become inaccessible.
Sample Question
A financial services organization is implementing customer-managed encryption keys (CMEK) using Cloud Key Management Service (Cloud KMS) to protect data across several Cloud Storage buckets. The compliance team requires a strict separation of duties and the enforcement of least privilege across cryptographic assets:
- Key administrators must create, rotate, and manage keys and permissions, but must be prevented from encrypting or decrypting data payloads.
- The Cloud Storage service agent must be capable of encrypting and decrypting data using the cryptographic keys, but must have no administrative privileges over key configurations.
- Access should be scoped to the minimal necessary resource level.
Which IAM role configuration should you implement to satisfy these requirements?
Assign the Project Owner (
roles/owner) role to the key administrators at the project level, and assign the Cloud KMS Admin (roles/cloudkms.admin) role to the Cloud Storage service agent on the KMS KeyRing.Assign the Cloud KMS Admin (
roles/cloudkms.admin) role to the key administrators, and assign the Storage Admin (roles/storage.admin) role to the Cloud Storage service agent on the target Cloud Storage bucket.Assign the Cloud KMS CryptoKey Encrypter/Decrypter (
roles/cloudkms.cryptoKeyEncrypterDecrypter) role to both the key administrators and the Cloud Storage service agent at the project level.Assign the Cloud KMS Admin (
roles/cloudkms.admin) role to the key administrators on the KeyRing or project, and assign the Cloud KMS CryptoKey Encrypter/Decrypter (roles/cloudkms.cryptoKeyEncrypterDecrypter) role to the Cloud Storage service agent on the specific CryptoKey.
How learners score on this domain
Last updated