Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Keyless CI/CD Access Using Workload Identity Federation
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise runs continuous integration and deployment (CI/CD) pipelines on an external cloud platform. Workloads running in these external pipelines need to deploy container images and update infrastructure in Google Cloud.
Company security policies strictly prohibit creating, downloading, and storing long-lived service account key files due to the risk of credential leakage.
What should you do to configure secure, keyless authentication for these external workloads?
Explanations
Create a Workload Identity Pool and provider, map external token claims to Google Cloud attributes, and grant the Workload Identity User role on a dedicated service account to the federated principal set.
Create a Workload Identity Pool and provider, map external token claims to Google Cloud attributes, and grant the Workload Identity User role on a dedicated service account to the federated principal set.
What Workload Identity Federation Is
Workload Identity Federation is Google Cloud's recommended mechanism for granting on-premises and external multi-cloud workloads access to Google Cloud resources without managing long-lived service account keys. It leverages Security Token Service (STS) and IAM to establish a trust relationship with external identity providers (IdPs) supporting OpenID Connect (OIDC) or SAML 2.0.
How It Meets the Requirements
- Eliminating Static Keys: Instead of storing long-lived JSON private key files in CI/CD platforms, external workloads exchange short-lived external identity tokens for short-lived Google Cloud federated credentials and access tokens.
- Attribute Mapping & Least Privilege: A Workload Identity Pool manages external identities, while the Workload Identity Provider maps incoming token claims (such as repository, branch, or workspace) to standard Google Cloud attributes (
google.subject,attribute.repository). - Service Account Impersonation: Granting the
roles/iam.workloadIdentityUserrole on a target service account specifically to the mapped external principal set (principalSet://iam.googleapis.com/...) ensures only authorized external workloads can impersonate the service account.
Keyless Token Exchange in Order
Sequence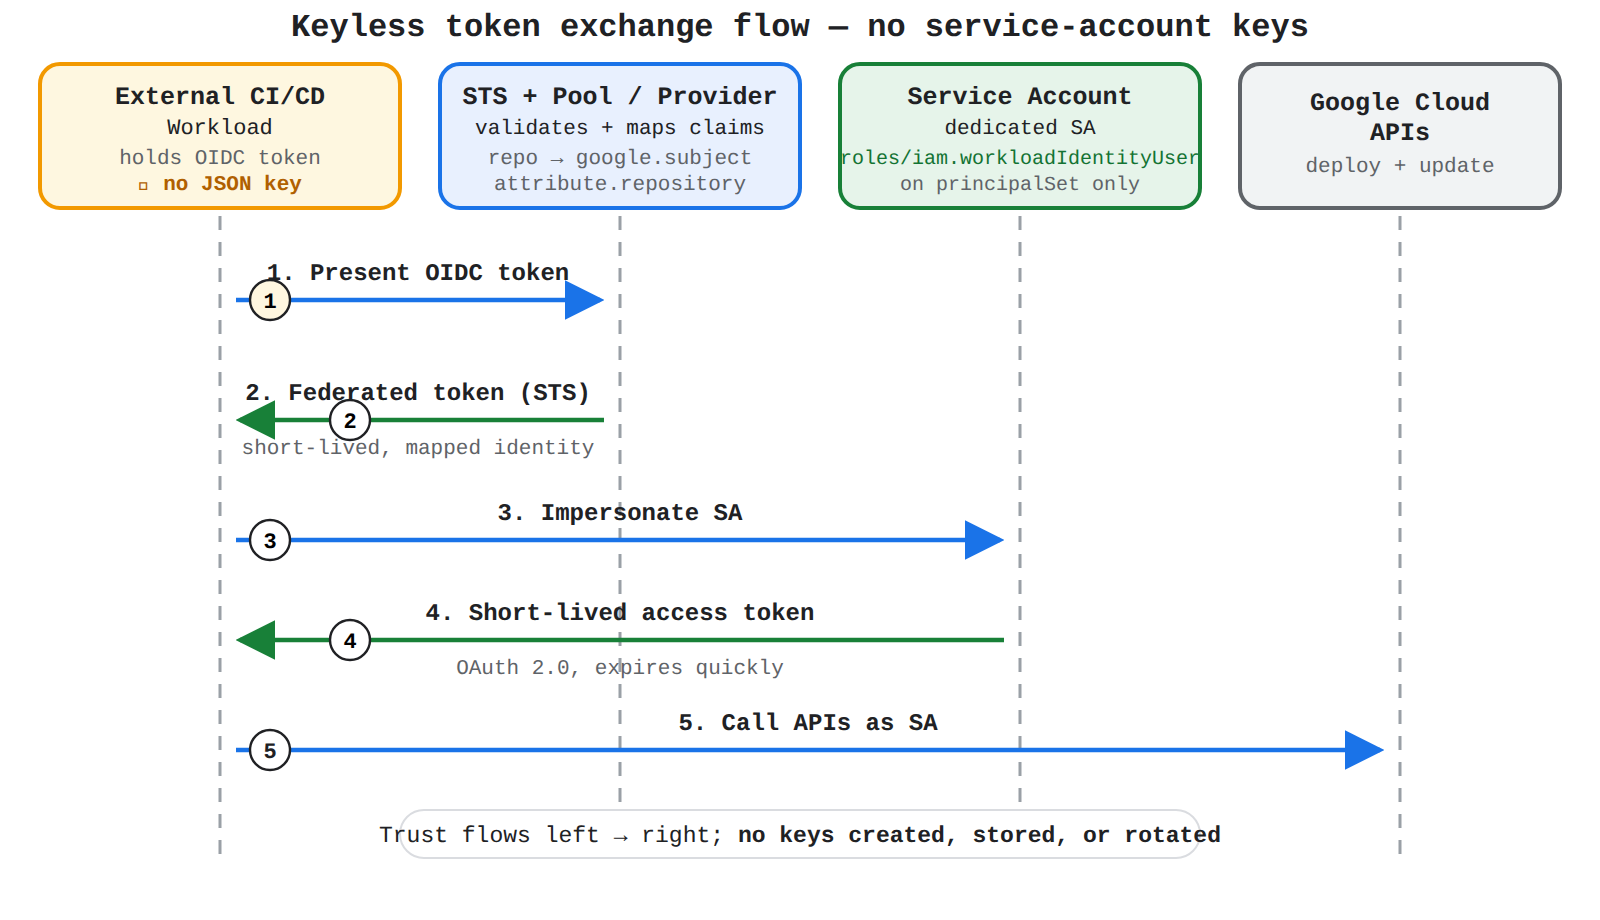
Key Advantages
- Zero Secret Management: Eliminates key creation, manual secret rotation, and leakage risks in third-party environments.
- Fine-Grained Attribute Conditions: Allows access restrictions based on external claims (e.g., restricting deployment access strictly to the production branch).
- Short-Lived Credentials: Downscoped, temporary OAuth 2.0 tokens expire automatically.
- Centralized Auditability: Identity federation events and service account impersonation are logged directly in Cloud Audit Logs.
Why This Is Optimal
Workload Identity Federation provides a direct, cloud-native standard for keyless authentication across heterogeneous environments, aligning perfectly with security best practices and the principle of least privilege.
Create a dedicated service account with the required IAM roles, generate a downloadable JSON service account key, and store it as an encrypted secret in the external CI/CD pipeline.
Create a dedicated service account with the required IAM roles, generate a downloadable JSON service account key, and store it as an encrypted secret in the external CI/CD pipeline.
What Service Account Keys Are
Service account keys are asymmetric, long-lived cryptographic credentials (typically formatted as downloadable JSON files) that allow any entity possessing the private key to authenticate as the associated Google Cloud service account directly.
Why It Doesn't Meet the Requirement
- Violates Keyless Policy: The scenario explicitly prohibits generating, downloading, and storing static service account key files due to the security risks associated with credential leakage.
- Operational Overhead: Managing static keys requires frequent manual or automated key rotation, secure key vault storage, and lifecycle management.
- High Risk Surface: If an external pipeline secret store is compromised, long-lived keys can be used from any network location without immediate revocation.
Key Characteristics and Limitations
- Valid for up to 10 years by default unless revoked or rotated.
- Lacks fine-grained context-based controls tied directly to external workload identity claims.
- Difficult to restrict if leaked outside authorized pipeline executors.
This Answer Would Be Correct If
The external environment lacked an OpenID Connect (OIDC) or SAML identity provider and had no capability to integrate with federated token exchange mechanisms.
Grant the primitive Editor role to the default Compute Engine service account and use Cloud VPN to route external pipeline traffic privately to Google APIs.
Grant the primitive Editor role to the default Compute Engine service account and use Cloud VPN to route external pipeline traffic privately to Google APIs.
What This Approach Does
This approach relies on granting overly broad primitive permissions (roles/editor) to Google Cloud default service accounts and establishing a network-layer tunnel (Cloud VPN) to route external traffic to Google Cloud API endpoints.
Why It Doesn't Meet the Requirement
- Violates Least Privilege: Assigning primitive roles like Editor or Owner grants wide-ranging administrative privileges across the entire project, directly violating security best practices.
- Does Not Solve Authentication: A VPN only establishes network-layer connectivity; it does not provide an identity or authentication token for external workloads calling Google Cloud REST APIs.
- Unsafe Default Account Usage: Default service accounts should not be used for production workload access or granted automatic broad permissions.
Key Characteristics and Limitations
- Default service accounts have generic privileges and lack granularity.
- Cloud VPN does not replace application authentication or token exchange.
- Organization policies often restrict automatic IAM grants to default service accounts to avoid broad exposure.
This Answer Would Be Correct If
The requirement was to provide private RFC 1918 network connectivity to private VM instances inside a VPC without traversing the public internet.
Configure Workforce Identity Federation and have pipeline runners authenticate using OAuth 2.0 authorization code flows with user credentials.
Configure Workforce Identity Federation and have pipeline runners authenticate using OAuth 2.0 authorization code flows with user credentials.
What Workforce Identity Federation Is
Workforce Identity Federation allows human users (such as employees, contractors, and partners) to authenticate to Google Cloud services and the Google Cloud console using an external identity provider (like Microsoft Entra ID or Okta).
Why It Doesn't Meet the Requirement
- Wrong Identity Type: Workforce Identity Federation is designed for human users and interactive browser sessions, not machine-to-machine automated workloads like CI/CD pipelines.
- Requires Interactive Flow: OAuth 2.0 authorization code flows require interactive web redirects and user consent, which automated, headless deployment pipelines cannot execute.
- Misaligned Architecture: Automated compute workloads running outside Google Cloud must use Workload Identity Federation, not Workforce Identity Federation.
Key Characteristics and Limitations
- Governs workforce user access to the Google Cloud console, gcloud CLI, and Cloud APIs.
- Manages human lifecycle events and Single Sign-On (SSO) integration.
- Not designed for non-human workload automation or keyless pipeline execution.
This Answer Would Be Correct If
Human developers and operations engineers needed single sign-on access to the Google Cloud console using their corporate identity provider credentials.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Service Account Token Creator Role
Secure remote access (e.g., Identity-Aware Proxy, service account impersonation, Chrome Enterprise Premium, and Workload Identity Federation)
IntermediateProfessional Cloud Architect
IAP Context-Aware Access
Secure remote access (e.g., Identity-Aware Proxy, service account impersonation, Chrome Enterprise Premium, and Workload Identity Federation)
IntermediateProfessional Cloud Architect
Cloud Trace and Cloud Profiler Correlation
Profiling and benchmarking
IntermediateProfessional Cloud Architect
Binary Authorization Attestation Enforcement
Securing software supply chain
IntermediateProfessional Cloud Architect
Cloud HA VPN MP-BGP Dual-Stack
Extending to on-premises environments (hybrid networking)
AdvancedProfessional Data Engineer
Data Sovereignty With CMEK And VPC Service Controls
Regional considerations (data sovereignty) for data access and storage
Last updated