Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Secure Remote Access with IAP and Federation
Service account (opens in a new tab) impersonation is a method that lets a user or external workload temporarily act as a service account to get short-lived Google access tokens. The workload authenticates with its own identity, exchanges that identity through federation, and then receives only the permissions granted to the impersonated service account. This design removes static JSON keys from code and pipelines while enforcing temporary, least-privilege access.
Why Short-Lived Tokens Replace Static Keys
Short-lived impersonation replaces downloadable service account keys with temporary tokens that expire quickly and are issued on demand. A static key is a long-lived credential that is hard to store safely, rotate, and revoke if it leaks. The organization policy constraint constraints/iam.disableServiceAccountKeyCreation blocks creation of user-managed keys in affected projects, so users and automation must use federation instead. When keys are blocked, Workload Identity Federation (opens in a new tab) and the Security Token Service (STS) (opens in a new tab) exchange ambient credentials for temporary access.
How the Token Exchange Flow Works
The token exchange flow is the ordered path an external workload follows to turn its own identity into a Google access token. The workload starts with a trusted external identity provider on one side of the trust boundary, Google Cloud Identity and Access Management (IAM) sits on the other side, and STS bridges the two sides:
Workload Token Exchange Flow
Sequence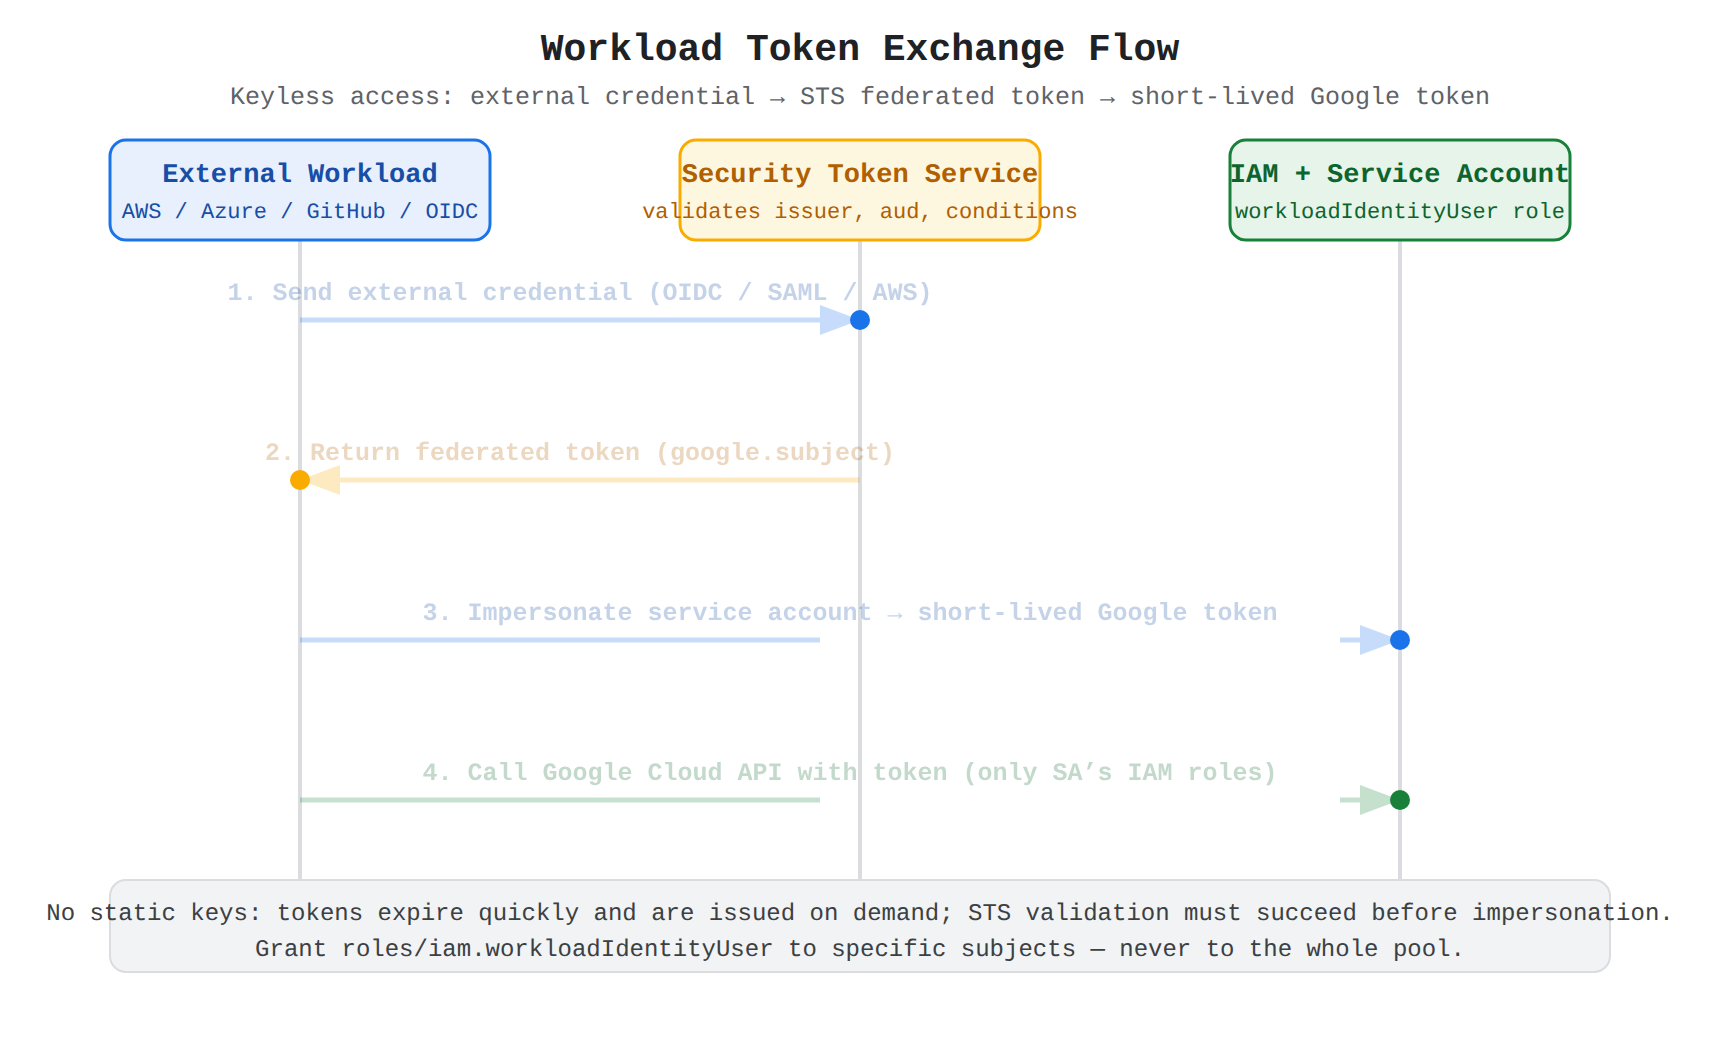
A sequence diagram showing an external workload obtaining an ambient credential from its identity provider, exchanging it with the Security Token Service for a federated token, then impersonating a service account via IAM to get a short-lived Google access token used to call Google Cloud APIs. Arrows light up in order to show the message sequence.
- Obtain an external credential: The application obtains an ambient credential, such as an OpenID Connect (OIDC) token, SAML assertion, or AWS credential, from its local environment.
- Exchange for an STS token: The application sends the external credential to STS, which validates the issuer, audience, and attribute conditions and returns a federated token.
- Impersonate the service account: The application presents the federated token to IAM to impersonate a specific service account and obtain a short-lived Google access token.
Only after STS validation succeeds can impersonation occur, and the resulting Google token carries only the IAM roles granted to that service account. If the ambient credential uses an unsupported format such as Kerberos, an extra first exchange can convert it to OIDC or SAML before the STS exchange.
Applying Least Privilege to Impersonation
Least-privilege impersonation limits both who can impersonate a service account and what that service account can do. Before impersonation is possible, an administrator must grant the roles/iam.workloadIdentityUser role on the service account to the federated identity. An overly broad grant lets a compromised external identity escalate privileges and reach resources it should not access. Least privilege for impersonation follows three practices:
- Use a service account in the same project as the resources: The service account resides in the same project as the target resources so permissions stay narrowly scoped and ownership is clear when the workload is retired.
- Use a dedicated service account for each application: Each application gets its own service account so IAM bindings grant only the resources that one workload requires, avoiding over-permissioning from a shared account.
- Avoid granting access to all members of a pool: Do not bind
roles/iam.workloadIdentityUserto every identity in a workload identity pool; instead bind it to specific subjects or to a filteredprincipalSet://identifier that matches trusted attributes.
Exam tip: Grant roles/iam.workloadIdentityUser to a specific federated principal or filtered principal set, never to all members of a workload identity pool.
Preventing Spoofing in Attribute Mappings
Attribute mappings control how claims from the external provider become the federated subject, groups, and custom attributes used in IAM bindings. Workload Identity Federation derives the external identity's google.subject value from the provider's mapping, and IAM bindings reference that value to authorize impersonation. If mappings use changeable or reusable values such as email addresses, a user can lose access by editing a profile or a new user can inherit an old user's access. To keep trust stable, limit mappings to attributes that are immutable and non-reusable over time, such as a unique user ID. Enforce attribute conditions so multi-tenant platforms like GitHub can authenticate only from authorized organizations, repositories, or accounts. Require tokens to carry the workload identity pool provider URL, https://iam.googleapis.com/projects/PROJECT_NUMBER/locations/global/workloadIdentityPools/POOL_ID/providers/PROVIDER_ID, as the audience so a token issued for another API cannot be replayed as a confused deputy attack.
Auditing Impersonation for Non-Repudiation
Auditing impersonation creates a non-repudiable trail that links Google Cloud actions back to the external identity that requested them. Cloud Audit Logs records the impersonating principal in the serviceAccountDelegationInfo section when a federated token is used to create short-lived service account credentials. Not all services include these details by default, so data access logs must be enabled for the Security Token Service API and the Identity and Access Management API in every project that hosts workload identity pools or impersonated service accounts. With those logs enabled, Cloud Audit Logs adds an entry when an application exchanges an external credential and when it impersonates a service account. A unique mapping for google.subject ensures one external identity maps to exactly one subject value and back, so investigators can identify which external identity acted and whether a compromised identity reached other resources.
Identity-Aware Proxy (IAP) (opens in a new tab) is an identity-aware intermediary that controls access to web applications and administrative interfaces without exposing them directly to the internet. Traffic flows from the user device to IAP, and IAP forwards the traffic to the protected resource only after identity and context checks pass. Chrome Enterprise Premium (opens in a new tab) adds context-aware rules to this flow, so every API request is also evaluated against device health, location, and credential conditions.
How Identity-Aware Proxy Controls Access
Identity-Aware Proxy (IAP) secures an application by acting as a reverse proxy between the client device and the backend VM or web app. The backend needs no external IP address because clients connect to IAP, and IAP connects to the backend on their behalf. Access requires the IAP-Secured Web App User role (roles/iap.httpsResourceAccessor) plus successful authentication. When a user attempts an SSH connection through IAP TCP-forwarding (opens in a new tab), IAP performs four checks in order:
- Authentication: IAP verifies that the user possesses a valid Google credential.
- Authorization: IAP checks Identity and Access Management (IAM) policies to verify permission to connect through IAP.
- Context-aware access: IAP optionally verifies that the user, device, and location satisfy the required access level.
- Auditing: When data access logs are enabled, IAP logs each successful and failed connection attempt.
By performing these functions centrally, IAP removes direct port 22 exposure and replaces network trust with identity and context checks.
Chrome Enterprise Premium Access Levels
Chrome Enterprise Premium access levels are user-centric controls that reject user API traffic that does not meet defined conditions. An access level is a set of attributes defined in Access Context Manager and evaluated on every API request, including IP address, geographic location, and certificate-based access for mutual TLS. Requests that use compromised authorization credentials but fail the access-level conditions are rejected. Basic access levels limit access by network or location. As a Chrome Enterprise Premium subscriber, additional attributes can be required, such as credential strength, browser configuration, and device posture. Context-aware access is most effective when Access Context Manager has rich signals about the user, device, and location.
Applying Access Levels to IAP-Protected Resources
An access level attachment is the IAM configuration that makes a context rule enforceable on an IAP-secured resource. The attachment is made by adding an IAM Condition that references the access level on the IAP role grant, so the role is usable only when the context conditions are met. Once applied, the resource enforces both identity and context on every request. Access levels can be enforced in two ways, depending on whether uniform or per-resource control is needed:
| Option | Scope | Choose when |
|---|---|---|
| Access bindings | Identity-based policy that applies to all resources a user accesses, including IAP, other APIs, and the Google Cloud console | Uniform context-aware access must be enforced across resources |
| IAM conditions | Resource-based policy that attaches an access level to an individual IAM role binding | Different policies must apply to different sets of VMs or apps |
Exam tip: Use access bindings for uniform enforcement across all resources, and use IAM conditions when different VMs need different access levels.
Verifying Device Health with Endpoint Verification
Endpoint Verification provides device-based trust signals for Chrome Enterprise Premium access levels. Endpoint Verification is a Chrome extension for Windows, Mac, and ChromeOS devices that collects device attributes. Access Context Manager references those collected attributes to enforce fine-grained access levels based on device posture. Managed devices can therefore be distinguished from unmanaged devices. If Chrome Enterprise Premium manages the device, access levels can restrict access based on device posture through access bindings or IAM conditions. If the device configuration is not controlled, the device must be treated as unmanaged and untrusted, so access can be managed only by user identity and IP address.
Securing SSH with Context-Aware IAP TCP-Forwarding
Context-aware IAP TCP-forwarding is an SSH access model that allows SSH only through IAP and controls access by identity plus device and location. This approach fits VMs that must be reachable from outside the VPC, are not part of a VPC Service Controls perimeter, and should be reachable only from certain devices, networks, or locations. By default, an SSH grant allows access from any device and network, which increases risk from compromised devices or untrusted networks. Firewall and network design supports this model by removing direct internet SSH. The VM is deployed without an external IP address or with firewall rules that deny public port 22 ingress, so the only permitted SSH path flows from the client device through IAP to the VM. Context-aware IAP then limits that path to the approved networks, locations, and healthy devices.
Working with VPC Service Controls Perimeters
VPC Service Controls is a resource-centric control that defines service perimeters within which resources can communicate. Chrome Enterprise Premium applies only to user identities in the organization, while VPC Service Controls applies to all user and service account identities. When used together, the two controls reduce the impact of compromised credentials used from an attacker-controlled machine outside the environment. For a VM inside a service perimeter, all SSH access should flow through IAP TCP-forwarding so perimeter checks apply. A connection from outside the perimeter must satisfy both IAM permission on the VM and the perimeter ingress rules, which can also enforce context-aware access. A connection from inside the perimeter must satisfy IAM permission but bypasses ingress rules. IAP considers a connection to originate from inside a service perimeter when any of the following applies:
- The source IP is the external IP address of a VM that is part of the service perimeter.
- The connection is made through Private Google Access from a VM that is part of the service perimeter.
- The connection is made through a Private Service Connect access endpoint that is part of the service perimeter.
This distinction prevents an external user with SSH access from copying data into or out of the perimeter except through explicitly allowed ingress rules.
Workload Identity Federation (opens in a new tab) is a keyless authentication method that lets workloads running outside Google Cloud access Google Cloud resources without long-lived service account keys. An external workload first presents its native identity credential to the Google Cloud Security Token Service (STS), and STS exchanges that credential for short-lived Google Cloud credentials. The workload then uses those short-lived credentials to temporarily impersonate a service account and call Google Cloud APIs with the permissions granted to that service account.
How Keyless Federation Replaces Service Account Keys
Keyless federation removes the maintenance and security burden of service account keys by replacing static RSA key pairs with federated trust and short-lived tokens. A service account key is the private portion of a service account public/private key pair, and it remains valid until it is explicitly revoked, which creates risk if it leaks. Federation instead relies on environment-specific credentials that already exist, such as AWS EC2 temporary credentials from an instance profile or Azure access tokens from a managed identity on an Azure VM. The authentication flow moves from the external environment to Google Cloud in order. First, the workload obtains its native credential from its external identity provider (IdP), such as AWS, Azure, GitHub, or an OpenID Connect (OIDC)-compatible or SAML 2.0-compatible provider. Then, the workload exchanges that credential with STS for a short-lived Google Cloud token. Finally, the workload uses that token to impersonate an authorized service account, so data and requests flow from the external workload to the Google Cloud API under the service account identity.
Identity Pools, Providers, and Attribute Mapping
A workload identity pool is the Identity and Access Management (IAM) resource in Google Cloud that represents trust in an external IdP, and a workload identity pool provider defines how a specific external issuer connects to that pool. The pool collects external identities in one trust boundary, while the provider verifies the incoming OIDC or SAML tokens from AWS, Azure, or another platform. You control which external workloads receive access by defining an attribute mapping and condition that translates external claims, such as AWS role or Azure subscription, into federated principal identifiers that IAM roles can be granted to. Configuring federation for AWS or Azure VMs follows an ordered setup:
- Define an attribute mapping and condition: Decide which external attributes identify the workload and which workloads are allowed to federate.
- Create the workload identity pool and provider: Create the pool in IAM and add a provider for the AWS or Azure issuer.
- Allow the external workload to access Google Cloud resources: Grant IAM roles to the federated principal or temporarily permit impersonation of a service account.
- Download or create a credential configuration: Generate the JSON file that tells Google Cloud libraries how to get the external subject token and which pool to use.
- Use the credential configuration to access Google Cloud: Deploy the file with the workload so calls to Google Cloud APIs automatically perform the STS exchange.
Before configuration, enable the iam.googleapis.com, sts.googleapis.com, and iamcredentials.googleapis.com APIs in the Google Cloud project that hosts the pool.
Authenticating Workloads with Auth Libraries
Google Cloud authentication libraries, known as auth libraries, authenticate federated workloads by exchanging external credentials for short-lived Google Cloud access tokens. The workload does not embed a Google key; instead, the library reads a credential configuration file, typically located through the GOOGLE_APPLICATION_CREDENTIALS environment variable. That file tells the library where to find the third-party subject token and which workload identity pool and provider to present it to. The credential configuration file supports three peer methods for obtaining the subject token:
- File-sourced: The library reads the subject token from a local file, while a separate process keeps that file populated with a valid, unexpired token.
- URL-sourced: The library fetches the subject token by making a request to a specified local URL endpoint.
- Executable-sourced: The library runs a configured executable command and reads the subject token from the standard output of that executable.
After GOOGLE_APPLICATION_CREDENTIALS points to the generated JSON file, client libraries handle the token exchange automatically for AWS, Azure, OIDC, and SAML workloads.
Choosing the Correct Identity Option
The correct identity option depends on whether the caller is a machine workload or a human user and where the workload runs. Identity management for Google Cloud (opens in a new tab) distinguishes machine federation, GKE workload identity, and workforce federation:
| Option | What it aggregates | Choose when |
|---|---|---|
| Workload Identity Federation | Machine workloads from AWS, Azure, GitHub, or OIDC/SAML IdPs | The workload runs outside Google Cloud and must access Google Cloud APIs without service account keys |
| Workload Identity Federation for GKE | Kubernetes service accounts in a Google Kubernetes Engine (GKE) cluster | The workload runs on GKE and a Kubernetes service account should act as an IAM service account directly |
| Workforce Identity Federation | Human workforce users from an external IdP | Employees or partners sign in with their external account to use the console, gcloud CLI, or other Google resources |
Workload Identity Federation is not related to Workload Identity Federation for GKE, even though the names are similar. Federation for GKE grants IAM access directly to GKE clusters and Kubernetes service accounts without service account impersonation, while federation for external environments exchanges third-party tokens through STS and then uses impersonation. Managed workload identities are a separate Compute Engine feature for workload-to-workload mutual TLS (mTLS) and cannot be used to authenticate to Google Cloud APIs.
Exam tip: Choose Workload Identity Federation for machine workloads calling Google Cloud APIs, and choose Workforce Identity Federation for human users; use service account keys only when no federated alternative is possible because keys are a security risk if not managed correctly.
Key Facts
- Service account impersonation exchanges an external credential through the Security Token Service for a short-lived Google access token that carries only the IAM roles of the impersonated service account.
- Granting roles/iam.workloadIdentityUser to all members of a workload identity pool allows over-permissioning; grant it to specific subjects or filtered principal sets instead.
- Identity-Aware Proxy forwards traffic to a backend only after authentication, IAM authorization, optional context-aware checks, and auditing, and the backend needs no external IP address.
- Access bindings enforce uniform context-aware access across all resources a user accesses, while IAM conditions attach an access level to an individual role binding for per-resource control.
- Workload Identity Federation serves machine workloads outside Google Cloud, Workload Identity Federation for GKE serves Kubernetes service accounts on GKE, and Workforce Identity Federation serves human users.
Frequently Asked Questions
When should I use Workload Identity Federation instead of Workforce Identity Federation or Workload Identity Federation for GKE?
Use Workload Identity Federation for machine workloads running outside Google Cloud that must access Google Cloud APIs without service account keys. Use Workload Identity Federation for GKE when the workload runs on Google Kubernetes Engine and a Kubernetes service account should act as an Identity and Access Management service account directly, and use Workforce Identity Federation for human employees or partners signing in with an external account to use the console, gcloud CLI, or other Google resources.
What are the steps for an external workload to exchange its own identity for a short-lived Google access token through service account impersonation?
The workload first obtains an ambient credential such as an OpenID Connect token, SAML assertion, or AWS credential from its local environment. It then sends that credential to the Security Token Service which validates the issuer, audience, and attribute conditions and returns a federated token, which the workload presents to Identity and Access Management to impersonate a specific service account and obtain a short-lived Google access token carrying only that service account's roles.
When should I use access bindings instead of Identity and Access Management conditions to enforce Chrome Enterprise Premium access levels on Identity-Aware Proxy-protected resources?
Use access bindings when uniform context-aware access must be enforced across all resources a user accesses, including Identity-Aware Proxy, other APIs, and the Google Cloud console. Use Identity and Access Management conditions when different policies must apply to different sets of virtual machines or apps, because the condition attaches an access level defined in Access Context Manager to an individual role binding so the role is usable only when the context conditions are met.
How does Identity-Aware Proxy (IAP) secure web applications and SSH access without exposing backends to the internet?
Identity-Aware Proxy acts as a reverse proxy between the client device and the backend virtual machine or web app, so the backend needs no external IP address and direct port 22 exposure is removed. When a user attempts a connection through Identity-Aware Proxy TCP-forwarding, Identity-Aware Proxy forwards traffic only after verifying a valid Google credential, checking Identity and Access Management permission to connect, optionally verifying user, device, and location against the required access level, and logging the attempt when data access logs are enabled.
Sample Question
Your organization hosts a sensitive internal administrative web application on Google Kubernetes Engine (GKE) behind an External HTTP(S) Load Balancer, along with private Compute Engine virtual machines (VMs) that administrators manage using SSH.
Your security team mandates the following requirements:
- Administrative web interfaces and VM instances must not be exposed directly to the public internet using public IP addresses.
- Access must be authenticated centrally without requiring an enterprise VPN.
- Only authorized users operating corporate-managed devices that meet specific device posture health criteria and originate from approved geographic locations can connect.
Which architecture should you implement?
How learners score on this domain
Last updated