Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Declarative GKE Deployments with Least Privilege Pipelines
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise is standardizing its deployment process across multiple Google Kubernetes Engine (GKE) environments (development, staging, and production) to align with the Operational Excellence pillar of the Google Cloud Well-Architected Framework.
Currently, developers manually run kubectl commands from their local workstations, leading to configuration drift, deployment inconsistencies, and elevated credential sprawl.
The team wants to implement an automated CI/CD pipeline using Cloud Build that satisfies the following requirements:
- Deployments must be declarative, version-controlled, and repeatable across all environments
- Manual configuration errors must be eliminated
- The pipeline service account must follow the principle of least privilege by having permissions to create, update, and rollback application workloads (such as
container.deployments.createandcontainer.deployments.update) without broad administrative control over the cluster
Which strategy should the cloud architect recommend?
Explanations
Store deployment configurations in Cloud Storage and grant the Cloud Build service account the Kubernetes Engine Admin role (roles/container.admin) at the project level
Store deployment configurations in Cloud Storage and grant the Cloud Build service account the Kubernetes Engine Admin role (roles/container.admin) at the project level
What Project-Level Container Admin Is
The roles/container.admin role provides full administrative access to all Kubernetes Engine resources within a project, including managing clusters, node pools, and security policies.
Why It Doesn't Meet the Requirement
- Violates least privilege: Granting
roles/container.admingives the deployment pipeline permission to delete clusters, modify node pools, and manage cluster certificates, far exceeding the necessary permissions (container.deployments.*andcontainer.ingresses.*). - Lacks version control benefits: Storing manifests in standard Cloud Storage buckets lacks native branch-based review mechanisms, version history, and automated merge gating compared to a dedicated Git repository.
Key Limitations
- Broad blast radius: A compromised pipeline service account could destroy or reconfigure entire GKE clusters.
- Unnecessary control-plane permissions: Workload deployment pipelines do not require permissions to create or scale GKE node pools.
- Audit complexity: Tracking manifest changes in object storage is more difficult than using standard version-control pull request workflows.
This Answer Would Be Correct If
The pipeline was specifically responsible for provisioning, upgrading, and tearing down the underlying GKE cluster infrastructure rather than deploying application workloads.
Additional Context
The Google Cloud Well-Architected Framework emphasizes separation of duties: infrastructure provisioning pipelines should remain separate from application delivery pipelines with strictly bounded IAM roles.
Execute imperative kubectl rollout commands directly from developer machines using shared service account keys that possess roles/container.developer
Execute imperative kubectl rollout commands directly from developer machines using shared service account keys that possess roles/container.developer
What Imperative Local Deployments Are
This approach relies on individual developers executing imperative CLI commands (kubectl run, kubectl set image, kubectl rollout) from their local command lines using downloaded JSON service account keys.
Why It Doesn't Meet the Requirement
- Fails automation goals: Manual command-line execution introduces human error, step omission, and deployment inconsistencies between staging and production.
- Security risk with service account keys: Exporting and distributing long-lived JSON service account keys poses high credential leakage risks.
- No declarative consistency: Imperative commands modify state directly without capturing the desired final state in a version-controlled repository.
Key Limitations
- No automated gating: Changes cannot undergo automated testing, policy checks, or standardized CI validation before reaching production.
- Configuration drift: Environments diverge because manual commands applied to one cluster are easily forgotten on another.
- Lack of central audit trails: Individual developer workstation execution makes central tracking and compliance auditing difficult.
This Answer Would Be Correct If
The organization were troubleshooting an emergency break-glass scenario in an isolated test sandbox where automated CI/CD infrastructure was temporarily offline.
Additional Context
The Operational Excellence pillar strongly discourages manual deployments from local workstations, recommending fully managed CI/CD pipelines (e.g., Cloud Build) running short-lived tokens via IAM Workload Identity.
Store Kubernetes resource manifests in a centralized Git repository, automate deployments via a Cloud Build CI/CD pipeline, and assign the pipeline service account the Kubernetes Engine Developer role (roles/container.developer) scoped to the cluster
Store Kubernetes resource manifests in a centralized Git repository, automate deployments via a Cloud Build CI/CD pipeline, and assign the pipeline service account the Kubernetes Engine Developer role (roles/container.developer) scoped to the cluster
What Declarative CI/CD with Scoped IAM Is
This strategy combines Infrastructure as Code (IaC), GitOps/declarative delivery pipelines, and role-based access management to automate workload lifecycles reliably within Google Kubernetes Engine (GKE).
How It Meets the Requirements
- Repeatable, declarative deployments: Storing manifests in a central Git repository establishes a single source of truth, enabling automated, consistent rollouts across development, staging, and production environments via Cloud Build.
- Minimizing manual errors: Eliminating manual
kubectlexecution removes operator error and prevents environment drift. - Principle of least privilege: The
roles/container.developerrole provides granular permissions to manage workloads—includingcontainer.deployments.create,container.deployments.update,container.deployments.rollback, andcontainer.ingresses.create—without granting cluster administration rights.
Declarative CI/CD Pipeline Flow to GKE
Process Flow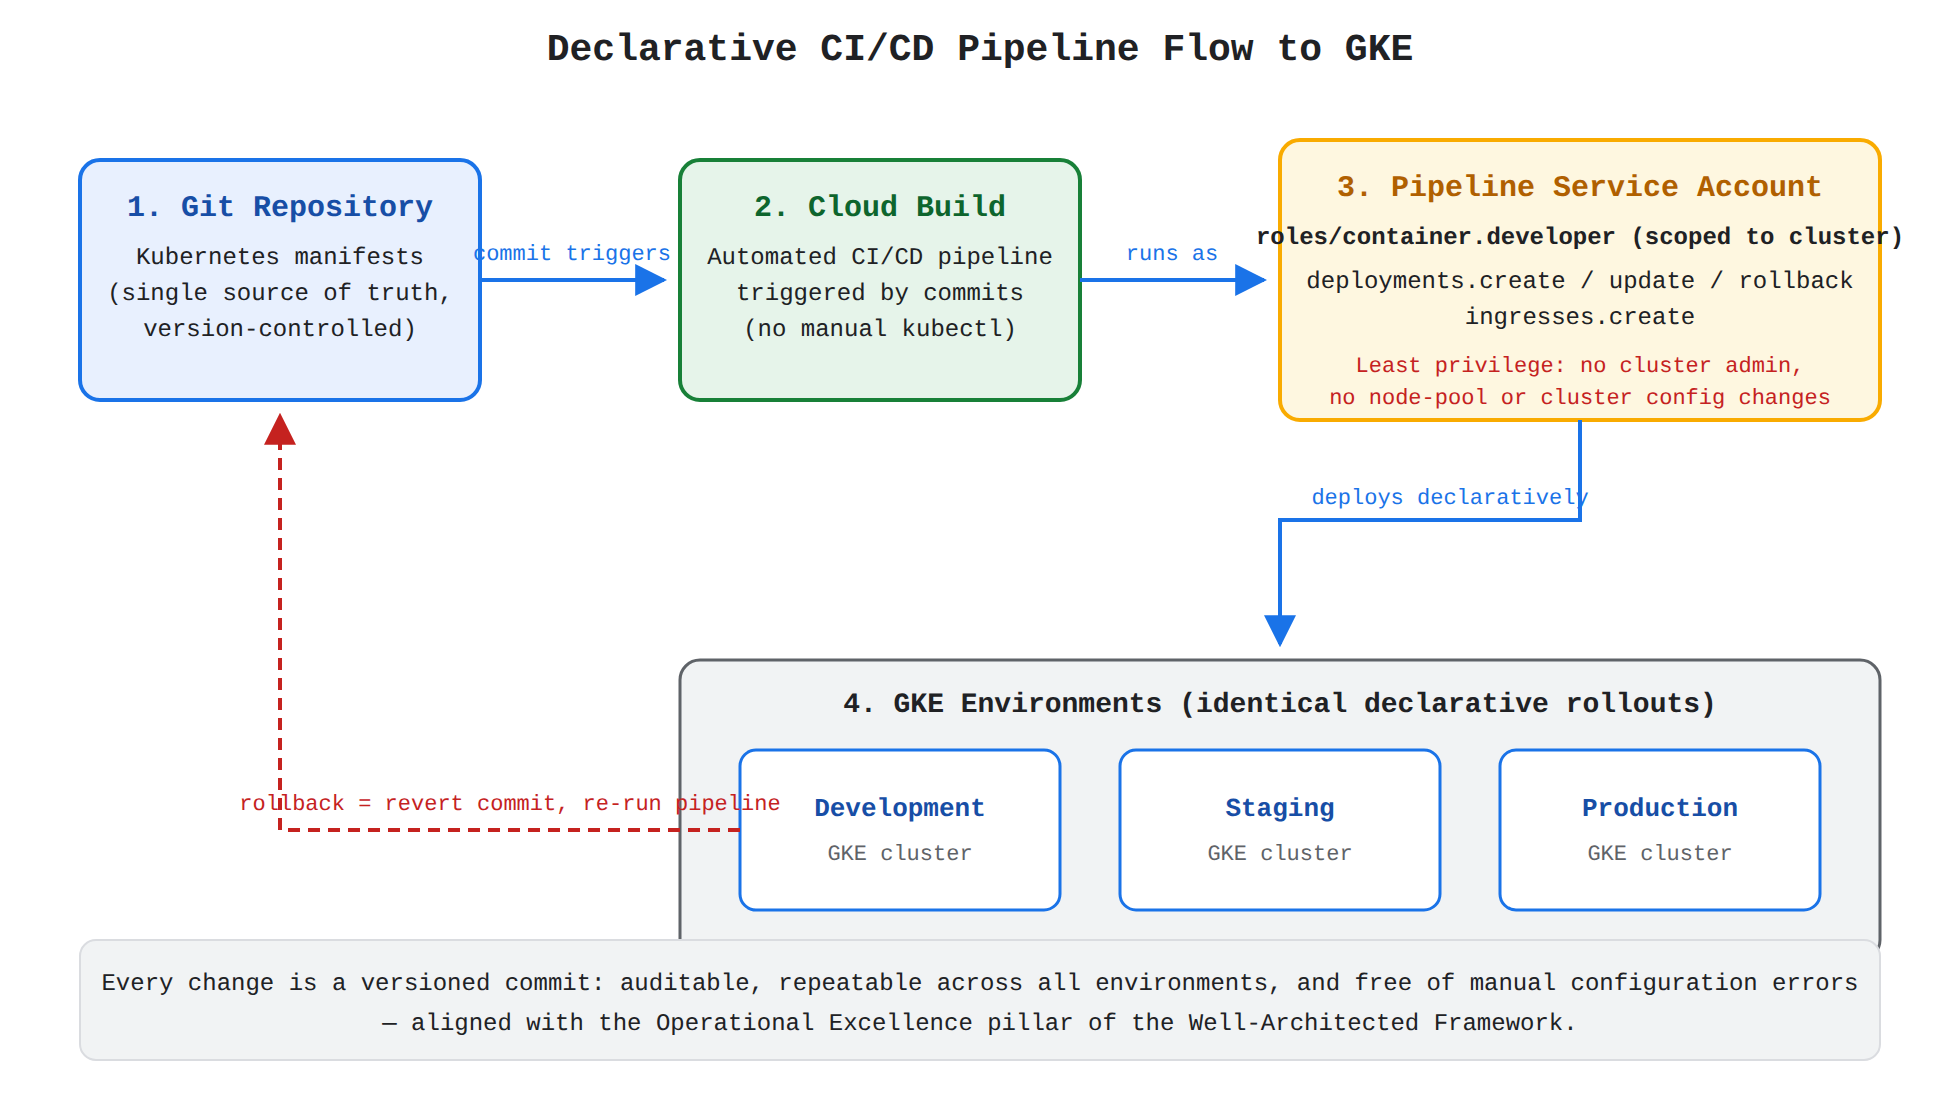
Key Advantages and Capabilities
- Auditability and Traceability: Every deployment change is tracked via commit histories and Cloud Build execution logs.
- Fine-Grained Security: Limits blast radius by restricting the automation service account from modifying underlying cluster configurations or node pools.
- Automated Rollbacks: Simplifies recovery by leveraging automated pipeline triggers and native Kubernetes rollout/rollback mechanisms.
- Consistency: Guarantees identical deployment logic across staging and production clusters.
Why This Is Optimal
Using declarative manifests combined with a least-privilege CI/CD service account aligns directly with the Operational Excellence pillar by replacing error-prone manual interactions with standardized, secure automation.
Configure Cloud Build to deploy workloads using the Project Viewer role (roles/viewer) along with container.ingresses.get permissions
Configure Cloud Build to deploy workloads using the Project Viewer role (roles/viewer) along with container.ingresses.get permissions
What Read-Only Project Access Is
The roles/viewer role grants read-only permissions to inspect Google Cloud resources and cluster assets without permitting any create, update, or delete operations.
Why It Doesn't Meet the Requirement
- Deployment failure: Read-only roles and
container.ingresses.getlack write permissions such ascontainer.deployments.create,container.deployments.update, andcontainer.ingresses.createrequired to apply manifests. - Pipeline execution breakage: Any automated CI/CD pipeline attempting to apply Kubernetes manifests or update replicas will be denied by IAM.
Key Limitations
- Insufficient write privileges: Cannot create pods, deployments, services, horizontal pod autoscalers, or ingress controllers.
- Incomplete workload management: Cannot initiate rollbacks or update workload scales when application traffic surges.
- Non-functional deployment target: Rendered incapable of fulfilling basic continuous delivery functions.
This Answer Would Be Correct If
The goal was to configure a read-only monitoring dashboard or an external compliance auditing tool that only inspects cluster resource state.
Additional Context
While least privilege requires minimizing permissions, it must still provide sufficient privileges for the workload. For deployment pipelines, this requires targeted write permissions on workload-level objects.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Compute Engine Incident Response Procedure
Understanding the principles and recommendations of the operational excellence pillar of the Google Cloud Well-Architected Framework
IntermediateProfessional Cloud Architect
Windows-Based SLI vs Request-Based SLI
Understanding the principles and recommendations of the operational excellence pillar of the Google Cloud Well-Architected Framework
IntermediateProfessional Cloud Architect
GKE Autopilot Regional Cluster
Container orchestration
IntermediateProfessional Cloud Architect
bq load Time Partitioning Field Expiration Filter
Google Cloud SDKs (e.g., gcloud, gsutil, and bq)
IntermediateProfessional Cloud Architect
AlloyDB Continuous Backup and PITR
Data protection (e.g., backup and recovery)
FundamentalAssociate Data Practitioner
Cloud Data Fusion
Choose products required to implement basic transformation pipelines
Last updated