Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Keyless Pod Authentication with GKE Workload Identity
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise is running containerized microservices in a Google Kubernetes Engine (GKE) cluster. Currently, these microservices access Google Cloud APIs by mounting long-lived service account private key JSON files stored as Kubernetes secrets.
The security compliance team has flagged this practice due to the severe risk of credential leakage and unauthorized key export. They require an authentication architecture that eliminates static keys and enforces least privilege access for each individual microservice workload.
Which solution should the cloud architect implement?
Explanations
Grant the necessary IAM roles directly to the default Compute Engine service account attached to the GKE cluster node pool.
Grant the necessary IAM roles directly to the default Compute Engine service account attached to the GKE cluster node pool.
What the node service account does
The node service account is the identity attached to the underlying Compute Engine virtual machines (VMs) that make up the GKE node pool. By default, applications running in pods on a node inherit access to the node's service account credentials via the instance metadata server unless Workload Identity is enabled.
Why it doesn't meet the requirement
- Violates least privilege: Every pod running on the same node pool shares the same node service account, meaning a compromise of a single pod exposes all IAM permissions granted to the node.
- Broad blast radius: The default Compute Engine service account frequently possesses overly broad permissions (such as Editor access in older setups), creating significant security risks.
- No per-workload isolation: Cannot restrict permissions to specific microservices or Kubernetes namespaces.
Key characteristics and limitations
- Node service accounts should only have minimal permissions needed for GKE node operations (such as logging and monitoring).
- Workload pods should never rely directly on the node's underlying infrastructure identity.
This answer would be correct if
You were configuring infrastructure-level logging and monitoring agents that operate strictly at the Kubernetes host node level.
Store the service account private key JSON files in Secret Manager and configure microservices to dynamically fetch the keys using Secret Manager API at startup.
Store the service account private key JSON files in Secret Manager and configure microservices to dynamically fetch the keys using Secret Manager API at startup.
What Secret Manager is
Secret Manager is a secure, centralized storage system for sensitive metadata such as API keys, passwords, certificates, and arbitrary configuration strings. It provides versioning, audit logging, and fine-grained access control via Cloud IAM.
Why it doesn't meet the requirement
- Fails to eliminate long-lived keys: While storing credentials in Secret Manager is more secure than hardcoding them in container images, it still relies on creating and managing static, long-lived service account private keys.
- Bootstrap authentication paradox: The application pod still needs an initial identity to authenticate to Secret Manager itself to retrieve the stored keys.
- Key exfiltration risk remains: The downloaded service account private key still exists in memory or local pod storage and can be abused if compromised.
Key characteristics and limitations
- Centralizes secret storage and rotation policies.
- Requires IAM permissions to access secret payloads.
- Does not replace the need for secure non-human workload authentication mechanisms.
This answer would be correct if
The scenario required storing third-party external API tokens, database connection passwords, or TLS private certificates that cannot use Google Cloud native identity federation.
Implement an automated Cloud Function to regenerate and rotate service account JSON keys every 24 hours, updating the Kubernetes secrets accordingly.
Implement an automated Cloud Function to regenerate and rotate service account JSON keys every 24 hours, updating the Kubernetes secrets accordingly.
What automated key rotation does
Automated key rotation uses serverless functions or scripts to periodically generate new service account keys via the IAM API, deploy them to workloads, and delete expired keys to limit the validity window of compromised credentials.
Why it doesn't meet the requirement
- Does not eliminate static keys: The architecture still generates, transmits, and stores static private key files, maintaining exposure to credential exfiltration and unauthorized use.
- High operational complexity and failure risk: If key propagation to Kubernetes secrets fails or gets out of sync, microservices will experience authentication outages.
- Suboptimal security practice: Key rotation is a remediation technique for legacy systems, whereas modern GKE environments should use keyless authentication through identity federation.
Key characteristics and limitations
- Service accounts have a strict limit of 10 active keys per account.
- Rotating keys introduces eventual consistency delays and application restart overhead.
This answer would be correct if
The workload was hosted in an external, legacy on-premises environment that cannot support Workload Identity Federation or OIDC token exchange.
Enable Workload Identity on the GKE cluster, configure each pod to use a dedicated Kubernetes Service Account (KSA), bind the KSA to a Google Service Account (GSA) using the Workload Identity User role, and annotate the KSA.
Enable Workload Identity on the GKE cluster, configure each pod to use a dedicated Kubernetes Service Account (KSA), bind the KSA to a Google Service Account (GSA) using the Workload Identity User role, and annotate the KSA.
What Workload Identity is
Workload Identity is the recommended best practice for authenticating workloads running on Google Kubernetes Engine (GKE) against Google Cloud APIs. It links a native Kubernetes Service Account (KSA) inside the cluster to a specific Google Service Account (GSA) in IAM, allowing pods to authenticate seamlessly without needing downloadable service account keys.
How it meets the requirements
- Eliminating static keys: Pods automatically obtain short-lived, auto-rotating OAuth 2.0 access tokens through the GKE metadata server, completely eliminating the need to generate, store, or manage long-lived service account private key JSON files.
- Enforcing least privilege: Distinct microservices run under their own specific KSAs, each mapped to a dedicated GSA that possesses only the minimal IAM permissions required for its specific task.
- Preventing credential exfiltration: Workload Identity prevents credentials from being extracted or reused outside the context of the cluster pods.
Keyless Pod Authentication Flow
Sequence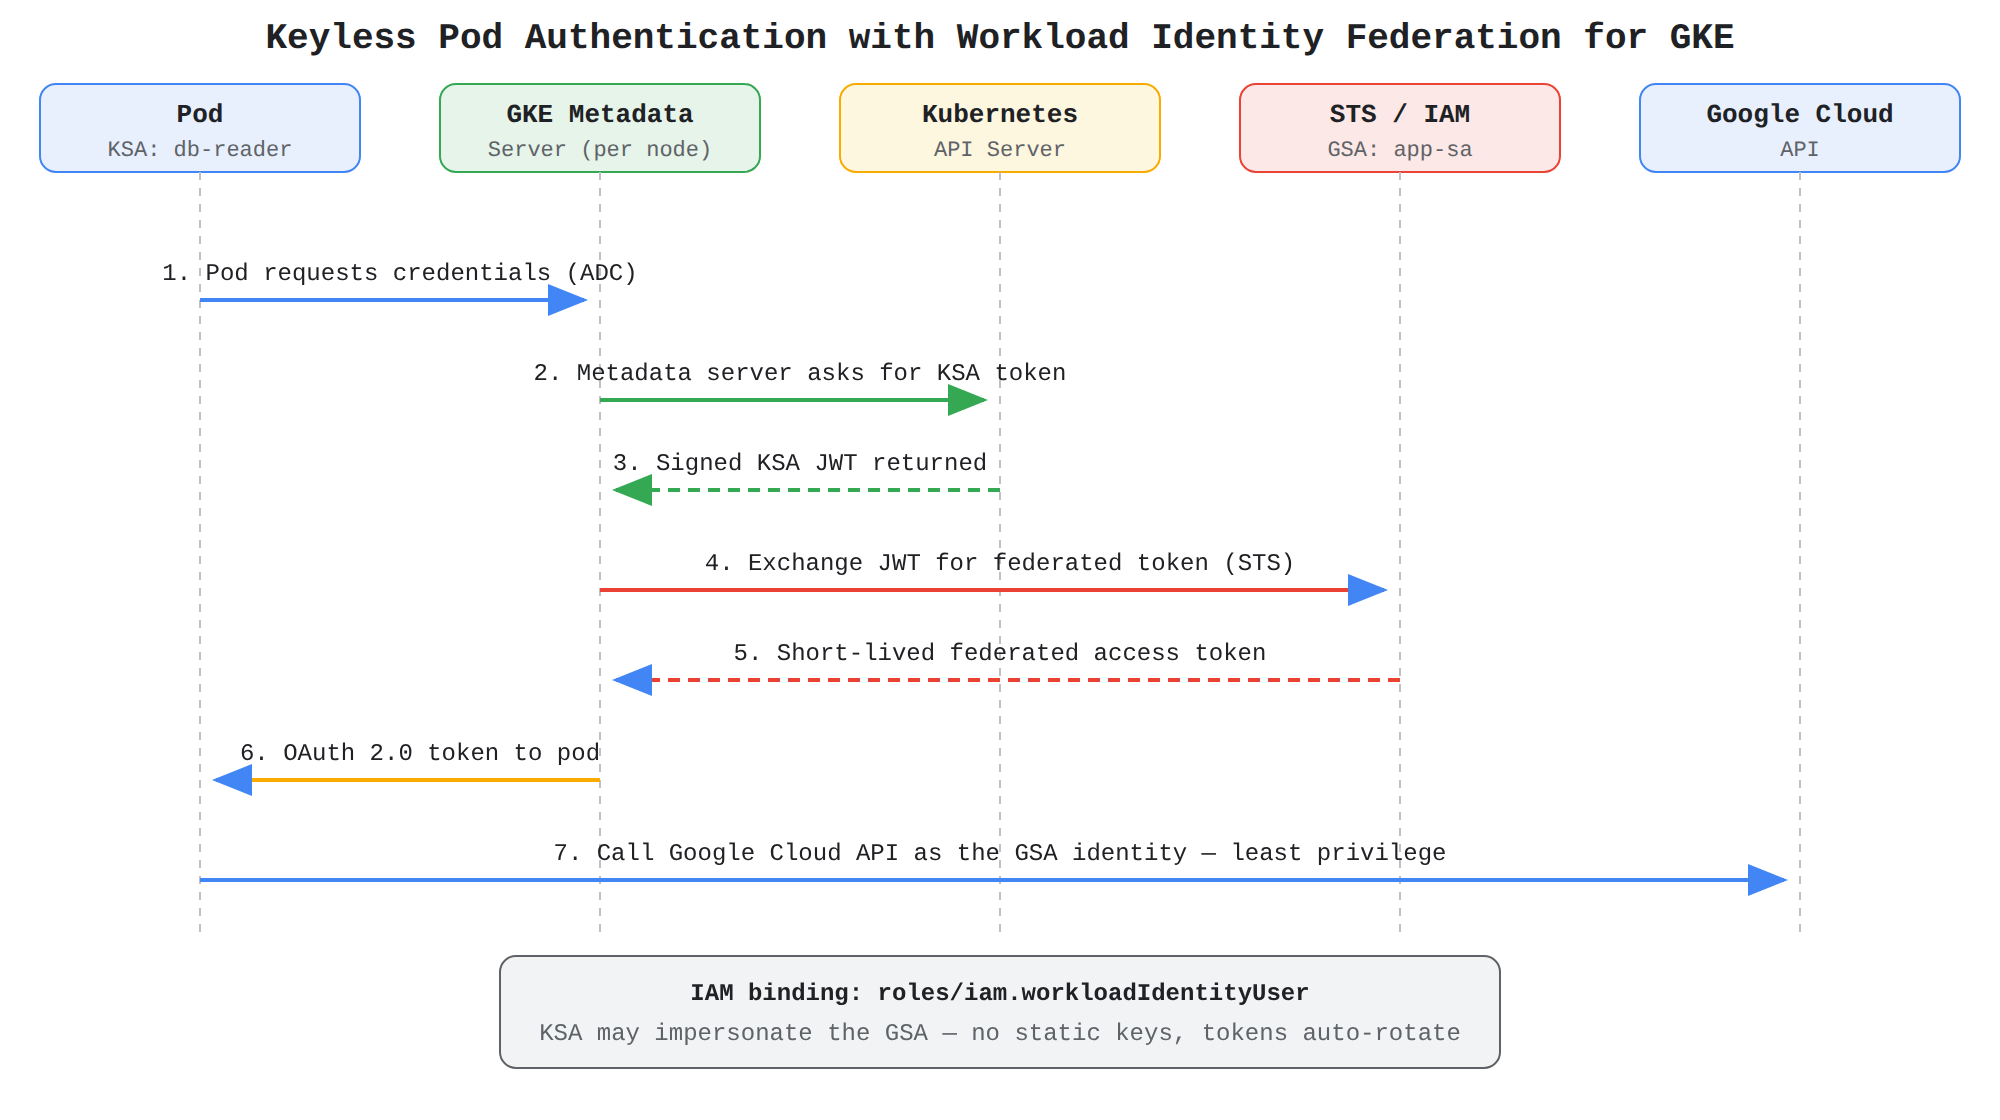
Key advantages and capabilities
- Automated credential lifecycle: Short-lived tokens are refreshed automatically by the client libraries.
- Granular access control: Eliminates shared node-level permissions by isolating access at the individual pod level.
- Auditability and compliance: Actions performed by the workload are logged and traceable in Cloud Audit Logs under the specific GSA identity.
- Secure impersonation: Uses the
roles/iam.workloadIdentityUserIAM role to tightly govern which Kubernetes namespaces and service accounts can act as the GSA.
Why this is optimal
Compared to managing Kubernetes secrets or node pool service accounts, Workload Identity provides strong security isolation, eliminates operational key management overhead, and ensures compliance with enterprise zero-trust security standards.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
IAM Recommender Role Recommendations
Identity and Access Management (IAM)
IntermediateProfessional Cloud Architect
IAM Allow Policy Inheritance
Identity and Access Management (IAM)
IntermediateProfessional Cloud Architect
Network Intelligence Center Connectivity Tests
Troubleshooting/root cause analysis best practices
IntermediateProfessional Cloud Architect
Dynamic Workload Scheduler Flex-start
Choosing compute resources (e.g., spot VMs, custom machine types, and specialized workload)
IntermediateProfessional Cloud Architect
NotebookLM Source Grounding
Integrating Gemini Enterprise features (AI Agents and NotebookLM) to enhance workflows
AdvancedProfessional Cloud DevOps Engineer
Cloud Pub/Sub Queue Metric Autoscaling
Adding capacity
Last updated