Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Correlating Cloud Trace with Cloud Profiler Results
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An e-commerce organization runs a distributed microservices application on Google Kubernetes Engine (GKE) managed with Cloud Service Mesh. Following a recent canary deployment, operations teams notice a distinct performance regression: overall transaction latency has doubled, and node CPU consumption has surged across backend workloads.
To remediate the issue and optimize the resource footprint before completing the rollout, the cloud architect needs to correlate end-to-end telemetry with granular code-level execution details.
Which approach should the architect use to diagnose the regression and identify the specific performance bottleneck?
Explanations
Review proxyless gRPC environment variables in pod specifications, verify the GRPC_XDS_BOOTSTRAP path, and update Prometheus exporters across all client deployments
Review proxyless gRPC environment variables in pod specifications, verify the GRPC_XDS_BOOTSTRAP path, and update Prometheus exporters across all client deployments
What gRPC Observability Configuration Does
Configuring GRPC_XDS_BOOTSTRAP and OpenTelemetry environment variables (OTEL_RESOURCE_ATTRIBUTES) ensures that proxyless gRPC microservices can communicate with the Cloud Service Mesh control plane and export telemetry metrics properly to monitoring backends.
Why It Doesn't Meet the Requirement
- Setup vs. Diagnosis: Checking bootstrap variables verifies whether metrics are being exported; it does not analyze the underlying cause of a runtime performance degradation occurring in an already reporting canary deployment.
- Lacks In-Depth Execution Profiling: Verifying exporter configurations does not explain which internal application functions are consuming excess CPU or creating latency bottlenecks.
Key Characteristics and Limitations
GRPC_XDS_BOOTSTRAPpoints gRPC clients and servers to the Traffic Director/Cloud Service Mesh control plane configuration.- Validates export pipelines for telemetry rather than diagnosing application-level latency spikes.
- Cannot capture runtime stack traces, memory allocations, or thread locks.
This Answer Would Be Correct If
The microservices were completely failing to emit metric data or were reporting unknown topology attributes in the Cloud Monitoring and Cloud Service Mesh dashboards.
Use Cloud Trace and Cloud Service Mesh telemetry to identify the downstream service experiencing elevated round-trip times, then inspect Cloud Profiler flame graphs for that service to isolate CPU-intensive code paths introduced in the new release
Use Cloud Trace and Cloud Service Mesh telemetry to identify the downstream service experiencing elevated round-trip times, then inspect Cloud Profiler flame graphs for that service to isolate CPU-intensive code paths introduced in the new release
What Correlating Trace Telemetry and Profiler Insights Is
This diagnostic strategy combines macro-level distributed tracing and mesh telemetry with micro-level continuous code profiling. Cloud Trace and Cloud Service Mesh provide visibility into distributed inter-service communication, while continuous code profiling measures CPU utilization and memory allocations at the function level inside running application containers.
Trace-to-Profiler Correlation Workflow
Process Flow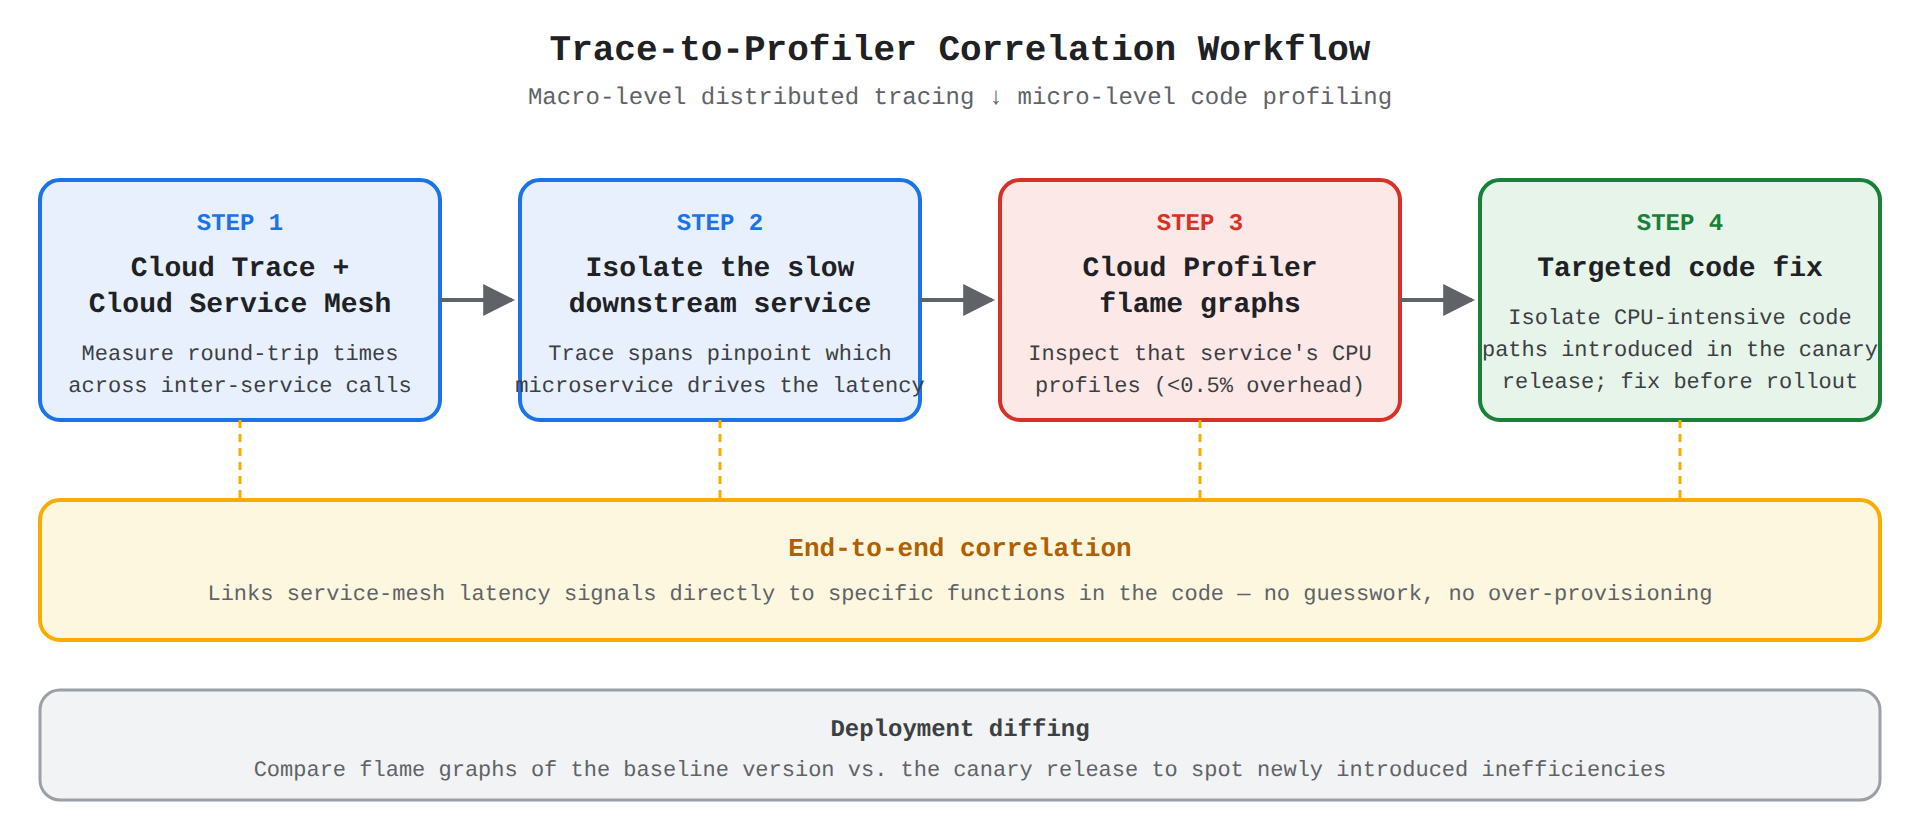
How It Meets the Requirements
- Diagnosing Performance Regressions: Distributed traces and mesh metrics allow teams to measure round-trip times between services, quickly isolating which microservice in the distributed call path is causing the latency regression.
- Optimizing Resource Footprint: Continuous profiling captures real-world CPU and memory execution profiles across deployments, highlighting specific functions or inefficient algorithms introduced in the canary revision that consume excessive resources.
Key Advantages and Capabilities
- End-to-End Correlation: Links high-level transaction delays observed at the service mesh layer directly to specific lines of application code.
- Low Overhead Profiling: Continuous profiling runs in production with negligible CPU overhead, eliminating the need to reproduce complex issues in synthetic test environments.
- Deployment Diffing: Enables direct visual comparison (flame graph diffs) between the baseline version and the canary release to detect newly introduced inefficiencies.
- Targeted Code Remediation: Guides developers directly to algorithmic bottlenecks, unnecessary serialization loops, or redundant memory allocations.
Why This Is Optimal
Correlating service-level distributed telemetry with code profiling provides complete observability from the request lifecycle down to the CPU instruction level. This avoids guesswork and prevents unnecessary infrastructure over-provisioning.
Execute istioctl analyze -A across all cluster namespaces to detect mesh misconfigurations, then apply namespace label updates to adjust sidecar proxy CPU limits
Execute istioctl analyze -A across all cluster namespaces to detect mesh misconfigurations, then apply namespace label updates to adjust sidecar proxy CPU limits
What istioctl analyze Is and Does
istioctl analyze is a static configuration analysis tool that inspects live Kubernetes clusters or local configuration files for structural errors, missing resource definitions, and invalid Cloud Service Mesh / Istio custom resource definitions (such as missing namespace injection labels or broken VirtualService routing rules).
Why It Doesn't Meet the Requirement
- No Code-Level Visibility: Configuration analysis evaluates YAML definitions and control plane metadata; it cannot observe runtime application execution, call stacks, or function execution times.
- Misses Performance Regressions: While useful for identifying broken routes or misconfigured sidecars, it cannot correlate distributed latency bottlenecks with application-level CPU spikes caused by software changes.
Key Characteristics and Limitations
- Evaluates static schema validation and configuration rules (e.g., warning
[IST0102]when namespace injection is omitted). - Does not monitor dynamic traffic, request latencies, or container resource utilization.
- Cannot pinpoint algorithmic regressions or inefficient database access patterns within application code.
This Answer Would Be Correct If
The canary deployment completely failed to route traffic due to a misconfigured mesh routing manifest or missing sidecar proxy injection labels.
Inspect the istiod control plane logs using kubectl logs in the istio-system namespace, then double the GKE node pool instance count to absorb the increased CPU load
Inspect the istiod control plane logs using kubectl logs in the istio-system namespace, then double the GKE node pool instance count to absorb the increased CPU load
What Inspecting Control Plane Logs and Scaling Node Pools Does
This approach checks the istiod control plane logs for synchronization failures and attempts to mitigate elevated CPU utilization by horizontally scaling the underlying GKE compute infrastructure.
Why It Doesn't Meet the Requirement
- Wrong Diagnostic Scope: The control plane (
istiod) handles configuration distribution and certificate management; it does not process application data plane traffic or capture code-level regressions. - Fails to Address Root Cause: Doubling the cluster node pool masks the underlying performance defect rather than identifying the regression or optimizing the application's resource footprint, leading to escalated cloud costs.
Key Characteristics and Limitations
istiodlogs reveal control plane sync issues, validation webhook timeouts, and discovery errors, but lack application call-path data.- Horizontal cluster scaling increases infrastructure spend without providing insight into why per-request CPU demand spiked.
- Does not provide application profiling, distributed tracing, or request-level breakdown.
This Answer Would Be Correct If
The service mesh control plane was failing to push dynamic endpoint discovery updates to sidecars due to resource exhaustion on the istiod pods.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Cloud Profiler
Profiling and benchmarking
IntermediateProfessional Cloud Architect
Same-Zone VPC Benchmarking Client
Profiling and benchmarking
IntermediateProfessional Cloud Architect
Workload Identity Federation
Secure remote access (e.g., Identity-Aware Proxy, service account impersonation, Chrome Enterprise Premium, and Workload Identity Federation)
IntermediateProfessional Cloud Architect
IAP Context-Aware Access
Secure remote access (e.g., Identity-Aware Proxy, service account impersonation, Chrome Enterprise Premium, and Workload Identity Federation)
IntermediateProfessional Cloud Architect
Eventarc Private Network Access
Serverless computing
AdvancedProfessional Data Engineer
Cloud Build Binary Authorization VPC Service Controls
Multi-environment use cases (development vs. production)
Last updated