Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Cross-Organization Access with Ingress and Egress Rules
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
Your enterprise has acquired a subsidiary operating under a separate Google Cloud organization. Workloads running in Project A (within Organization A) require private access to Cloud Storage buckets hosted in Project B (within Organization B).
Both organizations enforce strict data exfiltration defenses using VPC Service Controls perimeters around their respective projects. You must establish private, policy-governed communication between these disparate organizations without compromising perimeter boundaries.
What should you do?
Explanations
Configure an egress rule in Organization A's service perimeter and an ingress rule in Organization B's service perimeter to allow specific identities, methods, and resources.
Configure an egress rule in Organization A's service perimeter and an ingress rule in Organization B's service perimeter to allow specific identities, methods, and resources.
What Ingress and Egress Rules for VPC Service Controls Are
VPC Service Controls ingress and egress rules provide secure, bidirectional data exchange pathways across distinct service perimeters and separate Google Cloud organizations without dismantling existing security perimeters.
How It Meets the Requirements
- Cross-Organization Communication: Google Cloud restricts individual service perimeters to a single organization boundary. Ingress and egress rules allow communication between Project A (Organization A) and Project B (Organization B) across organizational boundaries.
- Strict Network Isolation: The egress rule on Organization A specifies which identities (such as a service account) can make outbound calls to external storage resources, while the ingress rule on Organization B permits only explicitly approved callers to access the Cloud Storage bucket.
- Data Exfiltration Defense: Both organizations maintain perimeter integrity while establishing fine-grained rules based on identity attributes, API methods, and target resources.
Cross-Organization VPC-SC Ingress & Egress Rules
System Architecture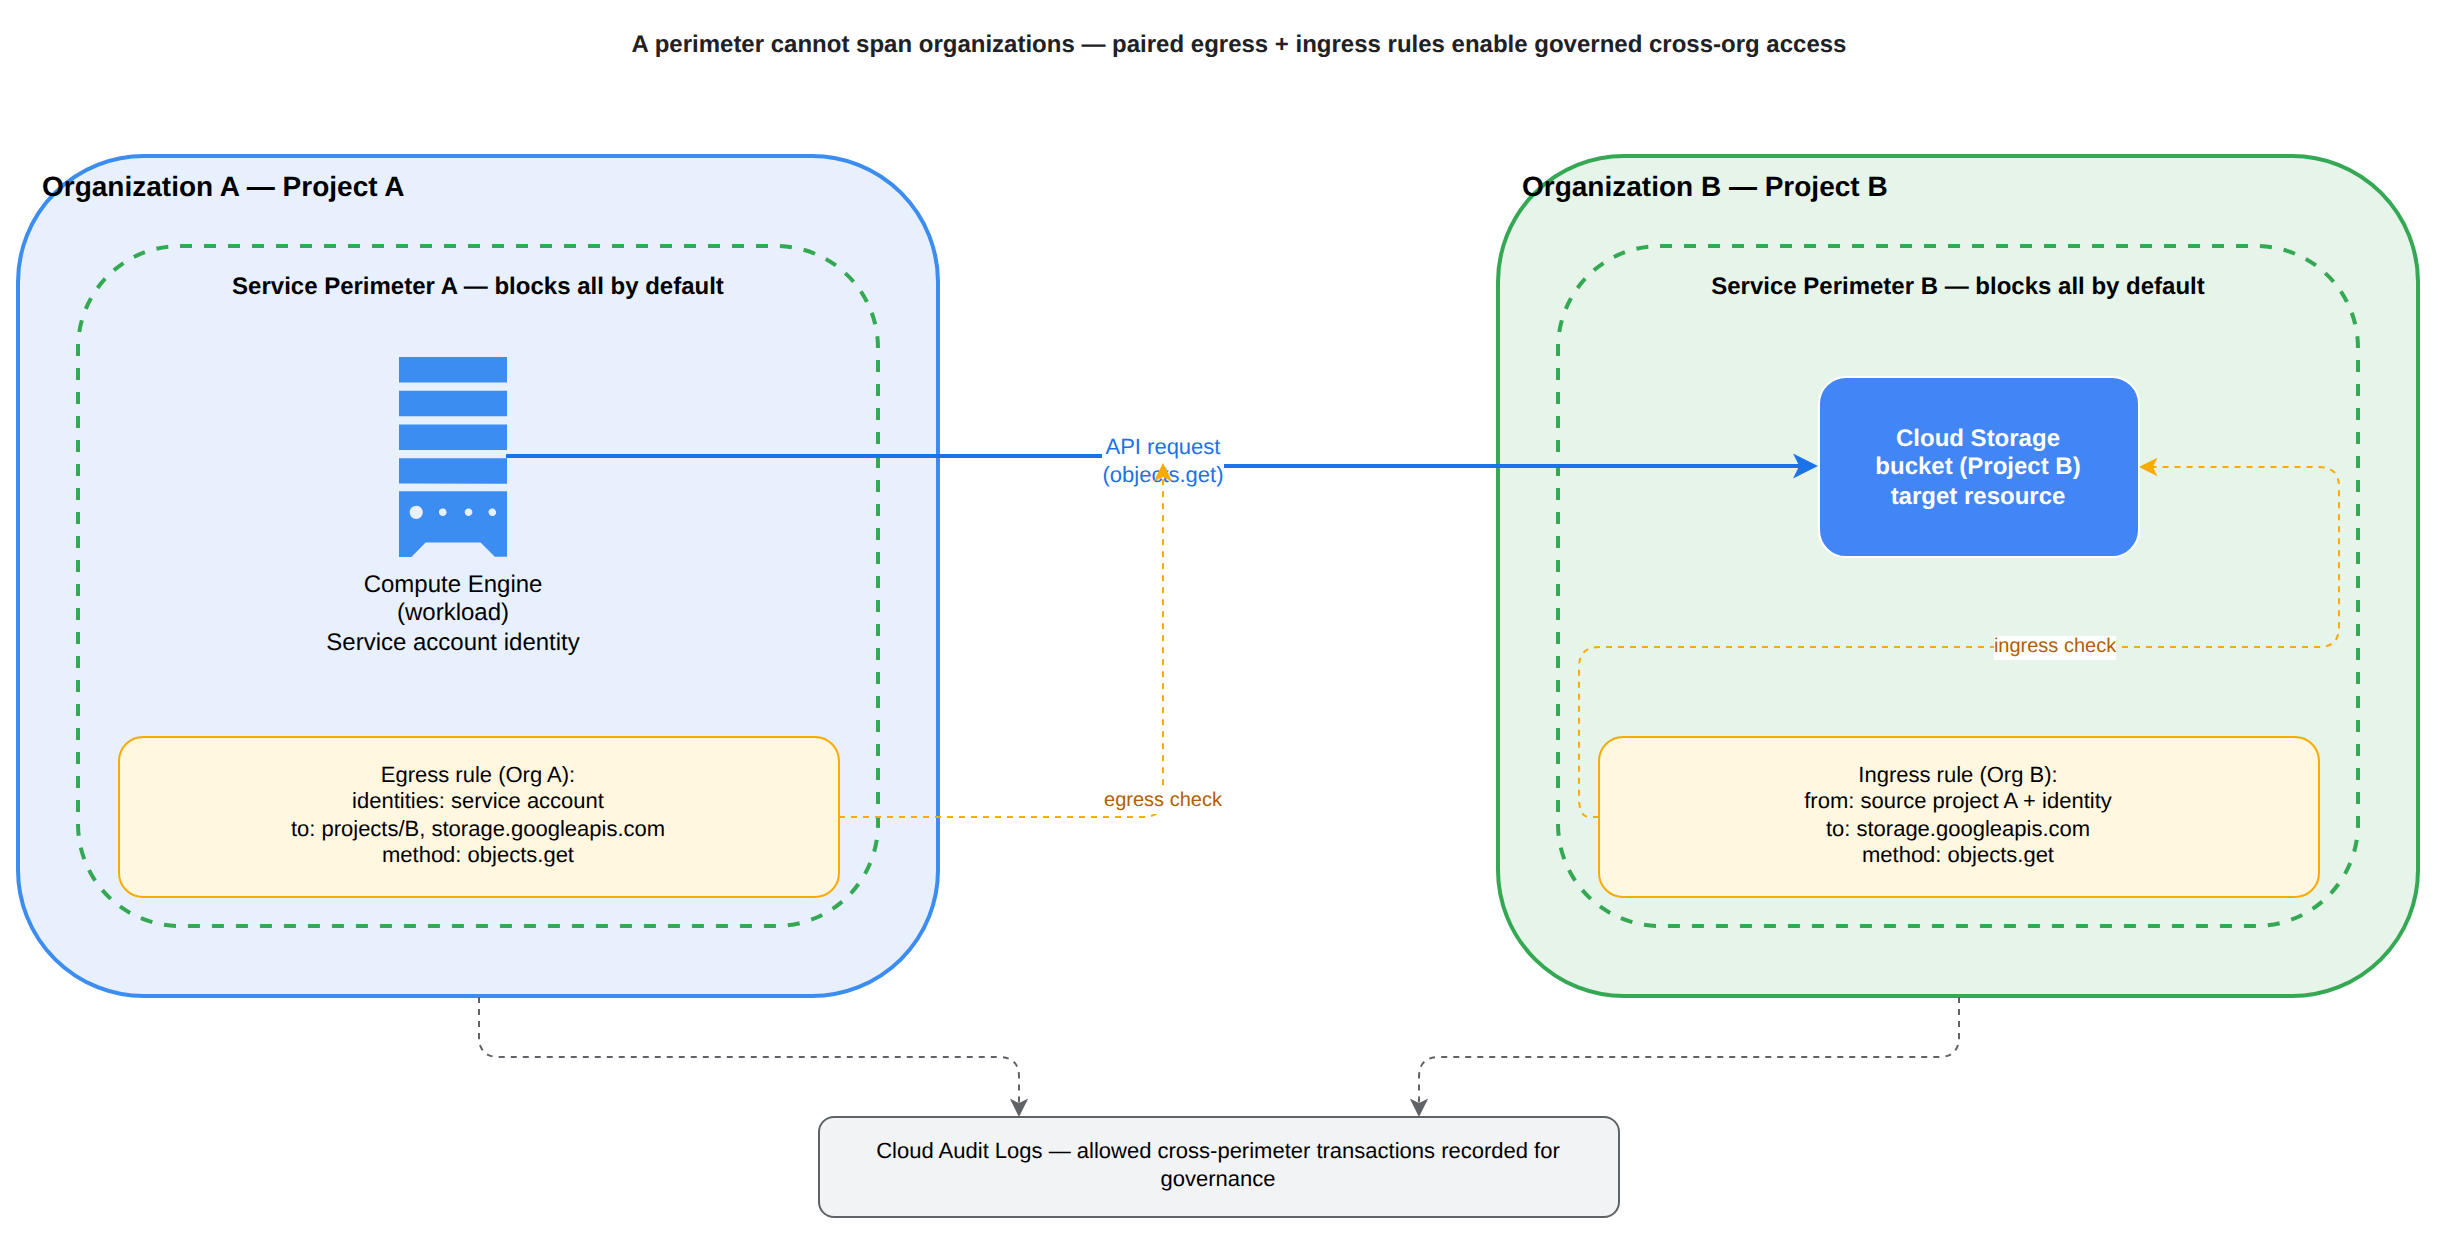
Key Advantages and Capabilities
- Context-Aware Security: Enables administrators to define access criteria based on source project, identity, and target services.
- Preserved Boundary Control: Avoids weakening or disabling perimeter protection for Google-managed APIs.
- Granular API Filtering: Restricts operations to specific methods (e.g., read-only vs. write operations) and specific bucket resources.
- Full Audit Logging: Captures allowed cross-perimeter transactions in Cloud Audit Logs for governance and compliance monitoring.
Why This Is Optimal
Because a service perimeter cannot span across multiple Google Cloud organizations, configuring directional ingress and egress rules is the standard, secure mechanism to enable authorized cross-organization data exchange while preventing unauthorized data exfiltration.
Configure Shared VPC across the organizations by designating Project B as the host project and attaching Project A as a service project.
Configure Shared VPC across the organizations by designating Project B as the host project and attaching Project A as a service project.
What Shared VPC Is and Does
Shared VPC allows an organization to connect resources from multiple projects to a common Virtual Private Cloud (VPC) network, enabling secure and private communication using internal IP addresses.
Why It Doesn't Meet the Requirement
- Organization Constraint: Shared VPC is strictly an intra-organization networking tool. A host project cannot share its subnets with service projects that reside in a different Google Cloud organization.
- Managed API Boundary: Shared VPC manages internal RFC 1918 network connectivity for compute resources (such as Compute Engine VMs or GKE nodes), but does not govern perimeter-protected public Google API endpoints like Cloud Storage.
- VPC-SC Requirements: Even when Shared VPC is used within a single organization, both the host project and service projects must still be placed within the same service perimeter to communicate without violations.
Key Limitations
- No Cross-Org Shared VPC: Shared VPC cannot span across distinct Google Cloud organization resources.
- Compute-Layer Focus: Shared VPC provides network-layer plumbing rather than API-layer perimeter security.
- Configuration Overhead: Fails to provide an access model for managed PaaS storage buckets.
This Answer Would Be Correct If
The workload required private L3/L4 IP connectivity between VMs in multiple projects belonging to the same parent organization.
Additional Context
When using Shared VPC inside a perimeter within one organization, both host and service projects must be explicitly added to the perimeter to avoid communication failures.
Establish VPC Network Peering between the VPC in Project A and the VPC in Project B, and disable VPC Service Controls on Project B.
Establish VPC Network Peering between the VPC in Project A and the VPC in Project B, and disable VPC Service Controls on Project B.
What VPC Network Peering Is and Does
VPC Network Peering enables direct, private connectivity between two VPC networks using RFC 1918 addresses across projects or organizations without using external IP addresses or VPN gateways.
Why It Doesn't Meet the Requirement
- Breaches Security Policy: Disabling VPC Service Controls on Project B directly violates the stated requirement to maintain strict data exfiltration defenses and perimeter isolation.
- Target Mismatch: VPC Network Peering routes traffic between VM instances in private VPC subnets. It does not control access to multi-tenant Google API services such as Cloud Storage.
- Exfiltration Vulnerability: Removing the perimeter exposes the storage bucket to exfiltration risks from compromised credentials or public copying.
Key Characteristics and Limitations
- VPC-to-VPC Routing: Peering operates at Layer 3/4 between VPC internal IP addresses rather than managing Google API calls.
- No Built-in Ingress/Egress Filtering for APIs: Peering does not replace perimeter controls for managed services.
- Quotas and Non-Transitivity: Peering groups have strict limits on subnet ranges per peering group and do not provide transitive routing.
This Answer Would Be Correct If
The requirement was to connect two private VM subnets directly across projects without using API-level perimeter protection.
Additional Context
To route Google API traffic privately within a VPC, organizations use Private Google Access or Private Service Connect, but access to perimeter-secured services is ultimately governed by VPC Service Controls ingress and egress rules.
Add Project A into Organization B's existing service perimeter and grant the Storage Object Viewer role to Project A's service account.
Add Project A into Organization B's existing service perimeter and grant the Storage Object Viewer role to Project A's service account.
What Cross-Project Perimeter Membership Is
Adding projects directly to a single service perimeter allows all resources within those member projects to communicate freely without triggering perimeter-level boundary violations.
Why It Doesn't Meet the Requirement
- Organizational Hierarchy Limits: A VPC Service Controls service perimeter is strictly tied to a single Google Cloud organization's Access Context Manager policy. It cannot include projects belonging to a different parent organization.
- Perimeter Creation Failure: Attempting to add Project A (Organization A) into a perimeter hosted by Organization B produces an administrative error.
- IAM Inadequacy: While granting the Storage Object Viewer role establishes IAM authorization, IAM alone does not bypass perimeter boundaries and will trigger a
RESOURCES_NOT_IN_SAME_SERVICE_PERIMETERerror.
Key Limitations
- Single-Org Scope: Service perimeters cannot contain projects from disparate Google Cloud organizations.
- No Cross-Org Consolidation: Perimeters rely on organizational access policies that do not cross resource management hierarchies.
- Access Denial: Cross-organization API requests without ingress/egress rules are blocked by default.
This Answer Would Be Correct If
Both Project A and Project B resided within the exact same Google Cloud organization and folder hierarchy, allowing a unified perimeter to envelop both projects.
Additional Context
Identity and Access Management (IAM) controls who has permission, but VPC Service Controls provides network and perimeter boundaries. Both layers must permit an operation for cross-project access to succeed.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Cross-Cloud Interconnect
Extending to a multicloud environment that may include Google Cloud-to-Google Cloud communication
IntermediateProfessional Cloud Architect
Cloud Router Bidirectional Forwarding Detection
Extending to a multicloud environment that may include Google Cloud-to-Google Cloud communication
IntermediateProfessional Cloud Architect
SRE Error Budget
Team assessment/skills readiness
IntermediateProfessional Cloud Architect
IAP with Access Context Manager
Security controls (e.g., auditing, VPC Service Controls, context aware access, organization policy, and hierarchical firewall policy)
IntermediateProfessional Cloud Architect
DMS Foreign Key and Trigger Disabling
Assessing and migrating systems and data to support the solution (e.g., Google Cloud Migration Center)
AdvancedProfessional Data Engineer
Security Command Center Event Threat Detection
Monitoring the data lake
Last updated