Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Immutable Archive Storage with Locked Bucket Retention
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
A financial services organization is migrating transaction archive data to Google Cloud Storage to satisfy SEC and FINRA regulatory compliance mandates. The compliance team outlines the following mandatory storage requirements:
- All uploaded archive files must be retained immutably for exactly seven years, with no possibility of modification or premature deletion by any user, including administrators.
- The retention policy duration must not be capable of being shortened, removed, or bypassed under any circumstance.
- Objects should be automatically deleted once their mandatory seven-year retention period has elapsed to minimize ongoing storage costs.
Which Cloud Storage configuration should you implement to satisfy these requirements?
Explanations
Configure Object Retention Lock in Unlocked mode for each object and set a Soft Delete retention duration of seven years on the bucket.
Configure Object Retention Lock in Unlocked mode for each object and set a Soft Delete retention duration of seven years on the bucket.
What Unlocked Object Retention Lock and Soft Delete Do
Object Retention Lock allows per-object retention configurations. When set to Unlocked mode (governance mode), authorized users can remove or reduce the retention period at any time. Soft delete preserves deleted or overwritten objects in a hidden soft-deleted state for a specified safety buffer.
Why It Doesn't Meet the Requirement
- Soft delete maximum limit: Cloud Storage soft delete supports a maximum retention duration between 7 to 90 days, making a 7-year (2,557 days) soft delete duration technically invalid.
- Unlocked mode vulnerability: In
Unlockedmode, the retention configuration is not permanently locked and can be modified or deleted by authorized administrators, failing compliance. - Requires individual object configuration: Object-level retention configurations must be assigned per-object rather than applying uniformly to the bucket unless orchestrated via continuous batch operations.
Key Characteristics and Limitations
- Soft delete retention: Intended exclusively for short-term disaster recovery from accidental deletions (7 to 90 days).
- Unlocked retention mode: Suitable for internal governance where administrators retain permission to override holds, not SEC/FINRA WORM compliance.
This Answer Would Be Correct If
You needed a 30-day safety window to recover accidentally deleted staging objects while allowing project administrators the discretion to alter object holds.
Place an event-based hold on all bucket objects and configure a Cloud Key Management Service (Cloud KMS) customer-managed encryption key with scheduled key destruction after seven years.
Place an event-based hold on all bucket objects and configure a Cloud Key Management Service (Cloud KMS) customer-managed encryption key with scheduled key destruction after seven years.
What Event-Based Holds and KMS Key Destruction Do
An event-based hold blocks object deletion until a specific external business event occurs (such as contract expiration) and an API request explicitly removes the hold. Cloud KMS customer-managed encryption keys (CMEK) allow customers to control the cryptographic keys used to encrypt data at rest.
Why It Doesn't Meet the Requirement
- Requires external event release: Event-based holds do not have a fixed time expiration; when an event-based hold is released, the retention timer only begins counting from zero at that moment.
- KMS destruction restrictions: Cloud Storage explicitly blocks the destruction of Cloud KMS key versions that encrypt locked objects that have not yet met their retention expiration times.
- Destruction vs. Lifecycle Deletion: Destroying encryption keys leaves unreadable ciphertext in storage rather than executing clean object deletions, continuing to incur base storage costs.
Key Characteristics and Limitations
- Event-based holds: Best suited for conditional retention dependent on outside business triggers, not fixed multi-year regulatory durations.
- Key destruction: Intended for cryptographic erasure and key lifecycle management, not automated data lifecycle management.
This Answer Would Be Correct If
You had legal records tied to an open-ended litigation event that required retention until an explicit case closure signal was issued by legal counsel.
Enable Object Versioning on the bucket, configure an Object Lifecycle Management rule to delete noncurrent versions after seven years, and enforce public access prevention.
Enable Object Versioning on the bucket, configure an Object Lifecycle Management rule to delete noncurrent versions after seven years, and enforce public access prevention.
What Object Versioning and Public Access Prevention Do
Object Versioning preserves previous iterations of objects when they are overwritten or deleted by converting live objects into noncurrent versions. Public access prevention is an organization policy constraint or bucket-level security feature that blocks public access over the internet by restricting permissions assigned to allUsers and allAuthenticatedUsers.
Why It Doesn't Meet the Requirement
- Lacks immutable retention: Object Versioning alone does not provide WORM guarantees or prevent authorized users from permanently deleting noncurrent object generations via explicit API calls.
- No deletion protection for live objects: Users with appropriate IAM permissions can still delete live objects, generating noncurrent versions that can also be deleted if not locked.
- Irreversibility requirement unmet: Versioning settings can be disabled or suspended at any time by administrators.
Key Characteristics and Limitations
- Object Versioning: Designed for recovery from accidental overwrites and version tracking, not immutable regulatory compliance.
- Public Access Prevention: Governs network-level identity exposure, having no impact on object retention durations or data immutability.
This Answer Would Be Correct If
The goal was simply to maintain an audit trail of modified files, recover accidentally modified drafts, and secure the bucket from public internet exposure.
Configure a bucket retention policy of seven years, lock the retention policy using Bucket Lock, and configure an Object Lifecycle Management rule to delete objects older than seven years.
Configure a bucket retention policy of seven years, lock the retention policy using Bucket Lock, and configure an Object Lifecycle Management rule to delete objects older than seven years.
What Bucket Lock and Object Lifecycle Management Provide
Bucket Lock is a Cloud Storage compliance feature that allows you to configure a retention policy on a bucket and permanently lock it. When a retention policy is locked, Cloud Storage enforces WORM (Write Once, Read Many) storage behavior across all existing and future objects in the bucket, preventing any object from being modified, overwritten, or deleted until its age exceeds the defined retention period.
Locked 7-Year Retention with Auto-Deletion
Timeline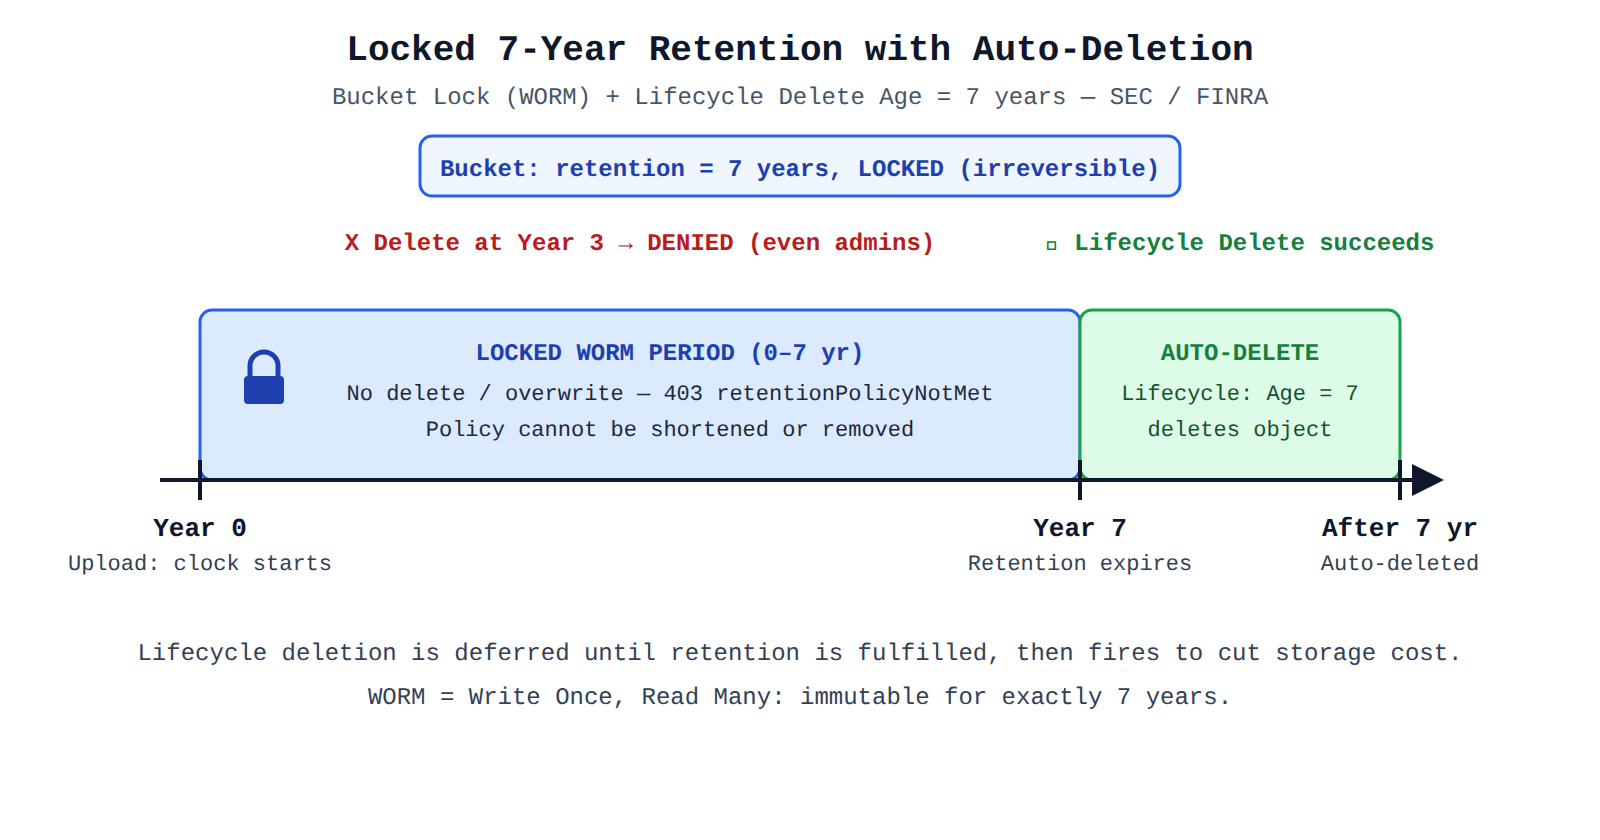
How It Meets the Requirements
- Immutable retention: Setting a 7-year retention policy ensures all objects cannot be deleted or replaced before reaching 7 years of age (
403 - retentionPolicyNotMet). - Irreversible protection: Permanently locking the bucket retention policy prevents anyone—including Project Owners and Storage Admins—from decreasing the retention period or removing the policy.
- Automated deletion after expiration: Object Lifecycle Management integrates directly with Bucket Lock. A lifecycle rule set to delete objects with an
Agecondition of 7 years will automatically purge objects as soon as their retention expiration date is satisfied.
Key Advantages and Capabilities
- Regulatory compliance: Meets stringent requirements for SEC Rule 17a-4(f), FINRA, and CFTC regulations.
- Retroactive enforcement: The locked bucket policy uniformly protects all current objects and incoming data.
- Coordinated lifecycle operations: Lifecycle management deletion actions are automatically deferred until retention conditions are completely fulfilled.
- Admin tamper resistance: The retention duration can only be increased, never reduced or deleted.
Why This Is Optimal
This solution meets every compliance and operational requirement natively within Cloud Storage without custom scripts, external orchestrators, or risk of accidental administrative data deletion.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
AlloyDB Continuous Backup and PITR
Data protection (e.g., backup and recovery)
IntermediateProfessional Cloud Architect
Cloud SQL DR Replica Failover
Data protection (e.g., backup and recovery)
IntermediateProfessional Cloud Architect
Google Cloud Migration Center TCO
Success measurements (e.g., key performance indicators [KPI], return on investment [ROI], and metrics)
IntermediateProfessional Cloud Architect
GKE Workload Identity and Network Policies
Container orchestration
IntermediateProfessional Cloud Architect
Cloud Build Provenance with Artifact Analysis
Deployment and release management
FundamentalAssociate Data Practitioner
BigQuery ML Linear Regression
Execute SQL to create, train, and evaluate models using BigQuery ML
Last updated