Fundamental
Prepare and test your skills
Fundamental
Prepare and test your skills
Automatic PII Redaction Before Model Prompts
Free sample question, answered and explained below. The Generative AI Leader practice bank has 2,191 more like it. Try 10 free: instant score, no account.
A retail company is launching a generative AI assistant that processes customer support inquiries. Customers frequently submit unstructured text messages that inadvertently contain sensitive Personally Identifiable Information (PII), such as phone numbers, home addresses, and credit card numbers. The engineering team needs to automatically discover, inspect, and redact or mask this sensitive data in near real time before passing the prompts to the foundation model.
Which Google Cloud service should the company integrate into their application workflow?
Explanations
Identity and Access Management (IAM)
Identity and Access Management (IAM)
What Identity and Access Management (IAM) Is
Identity and Access Management (IAM) is Google Cloud's authorization service. It defines who (identities such as human users, groups, or service accounts) has what access (roles and permissions) to specific Google Cloud resources.
Why It Doesn't Meet the Requirement
- No Content Inspection: IAM enforces access policies at the administrative control plane and API boundary. It does not read, parse, or evaluate the contents of application data streams or conversational text prompts.
- Cannot Redact or Mask PII: IAM cannot alter the text strings passed inside an API request. It can either allow or deny an identity from calling a model endpoint, but it cannot strip a credit card number or phone number from a user prompt.
- Resource-Level Rather than Data-Level Focus: IAM controls permissions on resources such as projects, buckets, and model endpoints, rather than managing the internal privacy hygiene of conversational text payloads.
Key Characteristics and Limitations
- Identity-Driven Controls: Restricts actions based on authenticated identities and assigned roles.
- Coarse-Grained Operational Boundary: Governs whether a service account can invoke an API, not what words are transmitted inside that API call.
- Static Permissions Model: Does not provide runtime content evaluation, token masking, or de-identification.
This Answer Would Be Correct If
The organization needed to enforce the principle of least privilege by restricting which application developers or backend service accounts have permission to invoke the generative AI foundation model API or access cloud storage buckets.
Additional Context
While IAM can be used in tandem with Sensitive Data Protection—such as restricting access to de-identification templates or raw audit logs—it cannot perform the in-flight content sanitization required in this scenario.
Security Command Center (SCC)
Security Command Center (SCC)
What Security Command Center (SCC) Is
Security Command Center (SCC) is Google Cloud's centralized security posture and risk management platform. It continuously monitors cloud assets for misconfigurations, vulnerabilities, and active threat activities across an organization.
Why It Doesn't Meet the Requirement
- Infrastructure Posture, Not Payload Transformation: SCC identifies misconfigured cloud settings, missing firewalls, and exposed resources. It is not an application-layer proxy designed to process and modify text strings in real time.
- No Redaction Engine: SCC does not offer automated text masking, redaction, or pseudonymization capabilities for incoming application inputs.
- Asynchronous Reporting: SCC generates findings and alerts for security operations teams to investigate, rather than synchronously intercepting and cleansing data during live user transactions.
Key Characteristics and Limitations
- Centralized Security Dashboard: Aggregates vulnerability findings, compliance scores, and threat alerts across projects and folders.
- Asset Inventory and Posture: Tracks cloud infrastructure assets like virtual machines, storage buckets, and IAM bindings.
- Threat Detection: Detects suspicious behaviors such as unauthorized cryptomining or credential leakage in cloud infrastructure.
This Answer Would Be Correct If
The organization needed to establish a unified dashboard to monitor security vulnerabilities, detect infrastructure misconfigurations, and receive alerts about unauthorized access attempts across their Google Cloud deployment.
Additional Context
Sensitive Data Protection can send summary data profiles and sensitive data discovery findings to Security Command Center to enhance overall organizational risk visibility, but SCC itself cannot sanitize or mask conversational prompts in real time.
Sensitive Data Protection (Cloud DLP)
Sensitive Data Protection (Cloud DLP)
What Sensitive Data Protection Is
Sensitive Data Protection (formerly known as Cloud Data Loss Prevention or Cloud DLP) is Google Cloud's fully managed service designed to discover, classify, and de-identify sensitive data across cloud and hybrid environments. It operates on structured datasets, cloud repositories, and real-time streaming text payloads.
How It Meets the Requirements
- Automated PII Discovery and Inspection: Sensitive Data Protection includes over 200 built-in infoType detectors (such as credit card numbers, email addresses, phone numbers, and national identifiers) that automatically identify sensitive tokens inside freeform text.
- In-Flight Masking and Redaction: Through the synchronous
content.deidentifyAPI method, the service accepts conversational text strings in near real time, masks or redacts the identified PII, and returns the sanitized text. - Protection of the Generative AI Lifecycle: Sanitizing prompts before invoking foundation models prevents sensitive customer details from entering model context windows, prompt logging systems, or potential downstream fine-tuning repositories.
In-Flight PII Redaction Before Gen AI
Process Flow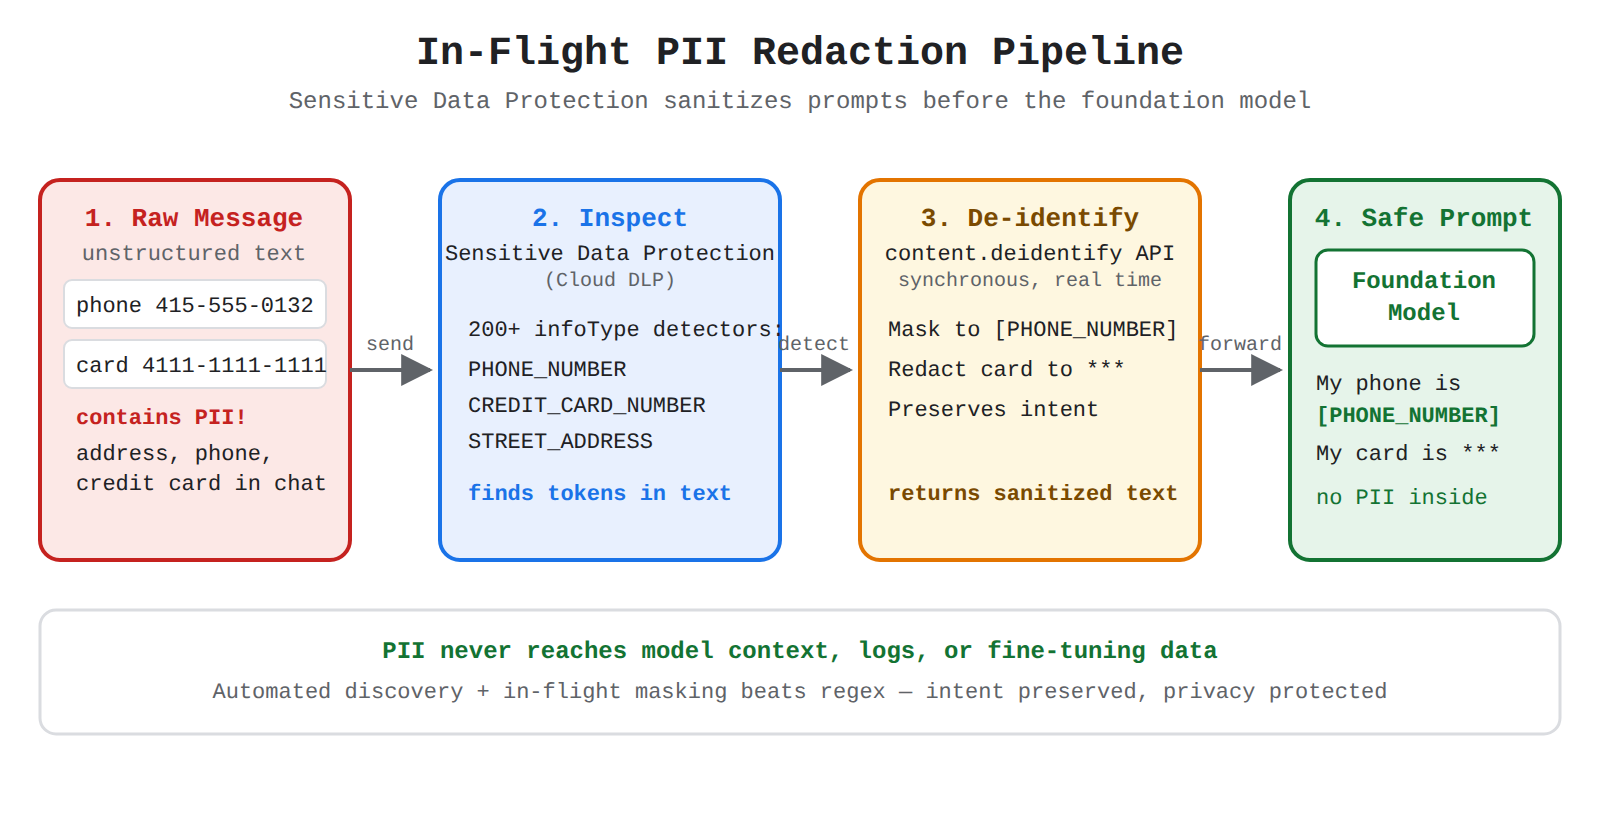
Key Advantages and Capabilities
- Comprehensive infoType Detectors: Accurately recognizes regional and global identifiers out of the box, with support for custom regular expressions and dictionaries.
- Versatile Transformation Techniques: Supports redaction, character masking, date-shifting, bucketing, and cryptographic pseudonymization (tokenization).
- Preserves Text Usability: Masks only the sensitive token (for example, replacing a phone number with
[PHONE_NUMBER]), allowing the generative AI model to comprehend the user's intent without exposing private details. - Low-Latency Synchronous Execution: Seamlessly integrates into application request pipelines prior to foundation model invocation.
Why This Is Optimal
Sensitive Data Protection is specifically purpose-built for discovering and de-identifying sensitive data in motion and at rest. Custom rule engines or basic regular expressions frequently fail to catch diverse variations of unstructured PII, whereas Sensitive Data Protection provides enterprise-grade, managed detection rules designed for privacy compliance and generative AI safety.
BigQuery ML
BigQuery ML
What BigQuery ML Is
BigQuery ML is a capability within Google BigQuery that allows data practitioners to train, evaluate, and operationalize machine learning models directly inside the data warehouse using familiar SQL commands.
Why It Doesn't Meet the Requirement
- Analytical Model Training, Not Privacy Sanitization: BigQuery ML is designed for analytical model creation (such as linear regression, classification, and forecasting) rather than detecting and de-identifying sensitive text tokens.
- Warehouse-Centric Execution: BigQuery ML operates on structured tables stored within the BigQuery data warehouse. It is not architected to serve as an in-line, low-latency microservice for real-time customer chat interactions.
- Lack of Built-In Privacy Detectors: BigQuery ML does not maintain specialized infoType libraries, token masking transformers, or redaction filters for unstructured text.
Key Characteristics and Limitations
- SQL-Based Modeling: Enables analysts to create ML models using standard database queries without moving data out of the warehouse.
- Batch Analytics Focus: Primarily suited for batch processing and tabular analytics rather than streaming real-time prompt preprocessing.
- No Native De-Identification Engine: Does not provide automated discovery, masking, or tokenization of personal identifiers.
This Answer Would Be Correct If
The engineering team needed to build, evaluate, and run predictive machine learning models on historical customer transactional data directly inside their enterprise data warehouse using SQL.
Additional Context
While BigQuery ML can be combined with Sensitive Data Protection in advanced analytical architectures (for example, analyzing sanitized event logs), it plays no role in redacting sensitive PII from incoming generative AI prompts.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,191 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalGenerative AI Leader
LLM Training Data Memorization
Describing privacy considerations (e.g., privacy risks, data anonymization and pseudonymization)
FundamentalGenerative AI Leader
Pseudonymization via Consistent Tokenization
Describing privacy considerations (e.g., privacy risks, data anonymization and pseudonymization)
FundamentalGenerative AI Leader
Data Quality and Tuning Integrity
Describing the implications of data quality, bias, and fairness
FundamentalGenerative AI Leader
VPC Service Controls Service Perimeters
Explaining security throughout the ML lifecycle
FundamentalGenerative AI Leader
Google Cloud Responsible AI Governance
Identifying the key factors that influence gen AI needs (e.g., business requirements, technical constraints)
IntermediateProfessional Cloud Architect
Active Assist and IAM Recommender
Gemini Cloud Assist
Last updated