Diagram
IAM Hierarchy: How Access Inherits Down
Hierarchy / Taxonomy
A tree from Organization to Folders to Projects to service resources showing allow policies inherit downward, with a deny policy callout on a project that overrides allows.
In the Domain
Allow Policies and the Resource Hierarchy
An allow policy, also called an IAM policy, is the object that attaches access rules to a Google Cloud resource. Each allow policy contains role bindings, and each role binding connects one or more principals to one IAM role on that resource. The granted access applies both to the resource with the policy and to resources contained within it, so a policy set on a Cloud Storage bucket can control its managed folders and objects, and a policy set on a project can control buckets and instances inside that project.
Domain 4 of 7
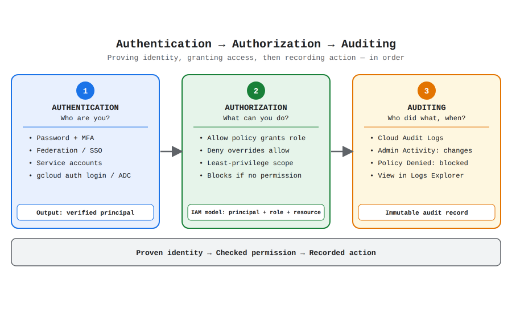
Differentiate between authentication, authorization, and auditing.
Read the Domain summaryPractice this Domain
27 practice questions
Practice this DomainMore from this Domain
Last updated