Diagram
CMEK Envelope Encryption, Step by Step
Sequence
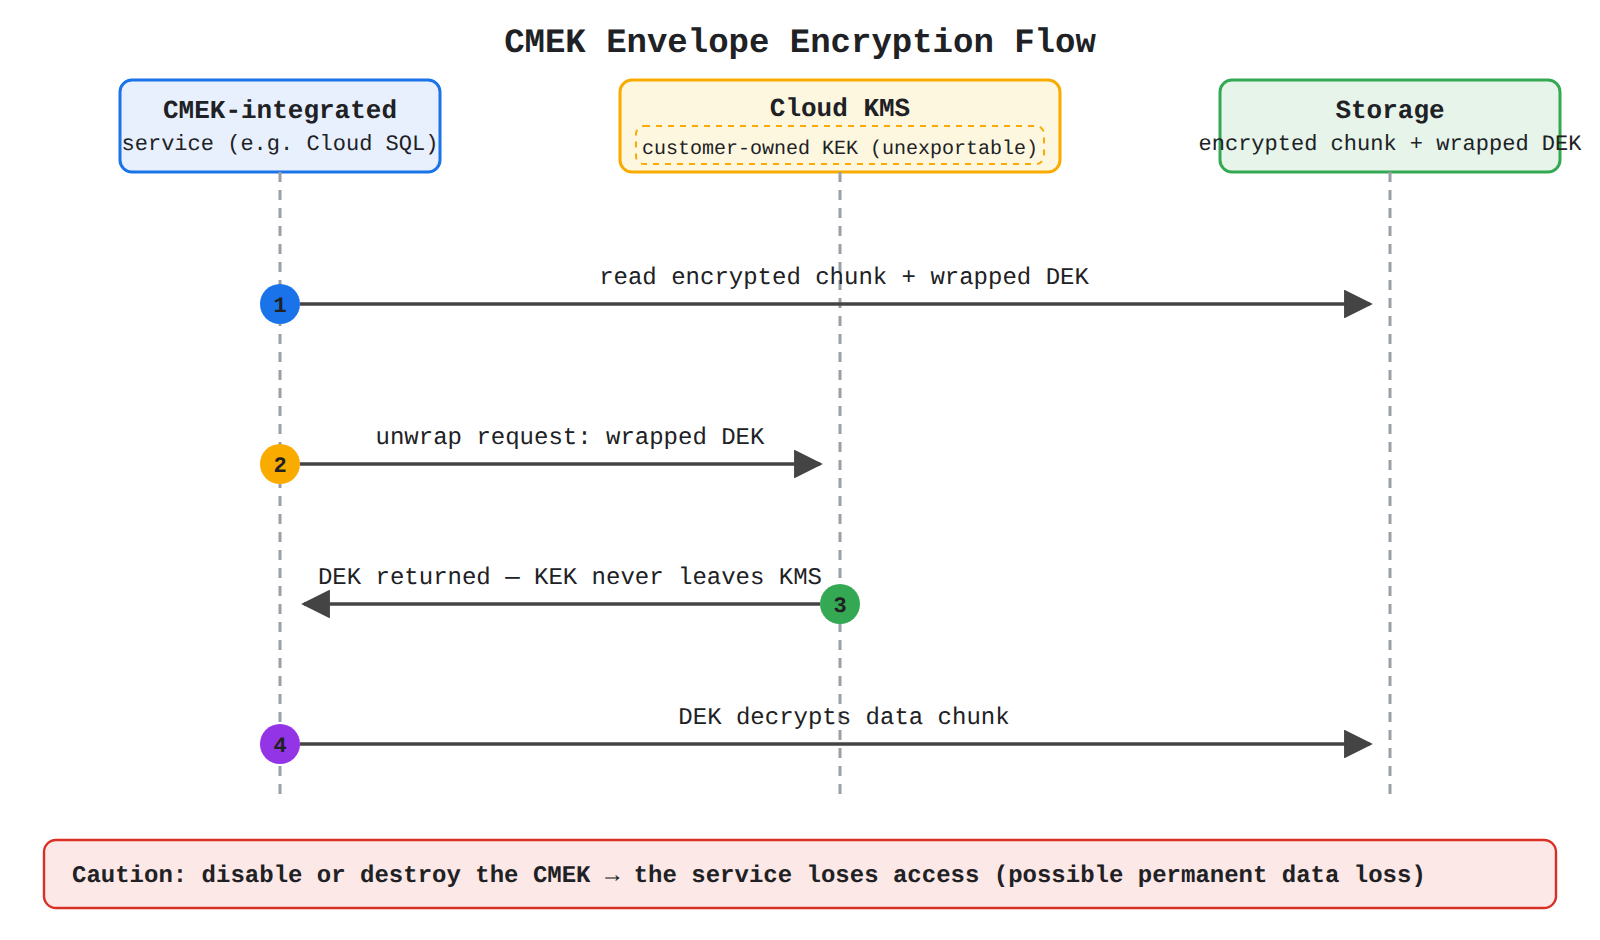
A sequence diagram showing a CMEK-integrated service reading an encrypted chunk and wrapped DEK from storage, sending the wrapped DEK to Cloud KMS, receiving the unwrapped DEK while the customer-owned KEK never leaves KMS, and using the DEK to decrypt the data chunk. Steps reveal in order, with a caution that disabling the key blocks access.
In the Domain
Customer-Managed Keys for Control and Compliance Needs
Customer-managed encryption keys (CMEK) are Cloud KMS keys that the customer controls and uses with CMEK-integrated services such as Filestore and Google SecOps. CMEK uses envelope encryption, where the service generates a data encryption key (DEK) to encrypt the data and the customer's KEK in Cloud KMS wraps, or encrypts, that DEK. Because the service depends on Cloud KMS to unwrap the DEK on every access, revoking or disabling the CMEK blocks the service from reading, writing, ingesting, or processing data.
Domain 1 of 3
Identify use cases for customer-managed encryption keys (CMEK), customer-supplied encryption keys (CSEK), and Google-managed encryption keys (GMEK)
Read the Domain summaryPractice this Domain
27 practice questions
Practice this DomainLast updated