Fundamental
Prepare and test your skills
Fundamental
Prepare and test your skills
CMEK Rotation and Revocation in Cloud KMS
Free sample question, answered and explained below. The Associate Data Practitioner practice bank has 1,156 more like it. Try 10 free: instant score, no account.
An enterprise is planning to store sensitive analytics data in Google Cloud Storage and BigQuery. The security and compliance team establishes the following operational and governance requirements:
- The organization must retain control over the encryption key lifecycle, including defining automatic rotation schedules and immediately revoking key access to make data unreadable.
- The operations team wants to avoid managing dedicated on-premises hardware security modules (HSMs) or passing raw cryptographic keys with every API request.
- Cryptographic keys must be generated, stored, and managed natively within Google Cloud.
Which encryption key management strategy should the organization implement?
Explanations
Customer-Supplied Encryption Keys (CSEK)
Customer-Supplied Encryption Keys (CSEK)
What Customer-Supplied Encryption Keys (CSEK) are:
Customer-Supplied Encryption Keys (CSEK) allow an organization to create and maintain raw AES-256 encryption keys outside of Google Cloud (such as on-premises) and supply the raw key string in the headers of each individual API request made to services like Cloud Storage or Compute Engine.
Why it doesn't meet the requirements:
- High operational burden (✗): Requires the customer to operate external key storage and manage key transmission logic across applications.
- Raw key transmission required (✗): The application must supply the raw key with every read and write API call; Google never stores the raw key.
- No native Cloud KMS storage (✗): Keys are not stored in Google Cloud KMS, making centralized cloud lifecycle controls and automated cloud rotations impossible.
- Risk of permanent data loss (✗): If the customer loses the supplied key, Google cannot recover or decrypt the data.
Key characteristics and limitations:
- Google stores only an ephemeral transient hash in memory to validate requests during processing.
- Limited service integration compared to CMEK (for example, not supported natively across all BigQuery workloads).
- Requires custom application architecture to inject key headers on every request.
This answer would be correct if:
The organization had strict regulatory requirements dictating that encryption keys must never be stored in cloud infrastructure under any circumstances, and the team was prepared to supply raw keys with every API request.
Client-Side Encryption (CSE)
Client-Side Encryption (CSE)
What Client-Side Encryption (CSE) is:
Client-Side Encryption (CSE) is an approach where data is encrypted locally by the client application before it is transmitted over the network and uploaded to Google Cloud. The cloud provider only ever sees already-encrypted ciphertext.
Why it doesn't meet the requirements:
- High development and operational overhead (✗): Applications must incorporate local cryptographic libraries and manage local key storage, rotation, and data decryption before processing.
- Incompatible with server-side cloud analytics (✗): Services like BigQuery cannot natively execute SQL queries, filter records, or perform aggregations on raw data that was encrypted on the client before upload.
- Not stored in Cloud KMS (✗): Encryption occurs entirely outside of Google Cloud's native key management lifecycle.
Key characteristics and limitations:
- Guarantees zero-knowledge storage where cloud services have no mechanism to decrypt the payload.
- Prevents server-side features like indexing, full-text searching, and managed analytical transformations.
- Increases client-side CPU and memory overhead due to local encryption/decryption operations.
This answer would be correct if:
The use case required end-to-end data obfuscation before transmission, where Google Cloud is used strictly as a blind storage repository and no in-cloud SQL querying or analytics are required.
Google-Managed Encryption Keys (GMEK)
Google-Managed Encryption Keys (GMEK)
What Google-Managed Encryption Keys (GMEK) are:
Google-Managed Encryption Keys (GMEK) represent the default encryption-at-rest state in Google Cloud. Google automatically generates, stores, and rotates the encryption keys using internal key management systems without requiring any user configuration.
Why it doesn't meet the requirements:
- No customer lifecycle control (✗): Customers cannot set custom key rotation schedules, inspect key versions, or view key metadata.
- Inability to revoke key access (✗): Customers cannot independently disable or destroy the underlying encryption keys to revoke data access on demand.
- No granular key audit trails (✗): Individual key usage operations are handled by internal Google systems and are not exposed as customer-managed Cloud KMS audit logs.
Key characteristics and limitations:
- Enabled automatically for all data stored at rest in Google Cloud at no additional cost.
- Zero operational overhead for configuration, deployment, or maintenance.
- Does not satisfy strict compliance mandates requiring customer ownership of encryption keys.
This answer would be correct if:
The organization wanted default, zero-configuration encryption at rest without needing custom rotation policies, compliance key ownership, or administrative control over key lifecycles.
Customer-Managed Encryption Keys (CMEK)
Customer-Managed Encryption Keys (CMEK)
What Customer-Managed Encryption Keys (CMEK) are:
Customer-Managed Encryption Keys (CMEK) allow organizations to manage their own cryptographic keys inside Google Cloud using Cloud Key Management Service (Cloud KMS) or Cloud HSM. With CMEK, the customer creates and controls the root key (Key Encryption Key or KEK) used to protect the data encryption keys (DEKs) generated by Google Cloud services like BigQuery and Cloud Storage.
How it meets all requirements:
- Lifecycle control and rotation (✓): Cloud KMS allows administrators to configure automated key rotation schedules (such as every 90 days) and generate new key versions without manually re-encrypting existing data.
- Immediate access revocation (✓): Administrators can disable or destroy a key version directly in Cloud KMS. Disabling the key immediately revokes access, rendering protected data inaccessible to all services and users.
- No on-premises infrastructure or per-request key transmission (✓): Keys reside securely within Google Cloud KMS, removing the operational burden of managing physical on-premises HSMs or passing raw key strings in API headers.
- Native Google Cloud integration (✓): Cloud KMS seamlessly integrates with services like BigQuery, Cloud Storage, Dataproc, and Compute Engine through service account IAM permissions.
CMEK Rotation to Revocation Lifecycle
State / Lifecycle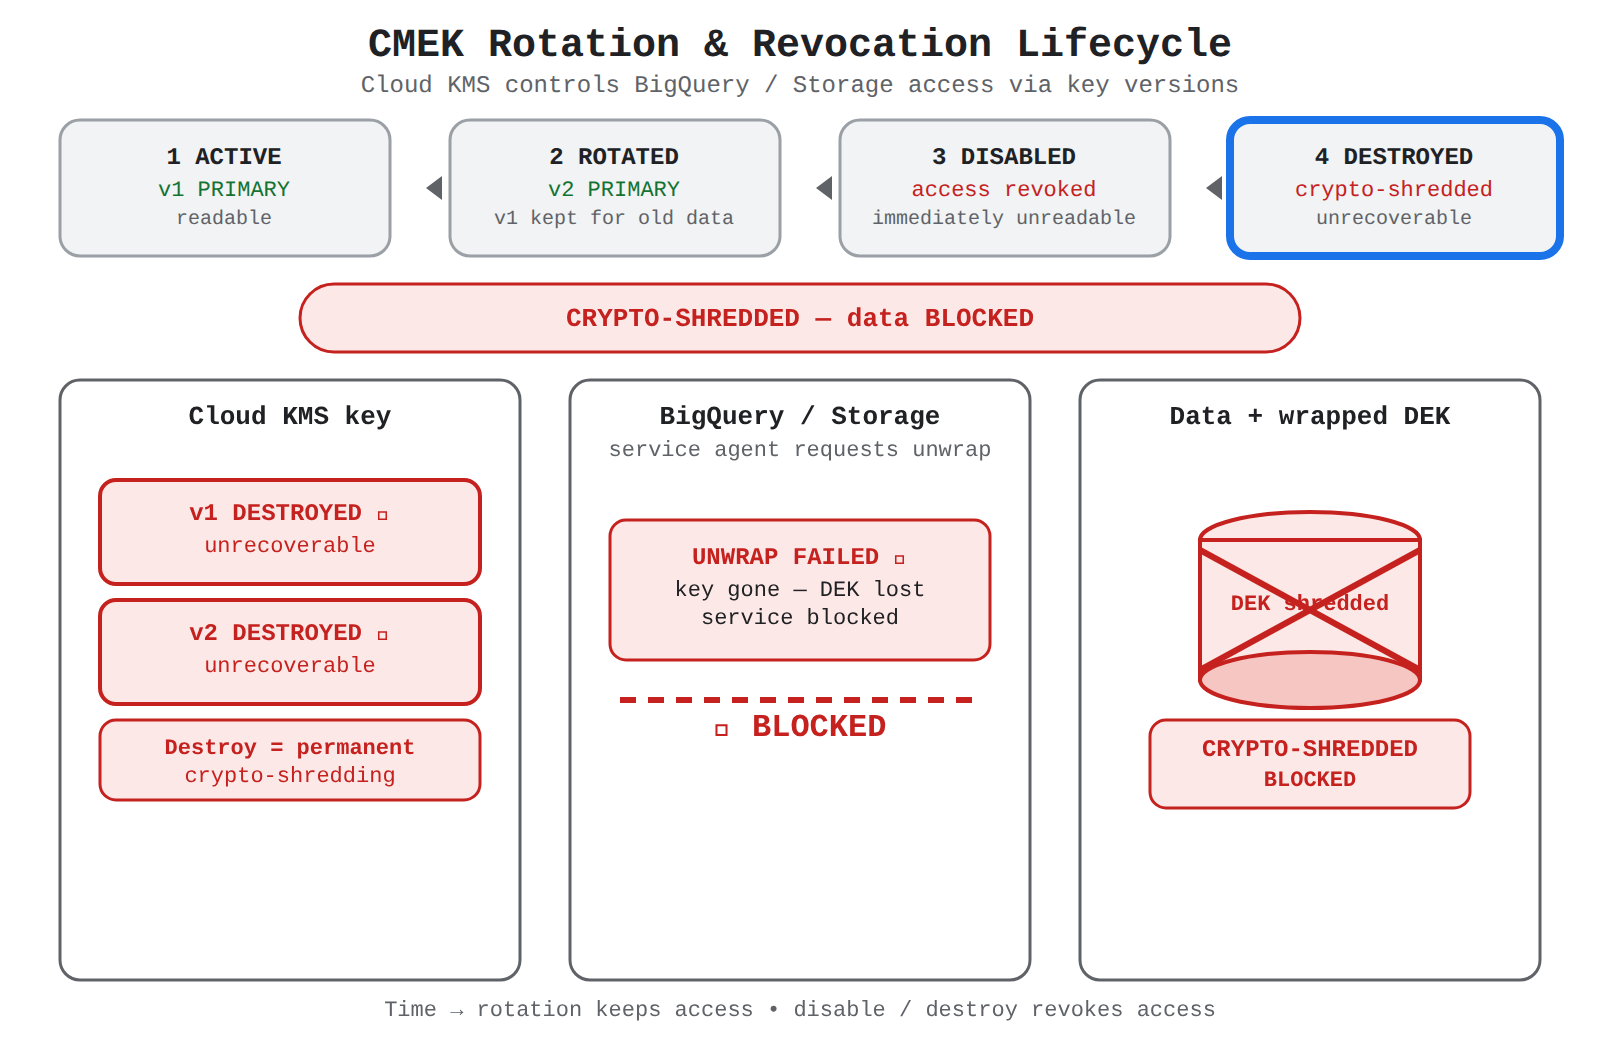
Key advantages and capabilities:
- Granular IAM permissions: Control who can administer, encrypt, and decrypt using specific Cloud KMS keys.
- Comprehensive audit logging: Every key access, encryption, and decryption action is logged in Cloud Audit Logs.
- Automated key lifecycle policies: Define destruction delays, scheduled rotation intervals, and primary key version transitions.
- Separation of duties: Distinct roles can be assigned to security administrators (key managers) and data practitioners (data users).
Why this is optimal:
CMEK provides the ideal balance between security compliance and operational efficiency. Unlike GMEK, it provides full customer control over key lifecycles and revocation. Unlike CSEK, it eliminates the operational risk of key loss and the complexity of supplying raw cryptographic keys with every API request.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 1,156 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Data Practitioner
CMEK vs CSEK vs GMEK
Identify use cases for customer-managed encryption keys (CMEK), customer-supplied encryption keys (CSEK), and Google-managed encryption keys (GMEK)
FundamentalAssociate Data Practitioner
CMEK vs CSEK vs Google-Managed Encryption Keys
Identify use cases for customer-managed encryption keys (CMEK), customer-supplied encryption keys (CSEK), and Google-managed encryption keys (GMEK)
FundamentalAssociate Data Practitioner
Cloud SQL PITR and Cloud Storage Object Versioning
Compare backup and recovery solutions offered as Google-managed services
FundamentalAssociate Data Practitioner
Eventarc Trigger Cloud Run
Use Eventarc triggers in event-driven pipelines (Dataform, Dataflow, Cloud Functions, Cloud Run, Cloud Composer)
FundamentalAssociate Data Practitioner
Structured Data Cloud SQL BigQuery
Classify use cases into having structured, unstructured, or semi-structured data requirements
AdvancedProfessional Data Engineer
Data Sovereignty With CMEK And VPC Service Controls
Regional considerations (data sovereignty) for data access and storage
Last updated