Diagram
Cloud NAT Outbound Flow in Sequence
Sequence
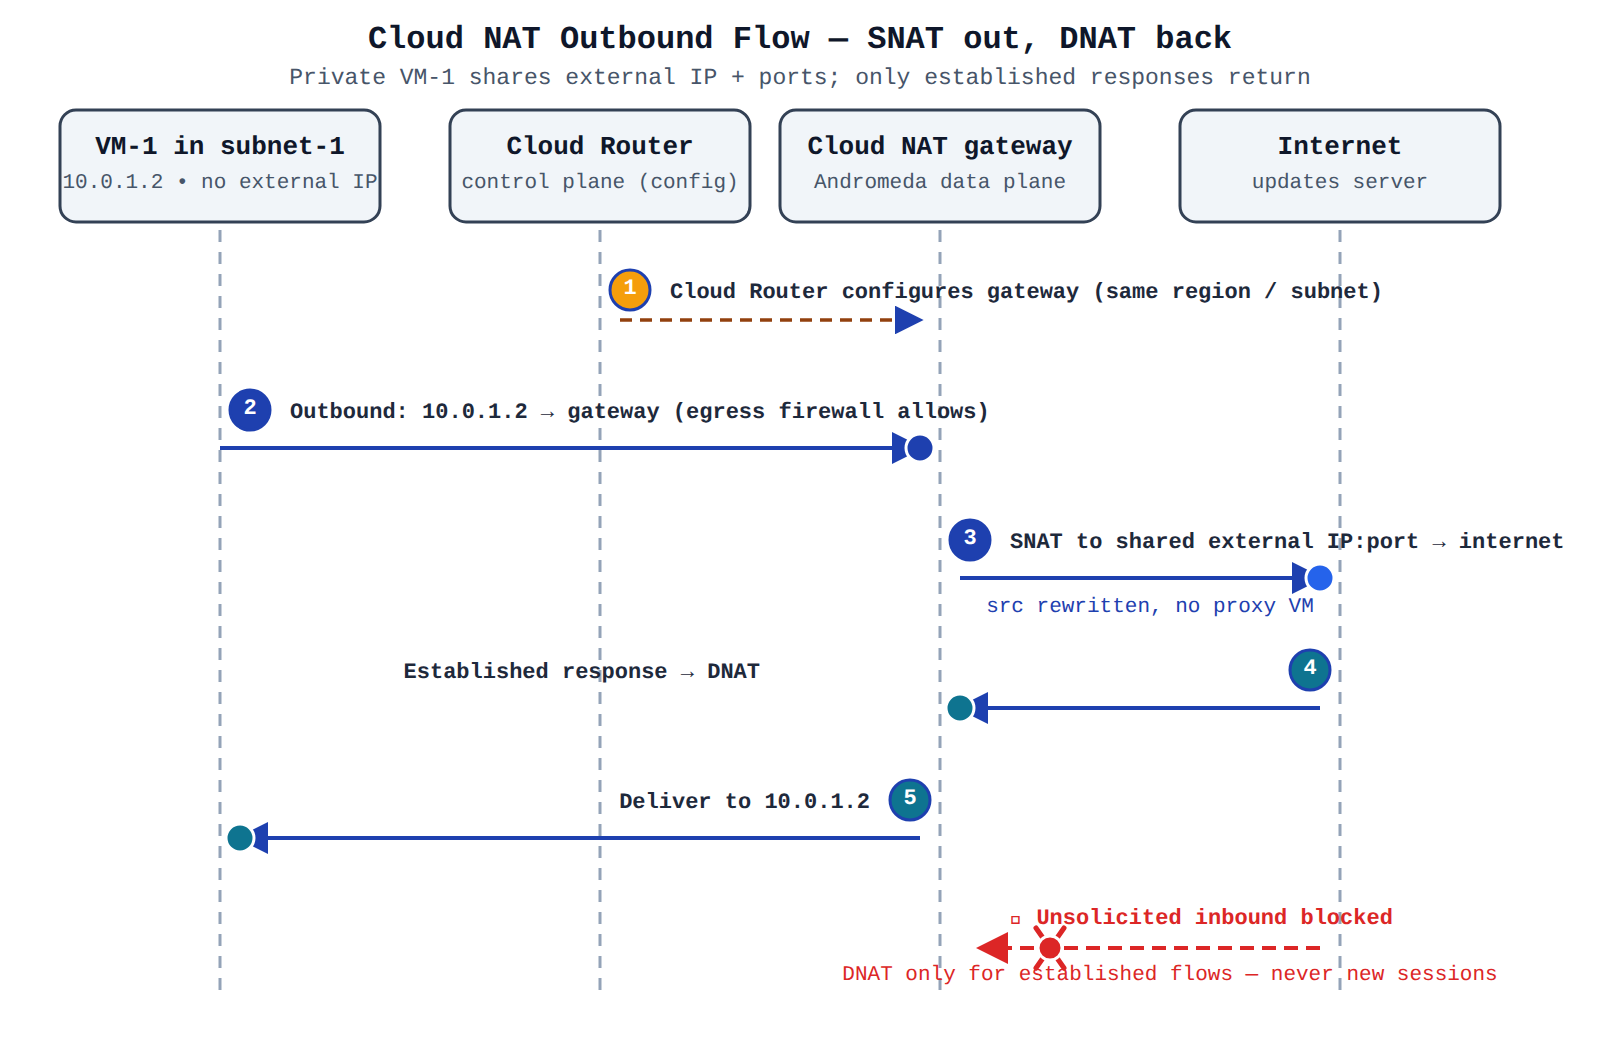
A sequence diagram showing VM-1 sending outbound traffic through Cloud NAT with SNAT to the internet and DNAT for the established response, while unsolicited inbound is blocked.
In the Domain
How Cloud NAT Enables Outbound Access for Private VMs
Outbound access for private VMs through Cloud NAT works by sharing a set of external addresses and ports instead of giving each VM its own external IP address. A Cloud NAT gateway allocates a set of external IP addresses and source ports to each VM that uses the gateway, and outbound traffic flows from the VM internal address through the gateway to the internet destination. For example, VM-1 in subnet-1 has no external IP address but needs to download updates, so a gateway configured for the address range of subnet-1 lets VM-1 send traffic by using its internal address. Cloud NAT performs source network address translation (source NAT or SNAT) for outbound packets and destination network address translation (destination NAT or DNAT) for the matching inbound responses.
Domain 5 of 5
Working with Cloud DNS and Cloud NAT
Read the Domain summaryPractice this Domain
24 practice questions
Practice this DomainLast updated