Diagram
Short-Lived Credential Creation Flow
Sequence
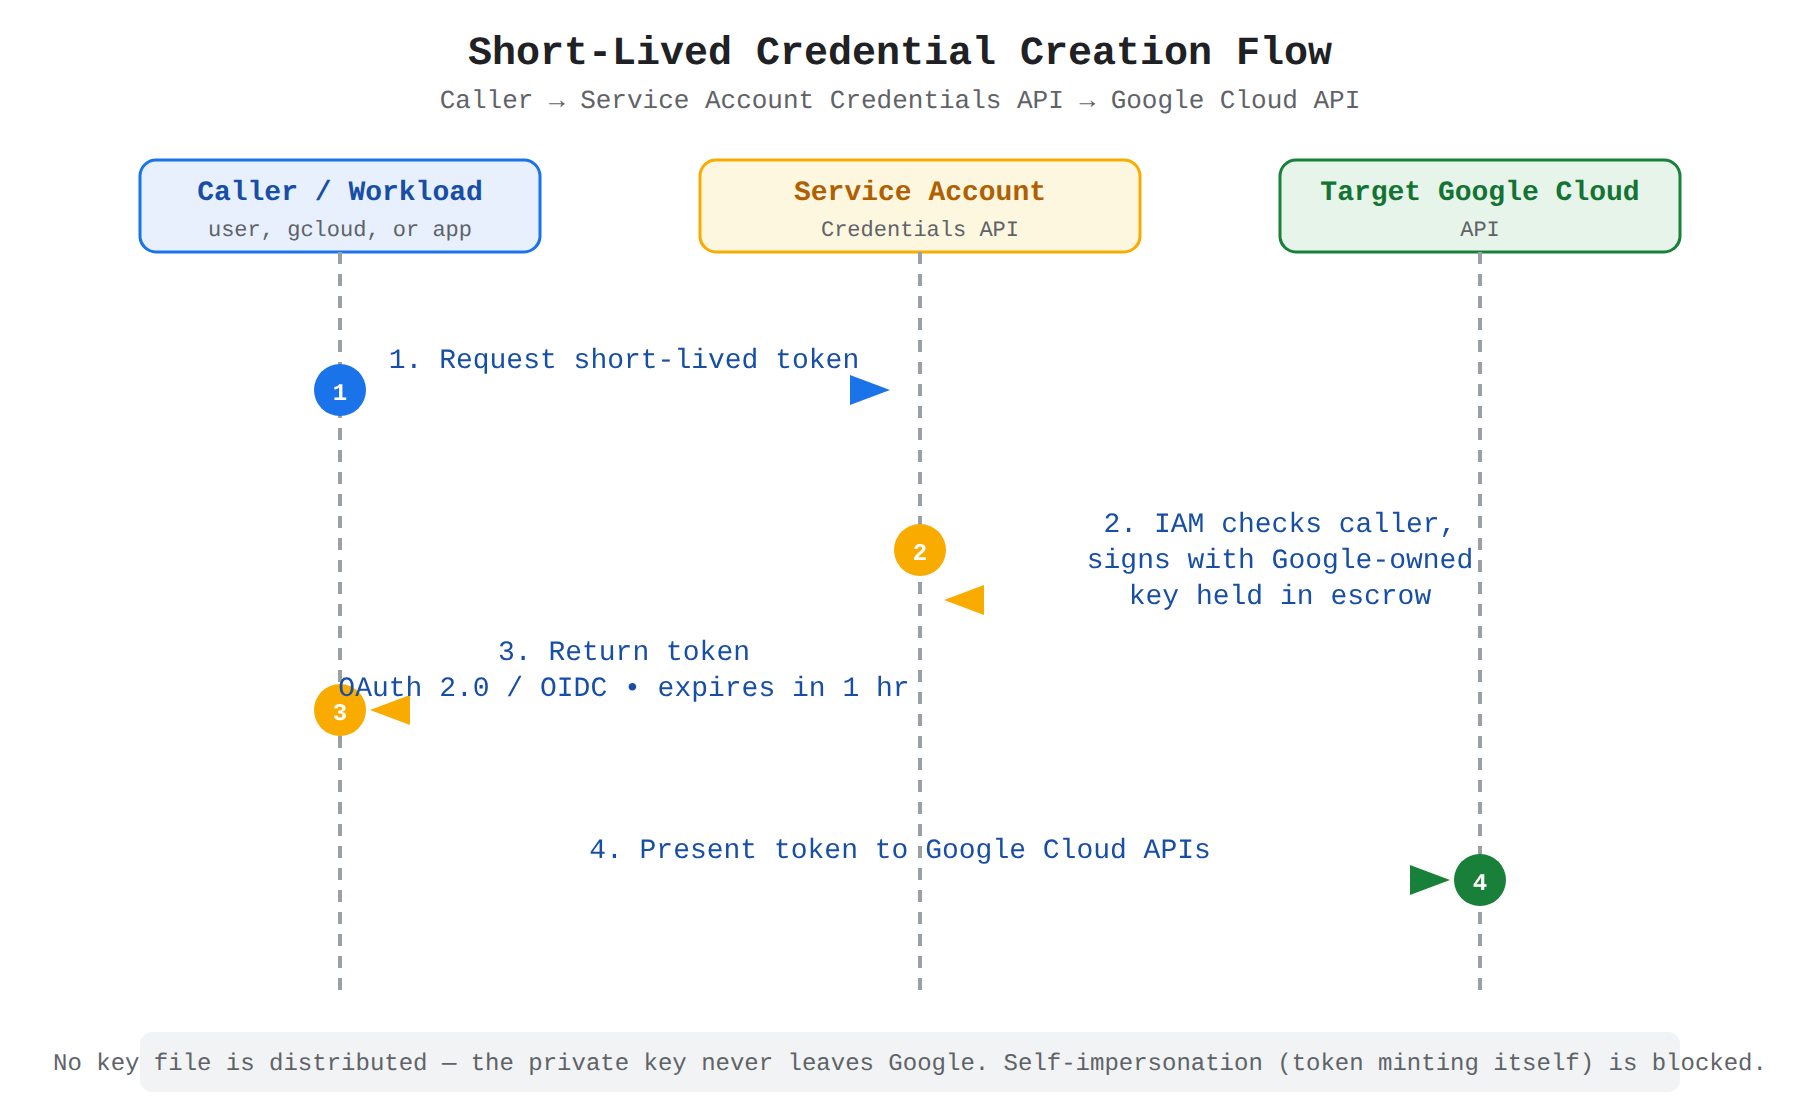
A sequence diagram with three lifelines: the caller workload, the Service Account Credentials API, and the target Google Cloud API. Animated arrows show the caller requesting a short-lived token, the API signing it with the escrowed Google-owned key, the token returning to the caller with a 1-hour default expiry, and the caller presenting the token to the Google Cloud API.
In the Domain
How Short-Lived Credentials Are Created
How short-lived credentials are created depends on a trusted identity asking the Service Account Credentials API to mint them on demand. In many cases the credentials are obtained automatically, so no key file has to be distributed. The flow always runs from the API to the requesting workload, and the workload then presents the credential to Google Cloud APIs:
- gcloud CLI request with the
--impersonate-service-accountflag creates short-lived credentials for that service account and runs the command with them. - Attached service account on a Compute Engine virtual machine (VM) instance lets code on the instance use Application Default Credentials (ADC) to obtain short-lived credentials through client libraries.
- Workload identity federation lets an external identity provider exchange its own credentials for short-lived service account credentials.
Domain 6 of 7
Creating and managing short-lived service account credentials
Read the Domain summaryPractice this Domain
24 practice questions
Practice this DomainLast updated