Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Folder Level Firewall Enforcement for Production VPCs
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your company has multiple Google Cloud projects grouped under a folder named Production. The central security team requires a baseline security rule to block all inbound traffic on port 22 (SSH) from the internet across all existing and future Virtual Private Cloud (VPC) networks inside this folder, without relying on individual project administrators.
Which type of firewall policy should you create and associate with the folder?
Explanations
A classic VPC firewall rule
A classic VPC firewall rule
What Classic VPC Firewall Rules Are
Classic VPC firewall rules (traditional firewall rules) are legacy firewall rules defined directly inside a single VPC network to allow or deny ingress and egress traffic to VM instances using network tags or service accounts.
Why It Doesn't Meet the Requirement
- Project and VPC bounded: Classic VPC firewall rules exist strictly inside a single VPC network. They have no awareness of resource hierarchy and cannot be applied to a folder or organization.
- Cannot prevent overrides: Rules configured inside a VPC can be modified or deleted by users holding project-level network administration permissions in that project.
- No inheritance: New projects and VPC networks created in the folder will not receive these rules unless explicitly scripted or manually created each time.
Key Characteristics and Limitations
- Scoped exclusively to the specific VPC in which they are created.
- Evaluated after any hierarchical firewall policies.
- Lack modern NGFW capabilities such as hierarchical inheritance, reusable policy objects, and integration with hierarchical tags.
This Answer Would Be Correct If
You needed to configure custom, project-specific port allowances for an application running inside one individual VPC network without needing organization-wide or folder-level governance.
A regional network firewall policy
A regional network firewall policy
What Regional Network Firewall Policies Are
A regional network firewall policy is a Cloud NGFW policy defined in a specific Google Cloud region and associated with a particular VPC network to govern traffic only within that designated region.
Why It Doesn't Meet the Requirement
- Bound to VPC and region scopes: Regional network firewall policies attach to individual VPC networks and only apply to VM instances residing within a specific region (such as
us-central1). They cannot attach to a folder. - Fails folder-wide coverage: A regional policy cannot enforce security across multiple projects and regions automatically.
- Manual attachment required: Every VPC in each project would require separate regional policy configurations and associations.
Key Characteristics and Limitations
- Limited to a single region within a target VPC.
- Evaluated alongside other network-level firewall policies after hierarchical policies.
- Useful for regional compliance or data-residency network control, not organization-wide or folder-wide baselines.
This Answer Would Be Correct If
The requirement was to enforce specific firewall rules for resources located exclusively within a single region of a specific VPC network (e.g., satisfying local regulatory requirements in europe-west3).
A global network firewall policy
A global network firewall policy
What Global Network Firewall Policies Are
A global network firewall policy is a Cloud Next Generation Firewall (NGFW) policy that groups firewall rules and attaches to one or more individual VPC networks, applying those rules globally across all regions within the attached VPCs.
Why It Doesn't Meet the Requirement
- Incorrect scope of application: Global network firewall policies can only be associated with VPC networks, not with folders or the organization level.
- High administrative overhead: Because they cannot attach to folders, administrators would have to manually attach the policy to every existing VPC in every project, and remember to attach it to any newly created VPCs in the future.
- Vulnerable to omission: Future projects and VPCs created in the folder would not automatically inherit the policy, violating the requirement for automatic, folder-wide enforcement.
Key Characteristics and Limitations
- Enforced at the network scope rather than the organizational hierarchy scope.
- Evaluated after hierarchical firewall policies.
- Must be explicitly associated with each VPC network via a network association.
This Answer Would Be Correct If
You needed to enforce a consistent set of firewall rules across all regions of a single VPC network (or specifically selected VPC networks) within a project, rather than enforcing baseline security across an entire folder hierarchy.
A hierarchical firewall policy
A hierarchical firewall policy
What Hierarchical Firewall Policies Are
Hierarchical firewall policies are security policies created and applied at the Organization or Folder level in the Google Cloud resource hierarchy. They allow organization administrators and central security teams to define and enforce consistent firewall rules across all projects and Virtual Private Cloud (VPC) networks contained within that organization or folder.
How It Meets the Requirements
- Folder-level enforcement: Hierarchical firewall policies attach directly to folders (such as the
Productionfolder) or the root organization node, applying automatically to all current and future projects beneath that hierarchy. - Consistent baseline security: Rules defined in a hierarchical firewall policy are evaluated before any VPC-level firewall rules or network firewall policies. This ensures individual project owners cannot bypass or override the mandatory restriction blocking port 22 from the public internet.
- Centralized management: Project administrators do not need to configure separate rules in each VPC, eliminating manual configuration and drift.
Firewall Rule Evaluation Precedence
Process Flow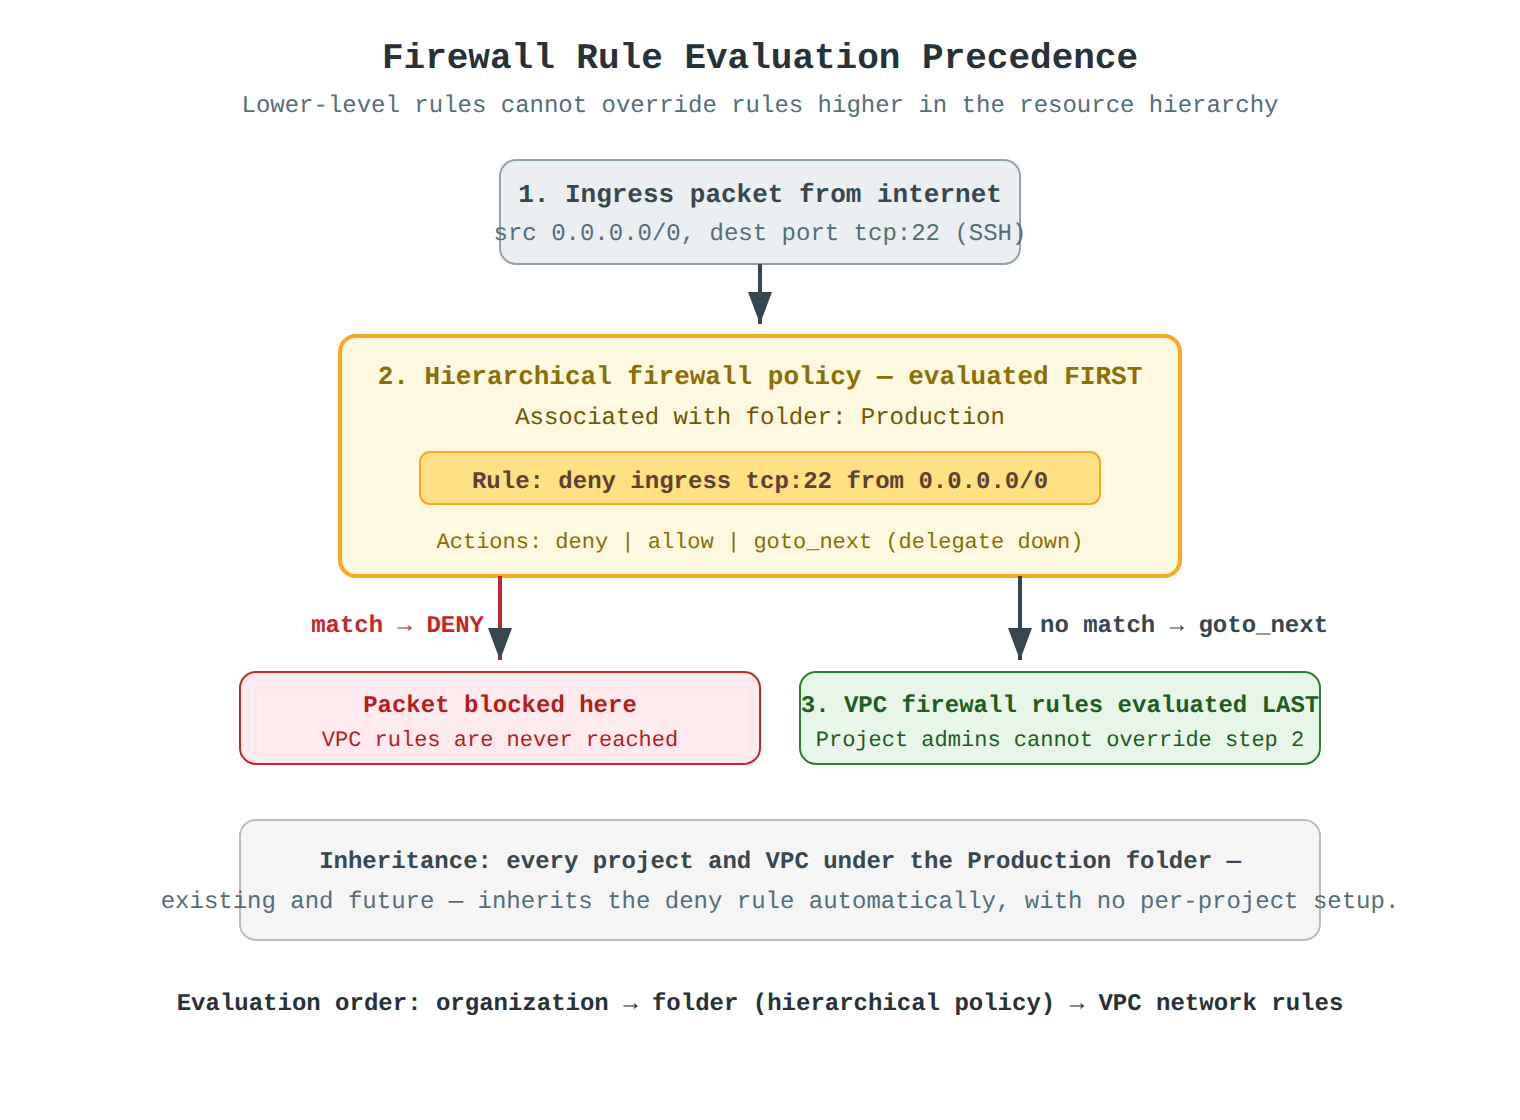
Key Advantages and Capabilities
- Inheritance: Any new VPC network created in any project inside the folder immediately inherits the policy rules without additional action.
- Precedence over VPC rules: Evaluated at the top of the firewall rule evaluation order, guaranteeing organizational guardrails.
- Delegation options: Supports rule actions such as
allow,deny, orgoto_nextto allow traffic evaluation to pass down to lower-level policies or VPC rules when appropriate. - Granular targeting: Rules can target all VMs or specific VMs using secure tags across projects within the folder scope.
Why This Is Optimal
Applying a hierarchical firewall policy to the Production folder is the only solution that enforces uniform security controls at the folder scope across multiple projects simultaneously, preventing individual project administrators from misconfiguring or overriding critical perimeter defenses.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Cloud Run Internal Ingress Setting
Creating and applying Cloud Next Generation Firewall (Cloud NGFW) policies with ingress and egress rules and attributes (e.g., action, source, destination, targets, protocols, ports)
FundamentalAssociate Cloud Engineer
VPC Firewall Ingress Rule Attributes
Creating and applying Cloud Next Generation Firewall (Cloud NGFW) policies with ingress and egress rules and attributes (e.g., action, source, destination, targets, protocols, ports)
FundamentalAssociate Cloud Engineer
Ops Agent Third-Party Metric Ingestion
Creating and ingesting Cloud Monitoring custom metrics (e.g., from applications or logs)
FundamentalAssociate Cloud Engineer
Dedicated vs Partner Interconnect
Establishing network connectivity (e.g., Cloud VPN, VPC Network Peering, Cloud Interconnect)
FundamentalAssociate Cloud Engineer
BigQuery Federated Queries EXTERNAL_QUERY
Executing queries to retrieve data from data instances (e.g., Cloud SQL, BigQuery, Bigtable, Spanner, Firestore, AlloyDB)
AdvancedProfessional Cloud Network Engineer
Dedicated Interconnect 99.99% Single-Region SLA
Creating Dedicated Interconnect connections and configuring VLAN attachments.
Last updated