Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Analyzing Inherited IAM Policies with Cloud Asset Inventory
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your company manages a complex Google Cloud environment structured with an Organization node, multiple departmental Folders, and dozens of Projects. Due to policy inheritance from ancestor nodes, security administrators need to analyze effective permissions across all cloud resources to detect potential security risks and understand asset dependencies.
Which service or capability should the administrators use to analyze IAM policy inheritance and export asset relationships across the entire hierarchy?
Explanations
Use the Google Workspace Super Admin console to audit all project and resource access policies
Use the Google Workspace Super Admin console to audit all project and resource access policies
What the Google Workspace Super Admin Console Is
Google Workspace Admin console (and Cloud Identity management) manages identity-level configurations, directory users, user groups, and domain-level security settings for an enterprise domain.
Why It Doesn't Meet the Requirement
- No Resource Metadata Access: The Super Admin console manages users, groups, and global organization administration, but it does not store, evaluate, or export Google Cloud resource metadata (such as VM instances, subnets, or storage buckets).
- Lacks IAM Policy Analysis: It cannot calculate effective project-level permissions or identify resource configuration risks within Google Cloud projects and folders.
Key Characteristics and Limitations
- Domain-Focused: Handles user life cycles, Single Sign-On (SSO), 2-Step Verification, and Workspace applications.
- Initial Bootstrap Role: Super Admins are typically responsible for initial domain setup and assigning the Organization Admin role, not performing day-to-day cloud resource auditing.
- No Cloud Asset Visibility: Does not interact directly with resource-level IAM policies or dependency mapping.
This Answer Would Be Correct If
The requirement was to manage user accounts, assign domain-wide administrator privileges, or manage Cloud Identity directory groups across the enterprise domain.
Query the Service Usage API consumer policy analyzer for all active services in each project
Query the Service Usage API consumer policy analyzer for all active services in each project
What the Service Usage API Is
Service Usage API is designed to enable, disable, and inspect the status of Google Cloud APIs and services across projects, folders, and organizations.
Why It Doesn't Meet the Requirement
- Wrong Scope of Analysis: The Service Usage API inspects which APIs and consumer policies are enabled on a given resource; it does not evaluate IAM principals, identity role bindings, or effective user permissions.
- No Resource Asset Repository: It does not maintain an inventory of cloud infrastructure resources (such as Compute Engine VMs or Cloud Storage buckets) or map relationships between them.
- Missing IAM Export Functionality: It lacks the ability to generate snapshots of IAM policies across the organization hierarchy.
Key Characteristics and Limitations
- API Activation Focus: Primarily used to control quota, activate specific Google Cloud APIs, and enforce service enablement restrictions.
- No Entitlement Mapping: Cannot identify over-privileged user accounts or analyze privilege escalation risks.
This Answer Would Be Correct If
The goal was to determine which Google Cloud APIs (such as Compute Engine API or Cloud Functions API) are enabled and active across individual projects.
Use Cloud Asset Inventory to analyze and export resource metadata and IAM policy hierarchies across the organization
Use Cloud Asset Inventory to analyze and export resource metadata and IAM policy hierarchies across the organization
What Cloud Asset Inventory Is
Cloud Asset Inventory is a fully managed metadata repository service provided by Google Cloud. It enables organizations to view, monitor, analyze, and export comprehensive asset and access metadata across an entire Google Cloud Organization, Folder, or Project hierarchy.
How It Meets the Requirements
- Hierarchy-wide IAM Analysis: Cloud Asset Inventory provides deep visibility into how access is inherited across resource levels. Because permissions set on an organization or folder node cascade down through child folders and projects, Cloud Asset Inventory evaluates the full inheritance chain to determine effective permissions.
- Metadata and Policy Export: Through permissions like
cloudasset.assets.exportIamPolicyandcloudasset.assets.exportResource, administrators can export large-scale snapshots of all resources and their associated IAM bindings for security evaluation and auditing. - Detecting Security Risks: It allows security teams to query and analyze relationships between resources and identities, exposing over-privileged users and misconfigured access rules across complex multi-project structures.
Org to Resource IAM Inheritance Chain
Hierarchy / Taxonomy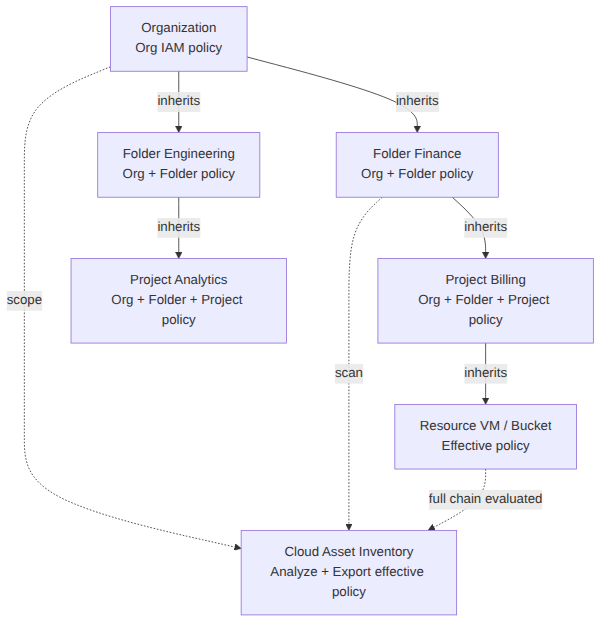
Key Advantages and Capabilities
- Comprehensive Visibility: Captures hundreds of Google Cloud resource types and IAM policies in a single centralized inventory.
- Policy Analysis: Supports IAM policy analysis to determine who has access to what resources and why (including direct vs. inherited access).
- Export to BigQuery and Cloud Storage: Facilitates long-term compliance auditing by exporting full asset dumps and changes over time.
- Real-Time Feeds: Allows monitoring of asset and policy changes via Cloud Pub/Sub for automated alerting.
Why This Is Optimal
Cloud Asset Inventory is the purpose-built Google Cloud service for discovering asset dependencies and evaluating organizational access graphs. Manually inspecting individual projects cannot account for nested inheritance at scale, making Cloud Asset Inventory the only enterprise-grade, comprehensive choice.
Inspect and manage permissions individually using Project-level IAM settings in the Google Cloud console
Inspect and manage permissions individually using Project-level IAM settings in the Google Cloud console
What Project-Level IAM Management Is
Project-level IAM management refers to configuring and viewing access control lists, roles, and bindings directly within an individual project's IAM page in the Google Cloud console, the gcloud CLI, or the Resource Manager API.
Why It Doesn't Meet the Requirement
- Fails to Capture Complete Inheritance: While project-level IAM shows local bindings and inherited parent roles for that specific project, it requires administrators to manually inspect each project one by one.
- Not Scalable: In an organization with dozens or hundreds of projects, reviewing each project individually is prone to error and provides no centralized export or relationship mapping mechanism.
- No Global Graph Analysis: It does not provide a holistic view of asset dependencies, folder structures, or organization-wide policy graphs.
Key Characteristics and Limitations
- Scoped to Single Project: Changes and visibility are focused primarily on the targeted project boundary.
- High Administrative Burden: Lacks bulk query and programmatic snapshot capabilities across multi-folder hierarchies.
- Limited Dependency Mapping: Does not visualize resource-to-resource or parent-to-child relationships across the enterprise.
This Answer Would Be Correct If
Administrators only needed to grant, update, or revoke a role assignment for a single user on one specific project without evaluating broad organizational risk or dependencies.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Cloud Asset Inventory Search and BigQuery Export
Configuring Cloud Asset Inventory and using Gemini Cloud Assist to analyze resources
FundamentalAssociate Cloud Engineer
Gemini Cloud Assist Required APIs
Configuring Cloud Asset Inventory and using Gemini Cloud Assist to analyze resources
FundamentalAssociate Cloud Engineer
Custom-Mode VPC Network
Setting up cloud networking
FundamentalAssociate Cloud Engineer
Cloud Storage Signed URLs
Managing and securing objects in Cloud Storage buckets
FundamentalAssociate Cloud Engineer
Service Account VM Access Scopes vs IAM
Using service accounts in IAM policies with minimum permissions
IntermediateProfessional Cloud Architect
Vertex AI Security Architecture
Securing AI (e.g., Model Armor, Sensitive Data Protection, and secure model deployment)
Last updated