Diagram
Microsoft Sentinel Ingestion and Response Flow
Process Flow
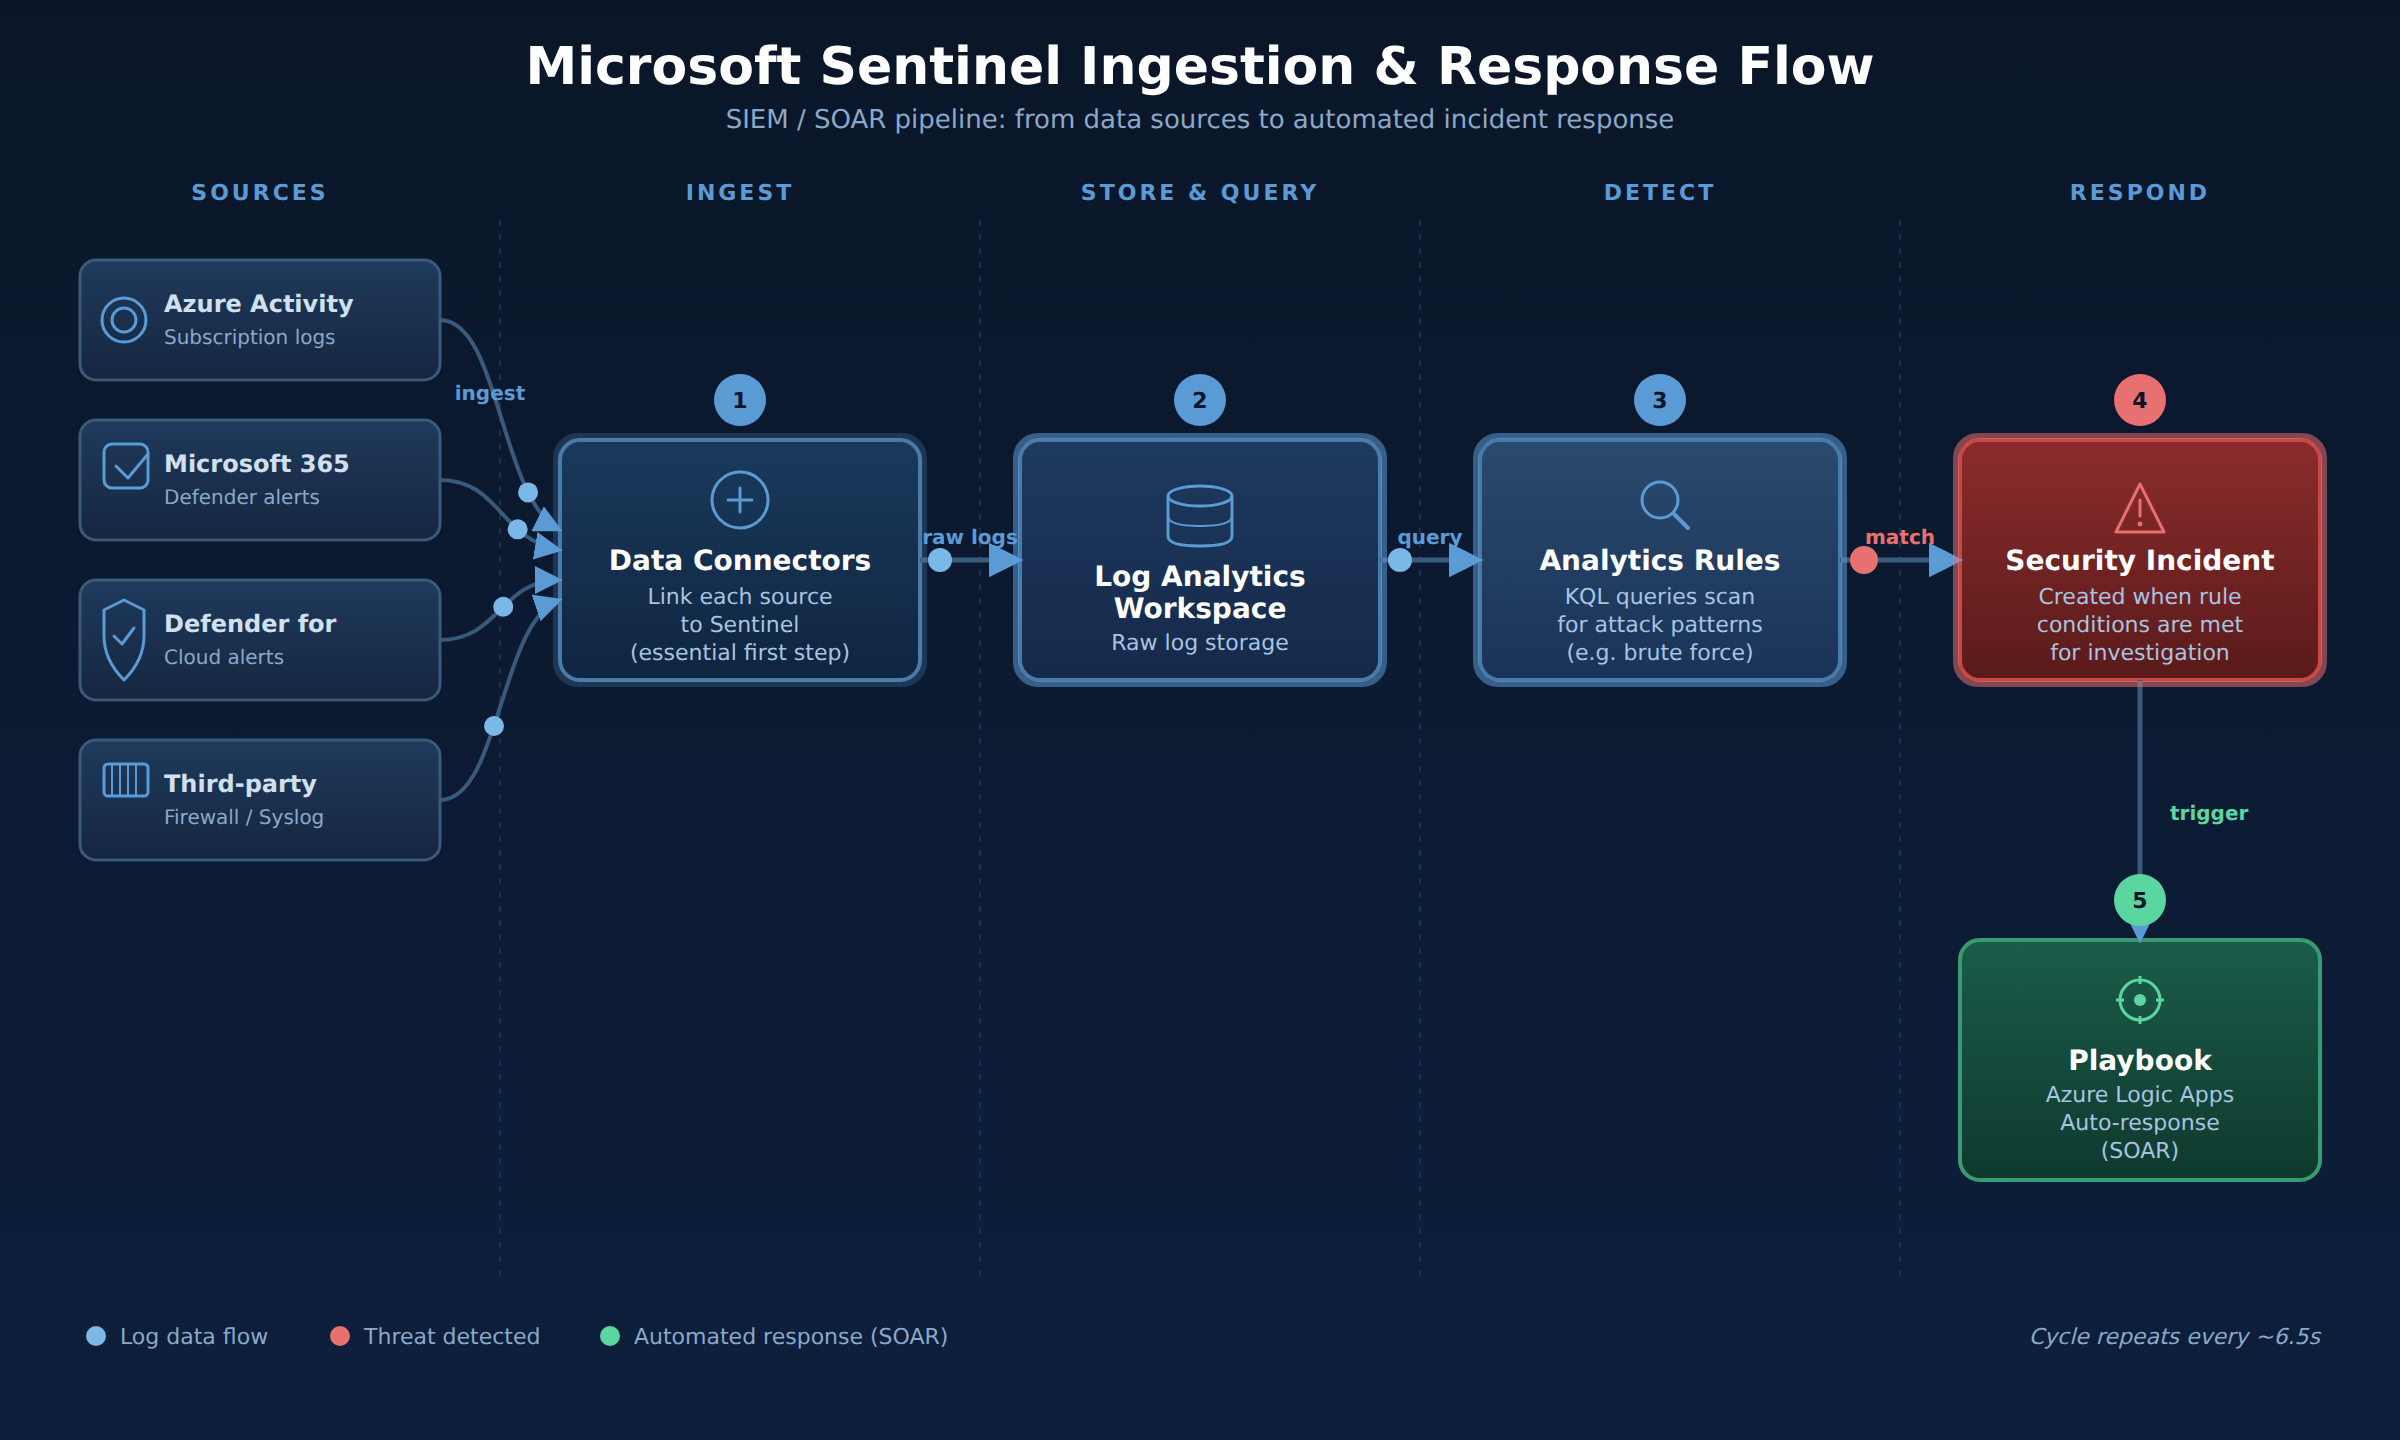
A process flow showing security data sources feeding through data connectors into a Log Analytics workspace, where analytics rules create incidents that trigger Logic Apps playbooks for automated response.
In the Domain
Configure Data Connectors in Microsoft Sentinel
Microsoft Sentinel is a cloud-native Security Information and Event Management (SIEM) system that aggregates security data from many sources. To bring data into Sentinel, you configure data connectors. Each connector links to a specific service like Azure Activity Logs, Microsoft 365 Defender, or a third-party firewall, and pulls raw log data from that source into Sentinel's underlying Log Analytics workspace. Configuring connectors is the essential first step to centralizing security monitoring—without data flowing in, Sentinel cannot perform analysis or generate insights.
Domain 4 of 4
Secure Azure using Microsoft Defender for Cloud and Microsoft Sentinel
Read the Domain summaryPractice this Domain
43 practice questions
Practice this DomainLast updated