Diagram
Azure Policy Admission Control Flow in AKS
Process Flow
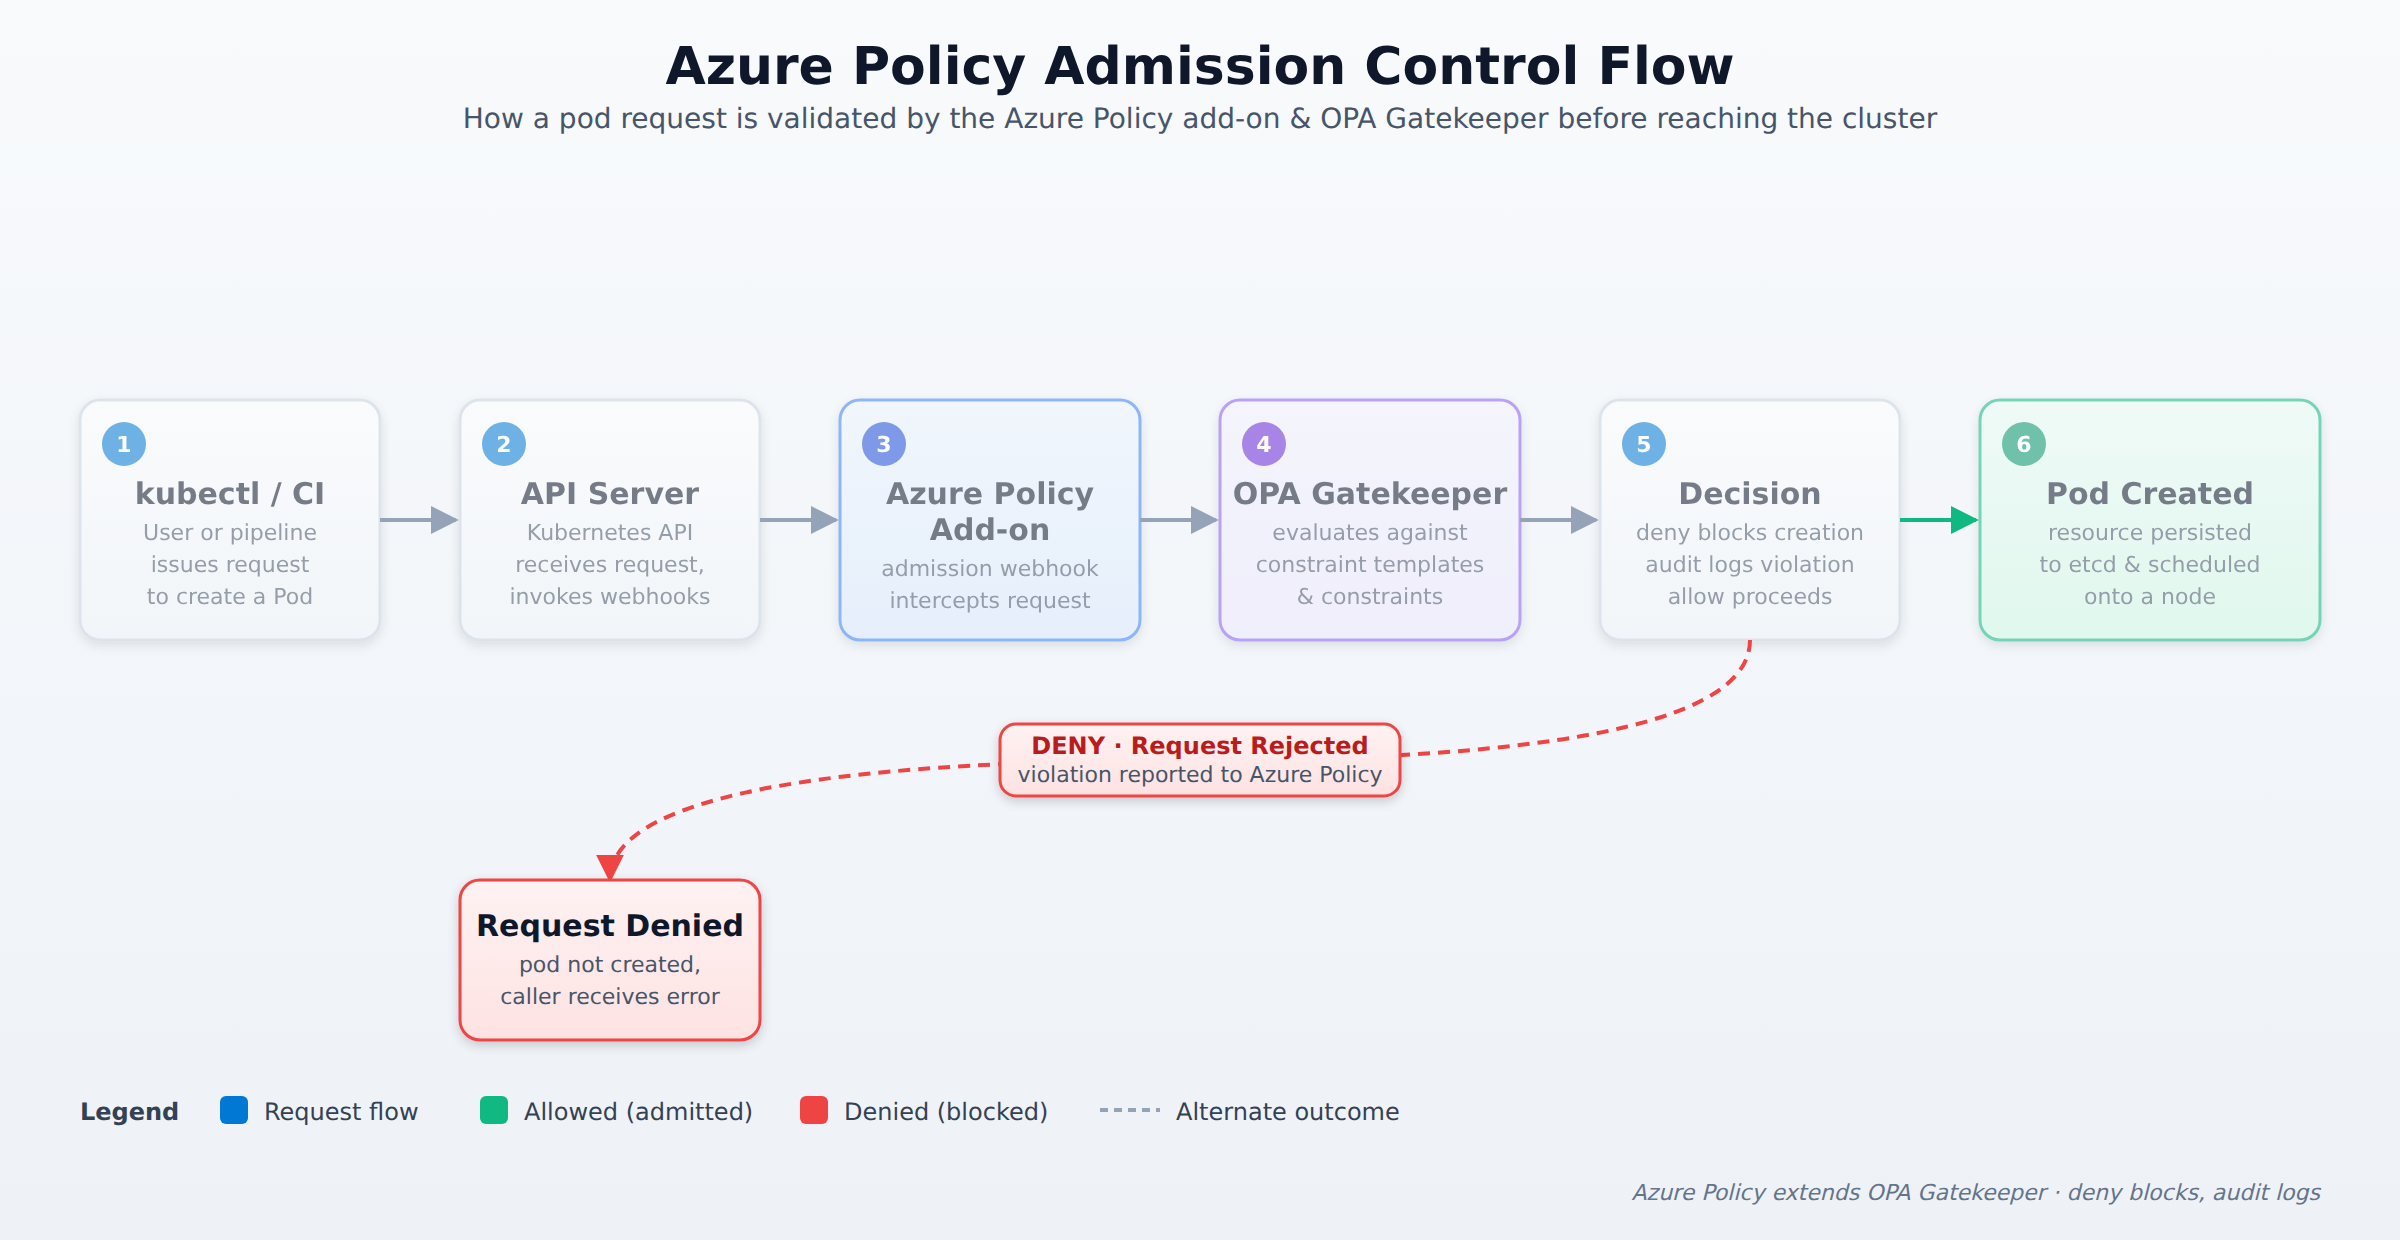
A horizontal process flow showing a pod request entering the AKS API server, being intercepted by the Azure Policy add-on and OPA Gatekeeper, evaluated against constraint templates, and either denied or admitted and created in the cluster. Animated packet motion conveys the order of the admission control sequence.
In the Domain
Azure Policy for Kubernetes
Azure Policy for Kubernetes extends the Open Policy Agent (OPA) Gatekeeper to enforce security and compliance rules directly inside your AKS cluster. By installing the Azure Policy add-on, you deploy policy definitions that act as constraint templates and constraints. The add-on continuously evaluates resources like pods and namespaces against these policies. If a resource violates a policy set to deny mode, its creation is blocked; if the policy is in audit mode, the violation is logged. This provides real-time enforcement and centralized compliance reporting without manual checks, ensuring security configurations are uniformly applied.
Domain 3 of 9
Secure and monitor AKS
Read the Domain summaryPractice this Domain
1 practice question
Practice this DomainLast updated