Diagram
App Service Certificate Lifecycle with Key Vault
Process Flow
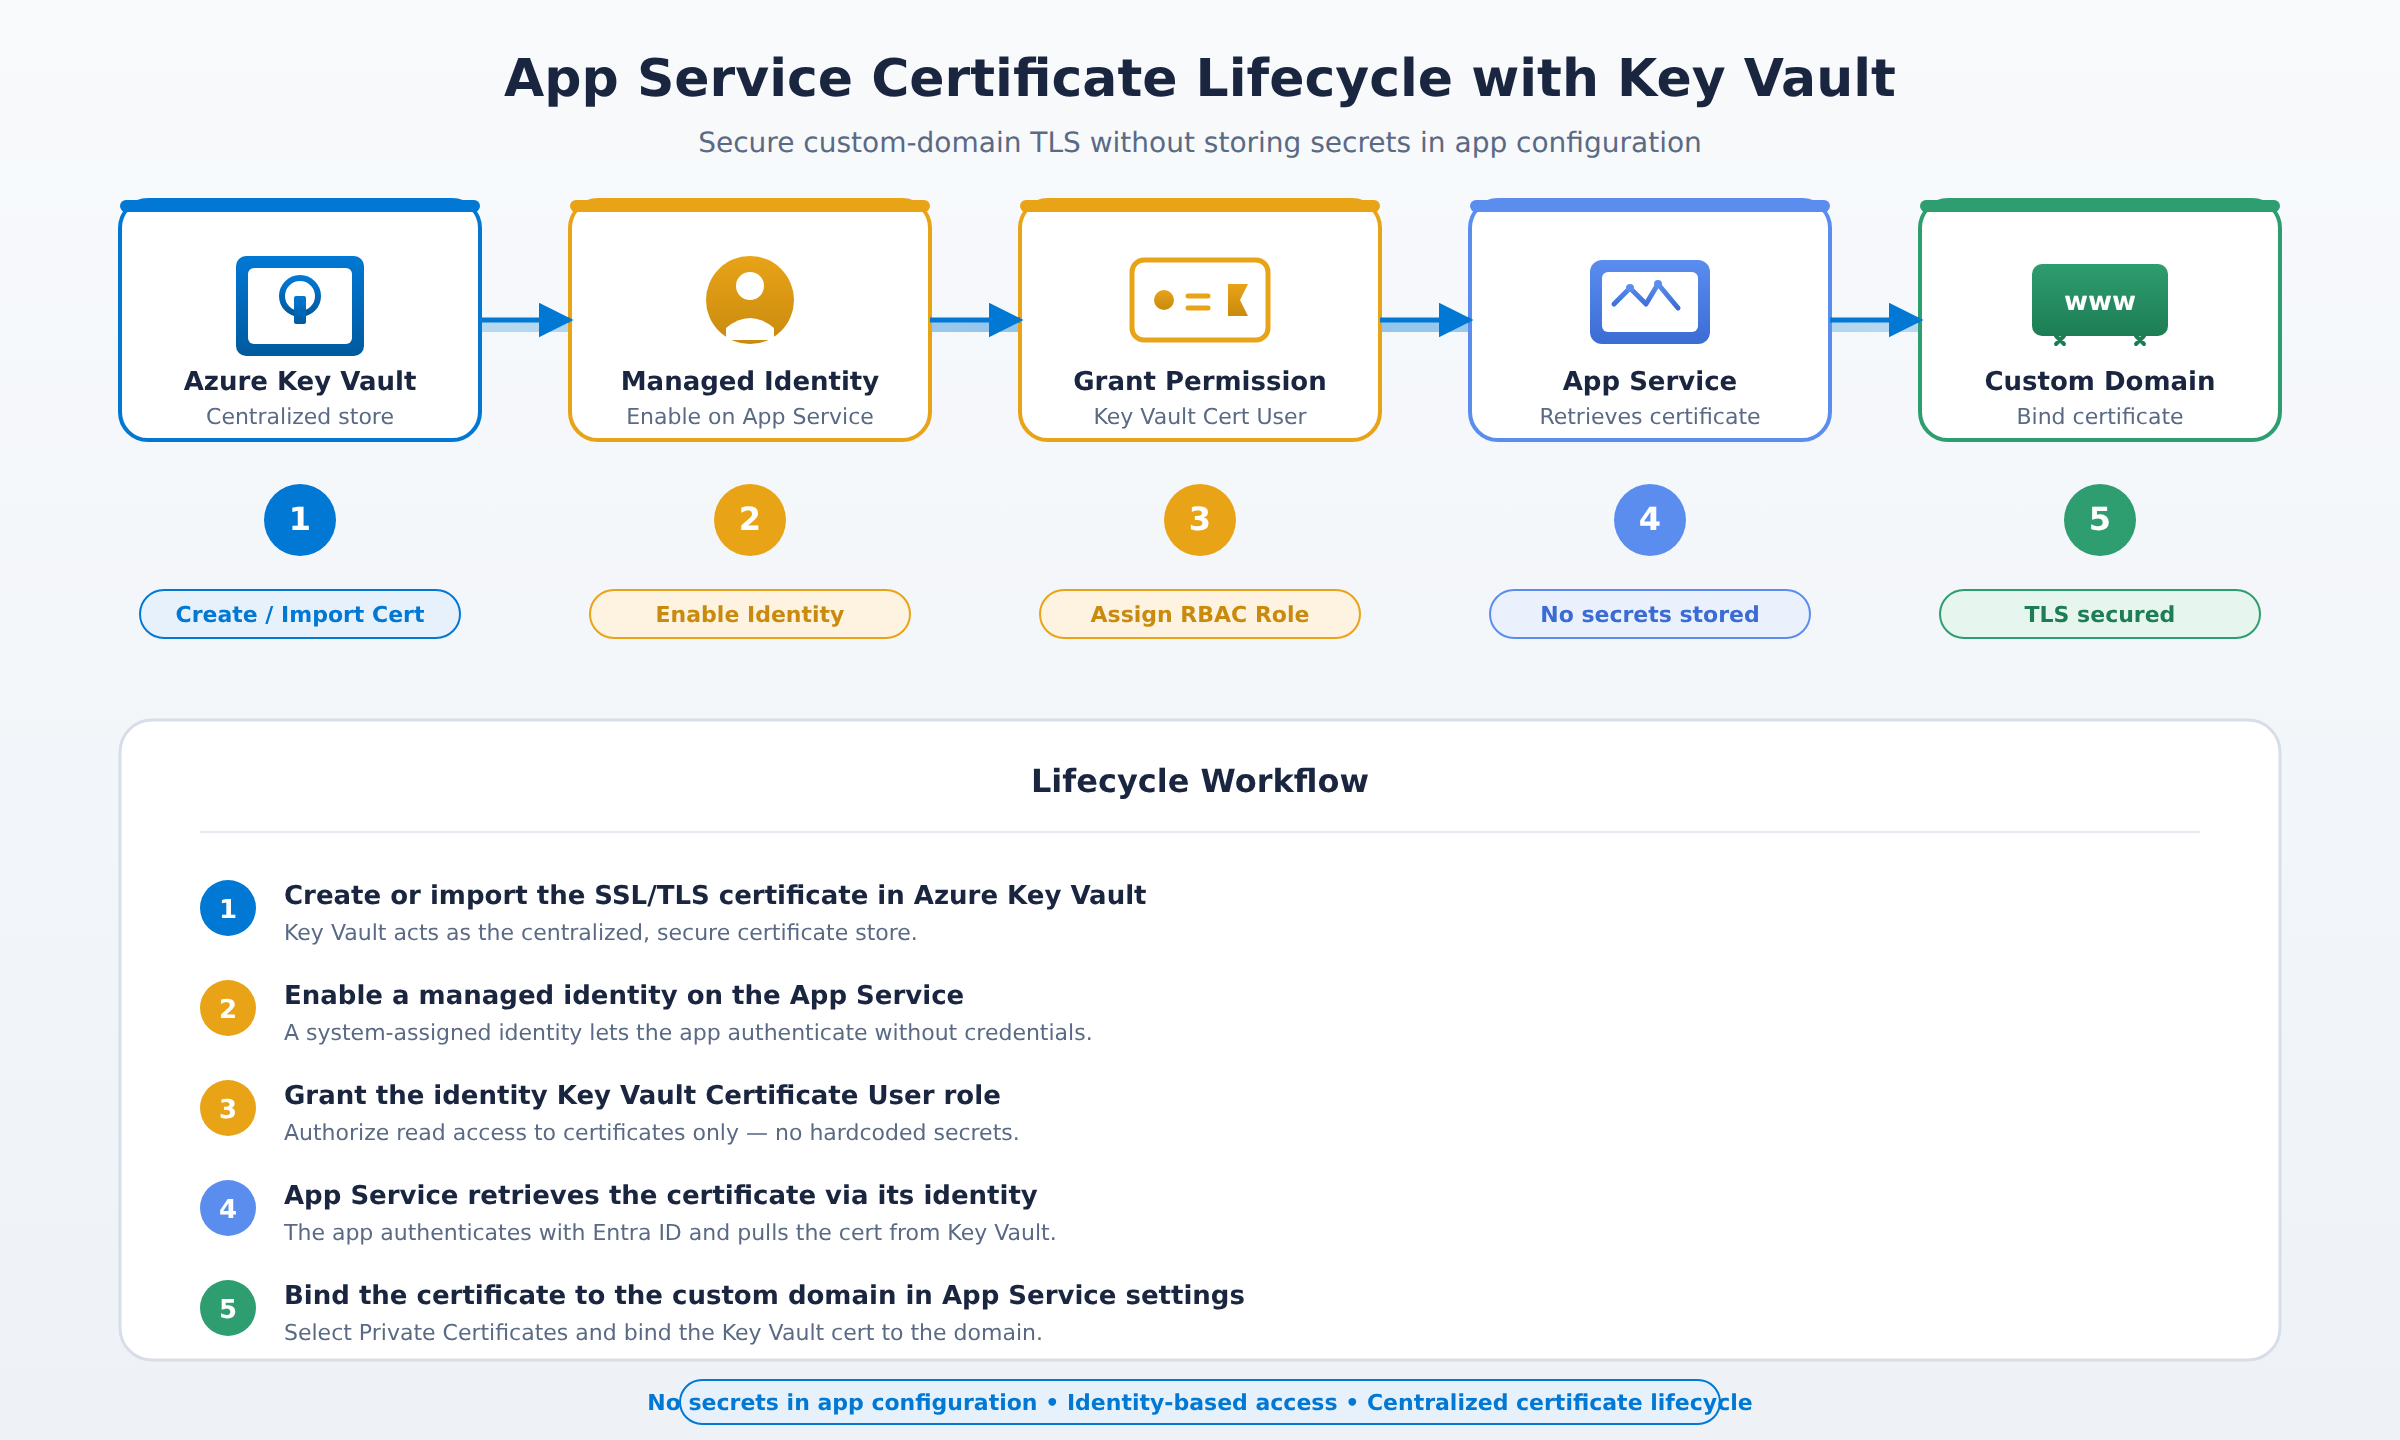
A five-step process flow showing how an SSL/TLS certificate is created in Azure Key Vault, a managed identity is enabled on the App Service, the identity is granted Key Vault Certificate User permission, the App Service retrieves the certificate, and the certificate is bound to a custom domain.
In the Domain
Certificate Lifecycle with Azure Key Vault
Using a custom domain name with an App Service requires a valid SSL/TLS certificate. The best practice is to manage this certificate's lifecycle within Azure Key Vault. You first store the certificate in the Key Vault. Then, you enable a managed identity on the App Service and grant it permission to read certificates from the vault. This setup allows the App Service to securely retrieve the certificate without storing any secrets in its configuration, and you can then bind that certificate to your custom domain directly from the App Service settings.
Domain 3 of 3
Plan and implement security for public access to Azure resources
Read the Domain summaryPractice this Domain
8 practice questions
Practice this DomainLast updated