Diagram
Managed Identity Authentication Flow
Sequence
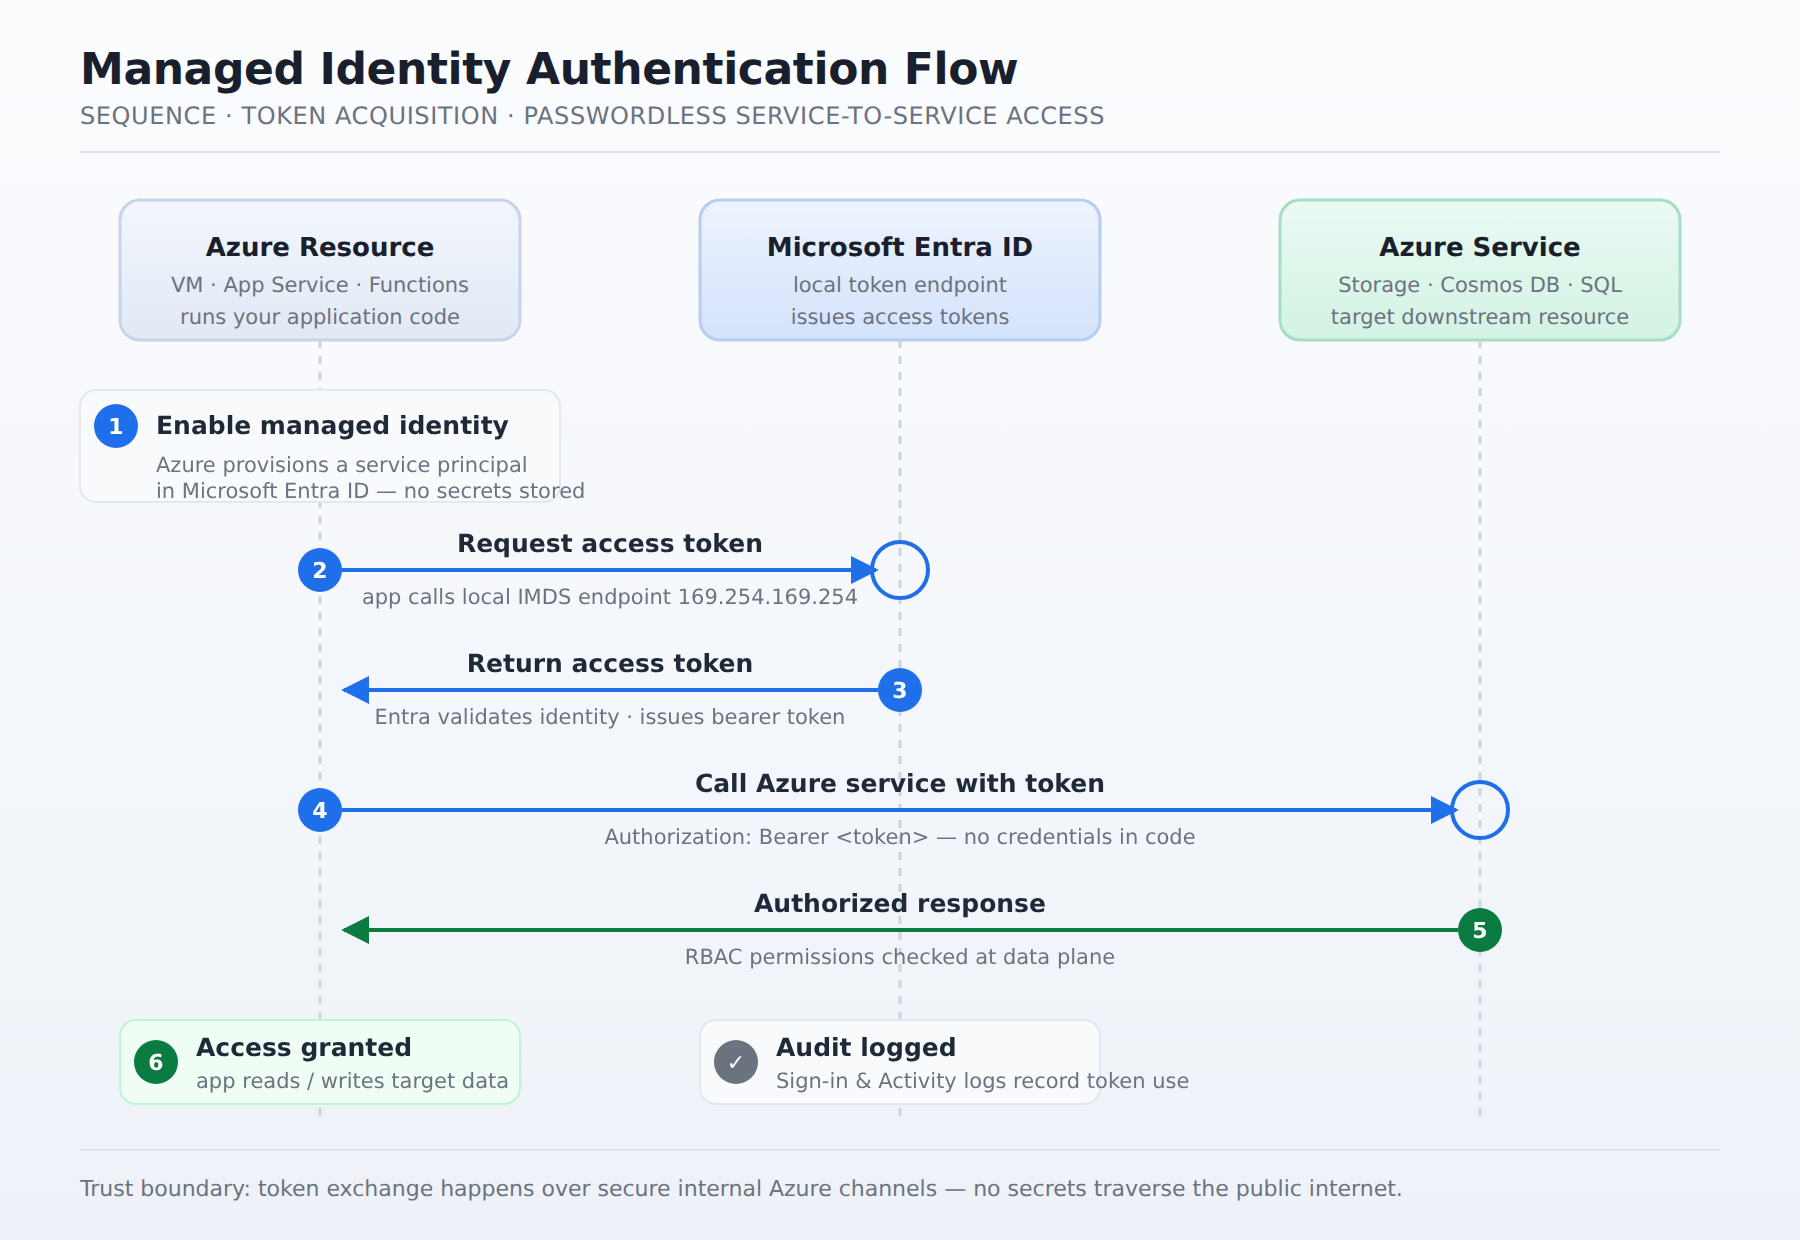
A sequence diagram showing an Azure resource requesting an access token from the local Microsoft Entra ID endpoint, then using that token to authenticate against a downstream Azure service like Storage or Cosmos DB.
In the Domain
Authentication and Authorization Flow
Managed identities simplify how applications authenticate by removing the risk of hard-coded credentials. When an application runs on an Azure resource, it requests an access token from the local Microsoft Entra ID token endpoint. The token endpoint returns a token that the resource uses to authenticate against other Azure services, such as Azure Storage or Azure Cosmos DB. This token-based exchange happens over secure internal channels, maintaining a strict trust boundary between the public internet and your private services. Authorization is then evaluated across two levels: the control plane, which uses Azure Role-Based Access Control (RBAC) via Azure Resource Manager, and the data plane, which uses service-specific authorization rules.
Domain 6 of 6
Manage managed identities
Read the Domain summaryPractice this Domain
2 practice questions
Practice this DomainLast updated