Diagram
AKS Azure AD Authentication Flow
Sequence
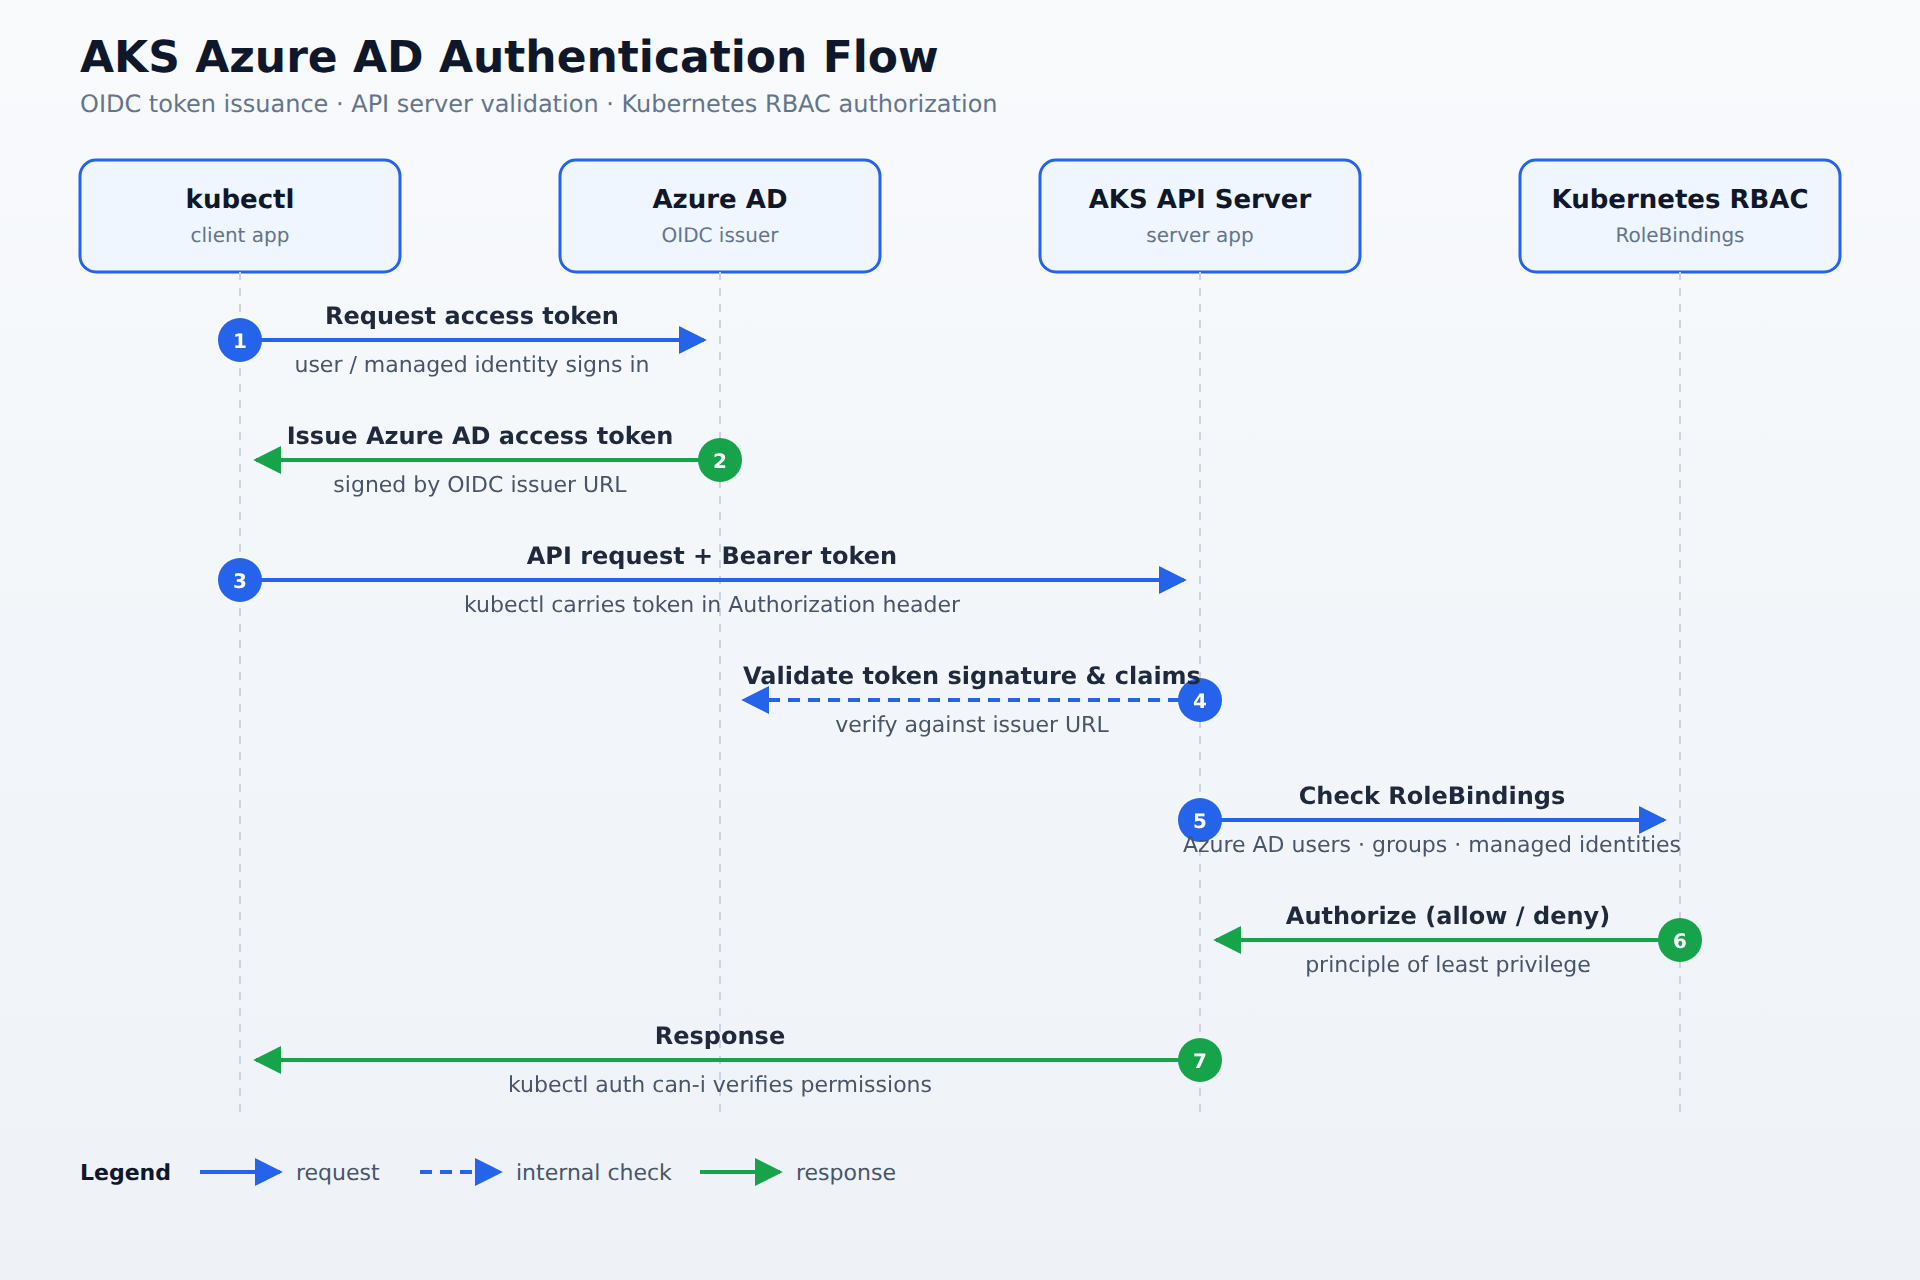
A sequence diagram showing kubectl requesting an Azure AD access token, Azure AD issuing it via OIDC, the AKS API server validating the token signature and claims, and Kubernetes RBAC authorizing the request through RoleBindings.
In the Domain
Enable Azure AD Integration and Kubernetes RBAC
Azure Kubernetes Service (AKS) can be secured by integrating Azure Active Directory (Azure AD) for authentication and using Kubernetes RBAC for authorization. OpenID Connect (OIDC) is the protocol that lets AKS trust Azure AD to authenticate users and applications. This integration enforces identity-based access control and supports the principle of least privilege. By combining these features, you ensure that only the right people and services can access your cluster.
To start, you must register two applications in Azure AD: a server application and a client application. The server application represents the AKS API server and needs the following:
- Client ID and Client Secret
- Redirect URI for token issuance
The client application represents administrative tools like
kubectland requires: - Client ID for user authentication
- Permission to request tokens Registering both apps ensures that AKS and users can securely exchange tokens.
Domain 4 of 9
Configure authentication for AKS
Read the Domain summaryPractice this Domain
2 practice questions
Practice this DomainLast updated