Diagram
Federated Identity Credential Authentication Flow
Sequence
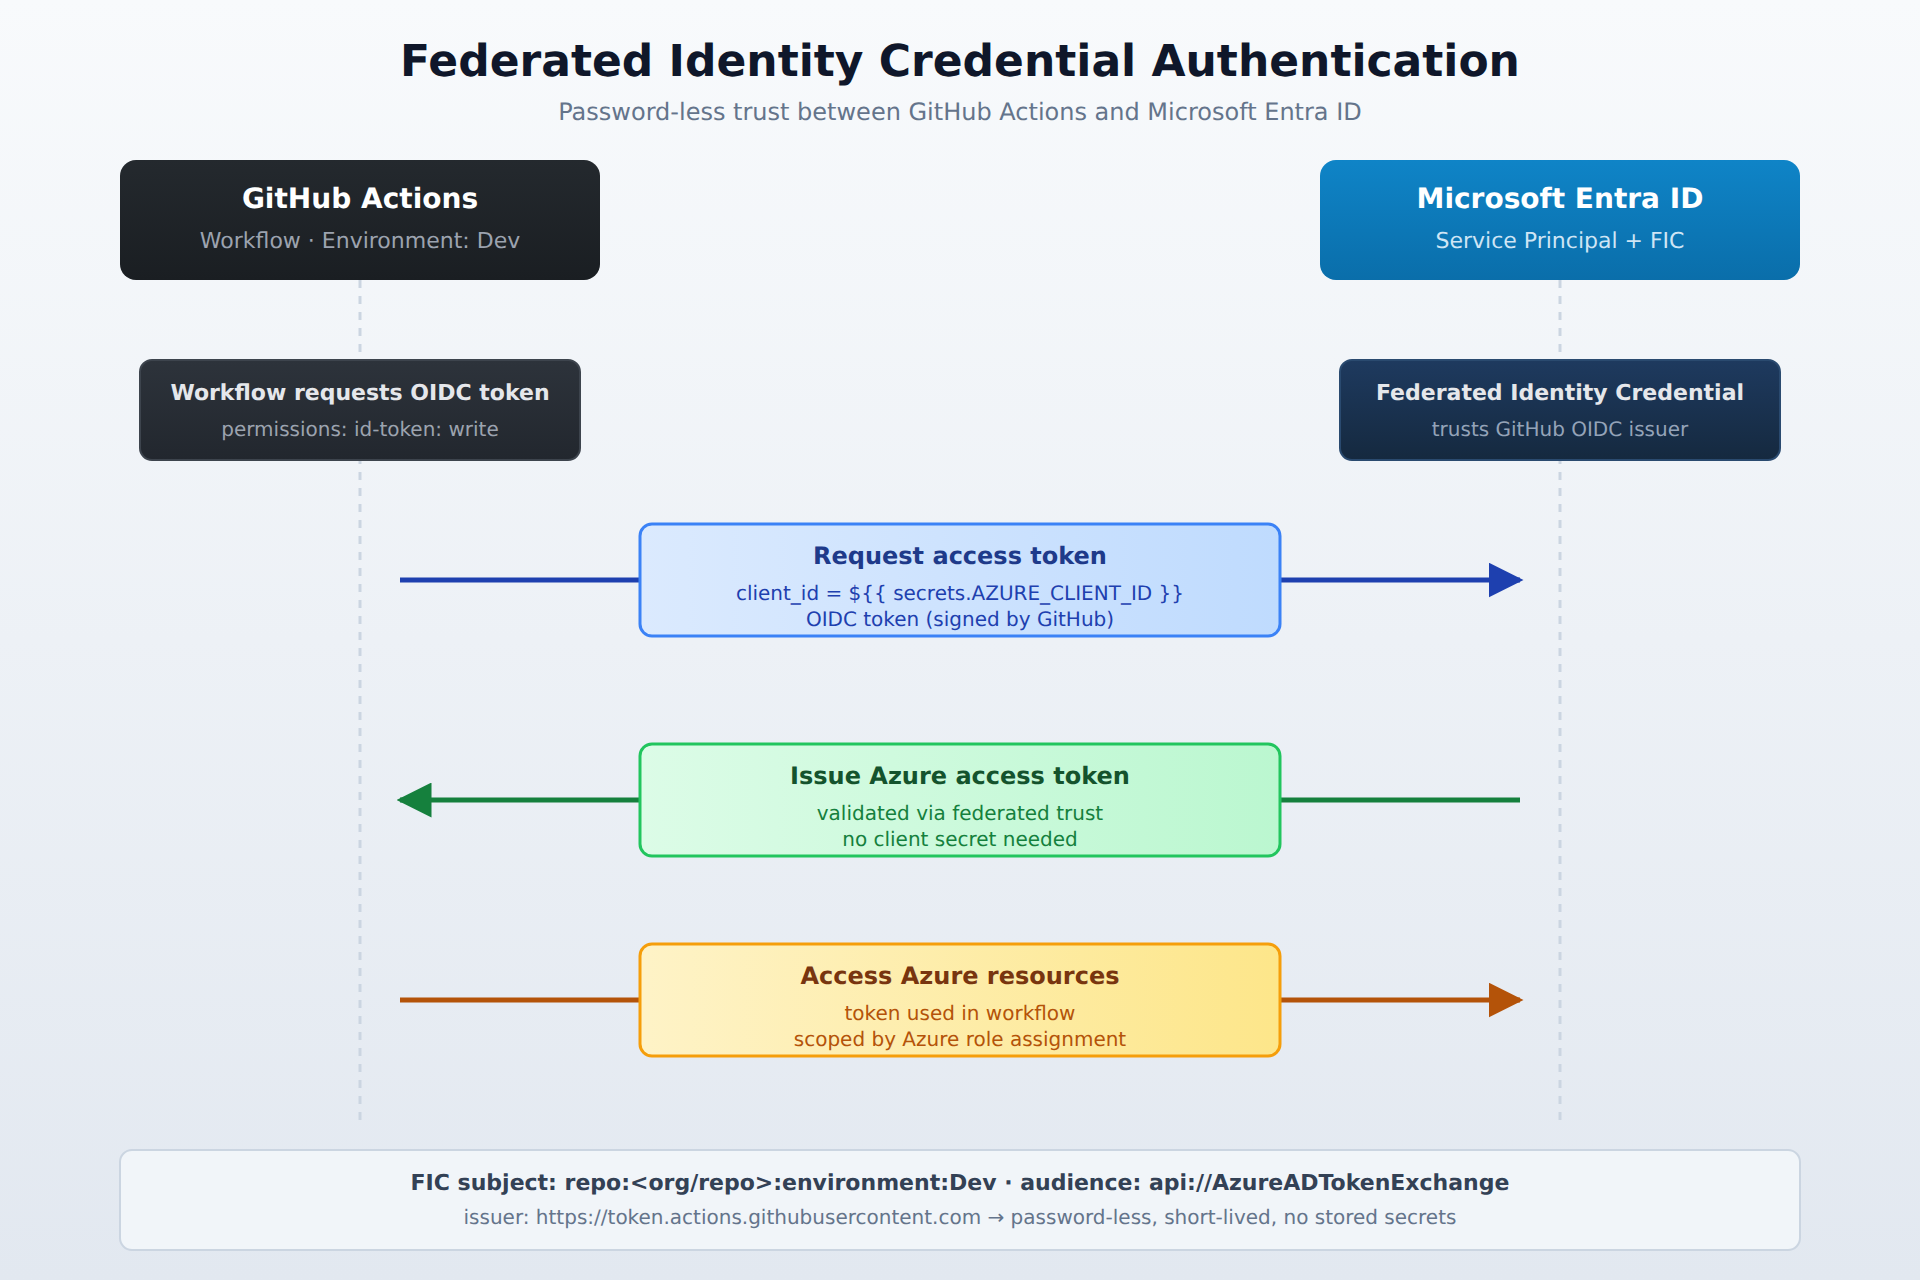
A sequence diagram showing how a GitHub Actions workflow obtains an Azure access token through a federated identity credential, exchanging a signed OIDC token for an Entra ID-issued token without using secrets.
In the Domain
Service Principals and Identity Credentials
For automated processes, like those run by GitHub Actions, you use a service identity instead of a user account. You create a service principal in Azure for each application environment (like Dev, Test, or Prod). This service principal acts as an identity for the automation. To let GitHub Actions securely use this identity, you configure a federated identity credential. This credential creates a trust relationship between your GitHub repository and the Azure service principal, allowing secure, password-less authentication for your workflows.
Domain 6 of 7
Recommend appropriate access levels, including stakeholder access inAzure DevOps and outside collaborator access in GitHub
Read the Domain summaryPractice this Domain
3 practice questions
Practice this DomainLast updated