Diagram
Azure RBAC Evaluation Logic Flow
Process Flow
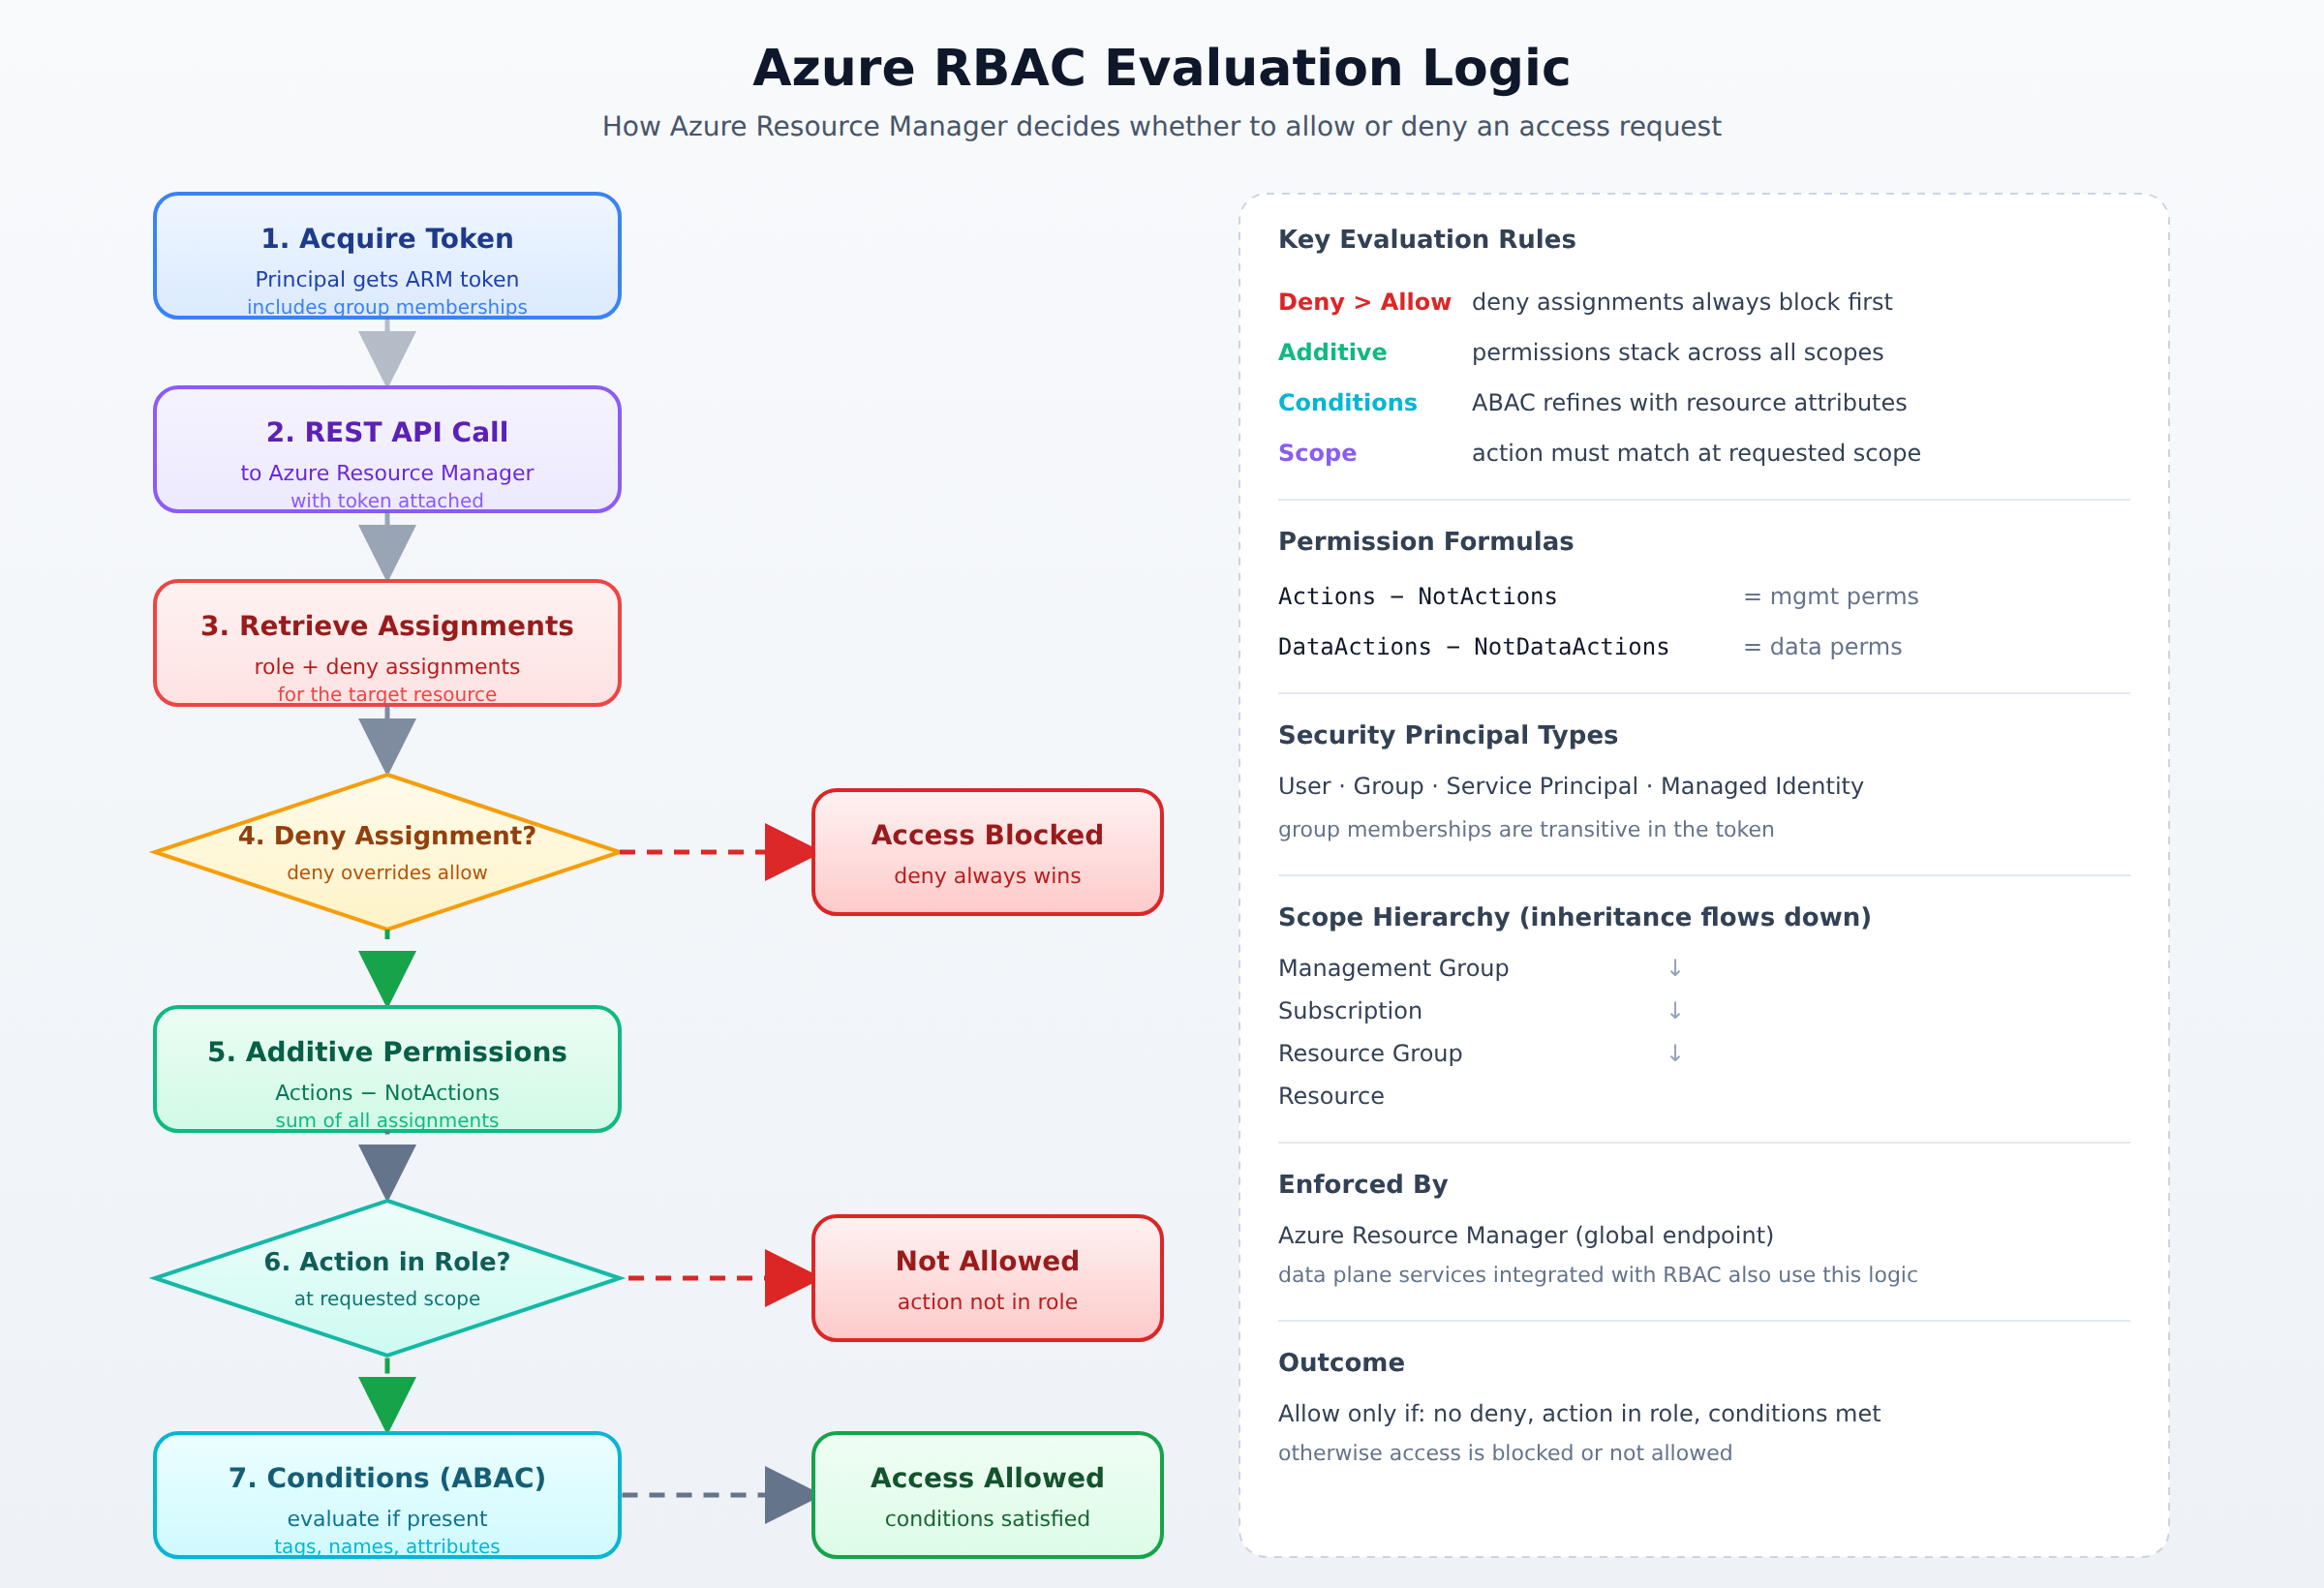
A process flow showing how Azure Resource Manager evaluates an access request in order: token acquisition, retrieval of role and deny assignments, deny check, additive permission calculation, action match check, and condition evaluation, ending in allow or deny.
In the Domain
Determine Effective Permissions
The system calculates effective permissions through an additive model that combines control plane management permissions and data plane storage permissions. When an access request occurs, the Azure Resource Manager retrieves all active role and deny assignments for the security principal. The authorization system evaluates deny assignments first; if any matching deny exists, access is immediately blocked. If no deny is found, the system subtracts NotActions from Actions to determine the final allowed administrative capabilities. In storage environments like Azure Data Lake Storage, the system evaluates traditional Access Control Lists (ACLs) alongside Azure RBAC to determine precise file and folder permissions.
Domain 2 of 3
Manage access to Azure resources
Read the Domain summaryPractice this Domain
102 practice questions
Practice this DomainLast updated