Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
JIT Access Groups and Default Service Account Guardrails
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise organization is establishing a standardized self-service provisioning and access management workflow for engineering teams in Google Cloud. The cloud architecture team must implement an access lifecycle model that meets the following security and governance requirements:
- Developers must be able to discover and request workload access through a self-service workflow with approval and justification.
- Access must automatically lapse after a defined time window to maintain Zero Standing Privileges (ZSP) and prevent privilege accumulation.
- Direct role assignments to individual user identities must be avoided across all environments.
- Automated project provisioning workflows must prevent services from receiving default, overly permissive roles such as
roles/editorupon creation.
Which combination of IAM and governance controls should you implement?
Explanations
Grant standing primitive Owner roles to developers via a central infrastructure pipeline, and schedule automated nightly scripts to delete and recreate project IAM policies.
Grant standing primitive Owner roles to developers via a central infrastructure pipeline, and schedule automated nightly scripts to delete and recreate project IAM policies.
What Standing Primitive Roles and Scripted Recreations Do
Granting standing primitive roles (roles/owner) provides full administrative and destructive control over Google Cloud project resources. Scheduling nightly script-based teardowns attempts to clean up stale permissions by resetting the IAM policy file.
Why It Doesn't Meet the Requirement
- Violates Zero Standing Privileges (ZSP): Providing standing owner access gives developers broad, persistent privileges throughout the workday, leaving systems vulnerable to unauthorized changes or data compromise.
- High operational risk: Nightly policy deletion scripts can cause widespread service outages, race conditions, and disruption to legitimate running workloads.
- Failure of least privilege: Primitive roles bypass fine-grained role segregation and grant unneeded permissions across all APIs.
- Ignores default service account policies: Fails to constrain default service account creation permissions during initial project setup.
Key Characteristics and Limitations
- Primitive roles do not align with modern enterprise governance or fine-grained service catalog models.
- Batch scripted policy resets do not provide an interactive request-and-approval self-service experience.
- Scripted resets introduce severe availability risks if policies fail to recreate accurately.
This Answer Would Be Correct If
You were provisioning disposable, isolated sandbox environments that are completely destroyed and purged at the end of every business day.
Assign IAM roles directly to individual developer accounts using IAM Conditions with scheduled expiration timestamps, while allowing default service account provisioning during project creation.
Assign IAM roles directly to individual developer accounts using IAM Conditions with scheduled expiration timestamps, while allowing default service account provisioning during project creation.
What Direct IAM Assignments with Conditions Do
Direct IAM assignments grant permissions directly to specific user email identities (user:developer@example.com). IAM Conditions allow administrators to define conditional expressions—such as request.time < timestamp('...')—to enforce time-limited access on individual policy bindings.
Why It Doesn't Meet the Requirement
- No direct IAM grants: The enterprise explicitly requires avoiding direct role grants to individual user accounts. Managing direct bindings creates bloated IAM policies that quickly become unmaintainable.
- No self-service governance: Native conditional IAM bindings on individual users require an administrator or automated pipeline with
resourcemanager.organizationAdminorroles/resourcemanager.projectIamAdminto continuously modify project policy bindings for every request. - Unchecked default service accounts: Allowing default service account creation without the organization policy constraint automatically grants broad roles like
roles/editor, violating least-privilege requirements during project provisioning.
Key Characteristics and Limitations
- Directly binding individual identities increases the risk of reaching policy size limits on resources.
- Does not provide a unified catalog for users to discover and request workload access.
- Manual or custom script-based policy updates do not provide standardized approval workflows.
This Answer Would Be Correct If
A single individual needed an emergency, one-off temporary bypass directly on a standalone resource where centralized access group management was unavailable.
Utilize Cloud Identity Groups for Business collaboration groups for IAM role assignments, and delegate group creation and membership management directly to all developers without approval guardrails.
Utilize Cloud Identity Groups for Business collaboration groups for IAM role assignments, and delegate group creation and membership management directly to all developers without approval guardrails.
What Groups for Business Collaboration Groups Are
Groups for Business (collaboration groups) are designed for unstructured communication, such as shared email lists and document collaboration. They generally allow open group creation by standard domain users and have loose membership controls.
Why It Doesn't Meet the Requirement
- Inappropriate for access control: Best practices state that collaboration groups should not be used for access control because they lack rigorous lifecycle management, eligibility restrictions, and approval gating.
- Privilege escalation risks: Permitting end users to create collaboration groups freely can lead to name-collision vulnerabilities, allowing unauthorized users to escalate their privileges into secured systems.
- Lack of automatic expiration: Collaboration groups do not support automated time-based membership revocation to enforce Zero Standing Privileges.
- Missing project provisioning guardrails: This approach does not address default service account permissions created during self-service onboarding.
Key Characteristics and Limitations
- Collaboration groups typically lack mandatory justification requirements and structured approver workflows.
- Memberships remain standing indefinitely unless manually removed.
- They do not protect against automatic default service account role grants.
This Answer Would Be Correct If
The objective was to create an open mailing list or shared discussion board for developer collaboration rather than governing sensitive cloud infrastructure access.
Manage access using workload-specific access groups integrated with a Just-In-Time (JIT) self-service tool with auto-expiring memberships, assign IAM roles to these groups, and enforce the constraints/iam.automaticIamGrantsForDefaultServiceAccounts organization policy constraint.
Manage access using workload-specific access groups integrated with a Just-In-Time (JIT) self-service tool with auto-expiring memberships, assign IAM roles to these groups, and enforce the constraints/iam.automaticIamGrantsForDefaultServiceAccounts organization policy constraint.
What Workload Access Groups and JIT Lifecycle Management Are
Workload-specific access groups and Just-In-Time (JIT) group management tools provide a scalable, self-service mechanism for governing permissions across Google Cloud resources. Instead of binding IAM roles directly to individual users, roles are assigned to dedicated access groups representing specific job functions. A self-service tool (such as JIT Groups) evaluates access requests, enforces justification and approval workflows, and automatically expires user memberships when the approved duration concludes.
JIT Group Membership Lifecycle
State / Lifecycle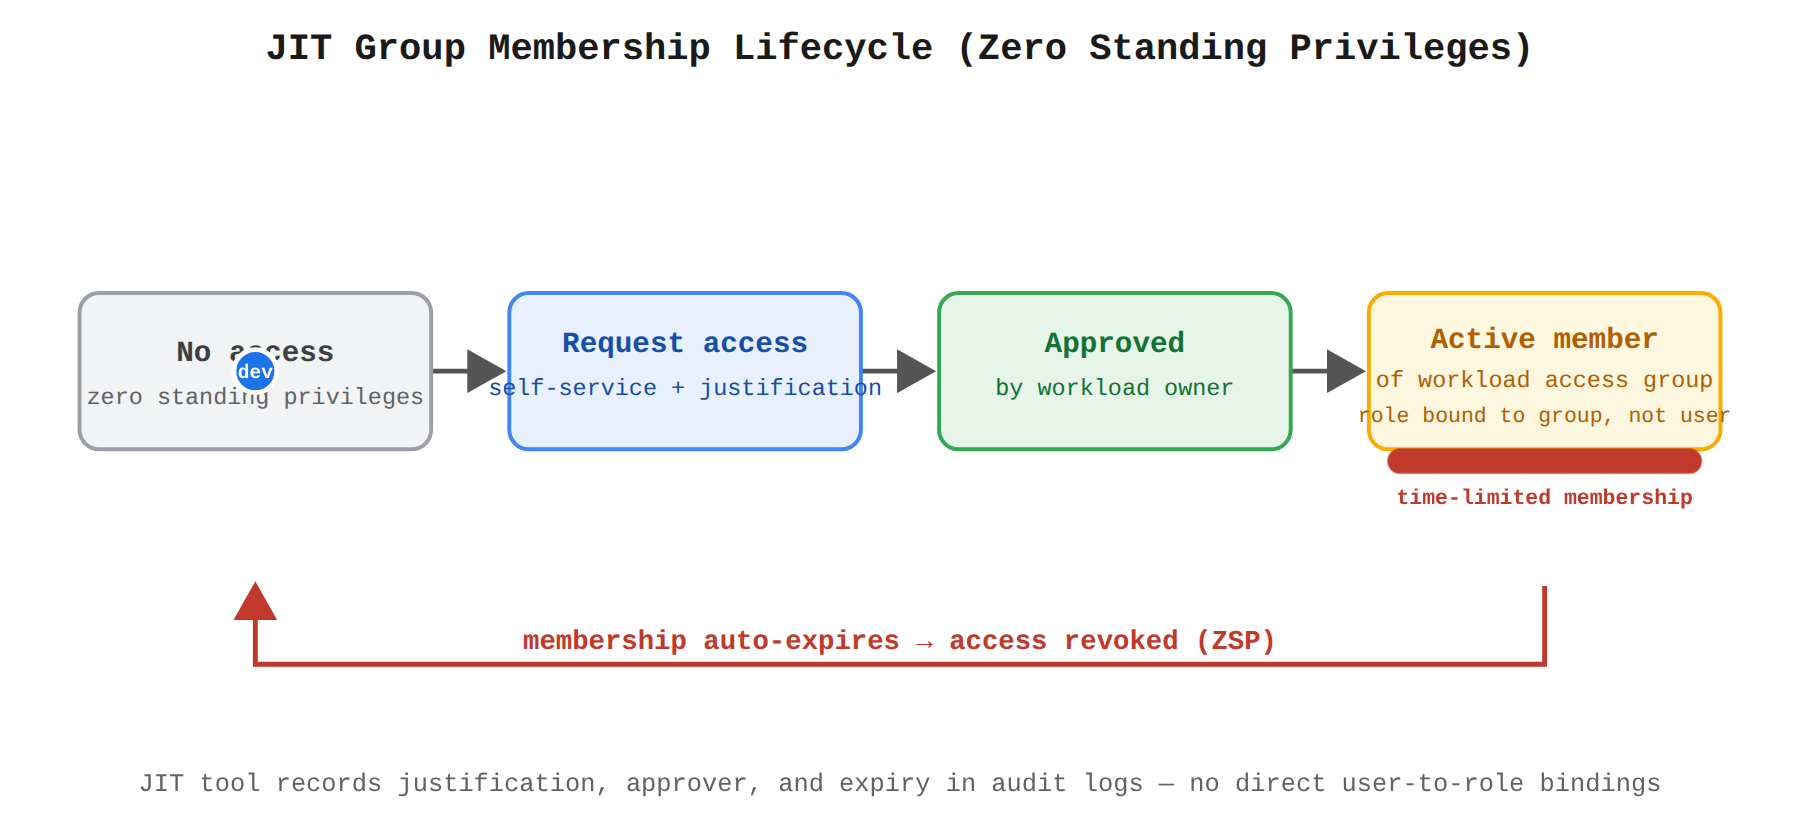
How It Meets the Requirements
- Self-service discovery and approvals: Dedicated access group management tools allow developers to discover workload groups, submit business justifications, and route requests to designated workload owners for approval.
- Zero Standing Privileges (ZSP): Auto-expiring group memberships add friction to long-term access retention, automatically revoking user membership and preventing gradual privilege creep over time.
- Group-based role assignment: Assigning IAM roles to access groups rather than individual user identities simplifies auditing and adheres to foundational IAM best practices.
- Preventing overly permissive defaults: Enforcing the
iam.automaticIamGrantsForDefaultServiceAccountsorganization policy constraint disables the automatic assignment ofroles/editorwhen new services or projects are provisioned.
Key Advantages
- Reduced administrative overhead: Workload owners manage group membership approvals without needing administrative IAM privileges on the project hierarchy.
- Comprehensive audit trail: JIT tooling captures access request justifications, approver IDs, and timestamps in central audit logs.
- Enforced least privilege: Prevents newly created service accounts from acquiring broad default project permissions.
- Automated decommissioning of access: Timed membership revocation ensures access terminates automatically without requiring manual deprovisioning scripts.
Why This Is Optimal
Combining JIT-managed access groups with organization policy constraints establishes a secure, repeatable self-service model. It enforces least-privilege access during runtime and guarantees baseline guardrails are inherited by every newly provisioned project.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Terraform GitOps with Cloud Build
Service catalog and provisioning
IntermediateProfessional Cloud Architect
Windows-Based SLI vs Request-Based SLI
Understanding the principles and recommendations of the operational excellence pillar of the Google Cloud Well-Architected Framework
IntermediateProfessional Cloud Architect
Vertex AI Pipelines Lineage Tracking
Using Vertex AI pipelines to automate and orchestrate the ML lifecycle
IntermediateProfessional Cloud Architect
Flex-start (Dynamic Workload Scheduler)
Using AI Hypercomputer (e.g., using AI Hypercomputer, Cloud Run functions, and Vertex AI for ML/AI workloads; integrating GPUs and TPUs in ML model training and serving; optimizing for different consumption models; and running large-scale AI model training
IntermediateProfessional Cloud Architect
Compliance Reports Manager
Industry certifications (e.g., SOC 2)
FundamentalGenerative AI Leader
Google Cloud Responsible AI Governance
Identifying the key factors that influence gen AI needs (e.g., business requirements, technical constraints)
Last updated