Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Encrypted Interconnect with Service Perimeter Protection
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
A financial enterprise is migrating multi-terabyte datasets containing sensitive customer records from an on-premises data center to Google Cloud. The compliance and security team has mandated the following requirements for data transit:
- Provide a dedicated, high-bandwidth physical connection between the on-premises facility and Google Cloud
- Enforce IPsec encryption in transit across the private connection for all transmitted packets
- Protect against unauthorized data exfiltration to external Google Cloud services and storage buckets
- Achieve a 99.99% Service Level Agreement (SLA) for the hybrid connectivity architecture
Which solution should the enterprise implement?
Explanations
Deploy standard HA VPN gateways over the public internet across two regions, and configure VPC firewall rules to block egress to non-approved IP addresses.
Deploy standard HA VPN gateways over the public internet across two regions, and configure VPC firewall rules to block egress to non-approved IP addresses.
What standard HA VPN over the internet does
HA VPN over the internet sets up site-to-site IPsec tunnels connecting an on-premises VPN gateway to a Google Cloud HA VPN gateway over public IP transport and standard ISP infrastructure.
Why it doesn't meet the requirement
- Dedicated physical connection: Internet-based Cloud VPN traverses the public internet, which does not provide a dedicated private physical link or predictable, unshared bandwidth.
- Perimeter exfiltration prevention: VPC firewall rules filter Layer 3/4 packet headers at the virtual machine interface level. They cannot inspect application-level API requests or prevent authorized users from exfiltrating data to external Cloud Storage buckets.
Key characteristics and limitations
- Bandwidth limitations: Individual VPN tunnels have throughput caps (typically up to 3 Gbps per tunnel), requiring complex tunnel scaling for large migrations.
- Variable latency: Best-effort internet routing introduces jitter and potential packet loss.
- No API-layer boundary: Firewalls cannot enforce security perimeters around multi-tenant Google Cloud API endpoints.
This answer would be correct if
The enterprise required a cost-effective, encrypted connection over commodity internet without needing a dedicated physical circuit or managed API-level exfiltration controls.
Additional context
VPC firewalls govern VM-to-VM and VM-to-IP traffic, whereas VPC Service Controls is required to restrict access to Google Cloud managed service APIs.
Establish VPC Network Peering directly between the on-premises router and the VPC, and assign strict Identity and Access Management (IAM) storage roles.
Establish VPC Network Peering directly between the on-premises router and the VPC, and assign strict Identity and Access Management (IAM) storage roles.
What VPC Network Peering and IAM do
VPC Network Peering connects two Google Cloud Virtual Private Cloud (VPC) networks using internal IP routing. Identity and Access Management (IAM) manages authentication and role-based access permissions for principals across cloud resources.
Why it doesn't meet the requirement
- Technical impossibility: VPC Network Peering can only be configured between two Google Cloud VPC networks; it cannot peer directly with on-premises routers or external data centers.
- Data exfiltration vulnerability: IAM only verifies whether a user has permissions on a given resource. If an authorized user has permissions in an external personal project, IAM alone cannot prevent that user from reading data and copying it out to an unauthorized external bucket.
Key characteristics and limitations
- Non-transitive routing: VPC Network Peering does not extend across non-peered hops or on-premises networks without proxy mechanisms.
- No network perimeter enforcement: IAM lacks context-aware network boundaries that tie access to specific VPC networks or client perimeters.
This answer would be correct if
The scenario involved private internal communication strictly between two separate Google Cloud VPC networks belonging to different projects.
Additional context
Hybrid connectivity to on-premises routers requires Cloud Interconnect or Cloud VPN running BGP via Cloud Router, not VPC Network Peering.
Deploy Dedicated Interconnect across two regions with encrypted VLAN attachments and HA VPN, and configure a VPC Service Controls perimeter around the target cloud resources.
Deploy Dedicated Interconnect across two regions with encrypted VLAN attachments and HA VPN, and configure a VPC Service Controls perimeter around the target cloud resources.
What Dedicated Interconnect with HA VPN and VPC Service Controls is
Dedicated Interconnect with HA VPN (HA VPN over Cloud Interconnect) combines the high-throughput, low-latency private physical transport of Google Cloud Dedicated Interconnect with network-layer IPsec encryption. VPC Service Controls establishes a secure isolation boundary (service perimeter) around Google Cloud managed services such as Cloud Storage and BigQuery to mitigate data exfiltration risks.
HA VPN over Interconnect with VPC-SC
System Architecture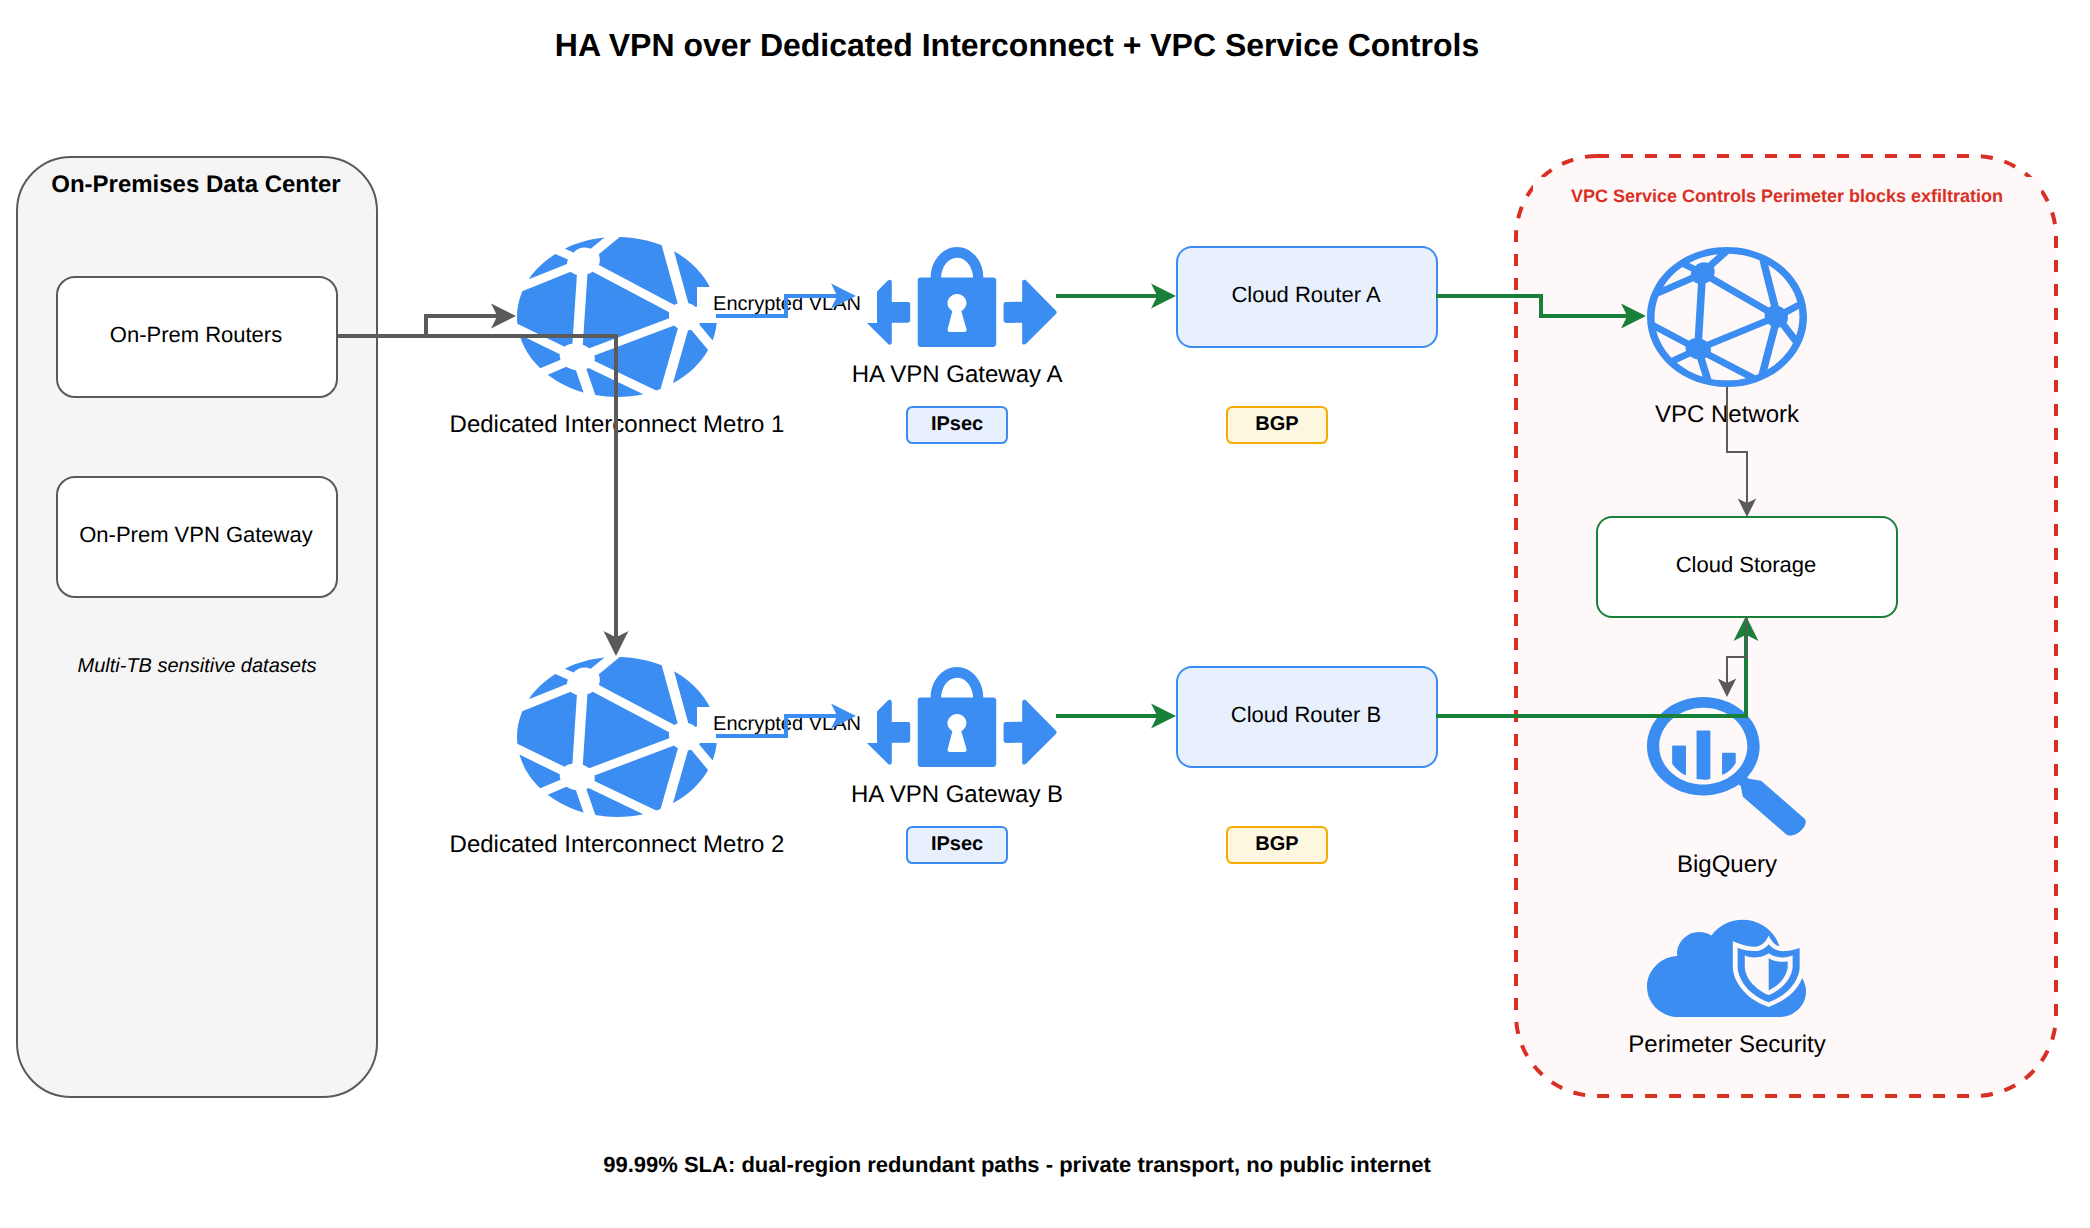
How it meets the requirements
- Dedicated high-bandwidth connection: Dedicated Interconnect provides direct physical 10 Gbps or 100 Gbps circuits between the on-premises network and Google's colocation facilities.
- End-to-end IPsec encryption: Encrypted VLAN attachments paired with HA VPN gateways and tunnels ensure all data passing across the private Interconnect circuits is encapsulated with standards-based IPsec encryption.
- Data exfiltration prevention: Placing Google Cloud resources within a VPC Service Controls service perimeter prevents data from being copied or moved to unauthorized buckets, services, or identities outside the perimeter.
- 99.99% SLA: Deploying four Dedicated Interconnect connections with HA VPN across two separate regions in redundant edge availability domains meets Google's architecture requirements for a 99.99% uptime guarantee.
Key advantages and capabilities
- Private and Encrypted Transit: Delivers line-rate encryption over private links without routing traffic across the public internet.
- Perimeter-level Data Security: Context-aware access policies and perimeter boundaries prevent malicious or accidental egress of sensitive records.
- Multi-Region Redundancy: Dual-region dual-zone topology guarantees enterprise-grade fault tolerance.
- Dynamic Route Management: Leverages BGP via Cloud Router for automated failover and topology updates.
Why this is optimal
This approach directly satisfies all bandwidth, high-availability, encryption-in-transit, and perimeter-level data exfiltration requirements simultaneously, whereas standard interconnect or internet VPN solutions fail to meet one or more of these criteria.
Provision Partner Interconnect Layer 2 connections with standard unencrypted VLAN attachments, and deploy Cloud Armor security policies on the target VPC.
Provision Partner Interconnect Layer 2 connections with standard unencrypted VLAN attachments, and deploy Cloud Armor security policies on the target VPC.
What Partner Interconnect and Cloud Armor do
Partner Interconnect connects an on-premises network to Google Cloud through a supported service provider, providing private RFC 1918 connectivity. Cloud Armor is a Web Application Firewall (WAF) and DDoS protection service operating at the edge of external and internal HTTP(S) load balancers.
Why it doesn't meet the requirement
- Encryption in transit: Standard VLAN attachments on Cloud Interconnect carry raw, unencrypted Ethernet/IP frames across the circuit unless overlaid with HA VPN or MACsec.
- Data exfiltration protection: Cloud Armor protects web applications from Layer 7 attacks (such as SQLi and XSS) and DDoS floods; it does not restrict data movement between cloud storage services and external entities.
Key characteristics and limitations
- Lack of default network-layer encryption: Private interconnect traffic is isolated from the internet but is not encrypted by default.
- WAF vs. Data Perimeter: Cloud Armor filters incoming HTTP(S) request payloads rather than governing cloud API data boundaries.
This answer would be correct if
The primary goal was connecting through a third-party carrier without in-transit IPsec requirements, while defending public web frontends from DDoS and injection attacks.
Additional context
To achieve IPsec encryption over Interconnect, encrypted VLAN attachments must be created specifically to host HA VPN tunnels.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Google Cloud Transfer Appliance
Movement of data
IntermediateProfessional Cloud Architect
Dataflow KafkaIO Exactly-Once Semantics
Movement of data
IntermediateProfessional Cloud Architect
Workload Identity Federation
Secure remote access (e.g., Identity-Aware Proxy, service account impersonation, Chrome Enterprise Premium, and Workload Identity Federation)
IntermediateProfessional Cloud Architect
Global External Application Load Balancer Premium Tier
Scalability to meet growth requirements
IntermediateProfessional Cloud Architect
Compliance Reports Manager
Industry certifications (e.g., SOC 2)
AdvancedProfessional Cloud Security Engineer
Confidential Computing and Shielded VM Hardening
Determining technical needs relative to compute, data, network, and storage.
Last updated