Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Centralized Hybrid Inspection with Transit NVA Hub
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise is architecting a mission-critical hybrid network topology connecting an on-premises data center to Google Cloud. The architecture must satisfy the following technical and operational requirements:
- Connect on-premises networks to multiple isolated workload VPCs (production and development) through a scalable hub-and-spoke model
- Enforce centralized Layer 7 deep packet inspection and filtering on all traffic flowing between on-premises and the cloud workload VPCs
- Distribute traffic across redundant Network Virtual Appliance (NVA) firewall instances with symmetric session handling
- Prevent route table overflow and route flapping by controlling prefix announcements over BGP sessions to on-premises routers
Which hybrid networking design should you implement?
Explanations
Connect each spoke VPC directly to on-premises routers using individual single-tunnel Cloud VPN gateways, assign a public IP to each workload VM, and advertise specific /32 host routes via BGP.
Connect each spoke VPC directly to on-premises routers using individual single-tunnel Cloud VPN gateways, assign a public IP to each workload VM, and advertise specific /32 host routes via BGP.
What This Option Is
This design establishes individual, isolated Cloud VPN tunnels from on-premises routers directly to each separate workload VPC. Workload instances receive direct external IP addresses, and routing tables advertise specific individual host routes (/32) over dynamic BGP sessions.
Why It Doesn't Meet the Requirement
- No Centralized Layer 7 Inspection: Bypasses any centralized transit hub, making it impossible to enforce uniform Layer 7 inspection across all environments without deploying duplicate firewall appliances in every spoke.
- Route Scaling Failures: Advertising individual /32 host routes quickly exceeds routing table quotas and BGP prefix limits on both Cloud Routers and on-premises hardware.
- Security and Availability Risks: Assigning public IPs directly to internal workload VMs expands the attack surface, while single-tunnel VPNs lack enterprise-grade high availability SLAs.
Key Limitations
- Lacks a centralized hub for traffic filtering and policy enforcement.
- Generates excessive BGP route updates that can cause routing instability.
- Significantly increases operational overhead by multiplying point-to-point connections.
This Answer Would Be Correct If
The workload consisted of isolated, independent cloud test environments that did not require centralized inspection or high-throughput private hybrid interconnects.
Deploy a transit hub VPC with an internal passthrough Network Load Balancer fronting a managed instance group of NVAs as the next hop for peered spoke VPCs, terminate redundant Cloud Interconnect VLAN attachments in the transit network, and configure Cloud Routers with summary custom route advertisements.
Deploy a transit hub VPC with an internal passthrough Network Load Balancer fronting a managed instance group of NVAs as the next hop for peered spoke VPCs, terminate redundant Cloud Interconnect VLAN attachments in the transit network, and configure Cloud Routers with summary custom route advertisements.
What the Solution Is
This architecture establishes a centralized transit hub-and-spoke topology that uses Cloud Interconnect for high-throughput, redundant hybrid connectivity. It leverages an internal passthrough Network Load Balancer as a next hop to distribute traffic evenly across a managed instance group (MIG) of firewall Network Virtual Appliances (NVAs), while using Cloud Router summary custom advertisements to manage BGP prefix scale.
How It Meets the Requirements
- Hub-and-Spoke Connectivity: The transit hub VPC connects to on-premises via Cloud Interconnect using multiple VLAN attachments and peers with isolated spoke VPCs (such as production and development), creating a clean separation of network environments.
- Centralized Layer 7 Inspection: Traffic entering from on-premises or moving across spoke VPCs is routed through virtual appliance firewalls deployed in the central hub VPC.
- High Availability and Symmetric Handling: The internal passthrough Network Load Balancer distributes traffic across healthy NVA instances in the MIG. Google Cloud's symmetric hashing ensures bidirectional traffic flows through the same NVA without requiring Source NAT (SNAT).
- BGP Optimization and Prefix Scale: Configuring summary custom advertisements on the Cloud Router condenses cloud network ranges into aggregated prefixes, preventing routing table limits and instability on on-premises BGP neighbors.
Transit Hub NVA Inspection Architecture
System Architecture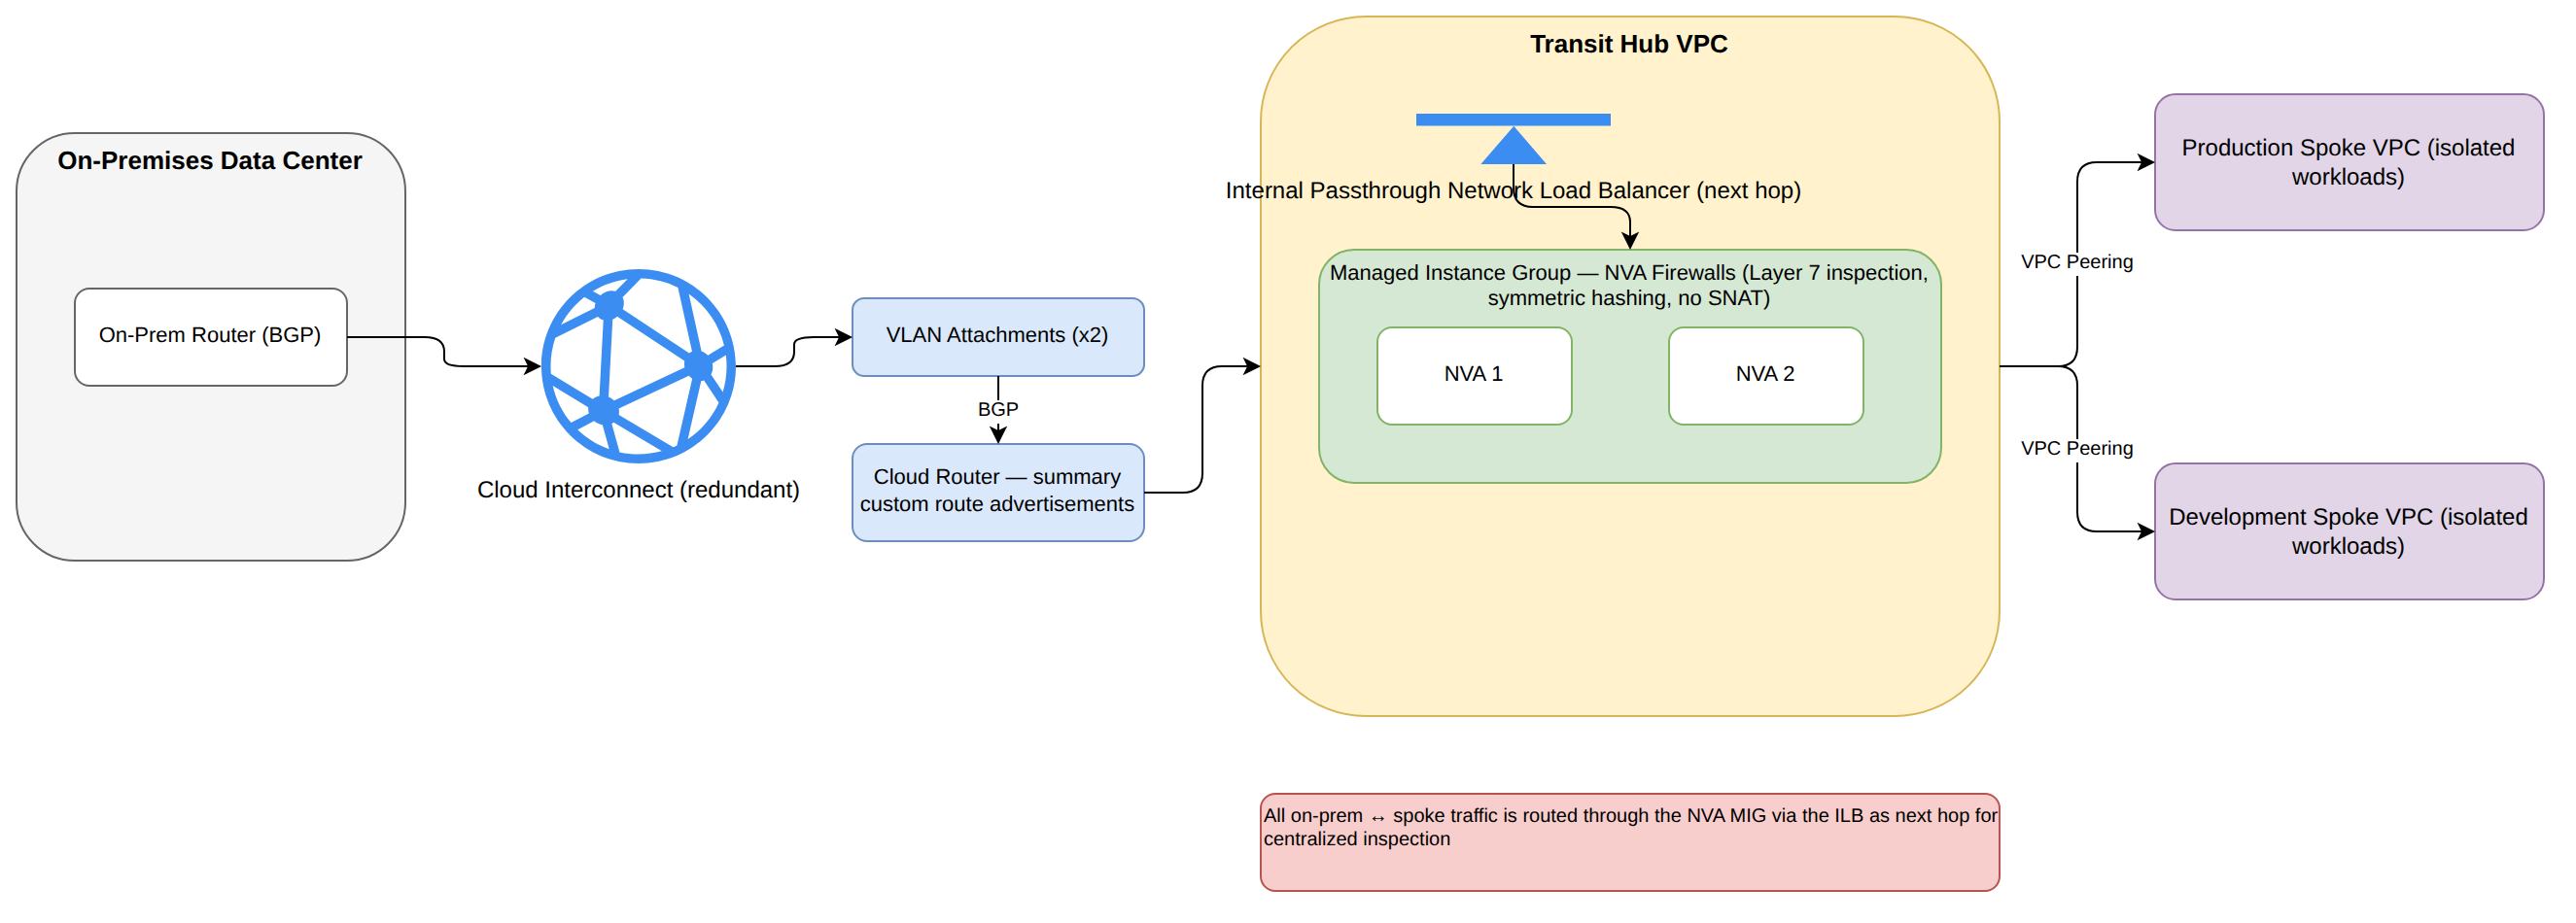
Key Advantages
- Enterprise-Grade Availability: Redundant VLAN attachments and autoscaling NVA backends eliminate single points of failure.
- Centralized Security Governance: Security teams manage deep packet inspection rules in one place rather than configuring per-spoke appliances.
- Predictable Routing: Custom prefix summarization prevents route churn and adheres to hardware route limits on on-premises routers.
- No Complex SNAT Overhead: Preserves original client IP addresses across hybrid flows via symmetric load balancing.
Why This Is Optimal
Combining a transit hub VPC with an internal load balancer as the next hop provides the resilience, scalability, and deep inspection required by enterprise landing zones without compromising routing stability.
Deploy an external Application Load Balancer in the transit VPC to inspect internal RFC 1918 traffic, and configure Cloud Routers to redistribute raw default static routes (0.0.0.0/0) directly into on-premises BGP tables without filtering.
Deploy an external Application Load Balancer in the transit VPC to inspect internal RFC 1918 traffic, and configure Cloud Routers to redistribute raw default static routes (0.0.0.0/0) directly into on-premises BGP tables without filtering.
What This Option Is
This setup attempts to place a public-facing external Application Load Balancer in front of internal hybrid traffic flows and indiscriminately redistributes default 0.0.0.0/0 static routes via BGP Cloud Routers to on-premises edge routers.
Why It Doesn't Meet the Requirement
- Mismatched Load Balancer Type: An external Application Load Balancer terminates public internet HTTP(S) traffic at Google's edge. It cannot serve as a next hop for internal private Layer 3/Layer 4 traffic between VPCs and on-premises environments.
- Routing Loops and Suboptimal Pathing: Redistributing unsummarized or unfiltered
0.0.0.0/0routes into on-premises BGP tables can override enterprise internet gateways, causing unintended routing loops and blackholing data center internet traffic. - Failure to Provide Transit Inspection: External load balancers cannot act as transparent transit next hops for non-HTTP enterprise protocols.
Key Limitations
- External Application Load Balancers are designed for internet ingress, not private hybrid transit.
- Uncontrolled BGP redistribution of default routes violates enterprise routing standards.
- Lacks next-hop integration with internal VPC routing tables.
This Answer Would Be Correct If
The primary goal was load balancing global, inbound public internet traffic to web application frontends with edge SSL termination.
Deploy a single Compute Engine VM configured as an NVA router in the hub VPC, use static host routes pointing to that VM's IP address, and disable Cloud Router BGP dynamic routing.
Deploy a single Compute Engine VM configured as an NVA router in the hub VPC, use static host routes pointing to that VM's IP address, and disable Cloud Router BGP dynamic routing.
What This Option Is
This architecture places a standalone, unmanaged Compute Engine VM inside a hub VPC to act as a monolithic router and firewall. All spoke VPCs and on-premises routers rely on manually maintained static routes pointing to this single VM instance.
Why It Doesn't Meet the Requirement
- Single Point of Failure: A single NVA VM lacks high availability and cannot scale dynamically to handle fluctuating hybrid traffic volumes, violating enterprise uptime requirements.
- No Automatic Failover: Using static routes pointing to a single VM IP address means that if the instance fails, all cross-environment traffic is dropped until manual intervention occurs.
- Operational Inefficiency: Disabling dynamic BGP routing eliminates automated prefix learning and failover capabilities between Google Cloud and the on-premises data center.
Key Limitations
- Static routing requires continuous administrative maintenance as networks grow.
- Lack of health checking and load balancing prevents zero-downtime maintenance of firewall appliances.
- Throughput is bottlenecked by the network egress limits of a single virtual machine.
This Answer Would Be Correct If
The deployment were a small, non-critical proof-of-concept where traffic volume is minimal and high availability is not a requirement.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Cloud HA VPN MP-BGP Dual-Stack
Extending to on-premises environments (hybrid networking)
IntermediateProfessional Cloud Architect
Partner Interconnect vs Dedicated Interconnect
Extending to on-premises environments (hybrid networking)
IntermediateProfessional Cloud Architect
Cloud Run Serverless Containers
Design decision trade-offs
IntermediateProfessional Cloud Architect
VPC Service Controls Ingress and Egress Rules
Extending to a multicloud environment that may include Google Cloud-to-Google Cloud communication
IntermediateProfessional Cloud Architect
gcloud Configurations Activate and Format Value
Google Cloud SDKs (e.g., gcloud, gsutil, and bq)
FundamentalAssociate Data Practitioner
Transfer Appliance vs Storage Transfer Service
Choose the appropriate data transfer tool (e.g., Storage Transfer Service, Transfer Appliance)
Last updated