Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Global Load Balancing with Centralized Firewall Enforcement
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise is designing a globally distributed multi-tier web application deployed across multiple Google Cloud regions. The compute backends reside in multiple service projects connected to a centralized Shared VPC hosted in a dedicated Production folder.
The architecture must meet the following requirements:
- Route global user traffic with minimal latency and automatically overflow excess traffic to the next closest region when a regional backend reaches capacity.
- Centrally enforce baseline firewall rules ensuring that Google Front End (GFE) proxies and health checking systems can communicate with backend instances across all service projects.
- Prevent individual service project teams from overriding or disrupting the core load balancer communication paths.
Which architecture and security implementation should you recommend?
Explanations
Deploy an Internal Application Load Balancer with cross-region routing, and configure a hierarchical firewall policy attached to each service project allowing ingress from 169.254.169.254.
Deploy an Internal Application Load Balancer with cross-region routing, and configure a hierarchical firewall policy attached to each service project allowing ingress from 169.254.169.254.
What this option is and does
This configuration proposes using a cross-region Internal Application Load Balancer and applying hierarchical policies that target the link-local metadata server address (169.254.169.254).
Why it doesn't meet the requirements
- Incompatible with external user traffic: An Internal Application Load Balancer is intended for internal, private RFC 1918 traffic within VPC networks and cannot directly serve public internet clients.
- Incorrect source IP ranges: The metadata IP
169.254.169.254provides internal instance metadata and is always allowed by default; it is not the source range used by GFE proxies or standard health check systems. - Misplaced hierarchical associations: Associating policies with service project folders does not affect VMs connected to the host project's Shared VPC network.
Key characteristics and limitations
- Internal Application Load Balancers terminate traffic using regional proxy-only subnets rather than global Anycast GFEs.
- Link-local IP addresses (
169.254.0.0/16) are reserved for internal infrastructure communication and not load-balanced client workloads.
This answer would be correct if
The goal was to build a private, multi-region internal microservices mesh reachable only by clients located within the corporate private network.
Deploy a Global External Application Load Balancer, and create local VPC firewall rules in each service project allowing ingress from 0.0.0.0/0 on port 80 and port 443.
Deploy a Global External Application Load Balancer, and create local VPC firewall rules in each service project allowing ingress from 0.0.0.0/0 on port 80 and port 443.
What this option is and does
This approach deploys a Global External Application Load Balancer but manages firewall rules locally inside individual service projects using standard VPC firewall rules.
Why it doesn't meet the requirements
- VPC ownership model in Shared VPC: In a Shared VPC architecture, VPC firewall rules must be created in the host project, not in service projects. Service projects do not hold their own VPC firewall rule objects for the shared network.
- No guardrails against overrides: Standard VPC firewall rules lack hierarchical policy controls. Decentralizing rules across multiple projects allows service project admins to accidentally create higher-priority deny rules that break application traffic.
- Overly broad ingress ranges: GFE-proxied application load balancers communicate with backends using specific Google IP ranges (
35.191.0.0/16and130.211.0.0/22). Allowing0.0.0.0/0unnecessarily widens the attack surface.
Key characteristics and limitations
- Local VPC firewall rules are evaluated after hierarchical policies and do not provide organization-wide governance.
- Service project teams lack permissions to manage host VPC firewall rules directly.
This answer would be correct if
The application were deployed within standalone, unshared VPCs where each development team had full administrative control over their isolated network security.
Deploy a Global External Application Load Balancer, and attach a hierarchical firewall policy to the Production folder that allows ingress from 35.191.0.0/16 and 130.211.0.0/22 to the backend instances.
Deploy a Global External Application Load Balancer, and attach a hierarchical firewall policy to the Production folder that allows ingress from 35.191.0.0/16 and 130.211.0.0/22 to the backend instances.
What Global External Application Load Balancing and Hierarchical Firewall Policies Are
A Global External Application Load Balancer is a Layer 7 load balancer built on globally distributed Google Front End (GFE) proxies that terminates HTTP(S) traffic at points of presence (PoPs) close to users. A hierarchical firewall policy allows organization or folder administrators to define and enforce firewall rules across the entire resource hierarchy, taking precedence over project-level and VPC-level firewall rules.
How it meets all requirements
- Global traffic routing and automatic overflow: The Global External Application Load Balancer uses the Waterfall by Region algorithm. Traffic is directed to the closest healthy backend region, and if a region exceeds its defined capacity threshold or becomes unhealthy, requests automatically and seamlessly overflow to the next closest region with available capacity.
- Centralized baseline enforcement: In a Shared VPC architecture, VM interfaces connected to the Shared VPC network inherit firewall policies from the host project's folder ancestry. Attaching the hierarchical firewall policy to the
Productionfolder covering the host project centrally applies the policy to all backends across all connected service projects. - Preventing team overrides: Hierarchical firewall rules are evaluated before VPC firewall rules and cannot be overridden or removed by project-level administrators or service project owners.
Waterfall Overflow Across Regions
System Architecture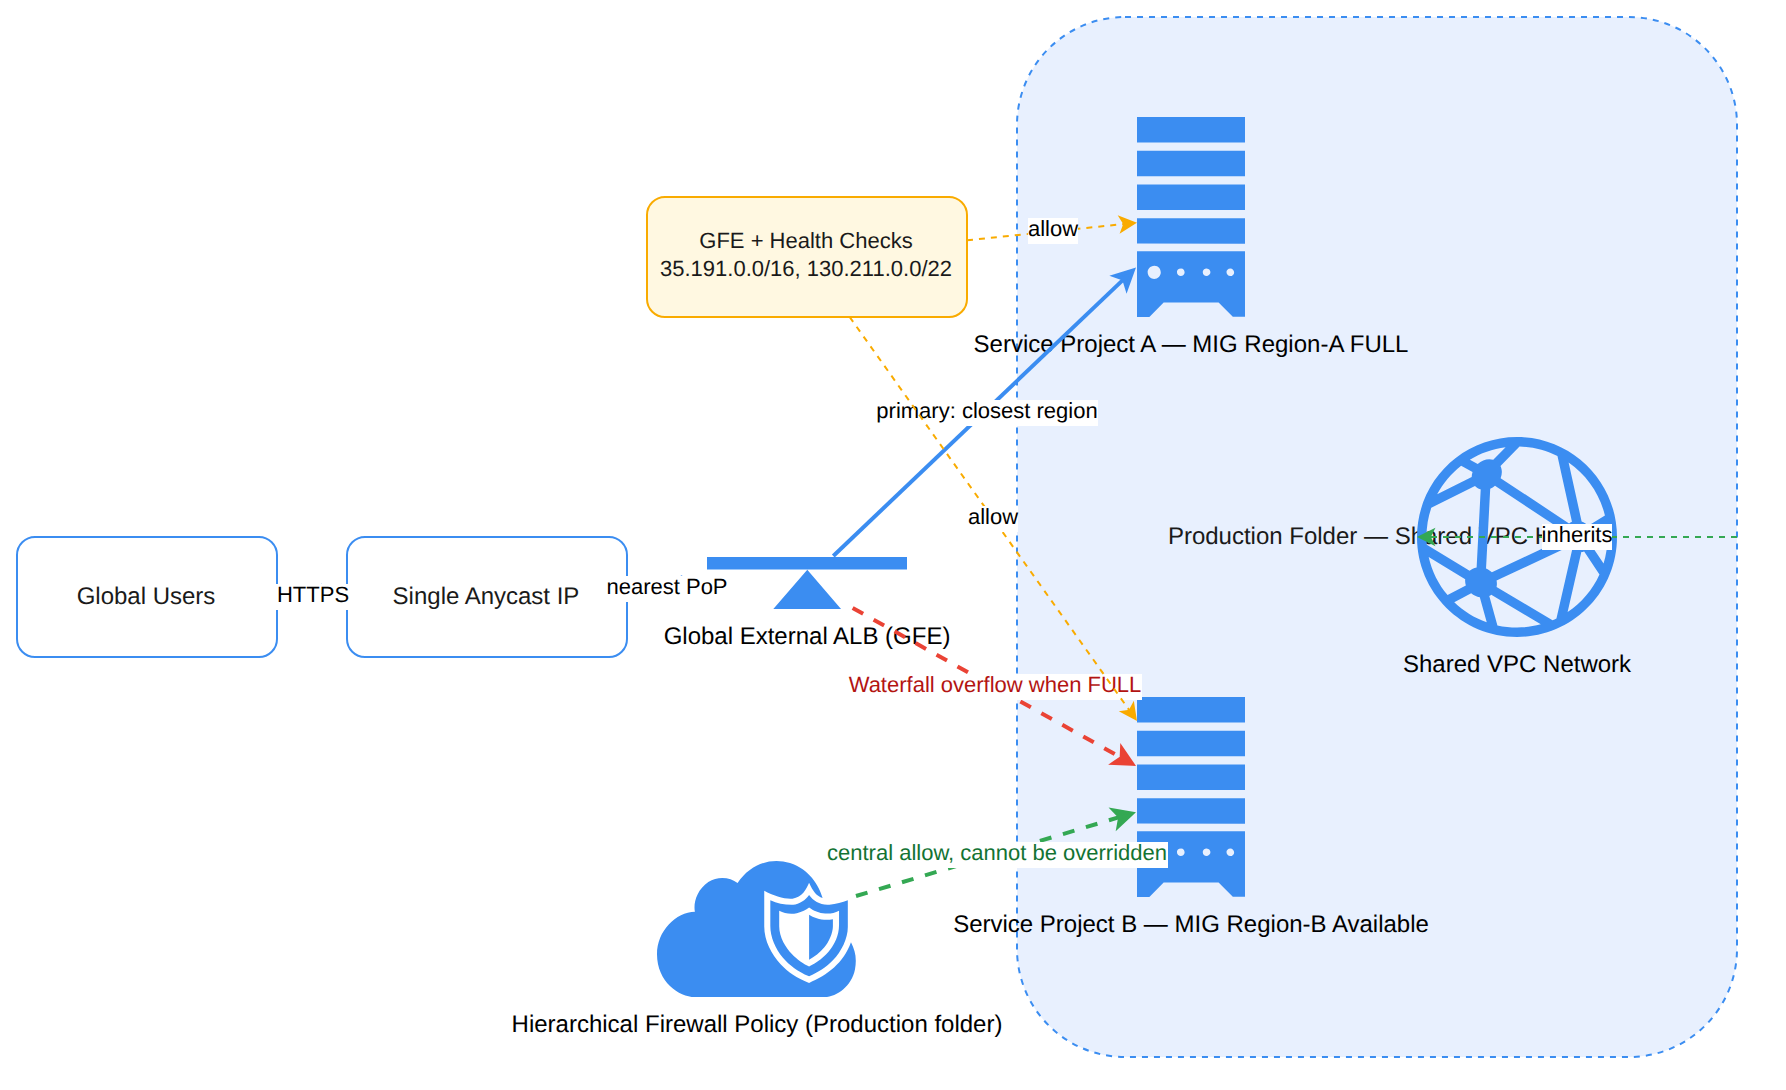
Key advantages and capabilities
- Single Anycast IP: Provides global Anycast routing so users worldwide connect to the nearest edge location.
- Consistent security posture: Ensures mandatory GFE proxy and health check probe CIDRs (
35.191.0.0/16and130.211.0.0/22) are permitted without depending on decentralized service project configurations. - Intelligent traffic management: Dynamically accounts for backend capacity and backend health without relying on DNS TTL delays.
Why this is optimal
This solution combines edge-terminated global HTTP(S) distribution with enterprise governance. It guarantees optimal multi-region traffic balancing while enforcing immutable security perimeters across distributed application backends.
Deploy an External Passthrough Network Load Balancer in each region, and configure regional network firewall policies in each service project allowing ingress from 0.0.0.0/0.
Deploy an External Passthrough Network Load Balancer in each region, and configure regional network firewall policies in each service project allowing ingress from 0.0.0.0/0.
What this option is and does
This configuration deploys regional External Passthrough Network Load Balancers in each region and relies on regional network firewall policies configured locally within individual service projects.
Why it doesn't meet the requirements
- Lacks intelligent cross-region overflow: External Passthrough Network Load Balancers are regional Layer 4 systems. They do not operate on GFE Anycast architecture and cannot automatically shift HTTP(S) traffic to the next closest region when a regional backend reaches its configured capacity.
- Fails centralized enforcement: Regional network firewall policies created inside service projects cannot be centrally managed at the organization or folder level and do not guarantee uniform security governance across the Shared VPC.
- Overly permissive security perimeter: Opening backends to
0.0.0.0/0at the service project level exposes workloads directly rather than restricting access to verified load balancer proxies and health checks.
Key characteristics and limitations
- Passthrough load balancers preserve client source IPs but lack HTTP-layer traffic routing and cross-region capacity balancing.
- Service project administrators can modify local project rules, creating potential configuration drift and security vulnerabilities.
This answer would be correct if
The workload required direct Layer 4 passthrough of non-HTTP protocols with client IP preservation and was strictly confined to isolated single-region deployments.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Private Service Connect Published Services
Cloud-native networking (e.g., virtual private cloud [VPC], peering, firewalls, load balancers, routing, container networking, shared VPC, and Private Service Connect)
IntermediateProfessional Cloud Architect
VPC Peering Non-Transitive Routing
Cloud-native networking (e.g., virtual private cloud [VPC], peering, firewalls, load balancers, routing, container networking, shared VPC, and Private Service Connect)
IntermediateProfessional Cloud Architect
IAM Recommender Role Recommendations
Identity and Access Management (IAM)
IntermediateProfessional Cloud Architect
Network Intelligence Center Connectivity Tests
Troubleshooting/root cause analysis best practices
IntermediateProfessional Cloud Architect
Cloud Router Advertised Route Priority
Integration with on-premises/multicloud environments
AdvancedProfessional Data Engineer
Cloud Composer Deferrable Operators
Interactive or batch query jobs
Last updated