Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Preserving Cloud Trace Context Across Projects
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
Your organization operates a distributed multi-tier microservices application deployed across multiple Google Cloud projects. The services communicate over HTTP and use Envoy sidecar proxies configured within a service mesh to generate telemetry.
During performance troubleshooting, the operations team notices that requests spanning across project boundaries appear as disconnected, isolated spans in Cloud Trace rather than a single contiguous end-to-end distributed trace.
What should you do to ensure trace continuity across the different projects?
Explanations
Grant the roles/cloudtrace.admin role to the Compute Engine default service accounts across all projects to enable automatic cross-project span federation.
Grant the roles/cloudtrace.admin role to the Compute Engine default service accounts across all projects to enable automatic cross-project span federation.
What the Cloud Trace Admin Role Is
The roles/cloudtrace.admin IAM role grants full administrative permissions over Cloud Trace resources, allowing principals to manage trace configurations, sampling rates, and read/write trace data within a given project.
Why It Doesn't Meet the Requirement
- Authorization vs. Context Propagation: Traces are fragmented because downstream requests lack the distributed trace context header (
X-Cloud-Trace-Context), not because of permission failures. If IAM permissions were missing, spans would be dropped entirely rather than appearing as disconnected traces. - Violates Principle of Least Privilege: Compute Engine workloads only require the
roles/cloudtrace.agentrole (roles/cloudtrace.agent) to write trace spans, making the administrative role unnecessarily broad and excessive.
Key Characteristics and Limitations
- Control Plane Permission: Manages IAM policies and trace sinking rather than runtime HTTP header injection.
- Agent Permissions: Workload VMs merely need write access via the Cloud Trace Agent role to send trace data.
This Answer Would Be Correct If
The sidecar proxies were receiving HTTP 403 Forbidden permission errors when attempting to post trace buffers to the Google Cloud Trace API endpoint.
Ensure that applications preserve and propagate the X-Cloud-Trace-Context HTTP header across service calls, and verify each proxy runs with credentials for its respective project.
Ensure that applications preserve and propagate the X-Cloud-Trace-Context HTTP header across service calls, and verify each proxy runs with credentials for its respective project.
What Distributed Tracing Context Propagation Is
Cloud Trace relies on context propagation to stitch individual operations (spans) across distributed architectures into a single coherent trace tree. In HTTP-based distributed environments, telemetry frameworks and sidecar proxies like Envoy use standardized tracking headers—specifically the X-Cloud-Trace-Context header—to pass trace identifiers, span identifiers, and trace flags between upstream callers and downstream callee services.
One Trace ID Across Projects via Header
Sequence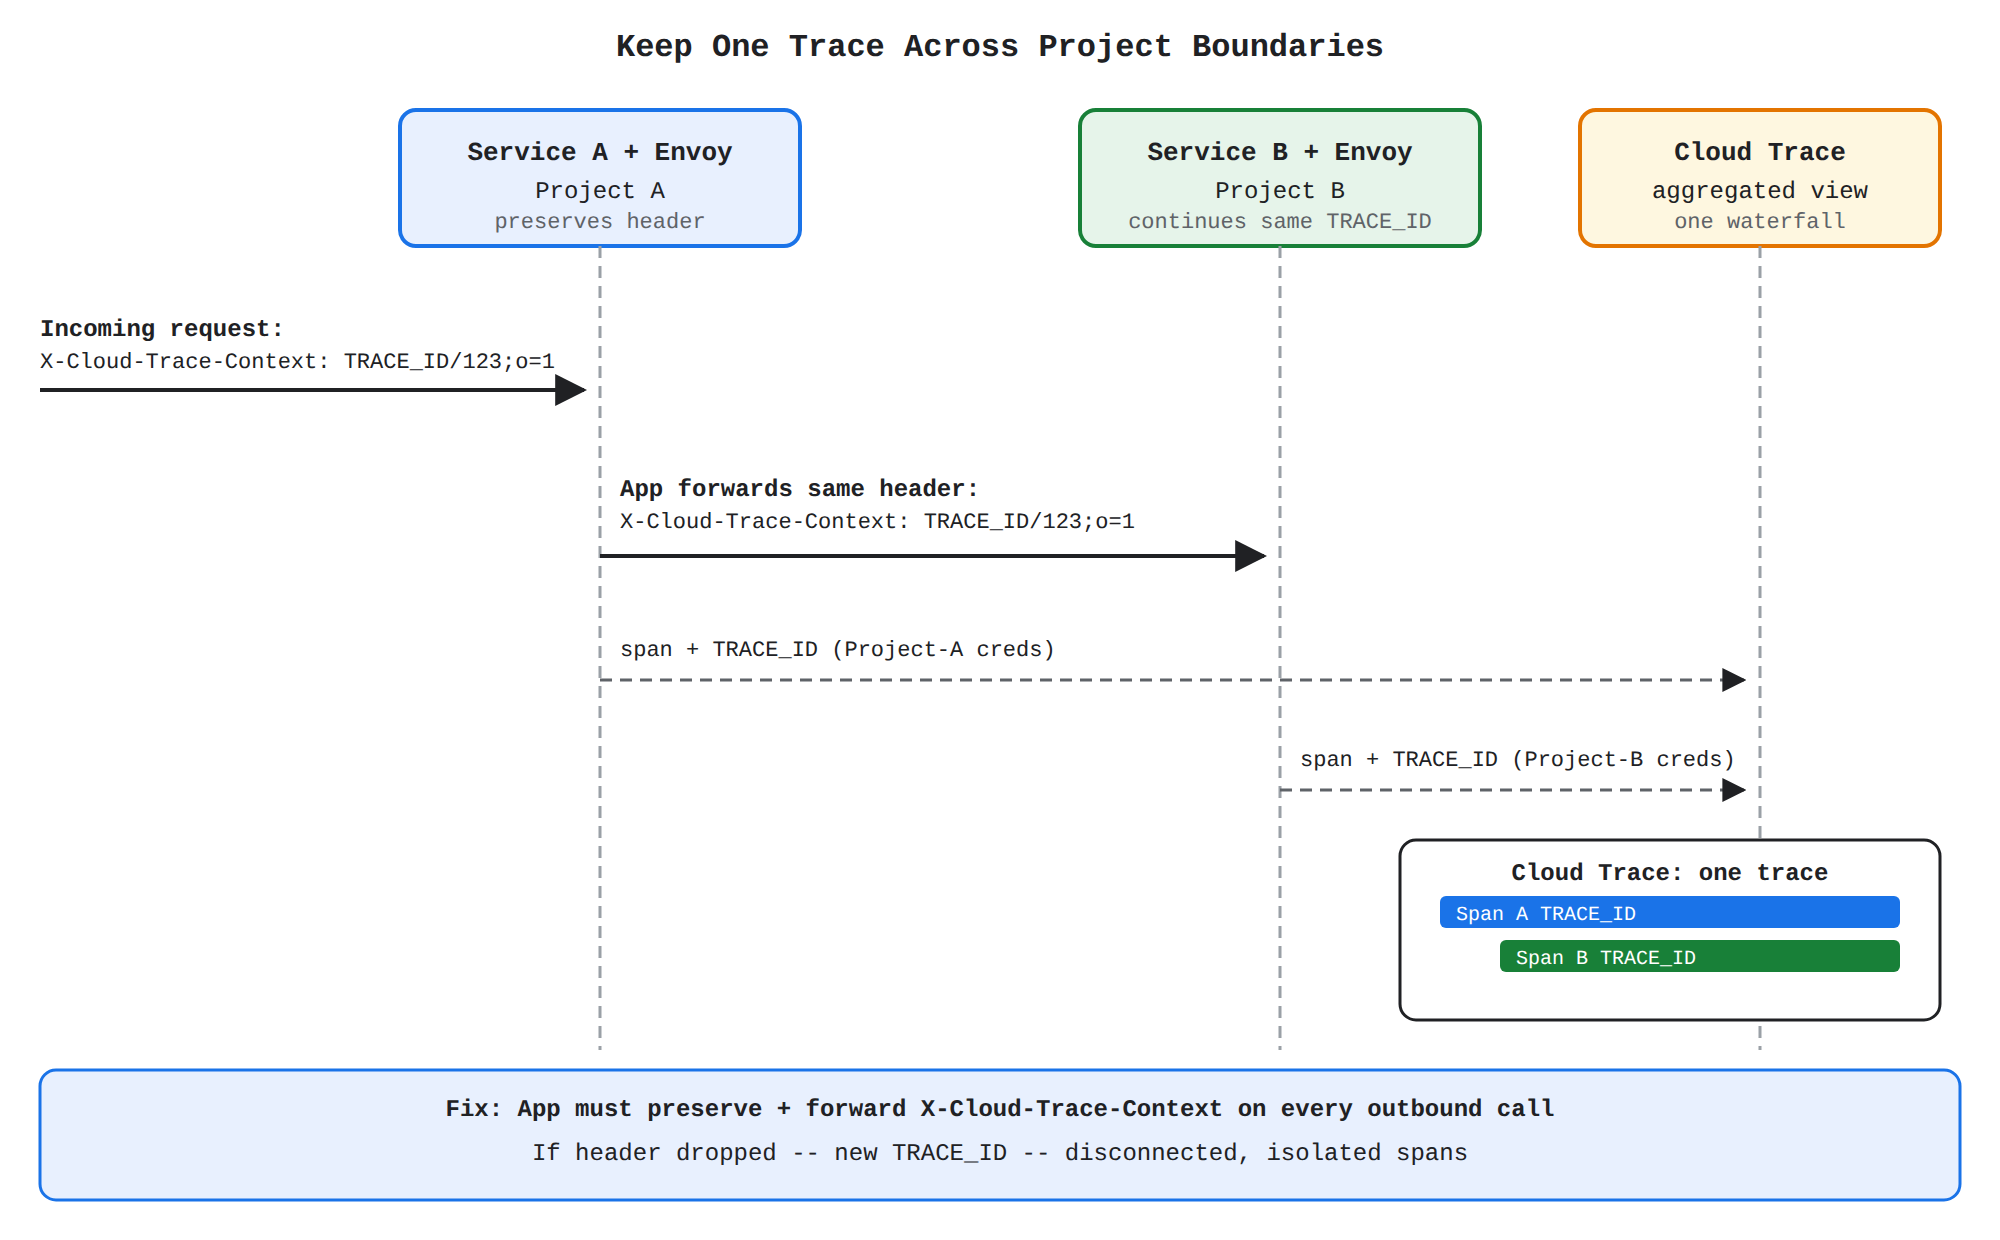
How It Solves the Disconnected Traces Issue
When a request traverses multiple Google Cloud projects:
- Header Forwarding: The upstream microservice must forward the incoming
X-Cloud-Trace-ContextHTTP header in all downstream outbound requests. If an intermediary service drops this header, the downstream proxy assumes the call is a new root request, generating a new trace ID and breaking trace correlation. - Project Authentication: Each Envoy proxy or telemetry exporter reports trace spans using credentials from its local hosting project. Cloud Trace aggregates these spans across project boundaries automatically when the trace ID is preserved.
Key Advantages and Capabilities
- End-to-End Latency Visibility: Provides distributed waterfall visualizations showing exact processing durations across service and project boundaries.
- Root Cause Isolation: Identifies the exact microservice or network hop introducing latency or raising exceptions.
- Cross-Project Aggregation: Eliminates data silos across multi-project landing zones without requiring centralized batch exports.
- Minimal Overhead: Propagates lightweight metadata across existing HTTP/gRPC communication channels.
Why This Is Optimal
Preserving context headers directly addresses the mechanism used by Cloud Trace and service proxies to establish parent-child span relationships across projects without requiring extra networking infrastructure.
Deploy an internal Application Load Balancer between project boundaries to inspect packets and inject missing trace metadata.
Deploy an internal Application Load Balancer between project boundaries to inspect packets and inject missing trace metadata.
What Internal Application Load Balancers Are
Internal Application Load Balancers (ALBs) are proxy-based regional Layer 7 load balancers that distribute HTTP and HTTPS traffic across backend VM instances, Google Kubernetes Engine pods, or serverless endpoints inside a Virtual Private Cloud (VPC).
Why It Doesn't Meet the Requirement
- Inability to Reconstruct Context: An intermediary load balancer cannot determine the original parent trace context if the calling upstream application dropped the context header before issuing the outbound call.
- Unnecessary Infrastructure Overhead: Adding intermediary load balancers strictly for header forwarding introduces unnecessary latency, financial cost, and architectural complexity.
- Native Mesh Capability: Service mesh sidecars and microservices natively manage HTTP headers when standard tracing libraries (such as OpenTelemetry or OpenCensus) are properly configured.
Key Characteristics and Limitations
- Traffic Distribution: Operates as a reverse proxy for Layer 7 load balancing and path-based routing.
- Does Not Fix In-App Omissions: Cannot infer application-level causality if headers are discarded by internal microservice business logic.
This Answer Would Be Correct If
You needed private Layer 7 traffic routing, path-based URL mapping, and SSL offloading across different VPCs connected via Private Service Connect.
Configure a centralized Cloud Storage bucket in the root project and modify the Logging agent on all VMs to stream raw trace files directly into the bucket.
Configure a centralized Cloud Storage bucket in the root project and modify the Logging agent on all VMs to stream raw trace files directly into the bucket.
What Cloud Storage Log Exporting Is
Exporting telemetry to Cloud Storage involves batching log entries or raw text files via Cloud Logging log sinks for long-term archiving, compliance retention, or offline analytical processing using BigQuery.
Why It Doesn't Meet the Requirement
- Not an Ingestion Path for Cloud Trace: Cloud Trace ingests live trace spans directly via the Cloud Trace API (
trace.googleapis.com) or OpenTelemetry collectors, not by scanning static raw files dumped into Cloud Storage buckets. - Fails Distributed Context Assembly: Storing raw unparsed files into an object bucket does not propagate trace contexts or repair disjointed parent-child span hierarchies in real-time observability tooling.
Key Characteristics and Limitations
- Batch-Oriented Storage: Optimized for long-term cold storage and security compliance rather than low-latency interactive performance analysis.
- No Distributed Correlation Engine: Cloud Storage does not index or link HTTP trace headers.
- Increased Latency: Introduces significant delay before diagnostic data is readable.
This Answer Would Be Correct If
Your objective was to meet long-term compliance regulations requiring archival storage of raw access logs for multi-year audit requirements.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Rolling Compliance Period and Error Budget
Monitoring and logging
IntermediateProfessional Cloud Architect
Aggregated Log Sinks and Exclusion Filters
Monitoring and logging
IntermediateProfessional Cloud Architect
Warm Standby Disaster Recovery Pattern
Disaster recovery
IntermediateProfessional Cloud Architect
Least Privilege IAM and GitOps with Break-Glass OU
Change management
IntermediateProfessional Cloud Architect
Pub/Sub StreamingPull Flow Control
Supporting the application design
AdvancedProfessional Cloud DevOps Engineer
Gemini Cloud Assist Recommendation Validation
Employing Gemini Cloud Assist for trace analysis
Last updated