Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Cloud Storage Lifecycle Rules for Audit Logs
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
A financial services organization stores transaction audit files in a Cloud Storage bucket with Object Versioning enabled. The files are written under the prefix audit-logs/ and follow specific access patterns:
- Files are accessed frequently during the first 30 days after creation.
- Files are accessed roughly once a month between 30 and 90 days.
- Files are accessed once a quarter between 90 and 365 days.
- Files must be permanently deleted after 365 days.
- To optimize costs, any overwritten or deleted noncurrent object versions under the
audit-logs/prefix should be permanently removed 14 days after becoming noncurrent.
Which Object Lifecycle Management (OLM) configuration meets these requirements with the least operational overhead?
Explanations
Configure Object Lifecycle Management rules with prefix condition audit-logs/ to transition storage to Nearline at age 30, transition to Coldline at age 90, delete live objects at age 365, and delete noncurrent versions using daysSinceNoncurrentTime: 14.
Configure Object Lifecycle Management rules with prefix condition audit-logs/ to transition storage to Nearline at age 30, transition to Coldline at age 90, delete live objects at age 365, and delete noncurrent versions using daysSinceNoncurrentTime: 14.
What Object Lifecycle Management (OLM) is
Cloud Storage Object Lifecycle Management (OLM) allows administrators to define declarative rules consisting of actions (such as SetStorageClass and Delete) coupled with specific conditions (such as Age, MatchesPrefix, IsLive, and DaysSinceNoncurrentTime). Cloud Storage automatically inspects objects within the bucket and executes the configured actions asynchronously without requiring external compute infrastructure.
How it meets the requirements
- Storage Class Transitions:
- Setting an action to
SetStorageClasswith target Nearline atAge: 30aligns with monthly access patterns. - Setting an action to
SetStorageClasswith target Coldline atAge: 90matches quarterly access requirements.
- Setting an action to
- Prefix Filtering: Applying the
MatchesPrefix: audit-logs/condition ensures that only audit log objects are affected by these policies. - Object Retention and Deletion: Setting a
Deleteaction withAge: 365purges live logs after one year. - Noncurrent Version Management: Using the condition
DaysSinceNoncurrentTime: 14(orIsLive: falsewith noncurrent age) ensures that superseded or deleted log versions are permanently removed 14 days after becoming noncurrent, preventing unbounded storage accumulation in version-enabled buckets.
Audit Log Lifecycle Timeline (OLM Rules)
Timeline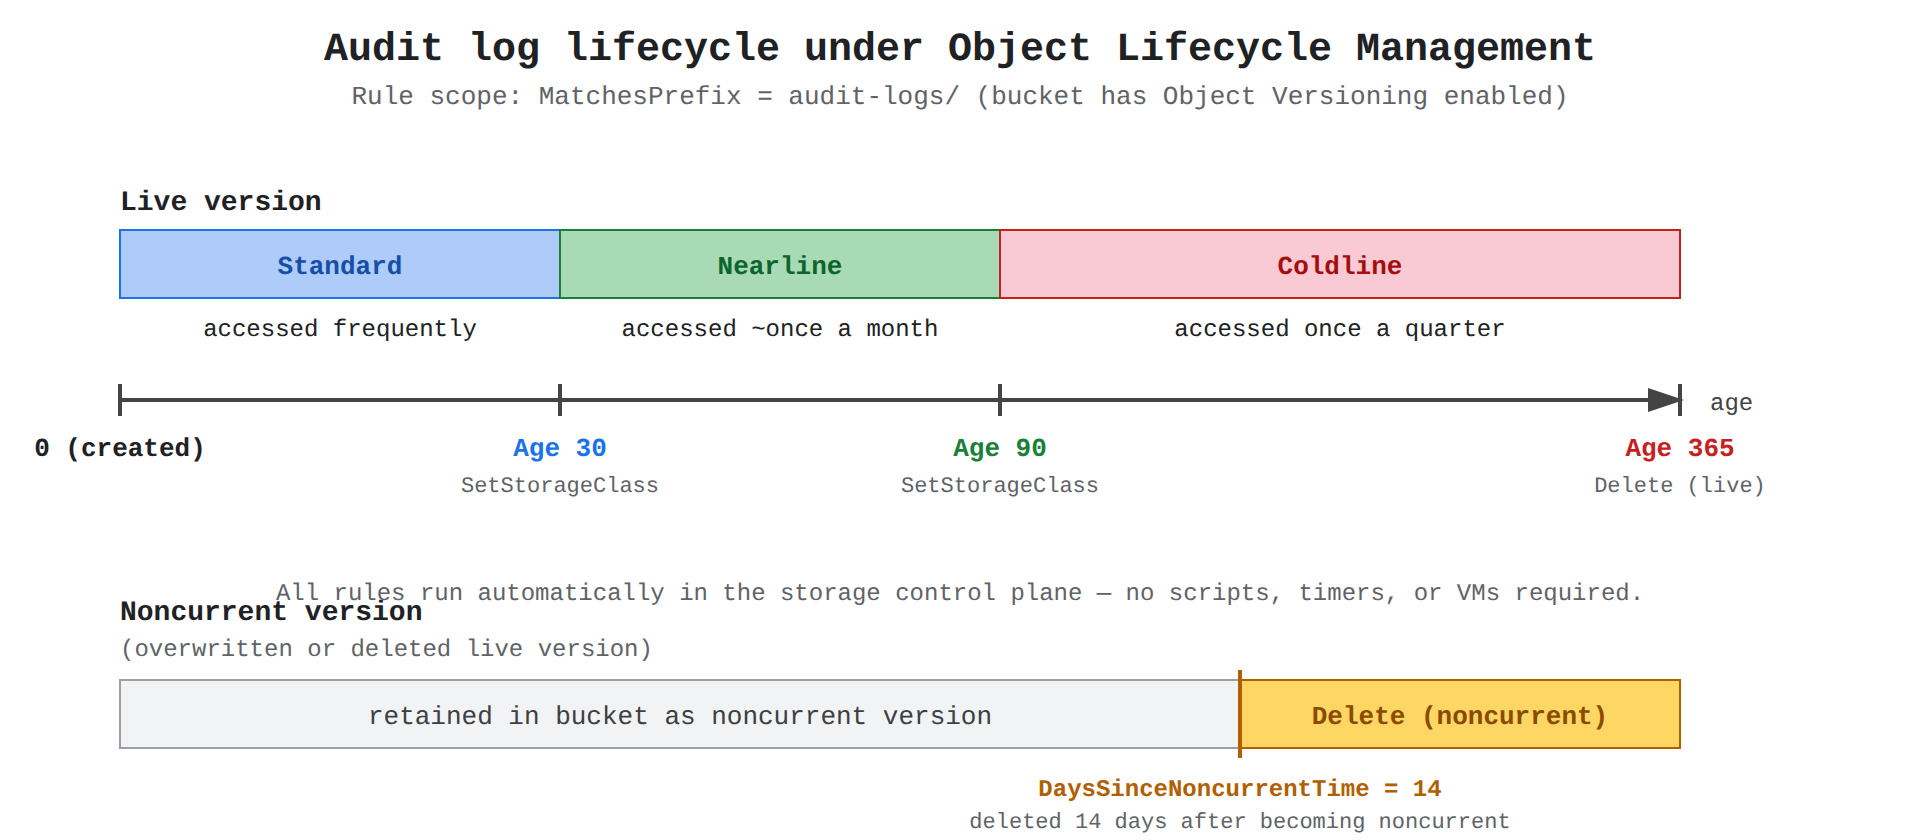
Key advantages of this approach
- Zero Management Overhead: Fully managed and native to Google Cloud Storage without requiring external scripts, timers, or virtual machines.
- Granular Cost Optimization: Automatically shifts data to lower-cost storage tiers based on proven access cadence (Nearline for monthly, Coldline for quarterly).
- Automated Hygiene: Cleans up noncurrent object versions created by bucket versioning policies automatically.
Why this is optimal
Native lifecycle policies execute directly within the storage control plane, providing predictable lifecycle transitions and deletions while strictly honoring prefix constraints and version states.
Enable bucket-level Autoclass with a 365-day Bucket Lock retention policy, and schedule a daily Cloud Run job to identify and delete noncurrent object versions.
Enable bucket-level Autoclass with a 365-day Bucket Lock retention policy, and schedule a daily Cloud Run job to identify and delete noncurrent object versions.
What this option does
Autoclass automatically transitions objects between Standard, Nearline, Coldline, and Archive based on individual object access patterns. A Bucket Lock (Retention Policy) places a compliance lock on objects to prevent them from being deleted until the retention period elapses.
Why it doesn't meet the requirement
- Incompatible Retention Controls: Applying a 365-day Bucket Lock retention policy prevents any deletion of live or noncurrent objects until 365 days have passed. This directly conflicts with the requirement to permanently purge noncurrent versions after only 14 days.
- Autoclass Misalignment: While Autoclass automates storage classes, it does not support prefix-scoped rule definitions for specific sub-directories (
audit-logs/) or automated time-bound object deletions. - Operational Overhead: Employing an external Cloud Run batch container requires managing container images, Cloud Scheduler triggers, and authentication to iterate through bucket listings.
Key limitations
- Bucket Lock policies cannot be bypassed to clean up noncurrent versions early.
- Autoclass charges an Autoclass management fee per 1,000 objects, which may be suboptimal for high-volume write-once workloads with known static schedules.
This answer would be correct if
Access patterns were entirely unpredictable across the entire bucket and regulatory mandates required a legal, immutable compliance lock preventing data deletion.
Deploy a Cloud Function triggered by Cloud Storage Pub/Sub notifications on object creation that calculates retention timestamps and invokes the Cloud Storage API to rewrite storage classes and delete noncurrent versions.
Deploy a Cloud Function triggered by Cloud Storage Pub/Sub notifications on object creation that calculates retention timestamps and invokes the Cloud Storage API to rewrite storage classes and delete noncurrent versions.
What this option does
This architecture relies on event-driven computing via Cloud Storage Pub/Sub notifications and Cloud Functions to handle storage tiering and deletion programmatically via custom code and storage API mutations.
Why it doesn't meet the requirement
- High Operational and Code Overhead: Writing, testing, deploying, and maintaining custom Cloud Function code creates significant architectural complexity when native Object Lifecycle Management rules already provide this capability natively.
- Inefficient Version and Time Tracking: Object creation notifications occur immediately upon upload. A function triggered at creation cannot sleep for 30, 90, or 365 days; it would require scheduling external cron tasks or persistent database state to track when to trigger future rewrites or deletions.
- Cost Inefficiency: Incurring execution charges for Cloud Functions, Pub/Sub messaging, and individual API rewrite calls is unnecessarily costly compared to free native OLM rule processing.
Key limitations
- Requires managing custom service account permissions and error-handling logic.
- Does not scale cleanly when managing millions of existing objects across complex versioning timelines.
This answer would be correct if
Custom business logic required external validation against an on-premises database or third-party approval system before authorizing storage tier shifts or deletions.
Configure Object Lifecycle Management rules to transition objects directly to Archive storage at age 30, and apply an IAM Deny policy on the bucket to prevent access to noncurrent versions older than 14 days.
Configure Object Lifecycle Management rules to transition objects directly to Archive storage at age 30, and apply an IAM Deny policy on the bucket to prevent access to noncurrent versions older than 14 days.
What this option does
This configuration moves objects directly to Archive storage after 30 days and uses Identity and Access Management (IAM) Deny policies to block identity access to noncurrent object versions.
Why it doesn't meet the requirement
- Improper Storage Class Tiering: Archive storage is designed for data accessed at most once a year. The scenario explicitly states files are accessed monthly between days 30 and 90, and quarterly between days 90 and 365. Reading Archive objects on a monthly or quarterly basis triggers high data retrieval fees and higher latency costs.
- IAM Deny Does Not Delete Data: An IAM policy controls authorization and access permissions; it does not delete underlying data. Noncurrent versions would remain stored indefinitely, continuing to incur monthly storage charges.
- Failure to Purge at End of Life: An IAM Deny policy does not meet the requirement to permanently delete live objects after 365 days.
Key limitations
- Archive storage has a minimum 365-day storage duration charge, making early deletion or frequent retrieval cost-prohibitive.
- IAM conditions cannot perform automated object lifecycle deletion actions.
This answer would be correct if
Data was strictly intended for long-term disaster recovery accessed less than once a year, and access needed to be administratively blocked without modifying bucket contents.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
BigQuery Partition Expiration
Data retention and data lifecycle management
IntermediateProfessional Cloud Architect
Cloud Storage Bucket Lock Object Legal Holds
Data retention and data lifecycle management
IntermediateProfessional Cloud Architect
gsutil rsync
Google Cloud SDKs (e.g., gcloud, gsutil, and bq)
IntermediateProfessional Cloud Architect
Apigee API Mediation and Response Caching
API management best practices (e.g., Apigee)
IntermediateProfessional Cloud Architect
Global External Application Load Balancer Cloud DNS Failover
Disaster recovery
FundamentalAssociate Data Practitioner
Cloud Storage Regional Location
Choose the appropriate data storage location type (e.g., regional, dual-regional, multi-regional, zonal)
Last updated